

donut
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
exploitationids-ips-evasionmemory-forensics+7
4.7k
thewover/donutGenerates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
 frkngksl/shoggoth
Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…
 jfmaes/lazysign
Create fake certs for binaries using windows binaries and the power of bat files
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
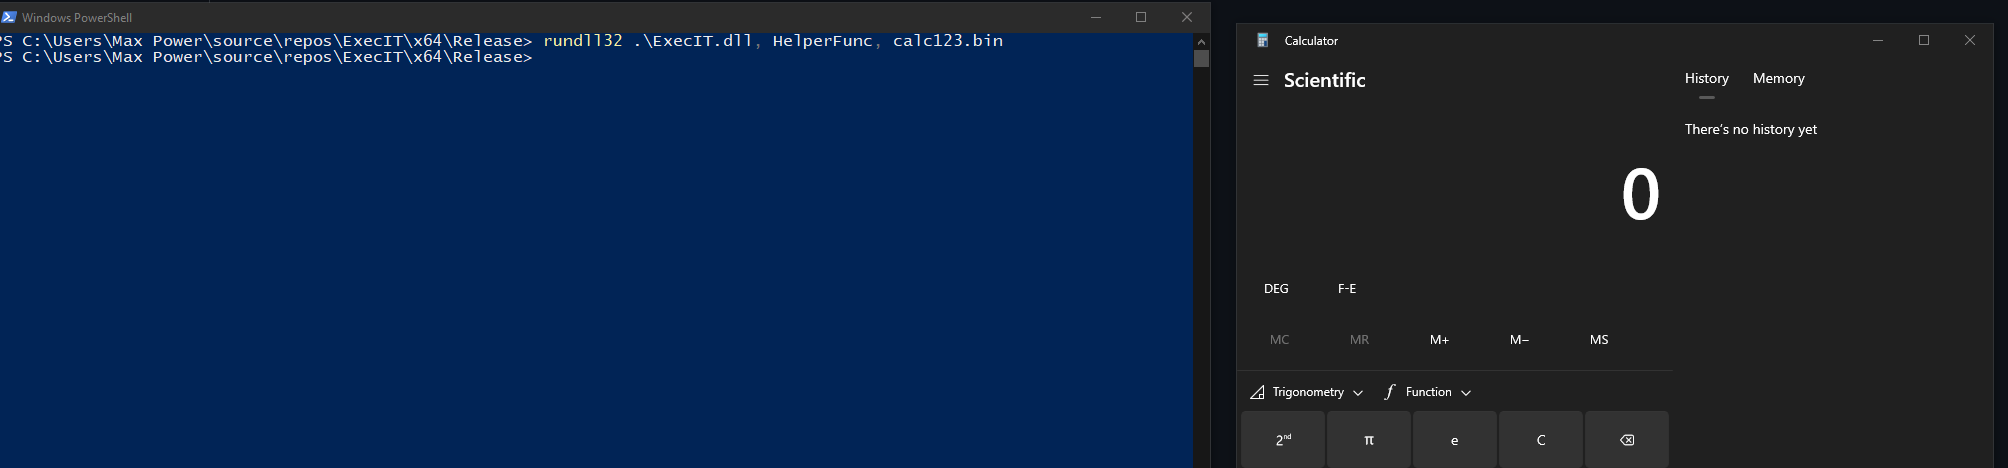 florylsk/execit
Execute shellcode files with rundll32
 epotseluevskaya/aspx_webshell_coffloader
ASPX web shell with COFF loader for executing Beacon Object Files (BOFs) on target servers via a semi-interactive Python client, designed for…
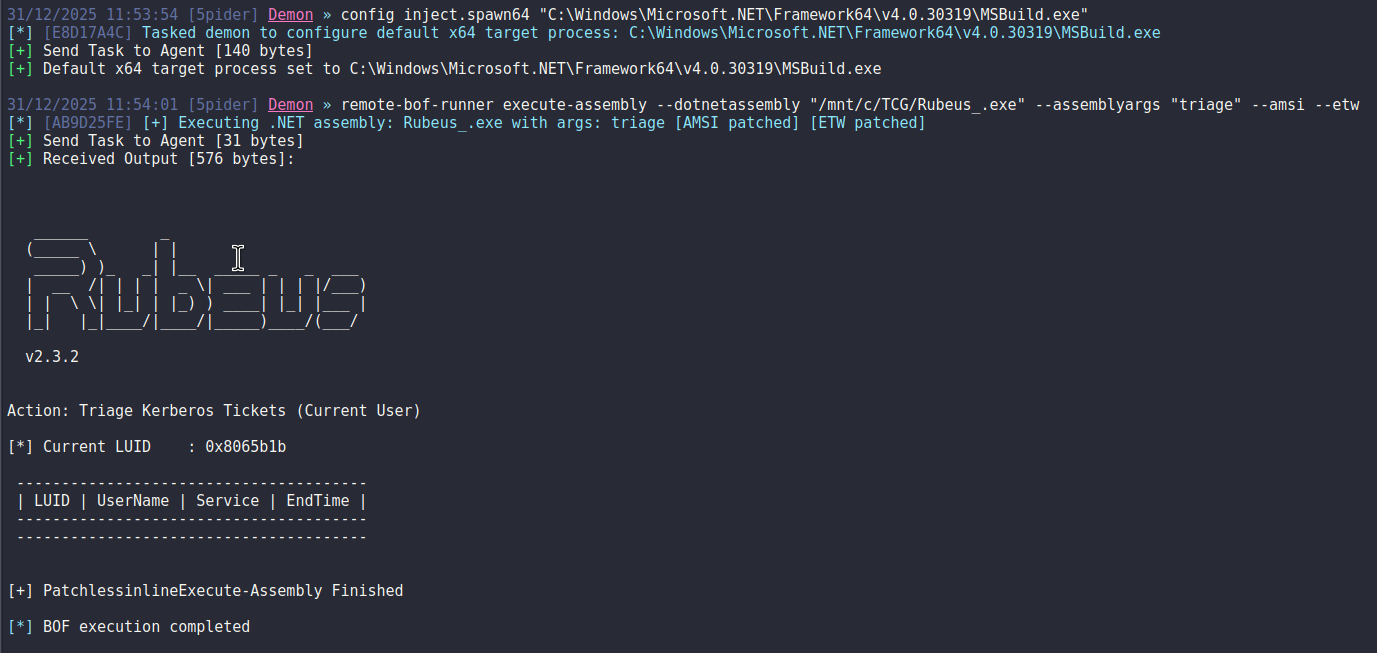 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 0x00jeff/cve-2025-27591
self cleaning CVE-2025-27591 Poc that grants a root reverse shell instead of modifying passwd files
 encrypter15/cve-2025-50165-x64-exploit
Generates weaponized JPEG files exploiting CVE-2025-50165 (Windows Graphics RCE) with custom x64 shellcode, heap spray, ROP chain, and AV/EDR evasion…
 abq0/rwsploit
Automated exploitation scanner for Oracle Reports Server (rwservlet) — CVE-2012-3152 / CVE-2012-3153. Detects, fingerprints, reads files via LFI,…
 maldiohead/tfc-chrome-v8-bug-cve-2021-38001-poc
Proof-of-concept exploit for CVE-2021-38001, a Chrome V8 JavaScript engine vulnerability, demonstrating remote code execution via crafted .mjs files.
 spiralbl0ck/partial-deobfuscated-sc-from-hackingteam-malware.-
This repo stores necessary files for the analysis blog which will come soon
 hexastrike/cve-2008-4654
A fully functional exploit for a stack-based buffer overflow vulnerability in VideoLan’s VLC Media Player 0.9.4 when processing TiVo files.
 rnnsz/cve-2008-4654
PoC exploit generator for CVE-2008-4654, a stack-based buffer overflow in VLC Media Player via crafted .ty+ files. Generates malicious payload file…
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 jthuraisamy/syswhispers
AV/EDR evasion via direct system calls.
 jthuraisamy/syswhispers2
AV/EDR evasion via direct system calls.