
K8tools
 k8gege/k8tools
K8工具合集(内网渗透/提权工具/远程溢出/漏洞利用/扫描工具/密码破解/免杀工具/Exploit/APT/0day/Shellcode/Payload/priviledge/BypassUAC/OverFlow/WebShell/PenTest) Web GetShell…
command-and-controlexploit-frameworkslateral-movement+9
6.2k
k8gege/k8toolsK8工具合集(内网渗透/提权工具/远程溢出/漏洞利用/扫描工具/密码破解/免杀工具/Exploit/APT/0day/Shellcode/Payload/priviledge/BypassUAC/OverFlow/WebShell/PenTest) Web GetShell…
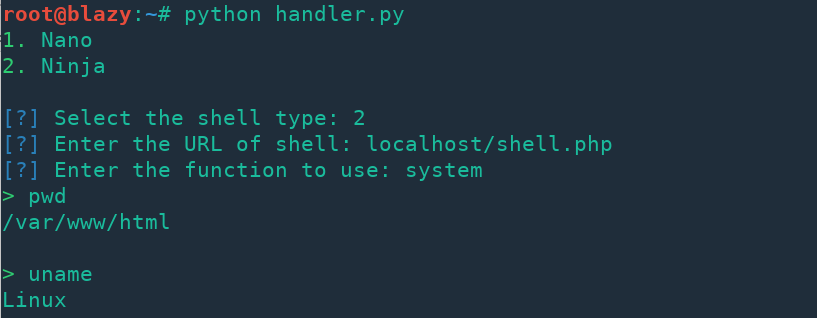 s0md3v/nano
Nano is a family of PHP web shells which are code golfed for stealth.
 flangvik/sharpproxylogon
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode injection
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
 epotseluevskaya/aspx_webshell_coffloader
ASPX web shell with COFF loader for executing Beacon Object Files (BOFs) on target servers via a semi-interactive Python client, designed for…
 gildasio/wshlient
A simple tool to interact with web shells and command injection vulnerabilities
 liangyueliangyue/spring-core-rce
Python-based exploit for CVE-2022-22965 (Spring4Shell) with vulnerability detection and webshell injection (Behinder/Godzilla) into Spring web…
 dust-life/cve-2019-18935-memshell
C++ memshell DLL generator for CVE-2019-18935, enabling in-memory web shell deployment via Telerik UI deserialization with Assembly.Load and IJW…
 satirush/cve-2025-14174-poc
Proof-of-Concept exploit for CVE-2025-14174 (EUVD-2025-203113) - Memory corruption in ANGLE allowing out-of-bounds access and RCE in web browsers.…
 hussienmisbah/exploits
Repository containing exploit scripts for various CVEs, targeting web applications, binaries, and network services, suitable for penetration testing…
 nu11secur1ty/shellupload
PHP-based web shell uploader for penetration testing, enabling file upload and remote command execution on vulnerable web servers.
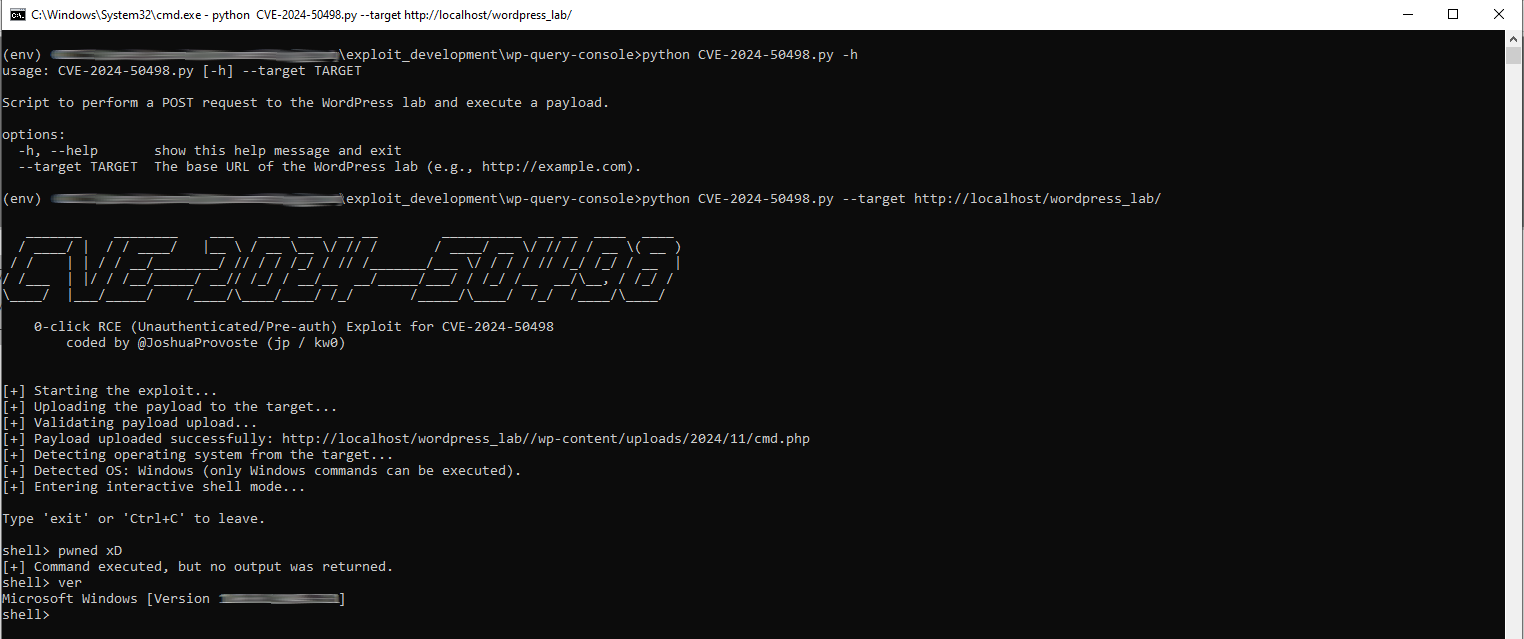 joshuaprovoste/0-click-rce-exploit-for-cve-2024-50498
Unauthenticated 0-click RCE exploit for CVE-2024-50498. Exploits a code injection vulnerability in the LUBUS WP Query Console plugin to execute…
 funixone/exploit-cve-2026-8832-
Automated RCE exploit for WordPress WPCode Lite v2.3.5. Executes 6-step exploitation chain via XML-RPC bypass with 8 built-in PHP payloads, including…
 themalwareguardian/cve-2002-1120
Classic stack-based buffer overflow in Savant Web Server 3.1 demonstrating early-2000s remote memory corruption through a crafted HTTP request.
 themalwareguardian/cve-2018-18912
SEH-based buffer overflow in Easy File Sharing Web Server 7.2 demonstrating how an authenticated HTTP POST parameter can corrupt the exception…
 0xryuk/cve-2022-24637
Open Web Analytics 1.7.3 - Remote Code Execution Exploit v2
 cancela24/cve-2019-16278-nostromo-1.9.6-rce
Exploit for CVE-2019-16278 targeting Nostromo Web Server 1.9.6, achieving remote code execution via directory traversal. Uses pwntools to deliver a…