

Rusty-Playground
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development
binary-analysisexploitationmalware-analysis+6
162
blacksnufkin/rusty-playgroundSome Rust program I wrote while learning Malware Development
 jfmaes/lazysign
Create fake certs for binaries using windows binaries and the power of bat files
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
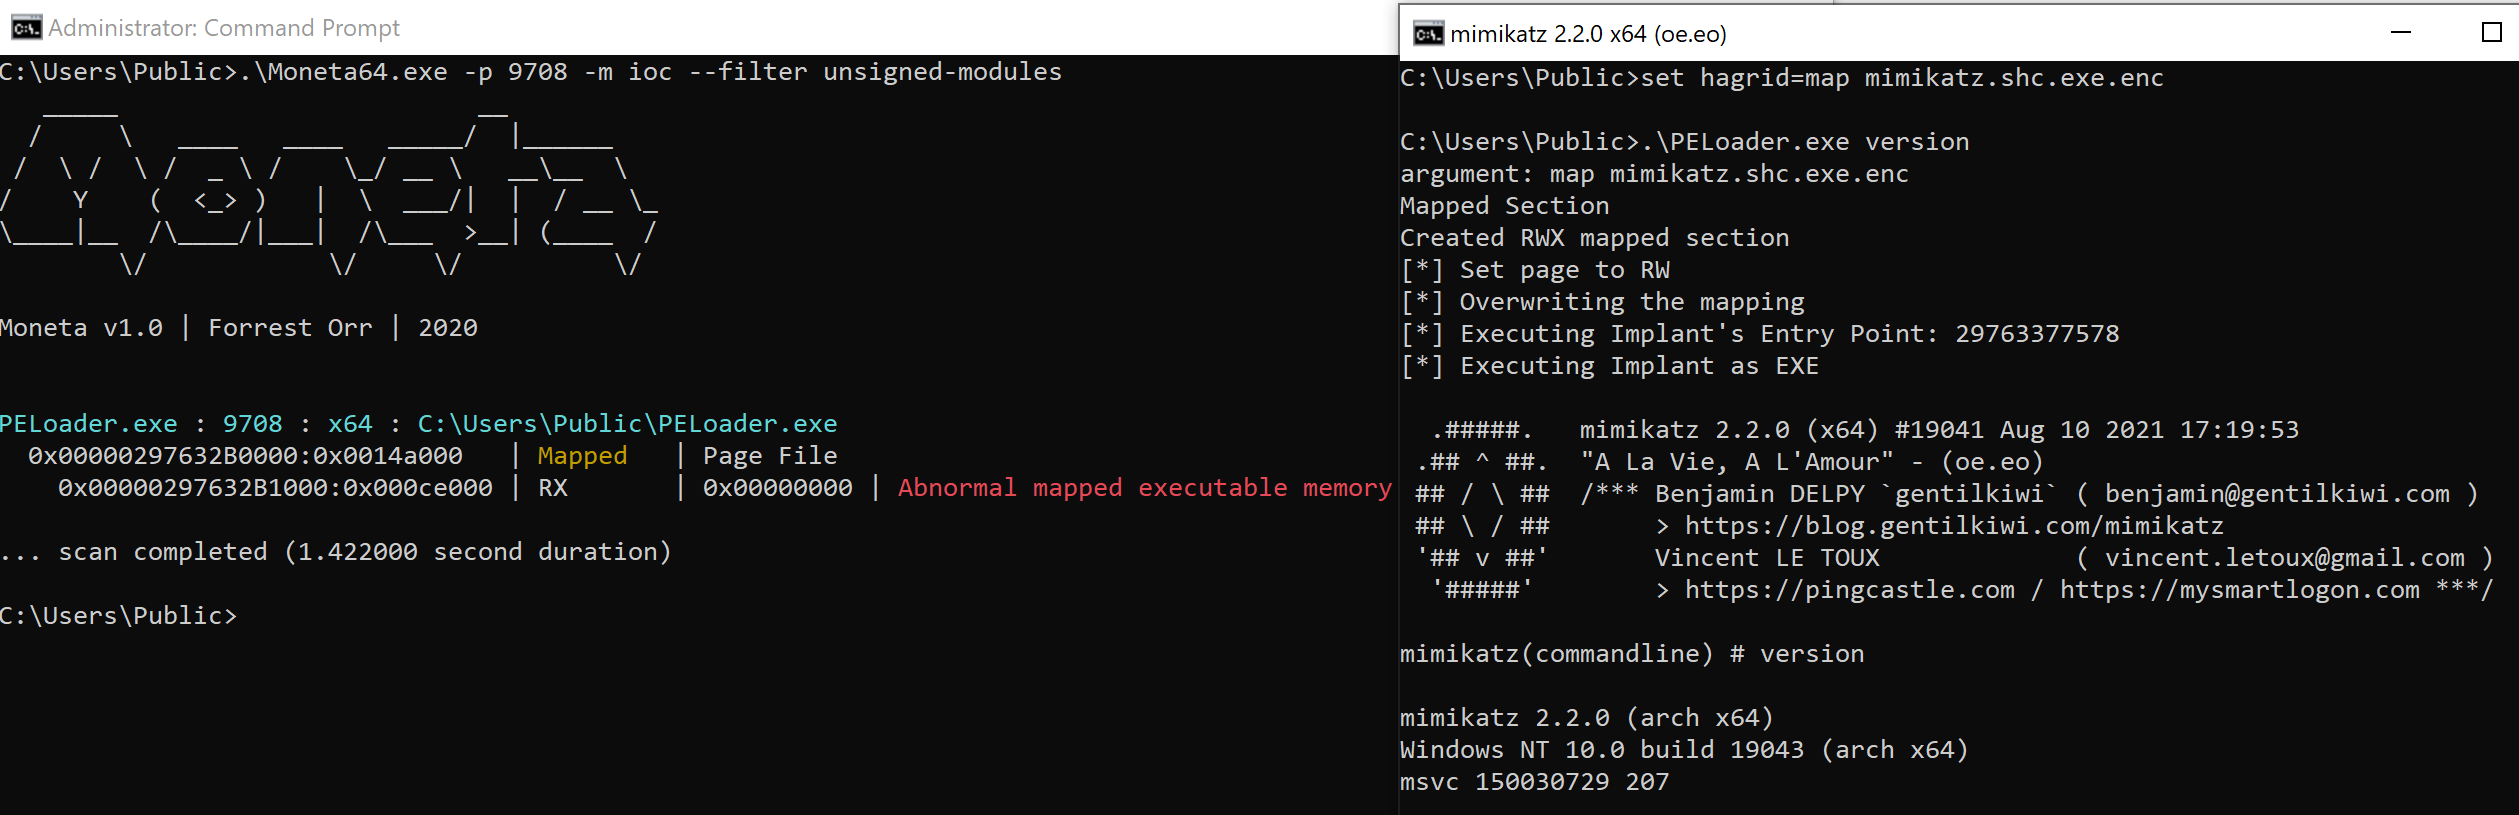 hagrid29/peloader
PE loader with various shellcode injection techniques
 jjyg/metasm
This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby
 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 0x00jeff/cve-2025-27591
self cleaning CVE-2025-27591 Poc that grants a root reverse shell instead of modifying passwd files
 epotseluevskaya/aspx_webshell_coffloader
ASPX web shell with COFF loader for executing Beacon Object Files (BOFs) on target servers via a semi-interactive Python client, designed for…
 spiralbl0ck/analysis-for-stage1-shellcode-loader-from-hacking-
Analysis for stage1 shellcode loader from hacking
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
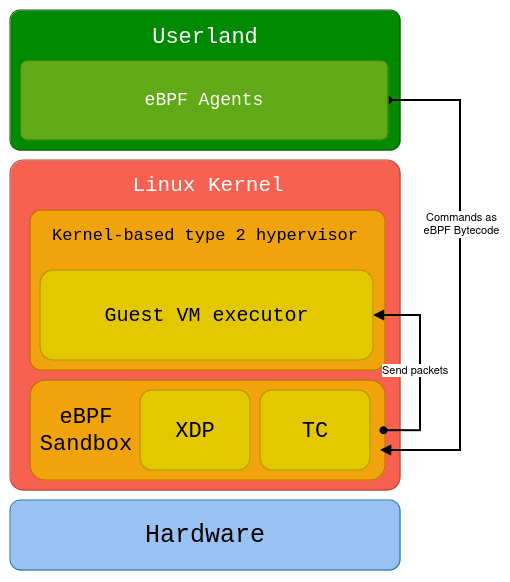 shard77/blackpill
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
 abq0/rwsploit
Automated exploitation scanner for Oracle Reports Server (rwservlet) — CVE-2012-3152 / CVE-2012-3153. Detects, fingerprints, reads files via LFI,…
 wireghoul/htshells
Self contained htaccess shells and attacks
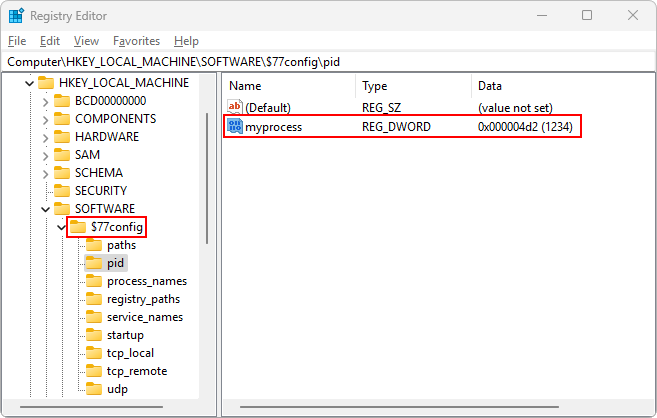 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
 frkngksl/shoggoth
Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
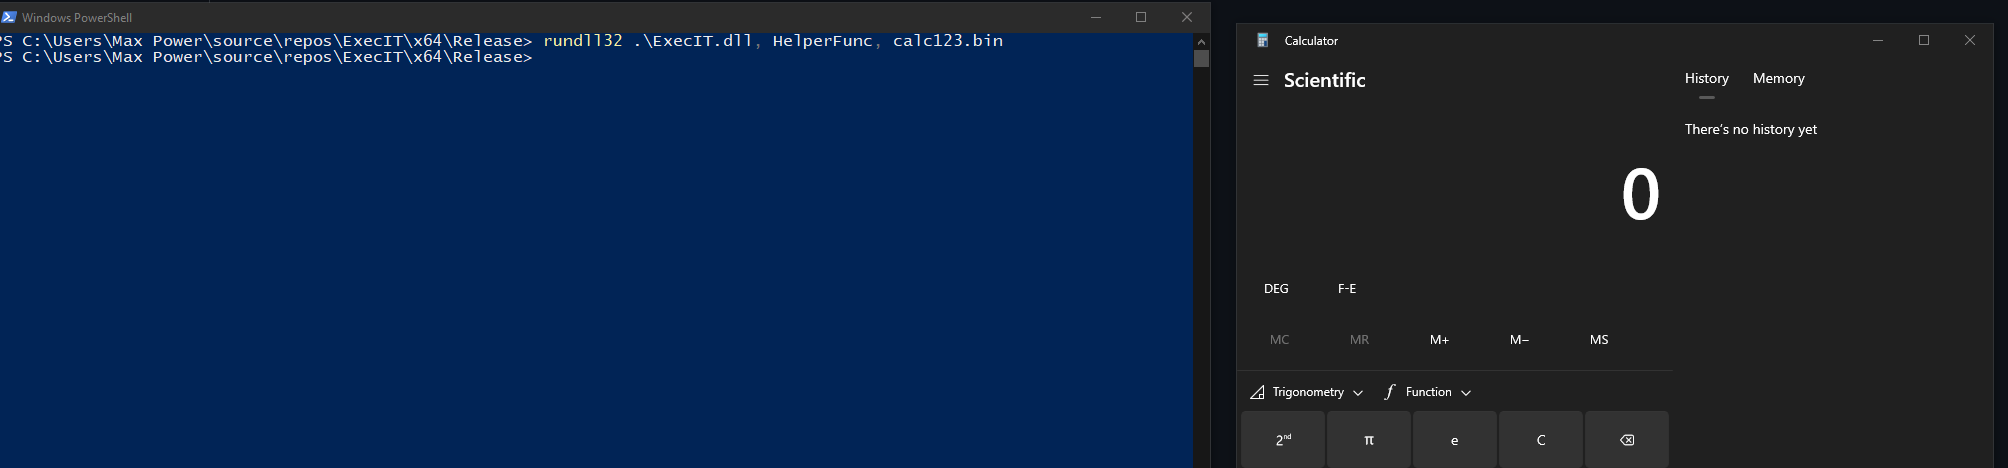 florylsk/execit
Execute shellcode files with rundll32
 encrypter15/cve-2025-50165-x64-exploit
Generates weaponized JPEG files exploiting CVE-2025-50165 (Windows Graphics RCE) with custom x64 shellcode, heap spray, ROP chain, and AV/EDR evasion…