

sRDI
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
exploitationids-ips-evasionmemory-forensics+7
monoxgas/srdiShellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
 jthuraisamy/syswhispers
AV/EDR evasion via direct system calls.
 jthuraisamy/syswhispers2
AV/EDR evasion via direct system calls.
 hasherezade/pe_to_shellcode
Converts PE into a shellcode
 egebalci/sgn
Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
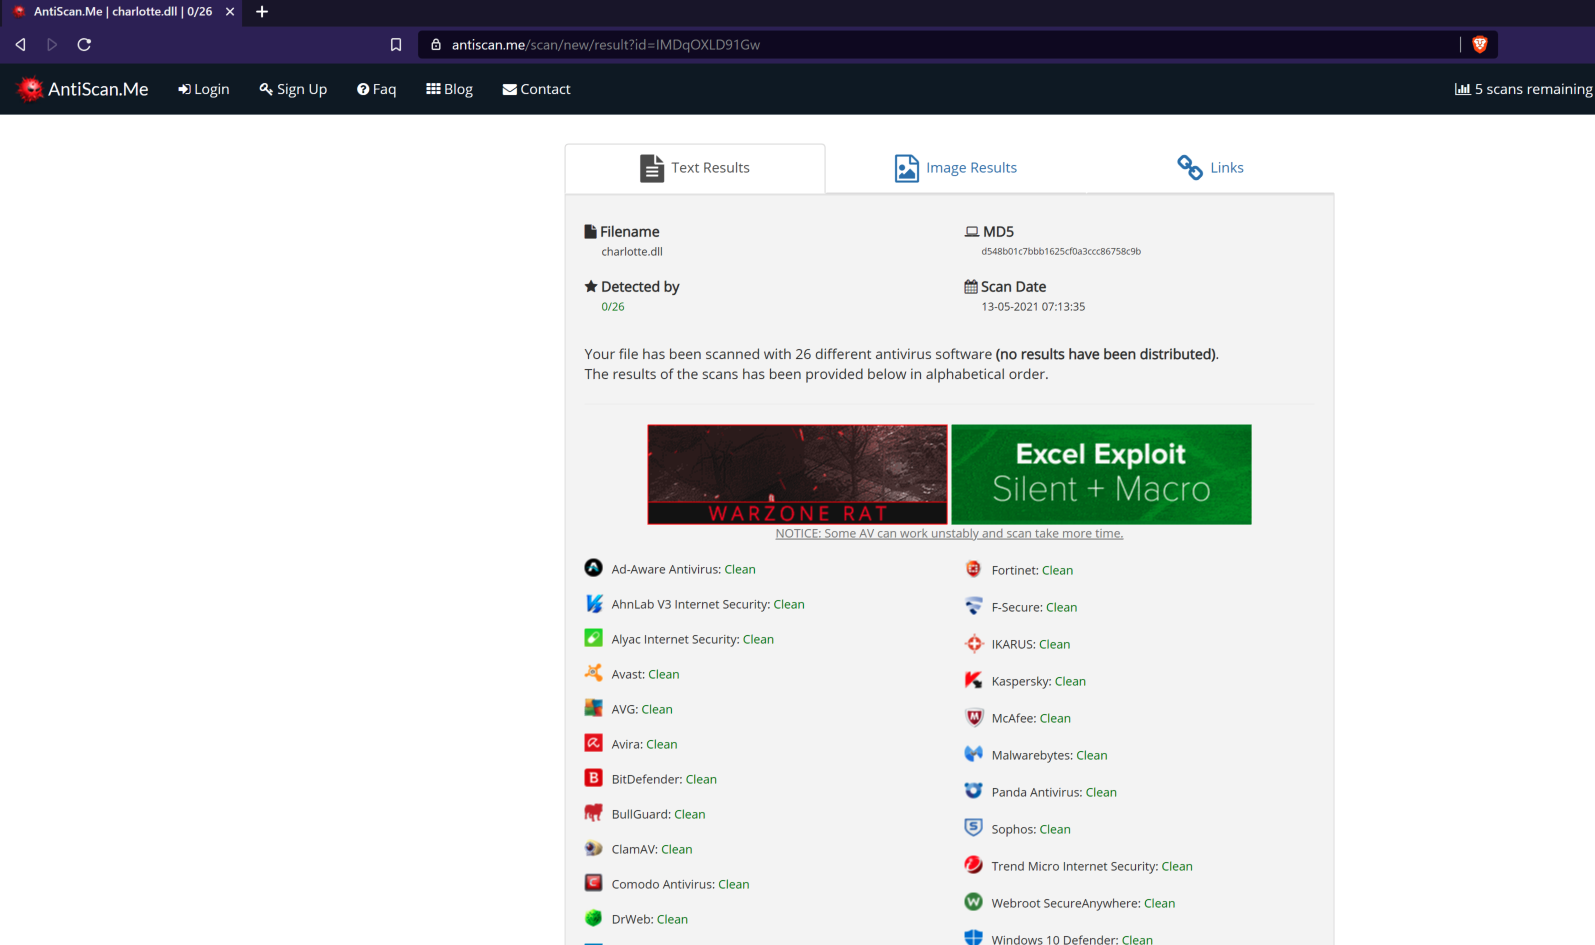 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
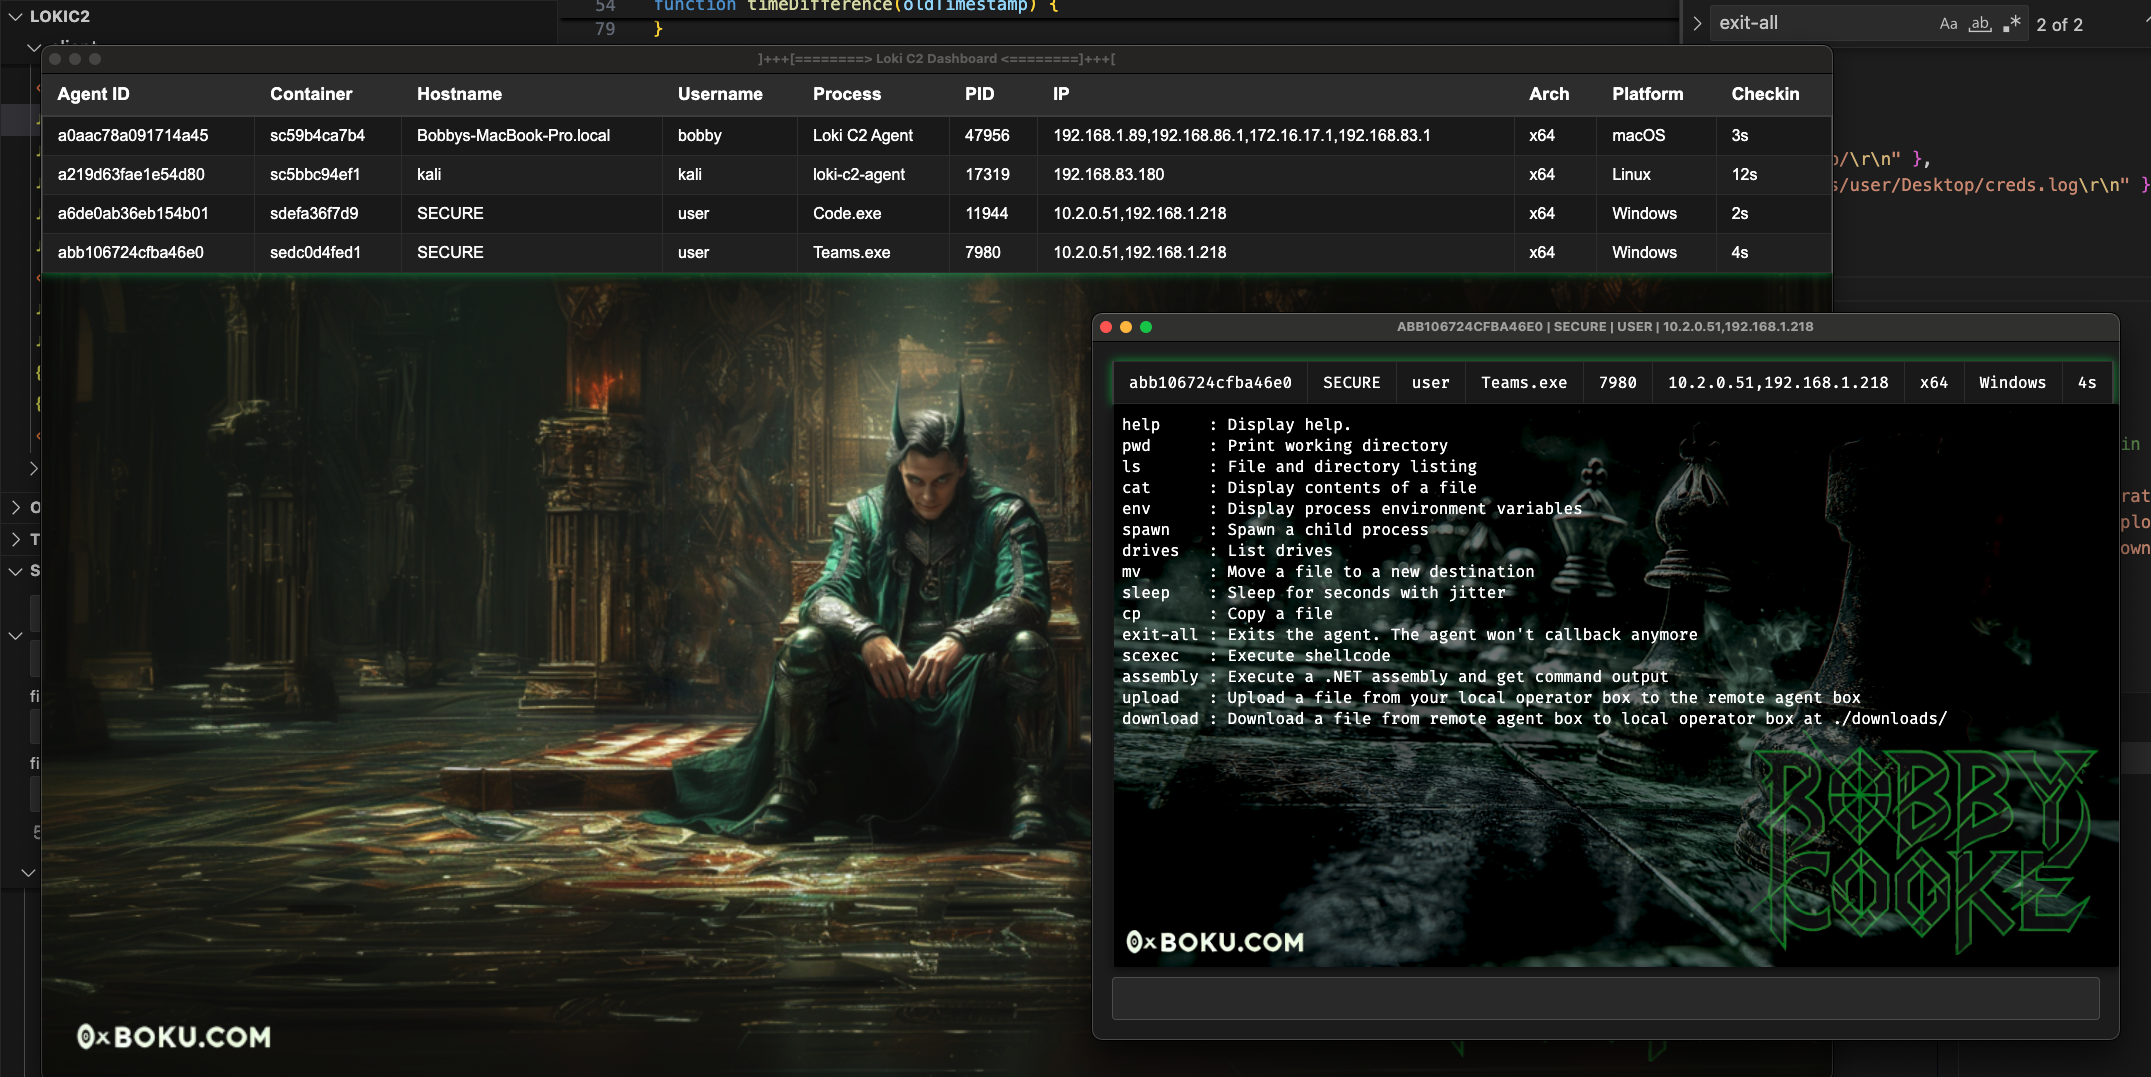 boku7/loki
🧙♂️ Node.js Command & Control for Script-Jacking Vulnerable Electron Applications
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
 kudaes/dinvoke_rs
Dynamically invoke arbitrary unmanaged code
 saadahla/d1rkldr
Shellcode Loader with Indirect Dynamic syscall Implementation , shellcode in MAC format, API resolving from PEB, Syscall calll and syscall…
 preemptdev/bluffy
Convert shellcode into :sparkles: different :sparkles: formats!
 0xninjacyclone/asmldr
Dynamic shellcode loader with sophisticated evasion capabilities
 solomonsklash/sleepycrypt
A shellcode function to encrypt a running process image when sleeping.