
Archived
CVE-2015-8522.RCE
 damariion/cve-2015-8522.rce
Exploit for CVE-2015-8522 targeting Tivoli FastBack Server with stack-based buffer overflow, ASLR/DEP bypass, and automated reverse-shell…
binary-exploitationexploitationexploit-frameworks+8
damariion/cve-2015-8522.rceExploit for CVE-2015-8522 targeting Tivoli FastBack Server with stack-based buffer overflow, ASLR/DEP bypass, and automated reverse-shell…
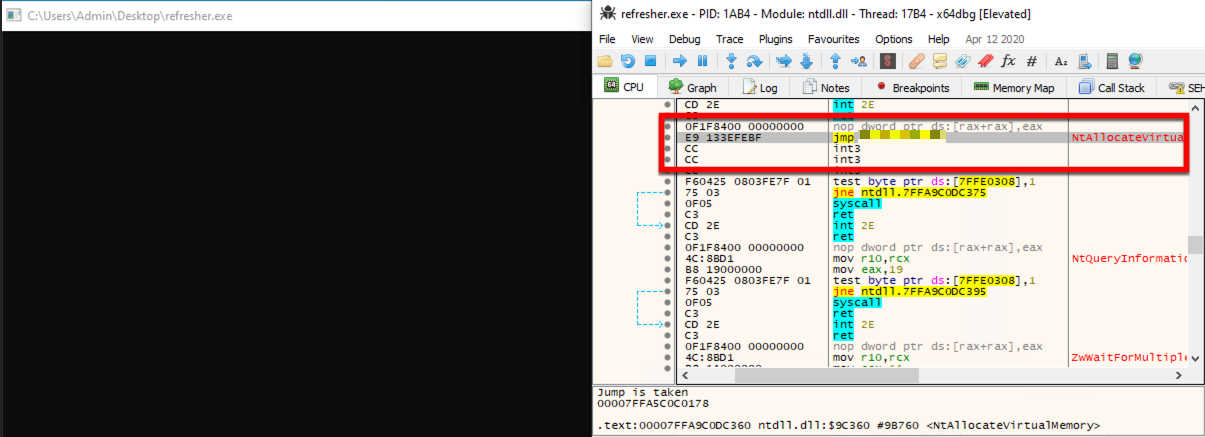 optiv/scarecrow
ScareCrow - Payload creation framework designed around EDR bypass.
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 gallopsled/pwntools
CTF framework and exploit development library
 bishopfox/sliver
Adversary Emulation Framework
 k8gege/k8tools
K8工具合集(内网渗透/提权工具/远程溢出/漏洞利用/扫描工具/密码破解/免杀工具/Exploit/APT/0day/Shellcode/Payload/priviledge/BypassUAC/OverFlow/WebShell/PenTest) Web GetShell…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 t3l3machus/villain
Villain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…
 mdsecactivebreach/sharpshooter
Payload Generation Framework

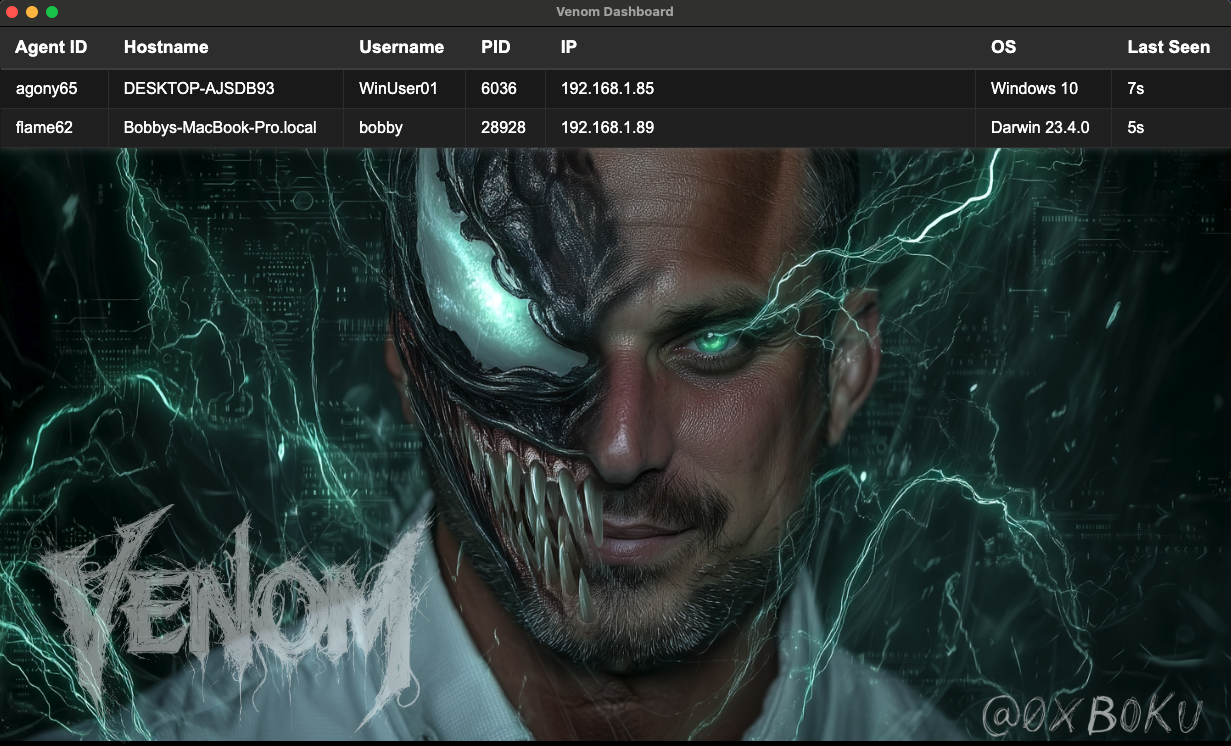 boku7/venom
Venom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence
 enkomio/alanframework
A C2 post-exploitation framework
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 s0lst1c3/dropengine
DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…
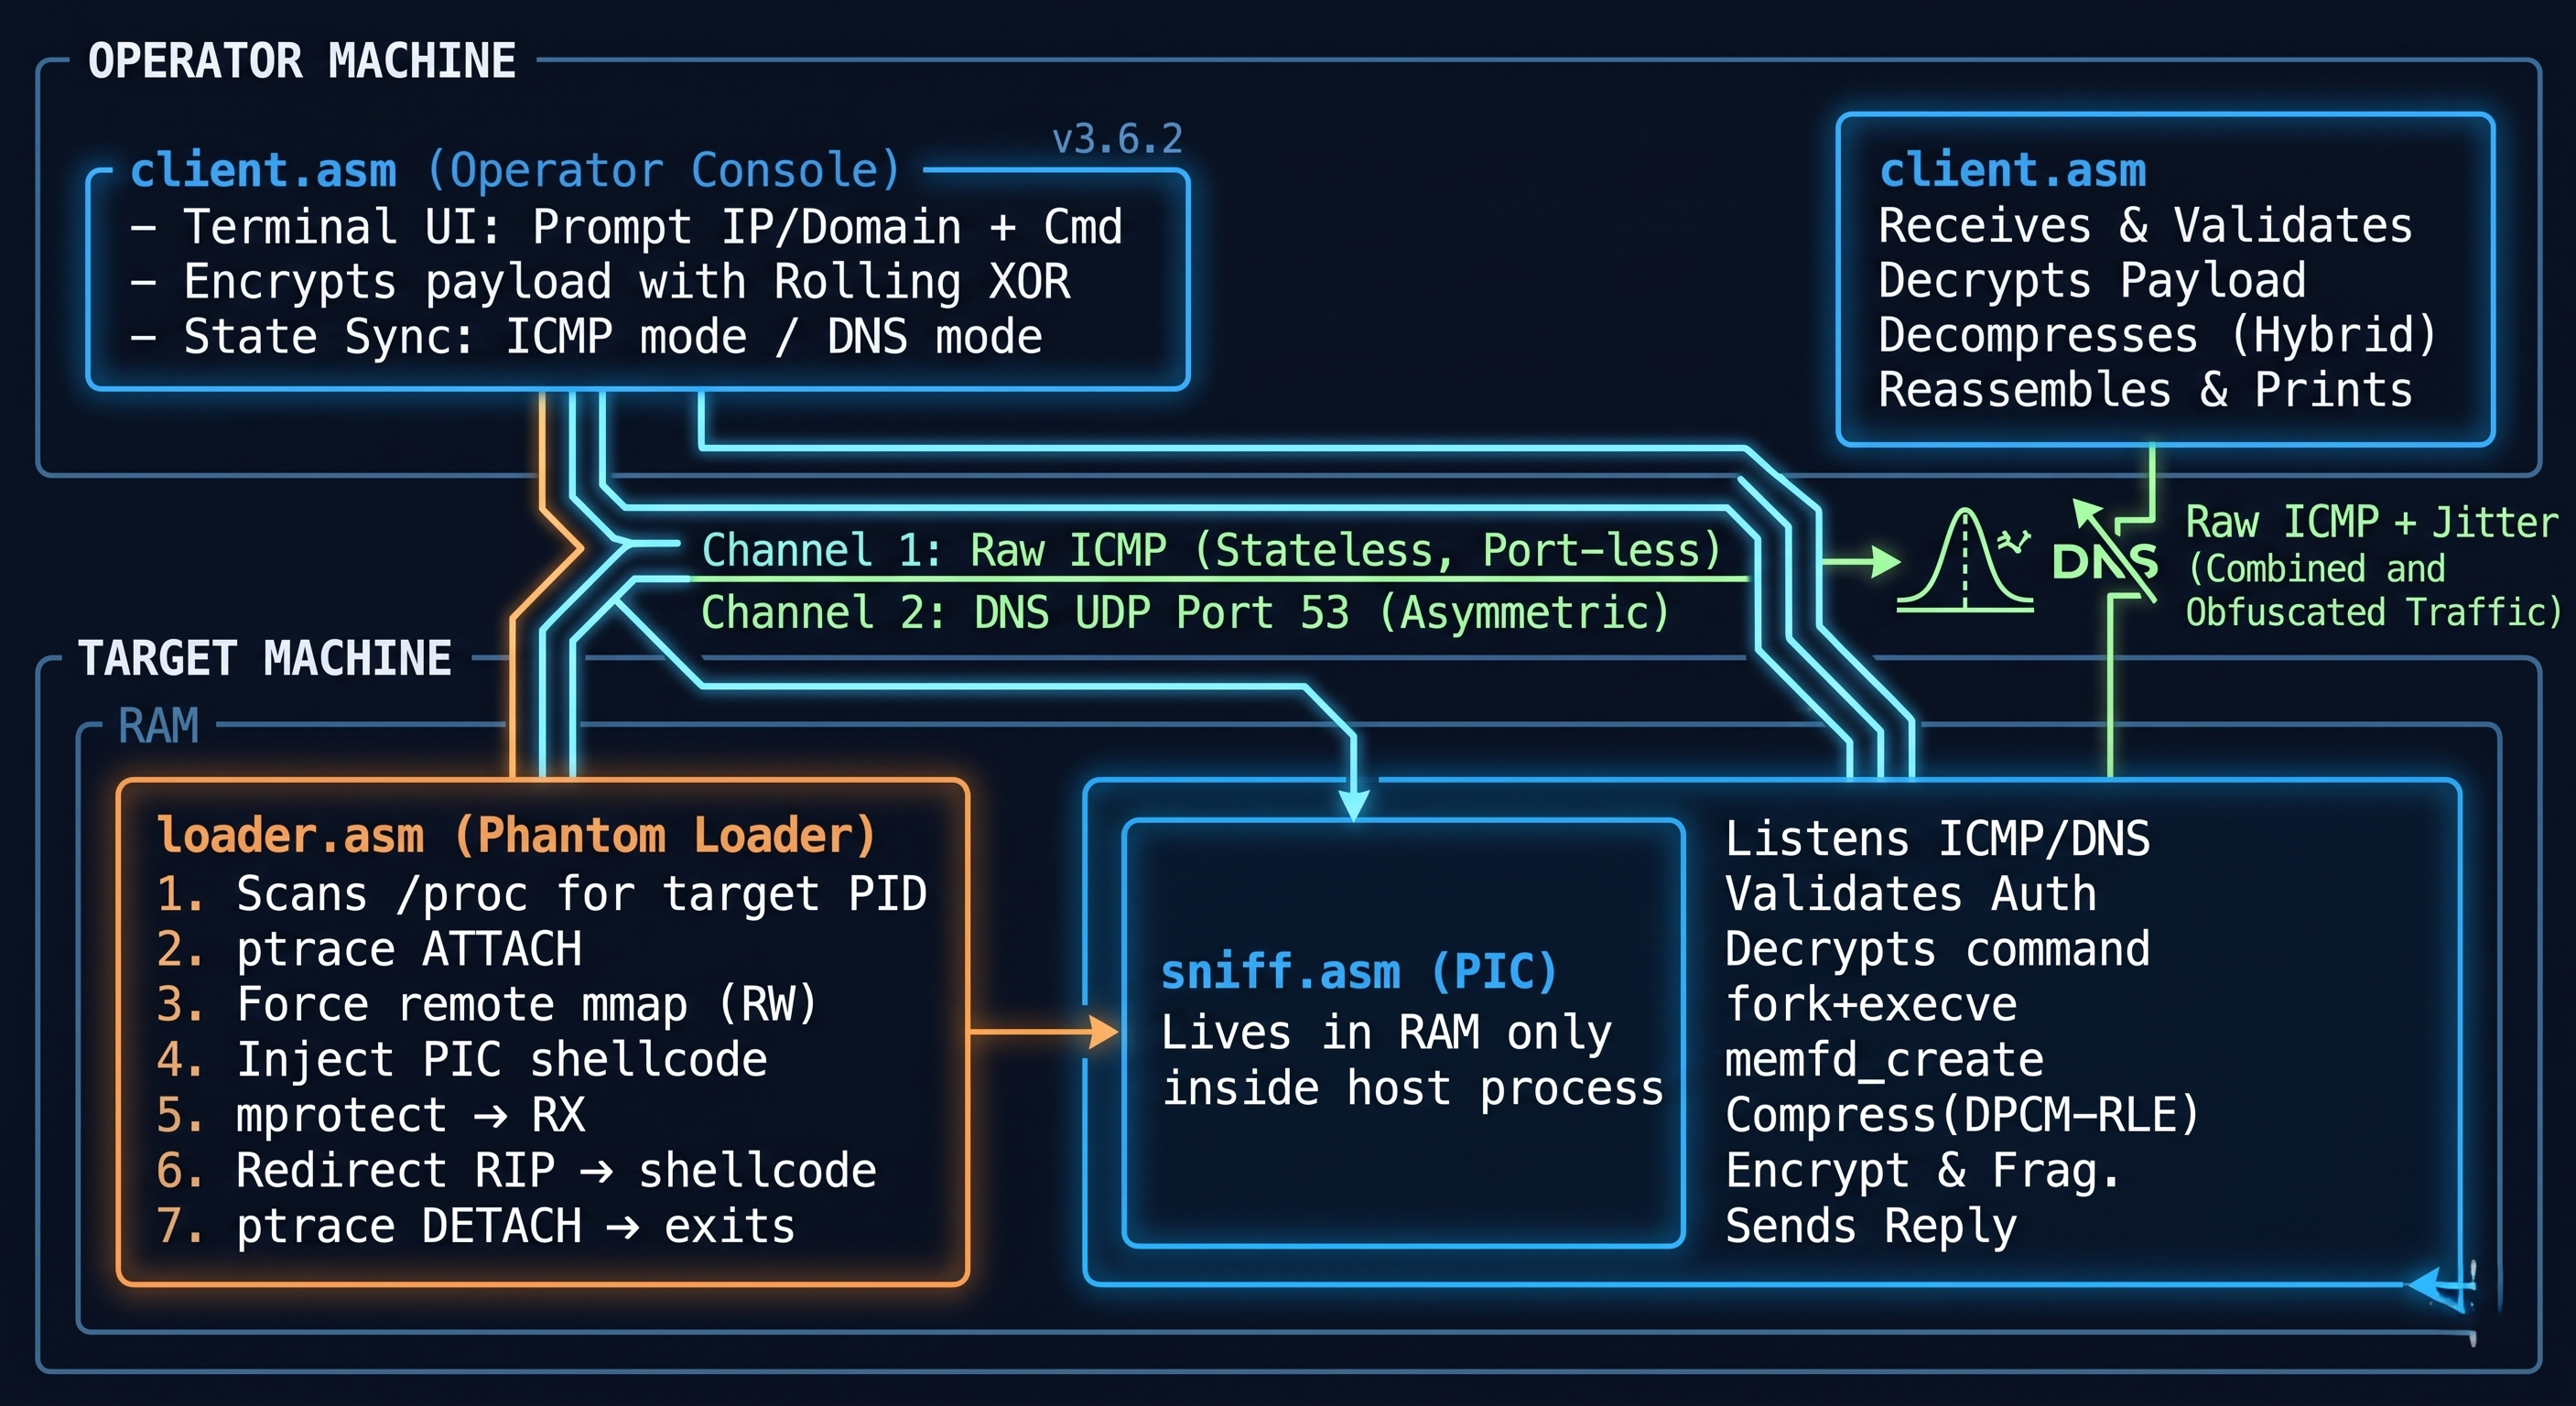 jm00nj/icmp-ghost-a-fileless-x64-assembly-c2-agent
Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…

 cerberusmrxi/wp-bricks-exploit-cve-2024-25600
CVE-2024-25600 - Unauthenticated RCE exploit for WordPress Bricks Builder Theme. Advanced exploitation framework with interactive shell, reverse…
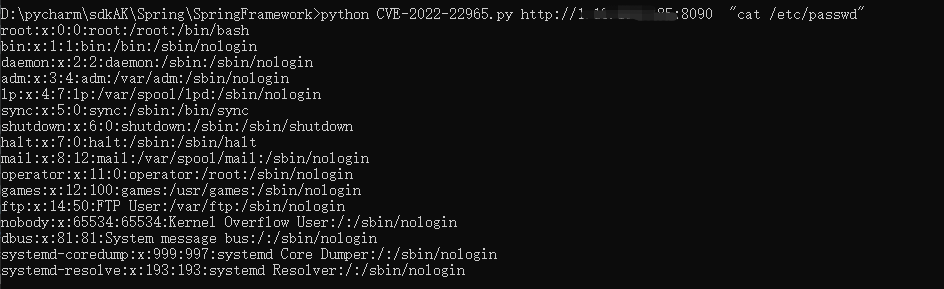 xsxtw/springframework_cve-2022-22965_rce
Python exploit for Spring Framework CVE-2022-22965 remote code execution with webshell deployment and Burp payload support for penetration testing.