
Archived
PowerSploit
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
lateral-movementpayload-generationpenetration-testing+5
13.1k
powershellmafia/powersploitPowerSploit - A PowerShell Post-Exploitation Framework
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
 optiv/mangle
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
 senzee1984/inflativeloading
Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.
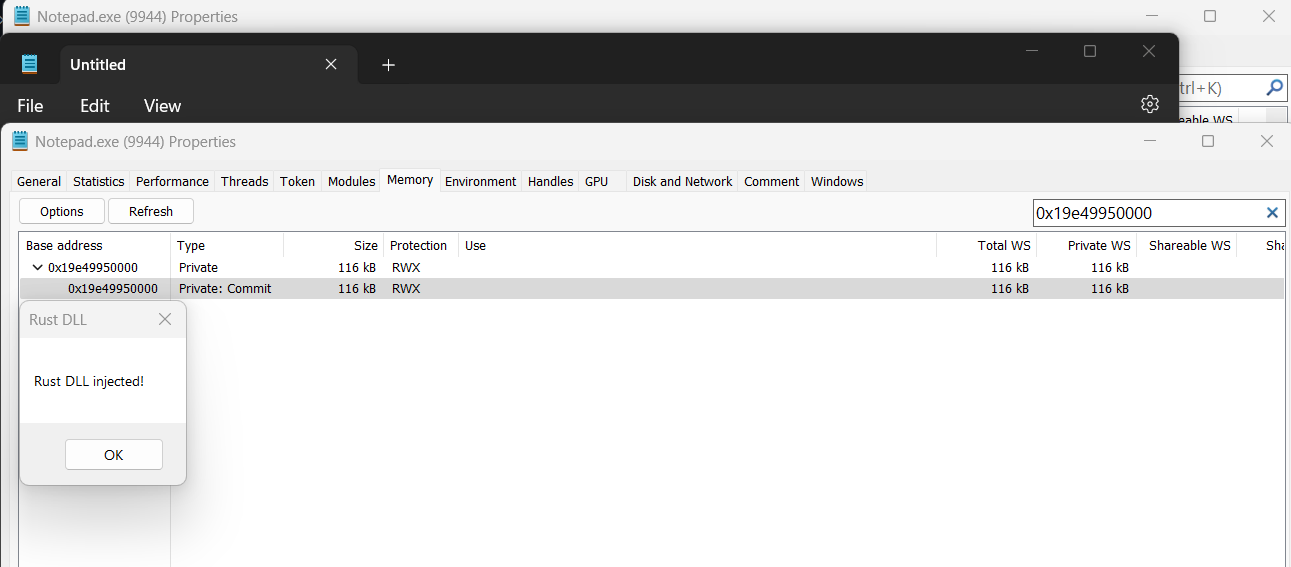 memn0ps/venom-rs
Rusty Injection - Shellcode Reflective DLL Injection (sRDI) in Rust (Codename: Venom)
 riftsandroses/cve-2024-50986
An issue in Clementine v.1.3.1 allows a local attacker to execute arbitrary code via a crafted DLL file (DLL Hijacking)
 enkomio/alanframework
A C2 post-exploitation framework
 georgesotiriadis/chimera
Automated DLL Sideloading Tool With EDR Evasion Capabilities
 dec0ne/dllnotificationinjection
A POC of a new “threadless” process injection technique that works by utilizing the concept of DLL Notification Callbacks in local and remote…
 aungsoepaing/cve-2024-39069
CVE-2024-39069
 egebalci/amber
Reflective PE packer.
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 kasturixbm5/staged-dll-injection-smb-
Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).
 bhassani/eternalbluec
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
 nhas/reverse_ssh
SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…
 cylancevulnresearch/reflectivedllrefresher
Reflective DLL that scans process memory and unhooks loaded libraries to evade security software, with UPX, TLS injector, and Meterpreter integration.