
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
31 results
Kernel_VADInjector preview

Kernel_VADInjector

GitHublleon1435/kernel_vadinjector

Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
adversarial-attackids-ips-evasionpayload-development+3
54
3 years ago
Mangle preview
Archived

Mangle

GitHuboptiv/mangle

Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
binary-analysisdefensive-toolsexploitation+6
1.2k3 years ago
Chimera preview

Chimera

GitHubgeorgesotiriadis/chimera

Automated DLL Sideloading Tool With EDR Evasion Capabilities
exploitationpayload-generationred-teaming+1
5102 years ago
PowerSploit preview
Archived

PowerSploit

GitHubpowershellmafia/powersploit

PowerSploit - A PowerShell Post-Exploitation Framework
lateral-movementpayload-generationpenetration-testing+5
13.1k6 years ago
InflativeLoading preview

InflativeLoading

GitHubsenzee1984/inflativeloading

Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.
binary-exploitationexploitationmalware-analysis+3
3262 years ago
VectoredOverloading preview

VectoredOverloading

GitHubcheckpointsw/vectoredoverloading

Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…

binary-exploitationexploitationmalware-analysis+6
12510 months ago
sRDI preview

sRDI

GitHubmonoxgas/srdi

Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
exploitationids-ips-evasionmemory-forensics+7
2.6k4 years ago
venom-rs preview
Archived

venom-rs

GitHubmemn0ps/venom-rs

Rusty Injection - Shellcode Reflective DLL Injection (sRDI) in Rust (Codename: Venom)
payload-developmentpost-exploitationred-teaming+2
3682 years ago
CVE-2024-50986 preview

CVE-2024-50986

GitHubriftsandroses/cve-2024-50986

An issue in Clementine v.1.3.1 allows a local attacker to execute arbitrary code via a crafted DLL file (DLL Hijacking)

binary-exploitationexploitationpayload-generation+4
1 year ago
reverse_ssh preview

reverse_ssh

GitHubnhas/reverse_ssh

SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…

shellcodeshellcode-generation
1.5k1 month ago
ReflectiveDLLRefresher preview

ReflectiveDLLRefresher

GitHubcylancevulnresearch/reflectivedllrefresher

Reflective DLL that scans process memory and unhooks loaded libraries to evade security software, with UPX, TLS injector, and Meterpreter integration.
ids-ips-evasionmalware-analysispayload-development+6
3248 years ago
ExecIT preview

ExecIT

GitHubflorylsk/execit

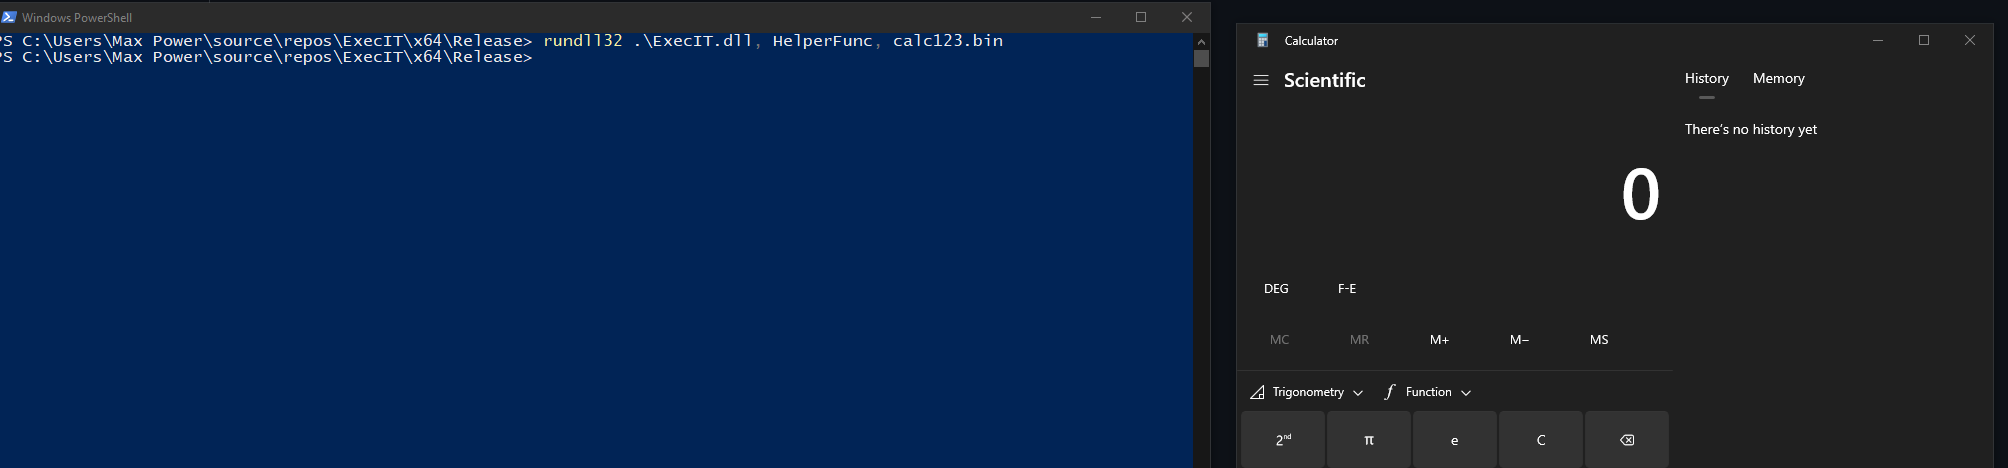
Execute shellcode files with rundll32
ids-ips-evasionmalware-analysispayload-development+4
2292 years ago
AlanFramework preview

AlanFramework

GitHubenkomio/alanframework

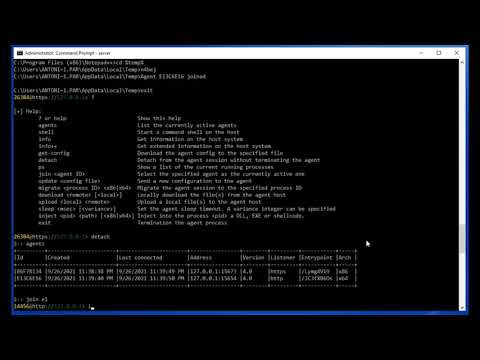
A C2 post-exploitation framework
command-and-controlencryption-decryption-toolslateral-movement+7
4872 years ago
PMD preview

PMD

GitHubrad9800/pmd

Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.
binary-analysiseducationlabs-practice+6
1571 year ago
artifacts-kit preview

artifacts-kit

GitHubforrest-orr/artifacts-kit

Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
exploitationforensicsmalware-analysis+5
2302 years ago
PELoader preview

PELoader

GitHubhagrid29/peloader

PE loader with various shellcode injection techniques
binary-analysisexploitationmalware-analysis+4
4654 years ago
exe_to_dll preview

exe_to_dll

GitHubhasherezade/exe_to_dll

Converts a EXE into DLL
binary-analysisbinary-exploitationpayload-generation+2
1.4k1 year ago
DllNotificationInjection preview

DllNotificationInjection

GitHubdec0ne/dllnotificationinjection

A POC of a new “threadless” process injection technique that works by utilizing the concept of DLL Notification Callbacks in local and remote…

exploitationred-teamingshellcode
4693 years ago
Previous12Next