
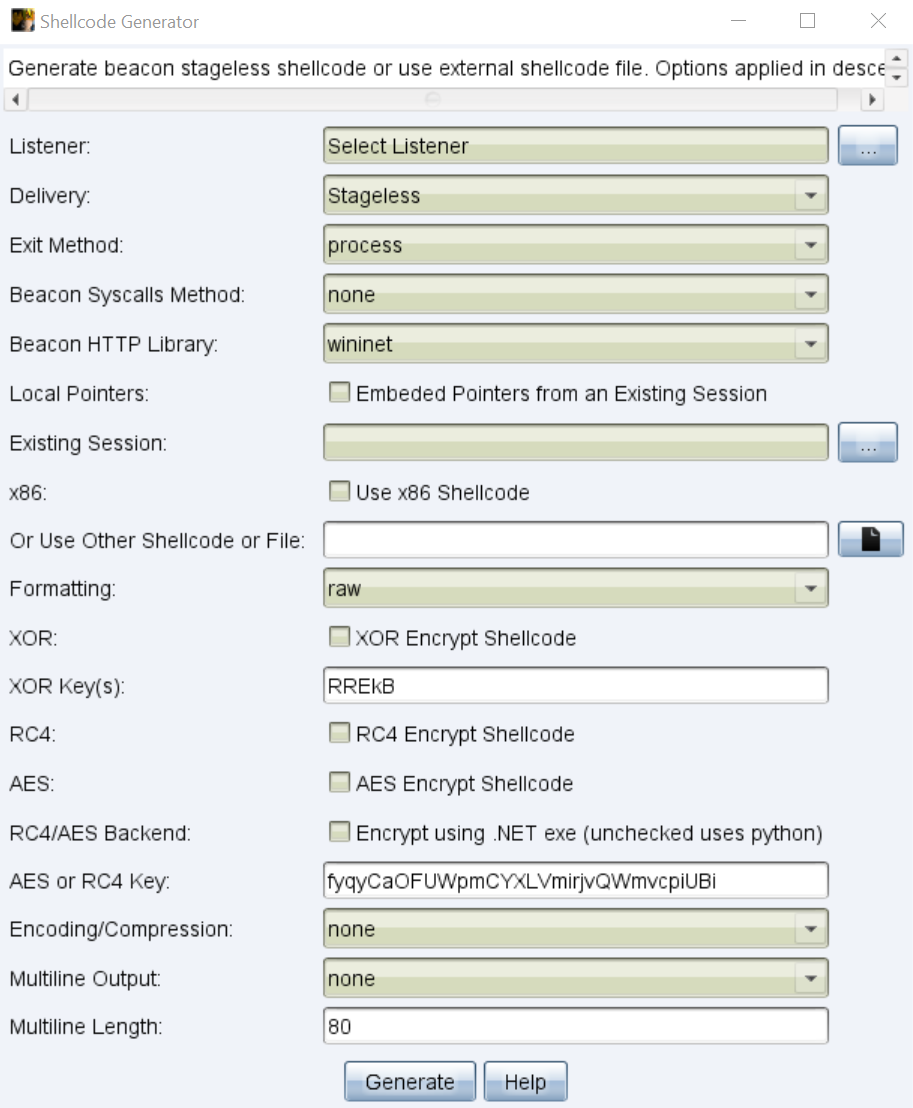
CSSG
 rcstep/cssg
Cobalt Strike aggressor script for generating, formatting, and encrypting beacon shellcode with support for multiple exit methods, syscalls, and…
encryption-decryption-toolsexploit-frameworkspayload-generation+2
666
rcstep/cssgCobalt Strike aggressor script for generating, formatting, and encrypting beacon shellcode with support for multiple exit methods, syscalls, and…
 bkreisel/cve-2022-41343
🐍 Python Exploit for CVE-2022-23935
 bkreisel/cve-2022-46169
🐍 Python Exploit for CVE-2022-46169
 redsiege/excelntdonut
Excel 4.0 (XLM) Macro Generator for injecting DLLs and EXEs into memory.
 thecybergeek/cve-2020-5844
Python proof-of-concept for authenticated remote code execution in PandoraFMS 7.0-NG 742, enabling admin users to upload malicious PHP and obtain a…
 0xm4ud/nosambanocry-cve-2017-7494
CVE-2017-7494 python exploit
 ivanitlearning/cve-2018-12613
Modified standalone exploit ported for Python 3
 randallbanner/spring-cloud-function-vulnerability-cve-2022-22963-rce
Python exploit for CVE-2022-22963 (Spring4Shell) targeting Spring Cloud Function RCE. Automates reverse shell delivery via wget and bash one-liner…
 cowsecurity/cve-2011-2523
Python exploit for vsFTPd backdoor vulnerability (CVE-2011-2523) using Pwntools for remote code execution against target IP and port.
 h3rm1tr3b0rn/cve-2020-8644-playsms-1.4
Python script to exploit PlaySMS before 1.4.3
 schn1tzelme1ster/cve-2025-6002
Python exploit for CVE-2025-6002 targeting authenticated arbitrary file upload in VirtueMart < 4.4.10. Logs in, uploads a PHP webshell, and triggers…
 3x1t1um/cve-2007-2447
Python exploit for CVE-2007-2447 that triggers Samba username map script command injection to open a reverse shell on vulnerable targets.
 kai-one001/wordpress-ht-contact-cve-2025-7340-rce
Python exploit for CVE-2025-7340, an unauthenticated file upload vulnerability in the WordPress HT Contact Form widget, enabling remote code…
 h3x0v3rl0rd/cve-2022-41544
Python exploit script for CVE-2022-41544 in GetSimple CMS. Automates API key leakage, CSRF token extraction, PHP shell upload, and reverse shell…
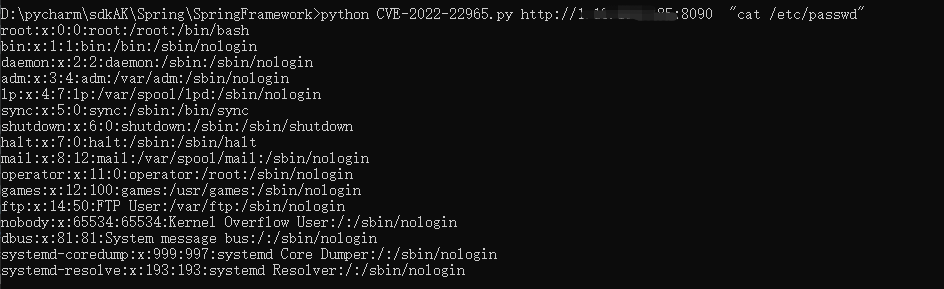 xsxtw/springframework_cve-2022-22965_rce
Python exploit for Spring Framework CVE-2022-22965 remote code execution with webshell deployment and Burp payload support for penetration testing.
 substing/cve-2019-11447_reverse_shell_upload
Python exploit for CVE-2019-11447 that uploads a PHP reverse shell to CuteNews 2.1.2, enabling remote command execution on vulnerable web…
 lowkey0808/cve-2022-29464
Python exploit for CVE-2022-29464 targeting WSO2 web servers with automated webshell upload and command execution capabilities.
 charchit-subedi/chamilo-lms-unauthenticated-rce-poc
This is a script written in Python that allows the exploitation of the Chamilo's LMS software security flaw described in CVE-2023-4220