Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
362 results
CVE-2019-5782_CVE-2019-13768 preview

CVE-2019-5782_CVE-2019-13768

GitHubedxsh/cve-2019-5782_cve-2019-13768

Full-chain Chrome exploit targeting CVE-2019-5782 and CVE-2019-13768 with custom ROP gadgets and shellcode for arbitrary command execution on Windows…

binary-exploitationexploitationpayload-development+3
21
5 years ago
CVE-2017-14980_syncbreeze_10.0.28_bof preview

CVE-2017-14980_syncbreeze_10.0.28_bof

GitHublipeozyy/cve-2017-14980_syncbreeze_10.0.28_bof

Proof-of-concept buffer overflow exploit for Sync Breeze Enterprise v10.0.28 (CVE-2017-14980). Sends crafted HTTP POST payload to overwrite EIP and…

binary-exploitationexploitationpayload-generation+4
21 year ago
CVE-2023-3519 preview

CVE-2023-3519

GitHubpasswa11/cve-2023-3519

Python exploit for CVE-2023-3519 targeting Citrix ADC with custom NASM shellcode, PHP backdoor deployment, and SUID privilege escalation.

exploitationpayload-developmentremote-access-tool+3
13 years ago
CVE-2017-7494 preview

CVE-2017-7494

GitHubincredible1yu/cve-2017-7494

C exploit for CVE-2017-7494 (Samba is_known_pipename) with custom shared object compilation and reverse shell payload generation.

binary-exploitationexploitationpayload-development+3
8 years ago
libpeconv preview

libpeconv

GitHubhasherezade/libpeconv

Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…

binary-analysismalware-analysismemory-forensics+4
1.4k5 months ago
sharem preview

sharem

GitHubbw3ll/sharem

SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…

ai-securitybinary-analysisdebuggers+5
4936 months ago
Shellcode-Hide preview

Shellcode-Hide

GitHubsaadahla/shellcode-hide

This repo contains : simple shellcode Loader , Encoders (base64 - custom - UUID - IPv4 - MAC), Encryptors (AES), Fileless Loader (Winhttp, socket)

cryptographyencryption-decryption-toolsids-ips-evasion+4
4393 years ago
TinyLoad preview

TinyLoad

GitHubiamsopotatoe-coder/tinyload

Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.

binary-analysisencryption-decryption-toolsexploitation+5
19229 days ago
CustomC2ChannelTemplate preview

CustomC2ChannelTemplate

GitHubcodextf2/customc2channeltemplate

template for developing custom C2 channels for Cobalt Strike using IAT hooks applied by a reflective loader.

command-and-controlexploit-frameworkspayload-development+3
1068 months ago
windows-x86-shellcode-poc preview

windows-x86-shellcode-poc

GitHubnataliadiak/windows-x86-shellcode-poc

Windows x86 PoC: Stack‑based buffer overflow with custom shellcode on legacy 32-bit Windows.

binary-exploitationeducationpayload-development+3
84 months ago
CVE-2024-0311 preview

CVE-2024-0311

GitHubcalligraf0/cve-2024-0311

Proof-of-concept exploit for CVE-2024-0311 bypassing Skyhigh Client Proxy policy via process injection and named pipe manipulation, with custom…

binary-exploitationexploitationids-ips-evasion+4
91 year ago
CVE-2025-50165-x64-Exploit preview

CVE-2025-50165-x64-Exploit

GitHubencrypter15/cve-2025-50165-x64-exploit

Generates weaponized JPEG files exploiting CVE-2025-50165 (Windows Graphics RCE) with custom x64 shellcode, heap spray, ROP chain, and AV/EDR evasion…

binary-exploitationexploitationids-ips-evasion+5
79 months ago
Ascii-And-Sub-Encoder preview

Ascii-And-Sub-Encoder

GitHubxen0vas/ascii-and-sub-encoder

This is a custom ASCII AND/SUB Encoder developed during my preparation for the legacy OSCE/CTP course

binary-exploitationeducationexploitation+2
4 years ago
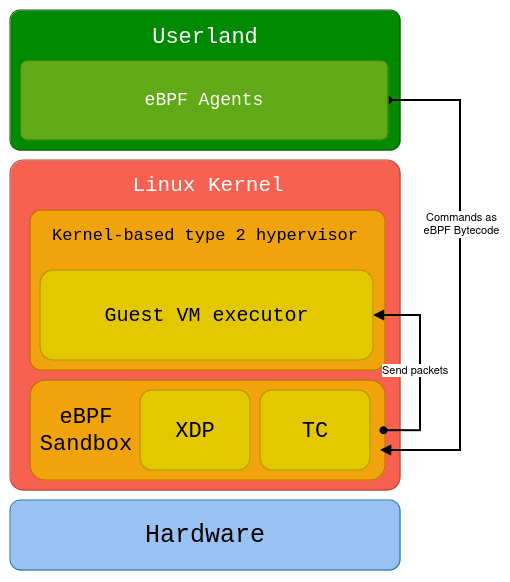
blackpill preview
Archived

blackpill

GitHubshard77/blackpill

A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs

binary-exploitationcommand-and-controlids-ips-evasion+7
3397 months ago
Foxit-Reader-RCE-with-virualalloc-and-shellcode-for-CVE-2018-9948-and-CVE-2018-9958 preview

Foxit-Reader-RCE-with-virualalloc-and-shellcode-for-CVE-2018-9948-and-CVE-2018-9958

GitHubmanojcode/foxit-reader-rce-with-virualalloc-and-shellcode-for-cve-2018-9948-and-cve-2018-9958

Foxit Reader version 9.0.1.1049 Use After Free with ASLR and DEP bypass on heap

binary-exploitationexploitationpayload-development+3
68 years ago
CVE-2025-43990-Magento-RCE preview

CVE-2025-43990-Magento-RCE

GitHubamkkk221/cve-2025-43990-magento-rce

Magento APSB25-94 Unauthenticated File Upload to RCE (CVE-2026-XXXX) - Eval Shell + Probe Scanner

exploitationpayload-generationpenetration-testing+4
5 months ago
Maverick preview

Maverick

GitHubblacksnufkin/maverick

Adaptix C2 agent using Crystal Palace PIC linker and PICO module system

binary-analysiscommand-and-controlencryption-decryption-tools+5
1183 months ago
CVE-2016-6187_LPE preview

CVE-2016-6187_LPE

GitHubmilo-d/cve-2016-6187_lpe

Kernel Exploit for CVE-2016-6187 (Local Privilege Escalation)

binary-exploitationexploitationprivilege-escalation+1
72 years ago
Previous12…21Next