gef
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
ai-assisted-reversingbinary-analysisbinary-exploitation+10
8.4k
hugsy/gefGEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 x0reaxeax/exec-prot-bypass
Bypassing Linux Executable Space Protection using 20+ years old tools (CVE-2022-25265).
 0x00pf/0x00sec_code
Educational repository of offensive security source code: remote shells, ELF injectors, crypters, memory injection, and droppers for Linux,…
 dullpurple-sloop726/cve-2026-31431-linux-copy-fail
Exploit CVE-2026-31431 on Linux using a Rust implementation to achieve local privilege escalation via an arbitrary page cache write primitive.
 4xura/cve-2026-31431-copy-fail
Research artifacts, PoC scripts, and lab assets for the Copy Fail Linux local privilege escalation writeup on https://4xura.com/binex/kernel/copy-fail
 bytereaper77/dirty-pipe
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe) enabling local privilege escalation on Linux kernels 5.8–5.16 via pipe buffer manipulation…
 kkirsche/slae
SecurityTube Linux Assembly Expert x86 Exam
 gbonacini/cve-2026-31431
Standalone C++/x86-64 assembly implementation of CVE-2026-31431 (Copyfail) for local privilege escalation. Compiles to a dependency-free binary that…
 gallopsled/pwntools
CTF framework and exploit development library
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
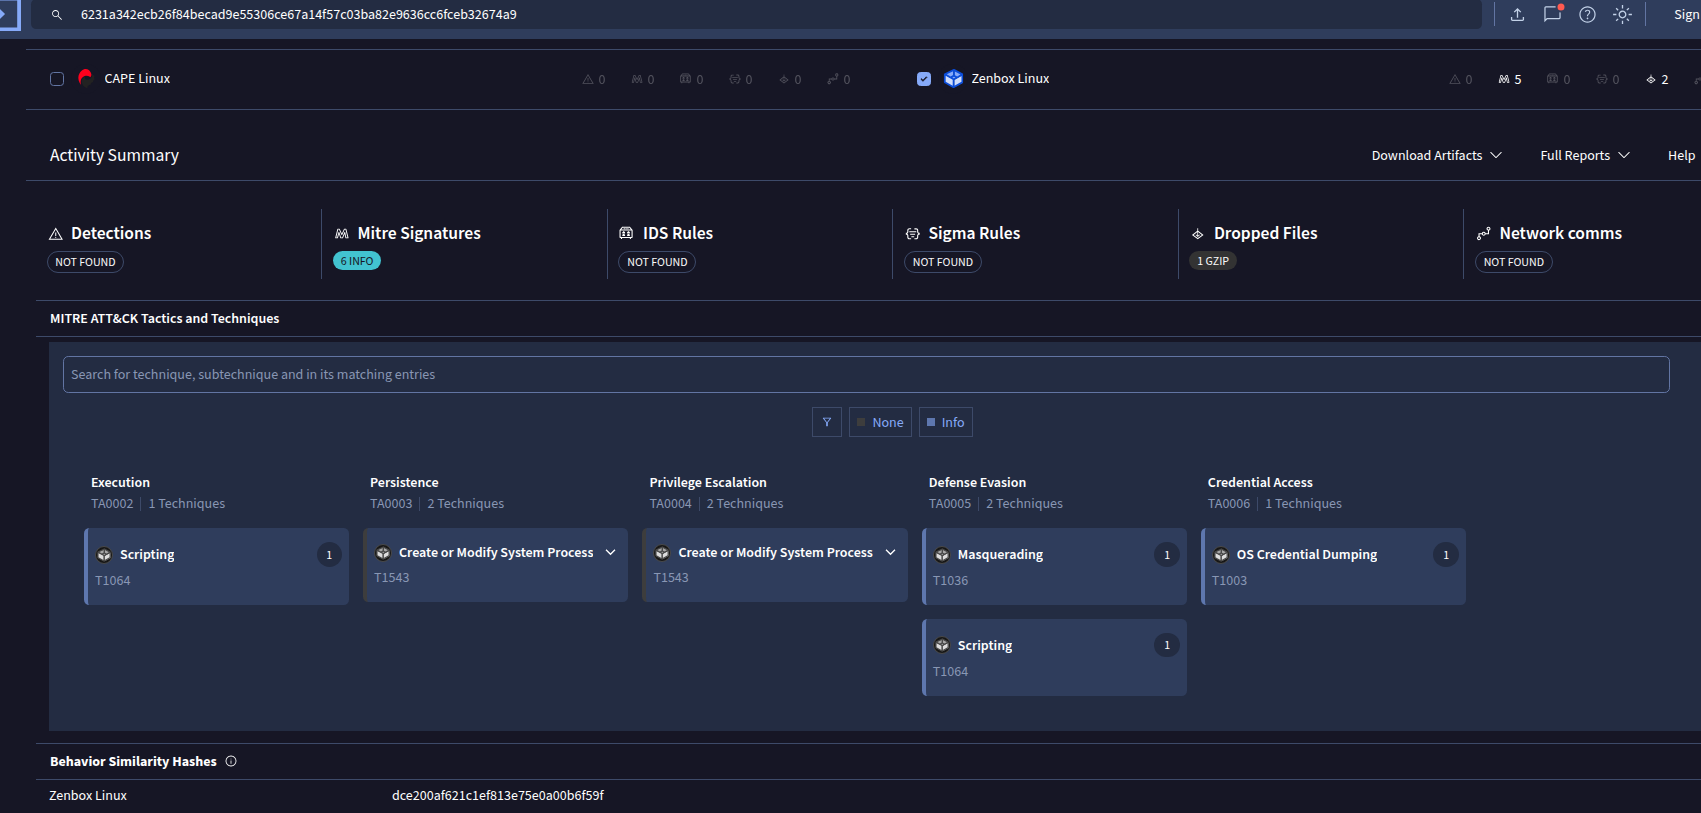 jm00nj/phantom-evasion-loader
x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…
 0xdea/shellcode
A collection of my shellcode samples.
 cyb3r-techie/pezor-docker
With the help of this docker image, you can easily access PEzor on your system!
 jarpex/cve-2023-4911-exploit-optimized
Pure C exploit for CVE-2023-4911 (Looney Tunables) — x86_64 & aarch64 implementations. Multi-processing brute-forcing, dynamic calibration,…
 sudoytang/copyfail-arm64
Analysis and ARM64 reproduction of Copy Fail (CVE-2026-31431)