
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
165 results
gmailc2 preview

gmailc2

GitHubmachine1337/gmailc2

A Fully Undetectable C2 Server That Communicates Via Google SMTP to evade Antivirus Protections and Network Traffic Restrictions
command-and-controleducationpayload-generation+4
489
1 year ago
Sandman preview

Sandman

GitHubidov31/sandman

NTP-based backdoor for hardened networks, delivering and executing arbitrary shellcode via spoofed NTP traffic with optional persistence as a Windows…

command-and-controlpayload-generationpersistence-mechanisms+2
8193 years ago
hershell preview

hershell

GitHublesnuages/hershell

Multiplatform reverse shell generator
command-and-controlencryption-decryption-toolsexploitation+6
5926 years ago
SMBRat preview

SMBRat

GitHuboperatorequals/smbrat

A Windows Remote Administration Tool in Visual Basic with UNC paths

command-and-controlexploitationlateral-movement+8
227 years ago
Villain preview

Villain

GitHubt3l3machus/villain

Villain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…
command-and-controlexploit-frameworkspayload-generation+4
4.5k1 year ago
AlanFramework preview

AlanFramework

GitHubenkomio/alanframework

A C2 post-exploitation framework

command-and-controlencryption-decryption-toolslateral-movement+7
4852 years ago
Maverick preview

Maverick

GitHubblacksnufkin/maverick

Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
binary-analysiscommand-and-controlencryption-decryption-tools+5
1204 months ago
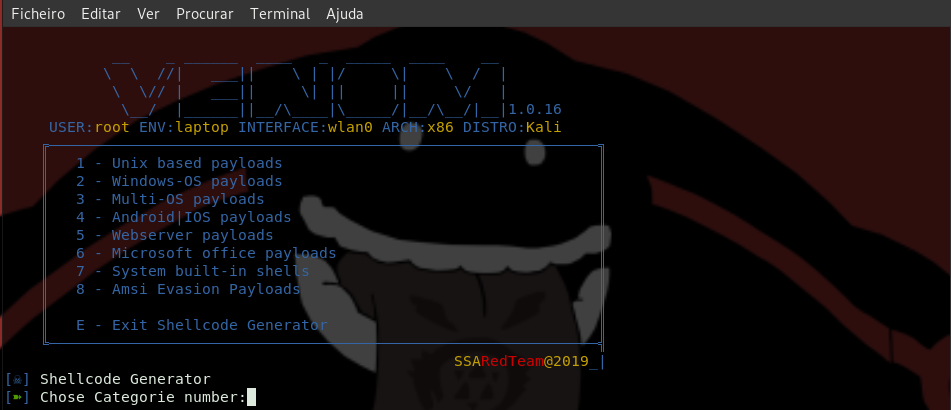
venom preview

venom

GitHubr00t-3xp10it/venom

venom - C2 shellcode generator/compiler/handler

command-and-controlexploit-frameworkspayload-development+5
2.0k5 years ago
Cooolis-ms preview

Cooolis-ms

GitHubrvn0xsy/cooolis-ms

Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…
command-and-controlexploit-frameworksids-ips-evasion+7
9252 years ago
CobaltStrike-Toolset preview

CobaltStrike-Toolset

GitHubqax-a-team/cobaltstrike-toolset

Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on

command-and-controlexploit-frameworkslateral-movement+8
5957 years ago
Medusa preview

Medusa

GitHubmythicagents/medusa

Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
command-and-controlexploit-frameworkslateral-movement+8
2122 months ago
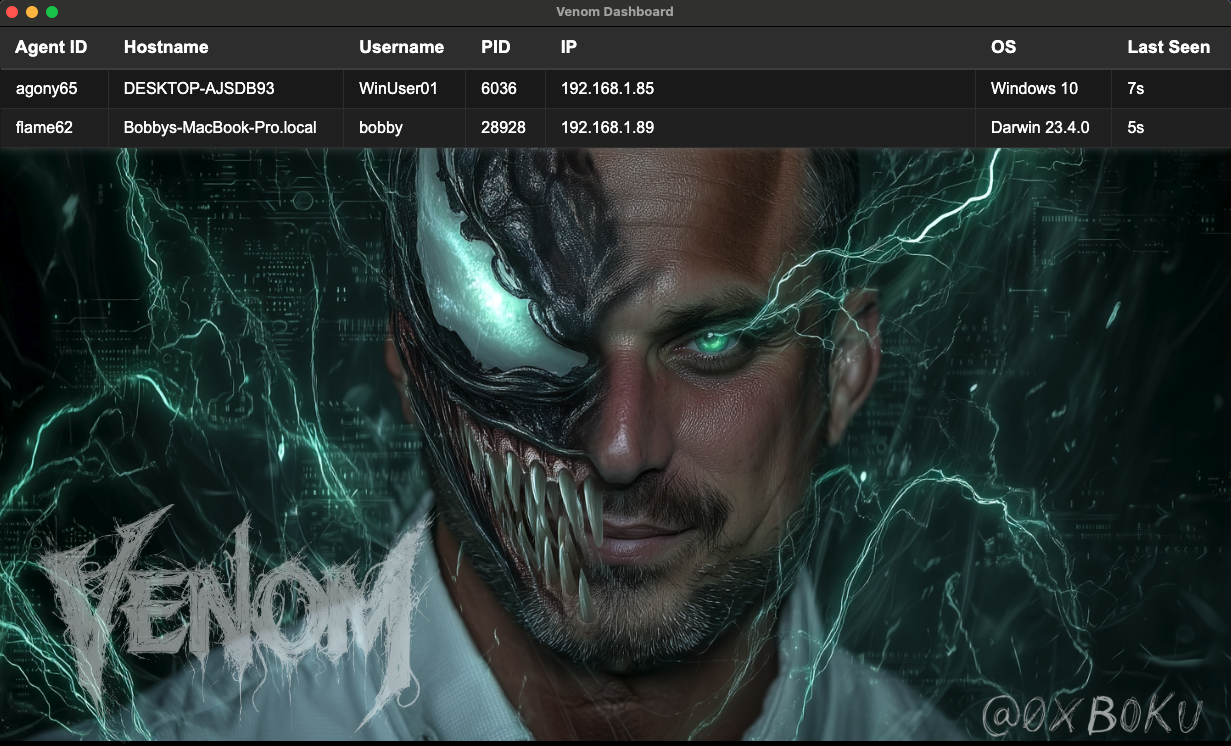
venom preview

venom

GitHubboku7/venom

Venom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence
command-and-controlencryption-decryption-toolslateral-movement+6
44211 months ago
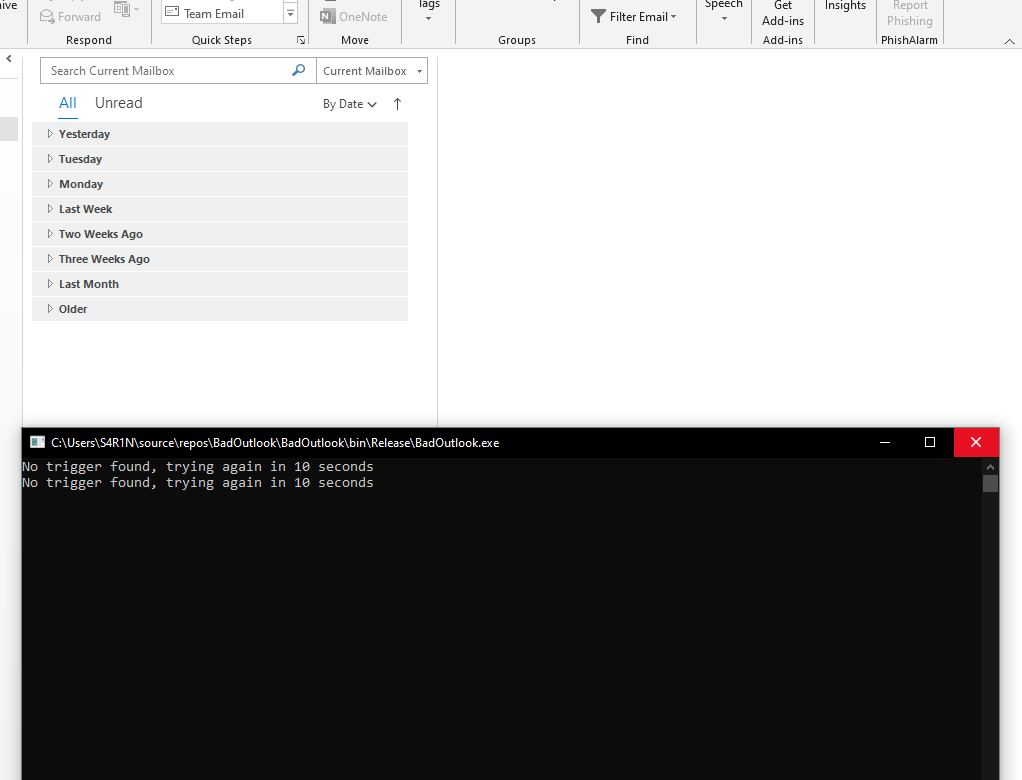
BadOutlook preview

BadOutlook

GitHubaahmad097/badoutlook

Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…
command-and-controlemail-securityexploitation+3
1375 years ago
KittyStager preview

KittyStager

GitHubenelg52/kittystager

KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
command-and-controleducationencryption-decryption-tools+6
2263 years ago
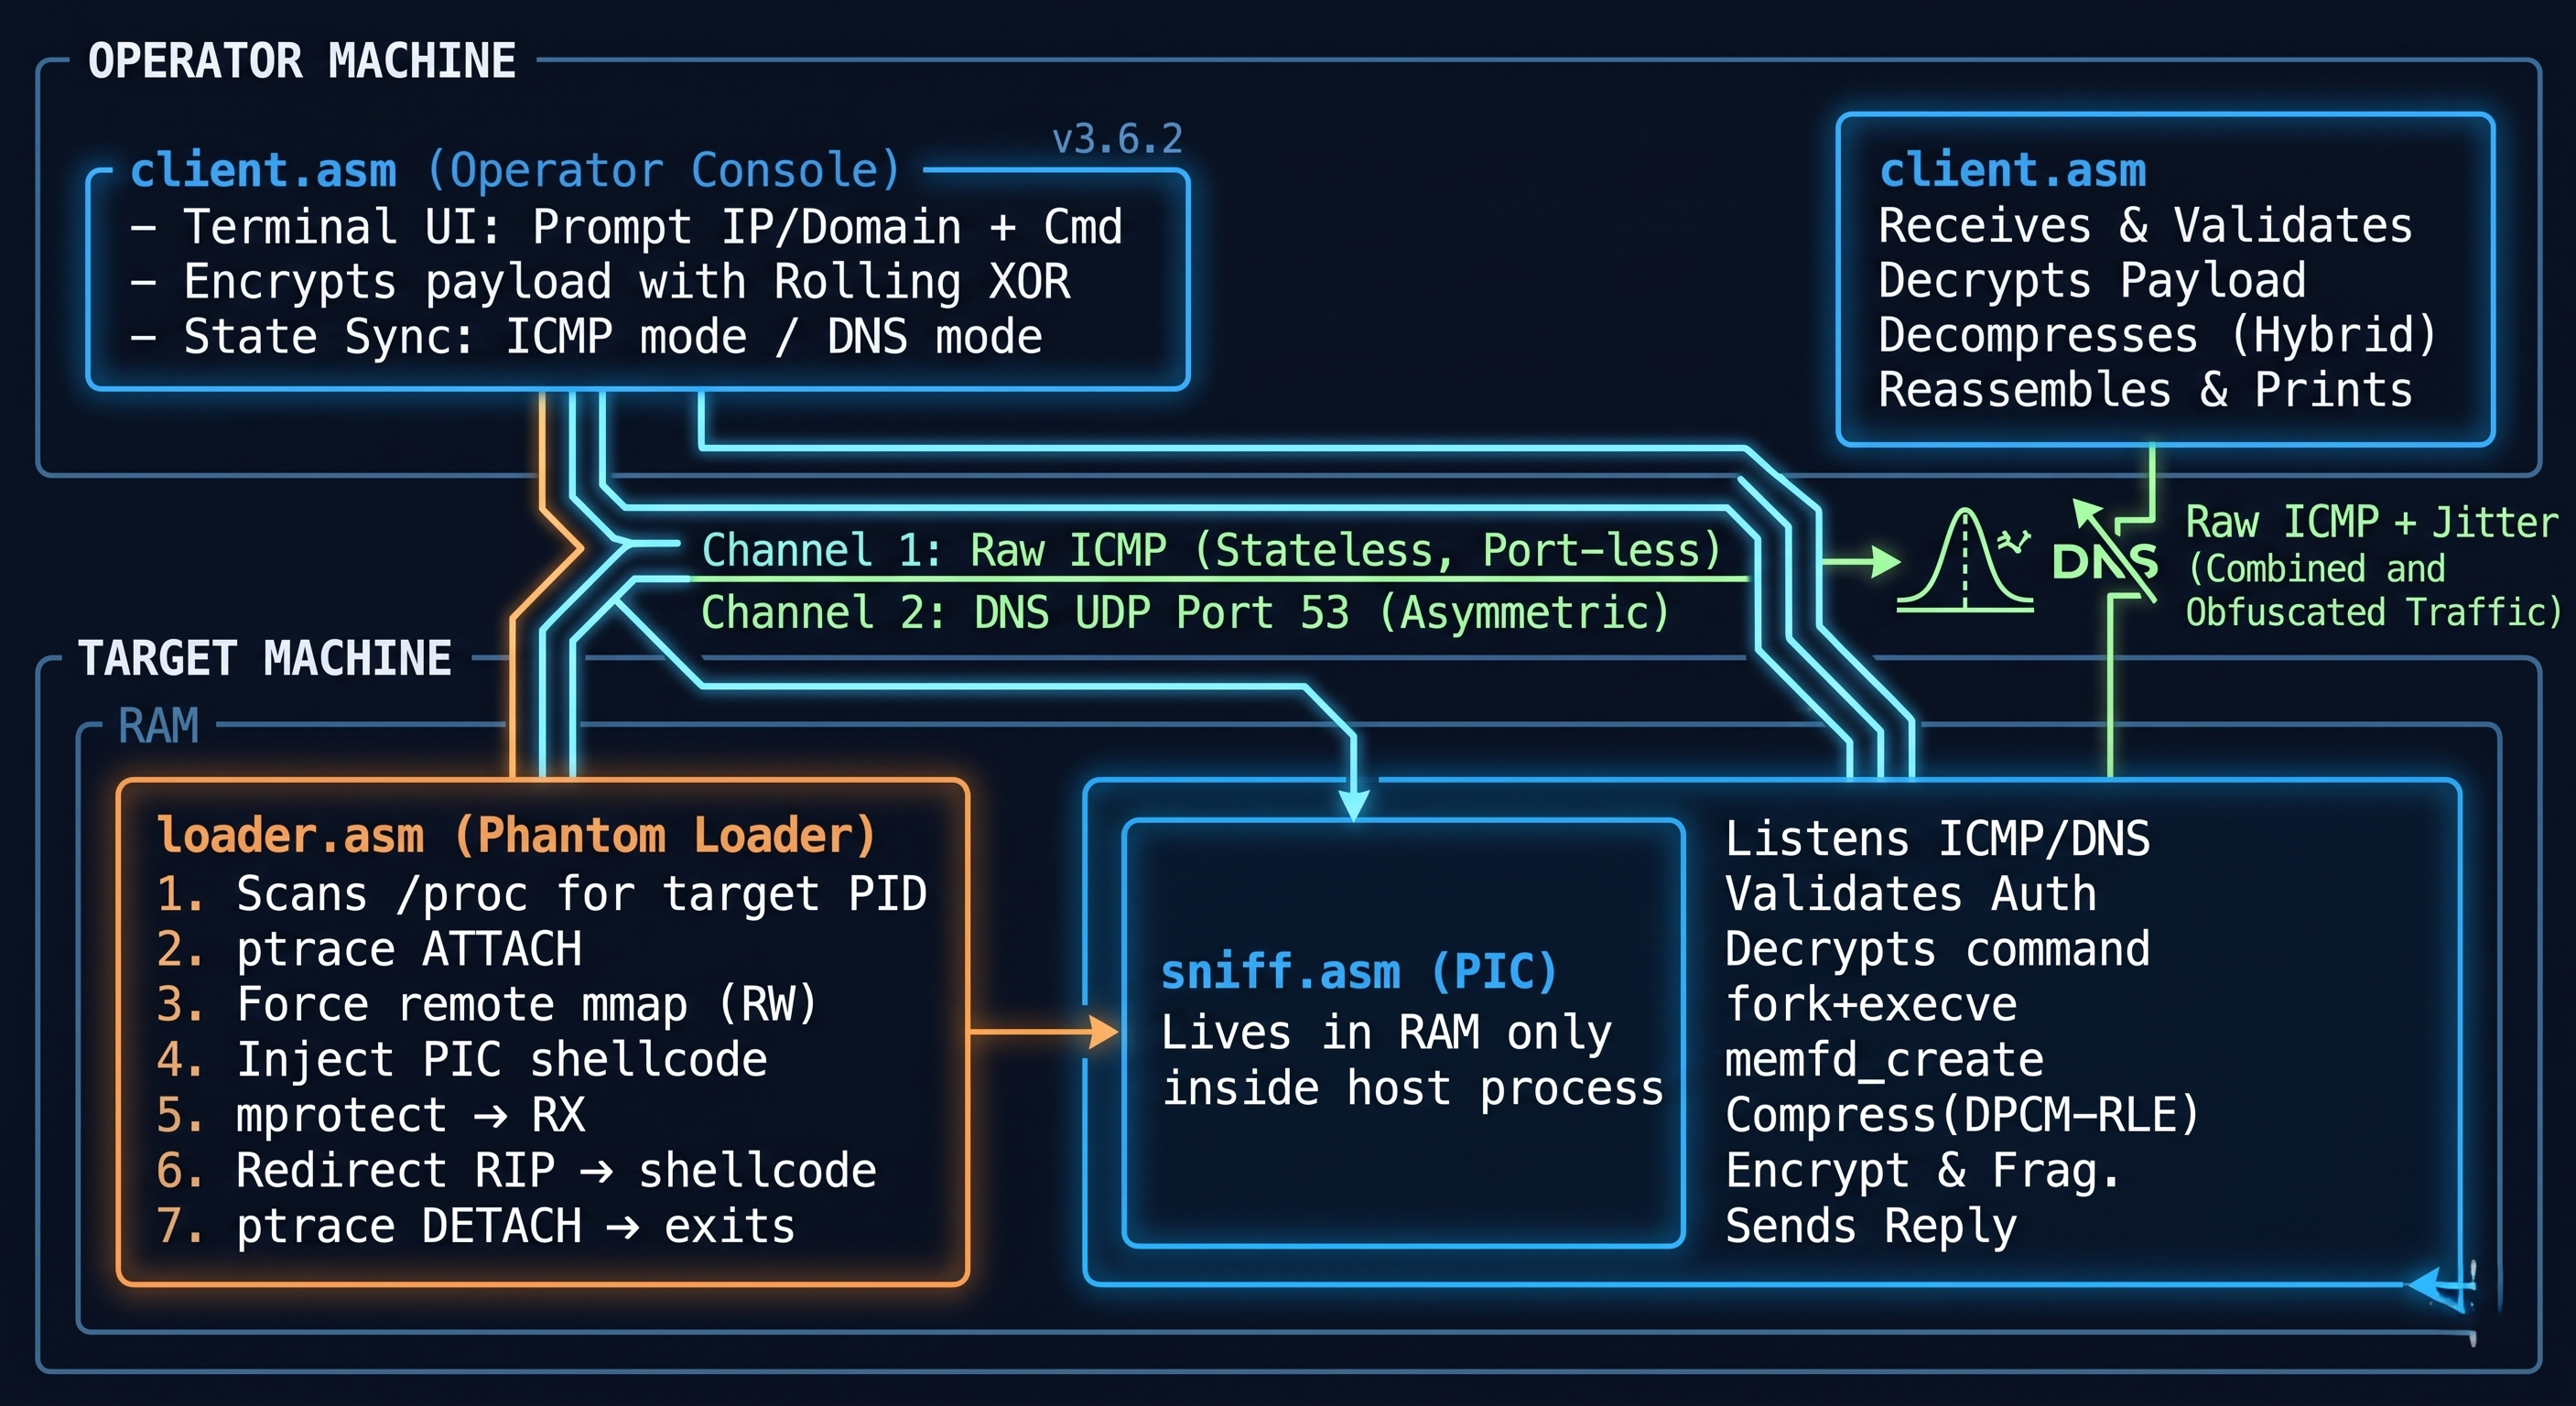
ICMP-Ghost-A-Fileless-x64-Assembly-C2-Agent preview

ICMP-Ghost-A-Fileless-x64-Assembly-C2-Agent

GitHubjm00nj/icmp-ghost-a-fileless-x64-assembly-c2-agent

Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…

command-and-controlexploit-frameworksids-ips-evasion+5
966 days ago
CustomC2ChannelTemplate preview

CustomC2ChannelTemplate

GitHubcodextf2/customc2channeltemplate

template for developing custom C2 channels for Cobalt Strike using IAT hooks applied by a reflective loader.

command-and-controlexploit-frameworkspayload-development+3
1069 months ago
FUD-C2-Framework preview

FUD-C2-Framework

GitHubx3r0day/fud-c2-framework

A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
command-and-controlencryption-decryption-toolsids-ips-evasion+9
75 months ago
Cerberus-React2Shell-Scanner-Exploit preview

Cerberus-React2Shell-Scanner-Exploit

GitHubcerberusmrxi/cerberus-react2shell-scanner-exploit

Elite exploitation toolkit for CVE-2025-55182 (React Server Components RCE). Async polymorphic payloads, advanced WAF/CDN bypass, proxy rotation,…

command-and-controleducationexploit-frameworks+9
21 month ago
Previous12…10Next