
CVE-2025-6002
 schn1tzelme1ster/cve-2025-6002
Python exploit for CVE-2025-6002 targeting authenticated arbitrary file upload in VirtueMart < 4.4.10. Logs in, uploads a PHP webshell, and triggers…
exploitationpayload-generationpenetration-testing+3
schn1tzelme1ster/cve-2025-6002Python exploit for CVE-2025-6002 targeting authenticated arbitrary file upload in VirtueMart < 4.4.10. Logs in, uploads a PHP webshell, and triggers…
 aadi0258/exploit-cve-2024-23897
Exploit for CVE-2024-23897 in Jenkins, enabling file read and remote code execution via crafted requests. Includes Docker setup and Groovy scripts…
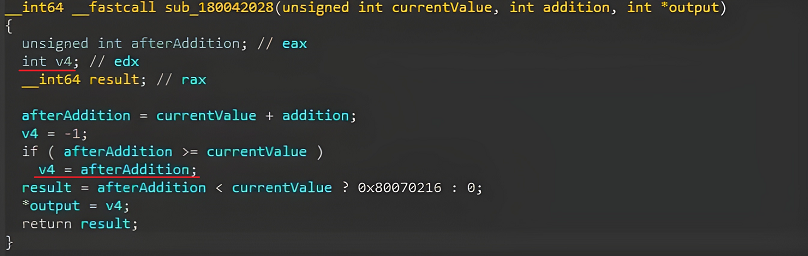 mr-alperen/cve-2022-26810
Remote code execution exploit for CVE-2022-26809 targeting Windows RPC heap buffer overflow with msfvenom shellcode integration and meterpreter…
 btar1gan/exploit_cve-2024-39205
Exploit for CVE-2024-39205, a js2py sandbox escape that enables remote code execution and establishes a reverse shell.
 1lkla/poc-exploit-for-dolibarr
POC exploit for Dolibarr <= 17.0.0 (CVE-2023-30253)
 orangepirate/cve-2018-9948-9958-exp
a exp for cve-2018-9948/9958 , current shellcode called win-calc
 kai-one001/wordpress-ht-contact-cve-2025-7340-rce
Python exploit for CVE-2025-7340, an unauthenticated file upload vulnerability in the WordPress HT Contact Form widget, enabling remote code…
 hexastrike/cve-2008-4654
A fully functional exploit for a stack-based buffer overflow vulnerability in VideoLan’s VLC Media Player 0.9.4 when processing TiVo files.
 user01-1/cve-2023-41892_poc
Customized this for my own use
 0xsojalsec/cve-2022-1609
Bash poc for CVE-2022-1609 WordPress Weblizar Backdoor
 andwati/cve-2025-24893
Python exploit for CVE-2025-24893 that executes a reverse shell on vulnerable web applications, with shell upgrade instructions.
 dadosneurais/cve-2023-3824
Proof-of-concept exploit for CVE-2023-3824 (PHP phar deserialization) enabling remote code execution via crafted phar archive and reverse shell…
 engranaabubakar/cve-2023-46818
Proof-of-concept exploit for authenticated PHP code injection in ISPConfig <= 3.2.11, enabling remote code execution via unsanitized language file…
 jeromeyoung/cve-2021-27965
Proof of concept for CVE-2021-27965 (Stack-based Buffer Overflow)
 matesz44/cve-2009-2265
posix sh poc for CVE-2009-2265 (deps: curl,msfvenom,uuidgen,tr)
 adenkiewicz/cve-2017-9544
SEH BO based exploit for Easy Chat Server on Win 7 32b
 likekabin/cve-2018-10933_ssh
Python exploit for CVE-2018-10933 that bypasses libssh server authentication and spawns an unauthenticated shell on vulnerable SSH servers.
 svchostmm/cve-2024-25600-mass
Mass exploit for CVE-2024-25600, uploading webshells to vulnerable WordPress sites via a list of targets.