

DFShell
 d3ext/dfshell
Python-based forward shell tool that creates a TTY-like interactive shell over HTTP using named pipes, enabling command execution on firewalled…
payload-generationpenetration-testingshellcode+1
122
d3ext/dfshellPython-based forward shell tool that creates a TTY-like interactive shell over HTTP using named pipes, enabling command execution on firewalled…
 arthastang/router-exploit-shovel
Automated Application Generation for Stack Overflow Types on Wireless Routers
 airbus-cert/yara-ttd
Use YARA rules on Time Travel Debugging traces
 coolboy4me/cve-2019-0708_bluekeep_rce
it works on xp (all version sp2 sp3)
 schich/lucky-spark
A stealthy stager designed for shellcode payloads staged with http/https like Sliver, or on github raw.
 pentestical/cve-2020-9484
Bash proof-of-concept exploit for CVE-2020-9484 enabling remote code execution on Apache Tomcat via insecure deserialization in file uploads, with…
 nataliadiak/windows-x86-shellcode-poc
Windows x86 PoC: Stack‑based buffer overflow with custom shellcode on legacy 32-bit Windows.
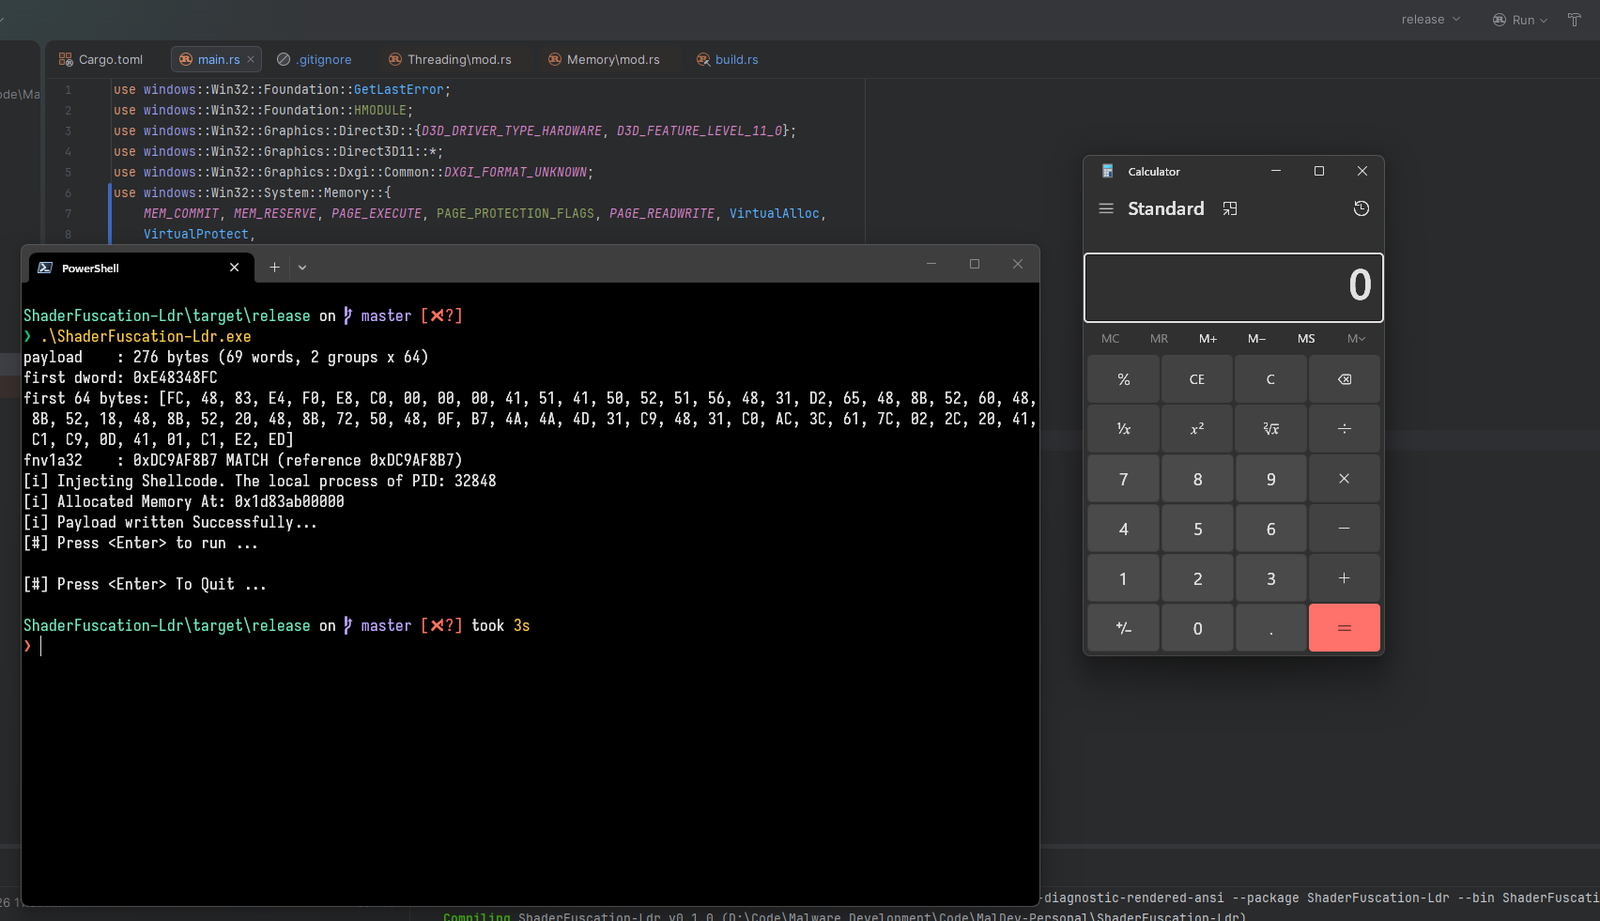 dovelus/polychrome-rs
A PoC on how to use a Compute Shader as Payload
 ludovicpatho/cve-2022-0847_dirty-pipe
Hacked up Dirty Pipe (CVE-2022-0847) PoC that hijacks a SUID binary to spawn a root shell. (and attempts to restore the damaged binary as well)
 kernelerr/vlc-cve-2008-4654-exploit
An EXP could run on Windows x64 against CVE-2008-4654.
 chicken3962/cve-2025-3500-poc
Educational lab environment for researching CVE-2025-3500, an integer overflow privilege escalation exploit in Avast Antivirus 25.1.981.6 on Windows,…
 3x1t1um/cve-2007-2447
Python exploit for CVE-2007-2447 that triggers Samba username map script command injection to open a reverse shell on vulnerable targets.
 themalwareguardian/cve-2019-25485
Stack-based buffer overflow in R 3.4.4. Full exploitation on x86, but only RIP control with gadget analysis on x64 due to program constraints. The…
 yaldobaoth/cve-2015-1578-poc-metasploit
This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…
 blackcat4347/cve-2025-32463_poc
Proof-of-concept exploit for CVE-2025-32463, demonstrating shared library injection via precompiled payload for immediate execution on affected…
 andwati/cve-2025-24893
Python exploit for CVE-2025-24893 that executes a reverse shell on vulnerable web applications, with shell upgrade instructions.
 adenkiewicz/cve-2017-9544
SEH BO based exploit for Easy Chat Server on Win 7 32b
 rnnsz/cve-2008-4654
PoC exploit generator for CVE-2008-4654, a stack-based buffer overflow in VLC Media Player via crafted .ty+ files. Generates malicious payload file…