
Archived
DKMC
 mr-un1k0d3r/dkmc
DKMC - Dont kill my cat - Malicious payload evasion tool
command-and-controlpayload-generationpenetration-testing+3
1.4k
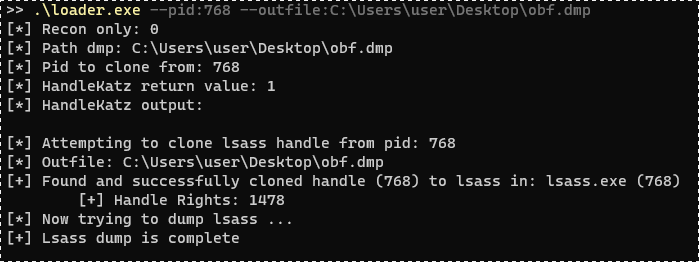 codewhitesec/handlekatz
PIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…
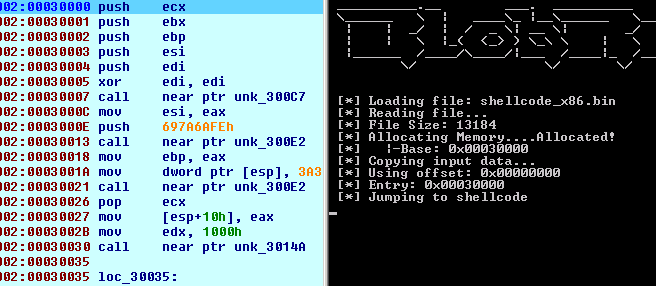 oalabs/blobrunner
Quickly debug shellcode extracted during malware analysis
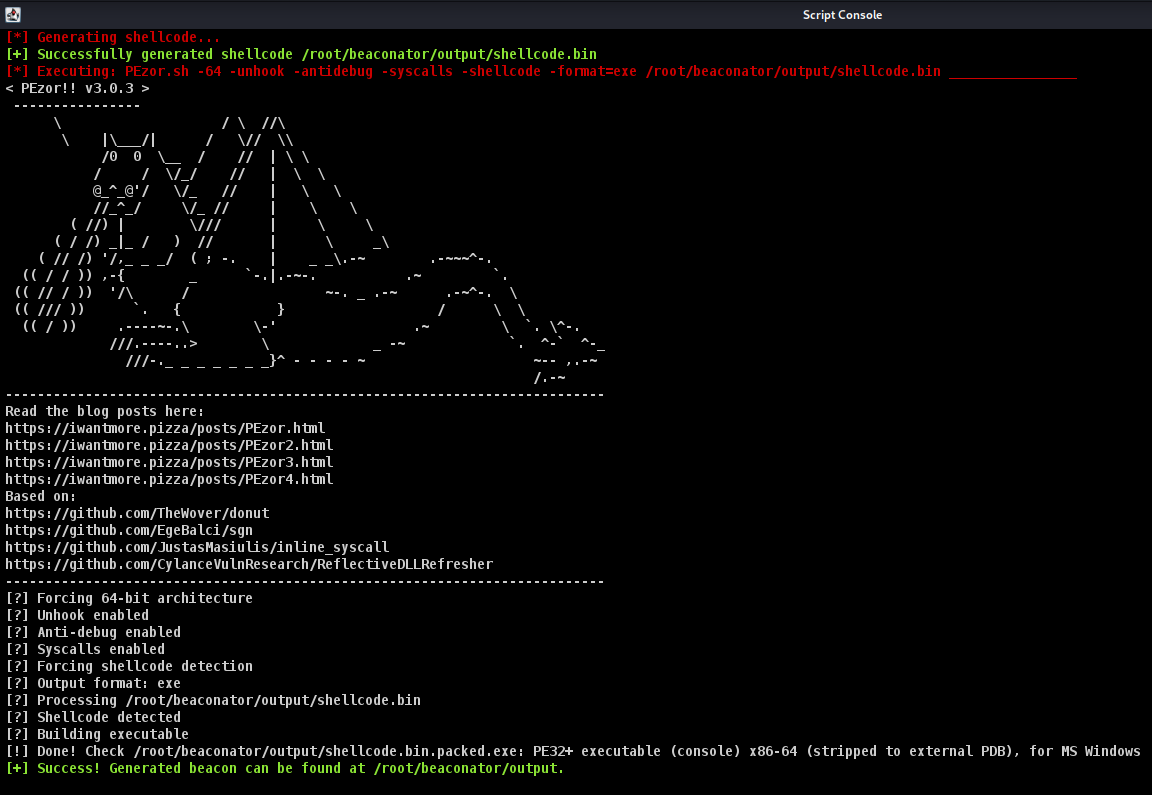 capt-meelo/beaconator
A beacon generator using Cobalt Strike and a variety of tools.
 ergrelet/themida-unmutate
Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.
 gamozolabs/elfloader
An architecture-agnostic ELF file flattener for shellcode
 m4sc3r4n0/astroid
ASTROID v 1.2 bypass most A.V softwares
 arthastang/router-exploit-shovel
Automated Application Generation for Stack Overflow Types on Wireless Routers
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 dullpurple-sloop726/cve-2026-31431-linux-copy-fail
Exploit CVE-2026-31431 on Linux using a Rust implementation to achieve local privilege escalation via an arbitrary page cache write primitive.
 anonstorks/cve-2025-0282-full-version
# CVE-2025-0282: Remote Code Execution Vulnerability in [StorkS]
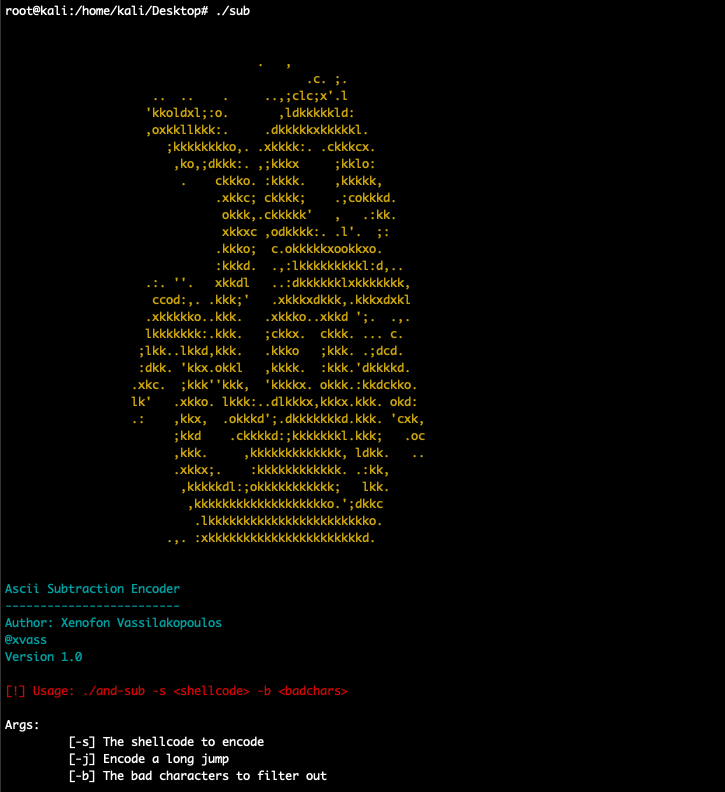 xen0vas/ascii-and-sub-encoder
This is a custom ASCII AND/SUB Encoder developed during my preparation for the legacy OSCE/CTP course
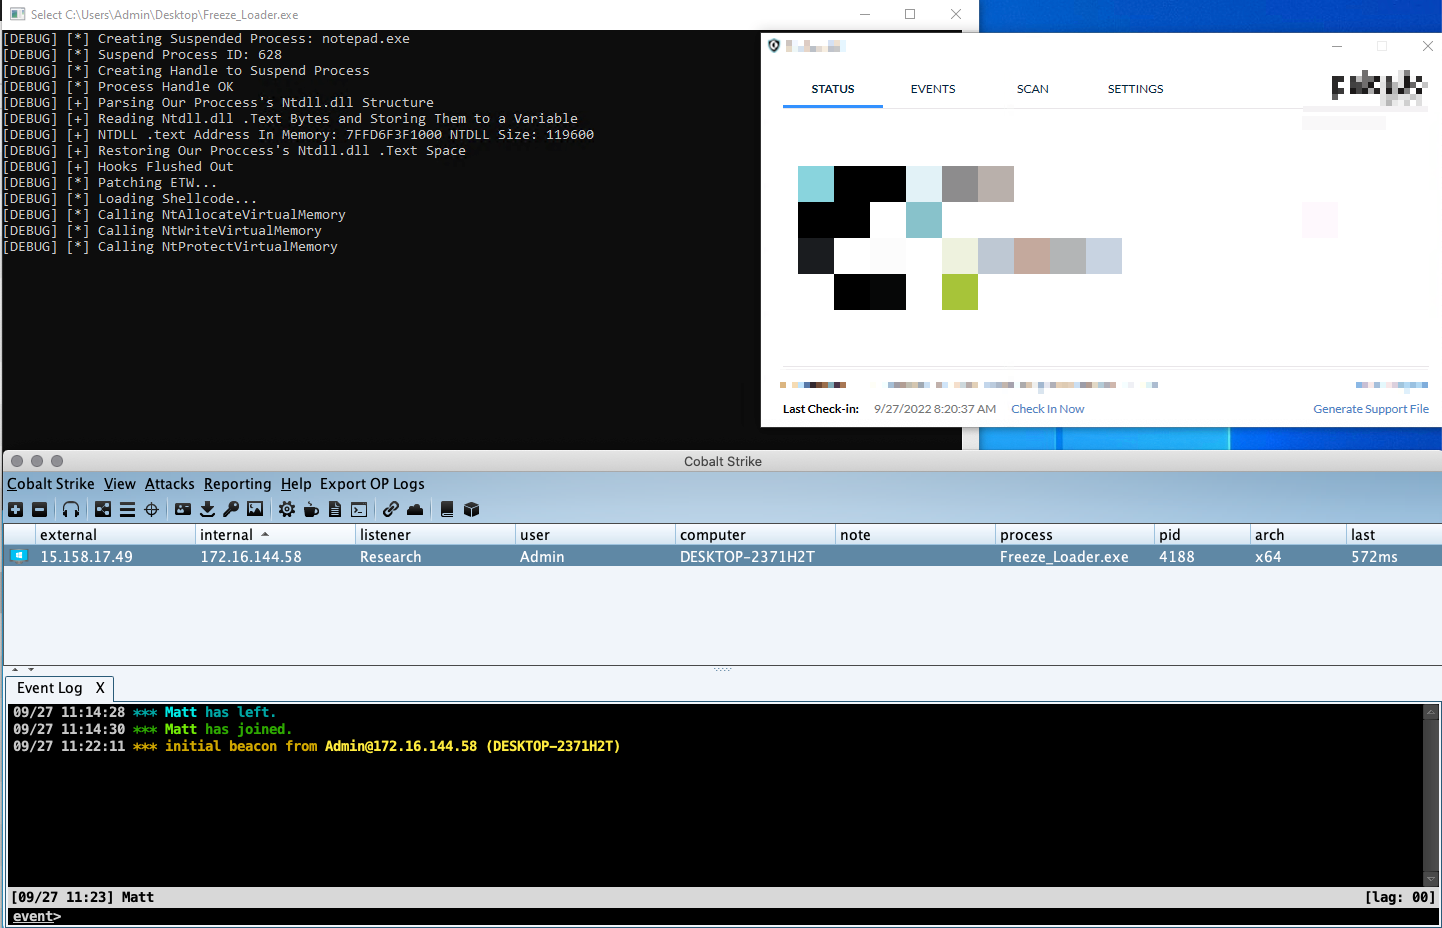 optiv/freeze
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 soledad208/cve-2018-10933
CVE-2018-10933 very simple POC
 likekabin/cve-2018-10933_ssh
Python exploit for CVE-2018-10933 that bypasses libssh server authentication and spawns an unauthenticated shell on vulnerable SSH servers.