
CVE-2023-45878_to_RCE
 byt3loss/cve-2023-45878_to_rce
This script chains and automates Arbitrary File Write to RCE on Gibbon LMS through CVE-2023-45878 exploitation.
exploitationpayload-generationpenetration-testing+3
2
byt3loss/cve-2023-45878_to_rceThis script chains and automates Arbitrary File Write to RCE on Gibbon LMS through CVE-2023-45878 exploitation.
 jacobtaylor3/cve-2021-21220
Browser-based CVE-2021-21220 exploit delivering a reverse shell via shellcode and a C2 implant for remote command execution on Windows targets.
 nicolasdamians/ms09-050-cve-2009-3103-exploit
Automated exploit wrapper for MS09-050 (CVE-2009-3103) targeting SMBv2 on Windows Vista/Server 2008. Generates shellcode, builds exploit, and creates…
 stivenhacker/ghoststrike
C++ process hollowing injector that encrypts and obfuscates shellcode with XOR, Base64, and dynamic API resolution to deploy stealthy reverse shells…
 sneakynachos/cve-2026-2764-but-with-wasm
Proof-of-concept exploit chain for Firefox JIT CVE-2026-2764, chaining JIT miscompilation and use-after-free into arbitrary read/write and WASM…
 t3l3machus/villain
Villain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…
 ntfargo/relapse-exploit
PS5 exploit chain for firmware 7.00-13.60 combining a WebKit JSC info leak and typedarray corruption with an aio_multi_wait UAF race for kernel…
 lukechilds/reverse-shell
On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.
 idov31/sandman
NTP-based backdoor for hardened networks, delivering and executing arbitrary shellcode via spoofed NTP traffic with optional persistence as a Windows…
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
 theleopard65/cve-2021-3156-baron-samedit
A simple Docker lab and Exploit setup for CVE-2021-3156 - "Baron Samedit".
 giovannipajeu1/cve-2024-23742
Proof-of-concept exploit for CVE-2024-23742 in Loom for macOS. Validates vulnerability and injects arbitrary code via RunAsNode settings to gain a…
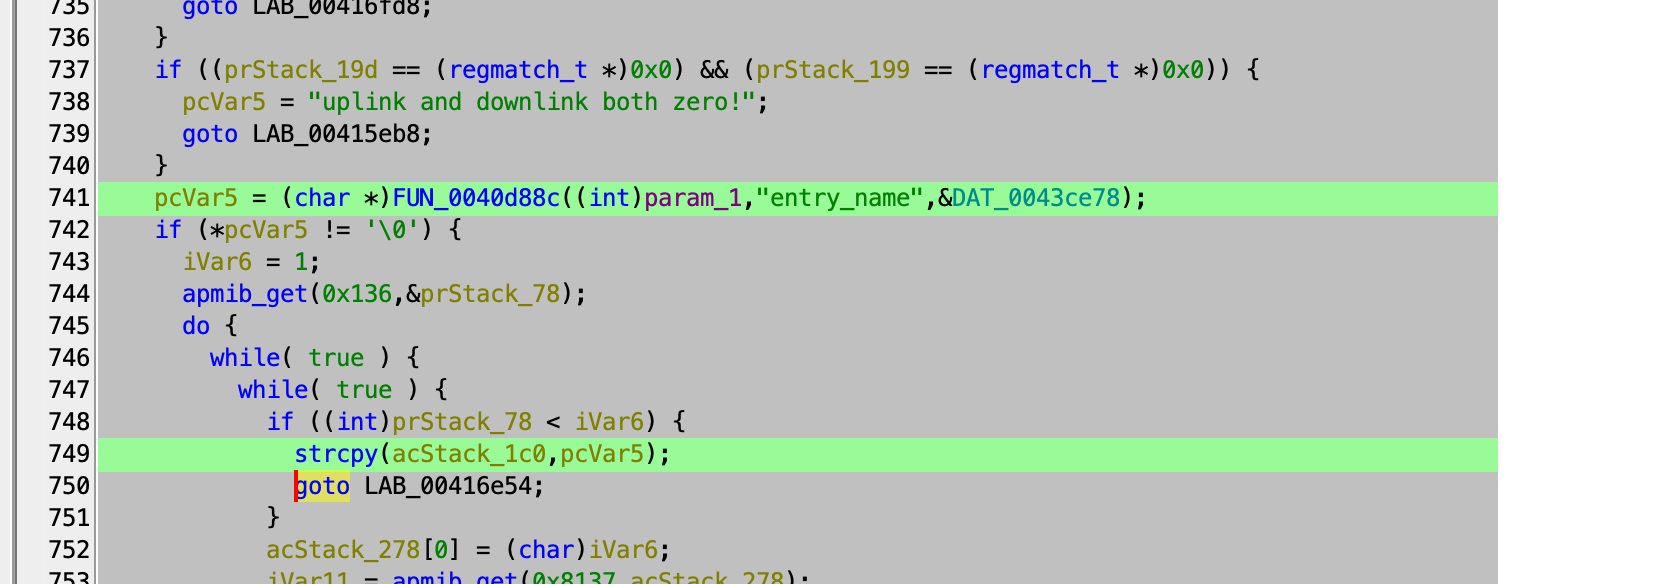 laskdjlaskdj12/cve-2024-35106-poc
Proof-of-concept exploit for CVE-2024-35106, a stack buffer overflow in NEXTU FLETA AX1500 Wi-Fi 6 router. Demonstrates denial-of-service and…
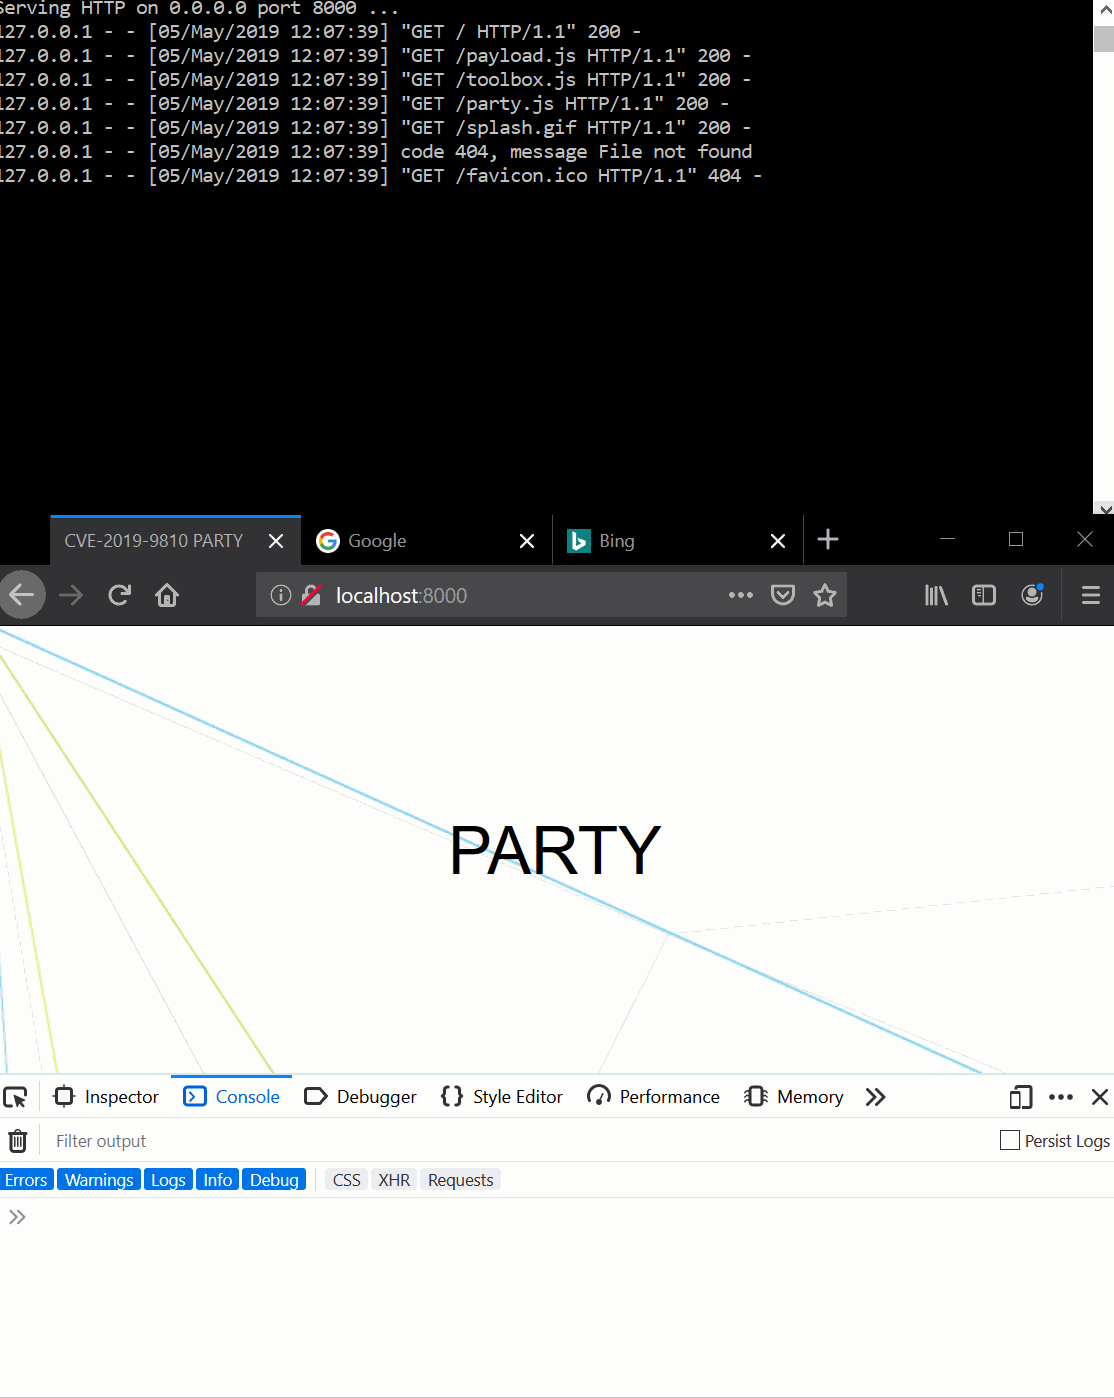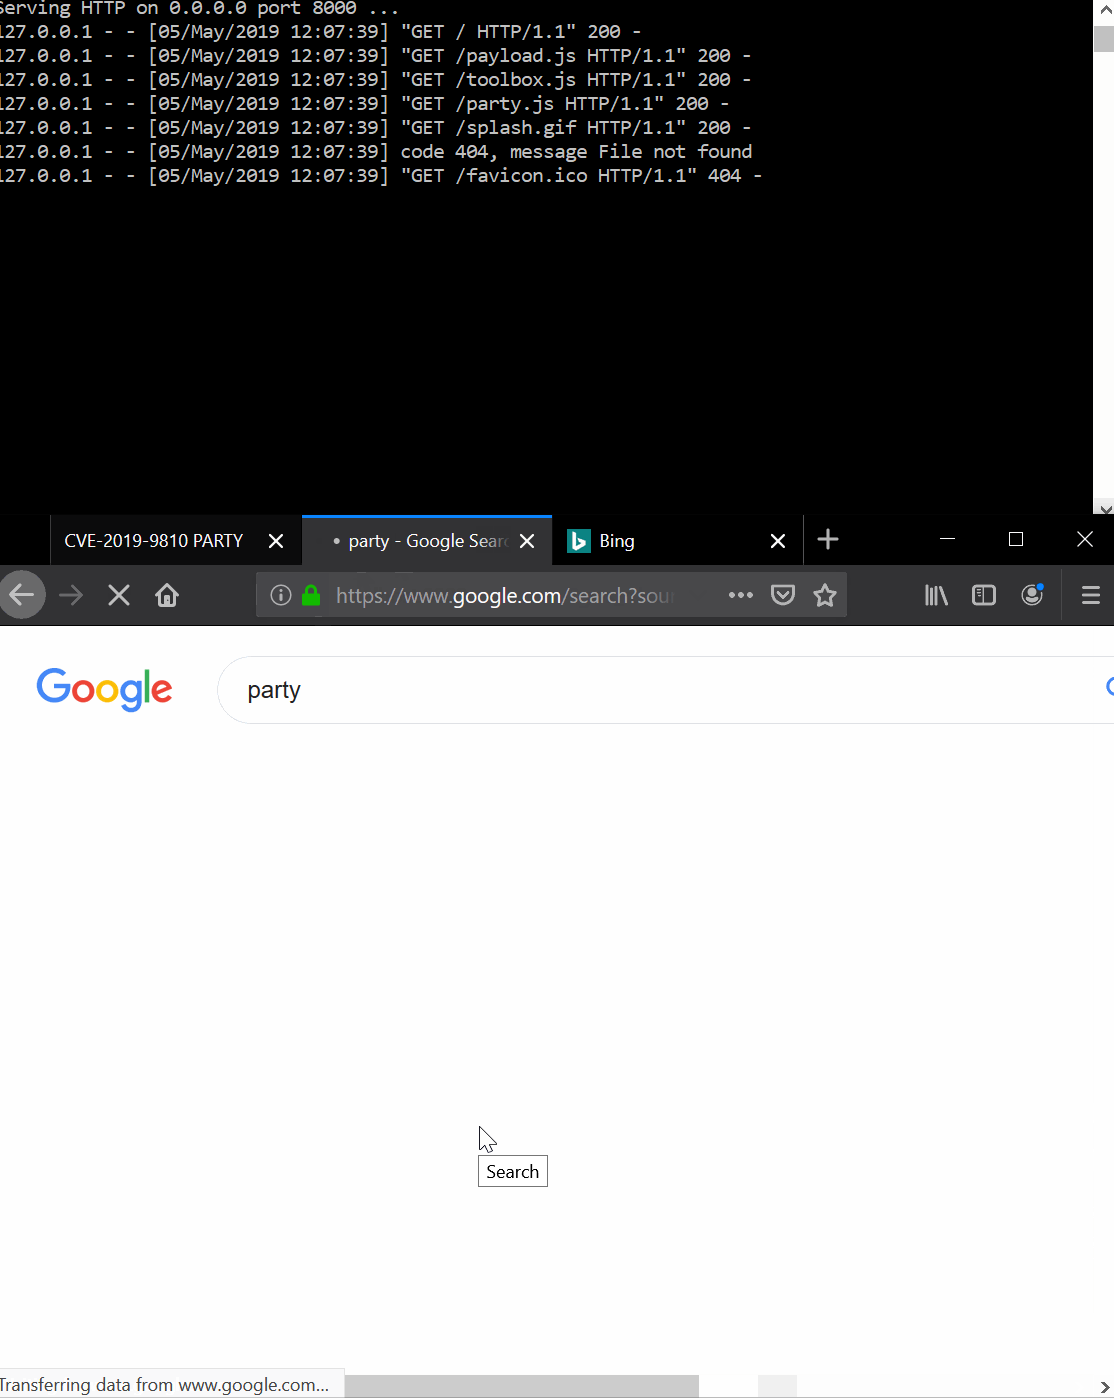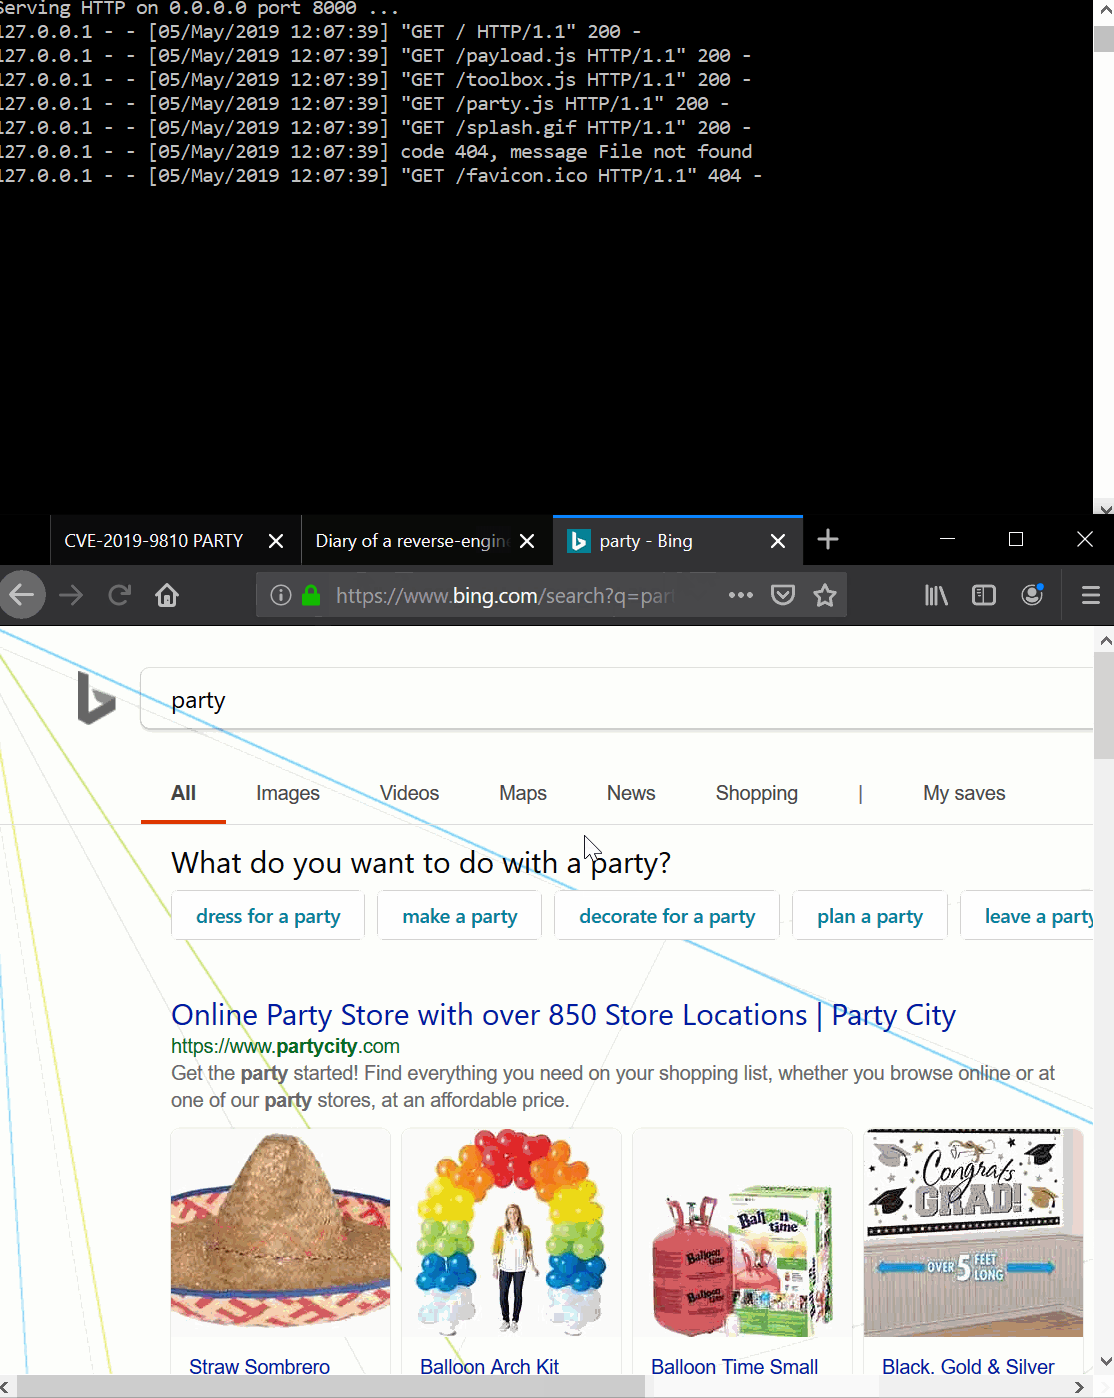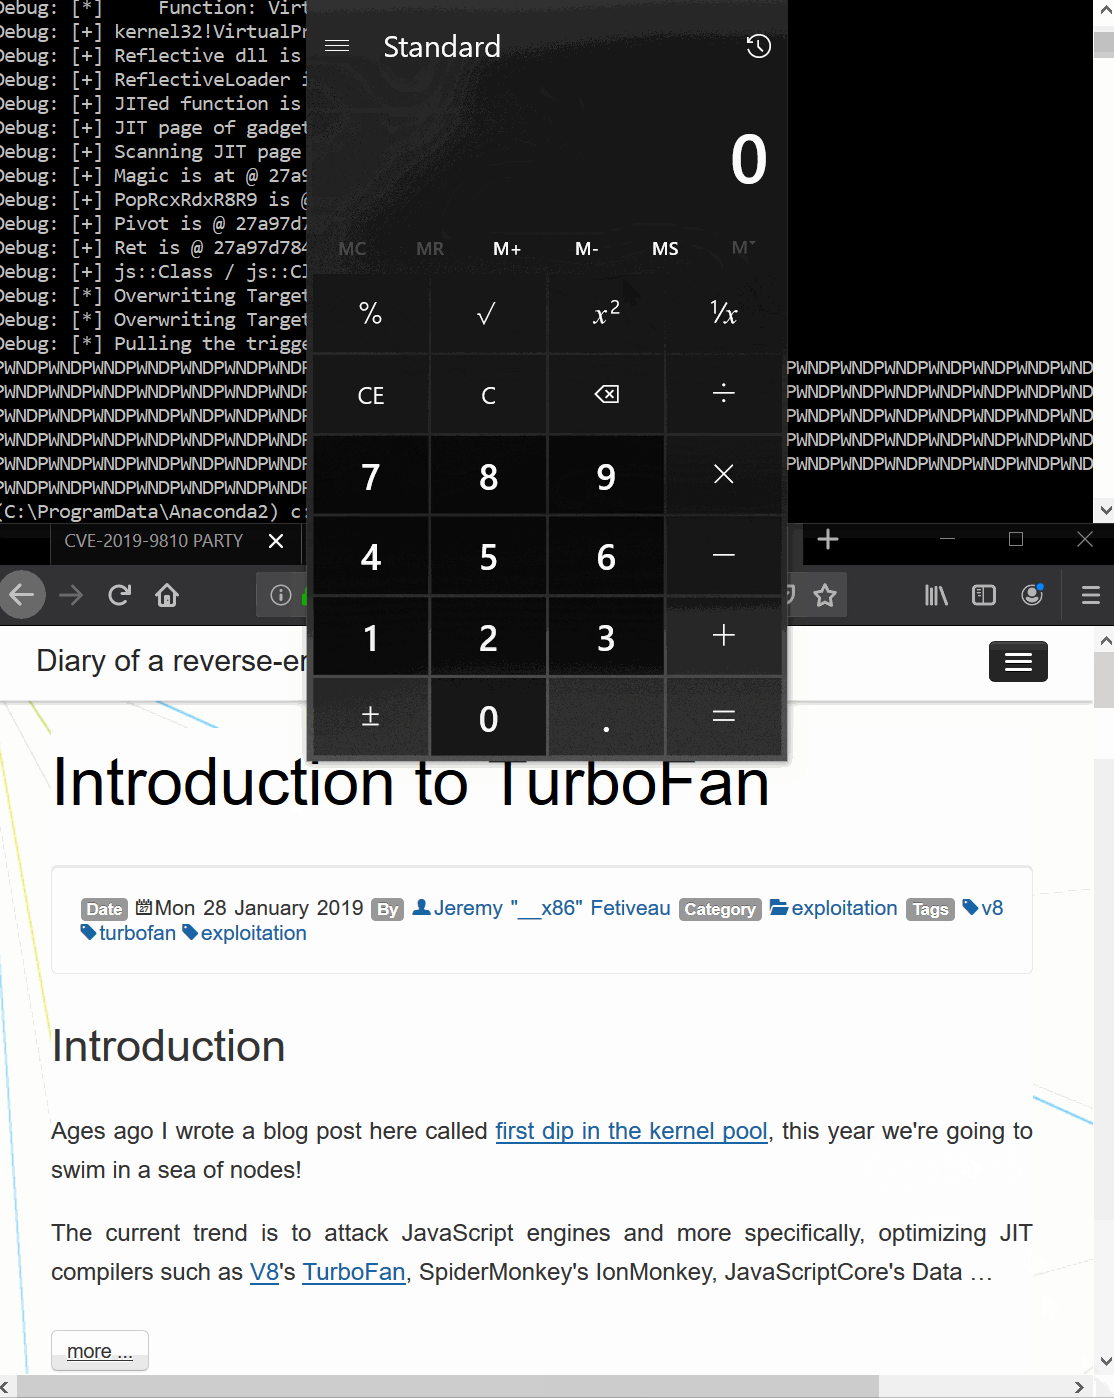 0vercl0k/cve-2019-9810
Exploit for CVE-2019-9810 Firefox on Windows 64-bit.
 thiscitze/cve-2026-98432-root-shell
CVE-2026-98432 lab root-shell kit (aid kernel; not a stock remote exploit)
 x86byte/obfusk8
Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.