

CVE-2018-10933
 soledad208/cve-2018-10933
CVE-2018-10933 very simple POC
authentication-authorizationexploitationpayload-generation+3
1268 years ago
soledad208/cve-2018-10933CVE-2018-10933 very simple POC
 3xpl01tc0d3r/obfuscator
The program is designed to obfuscate the shellcode.
 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
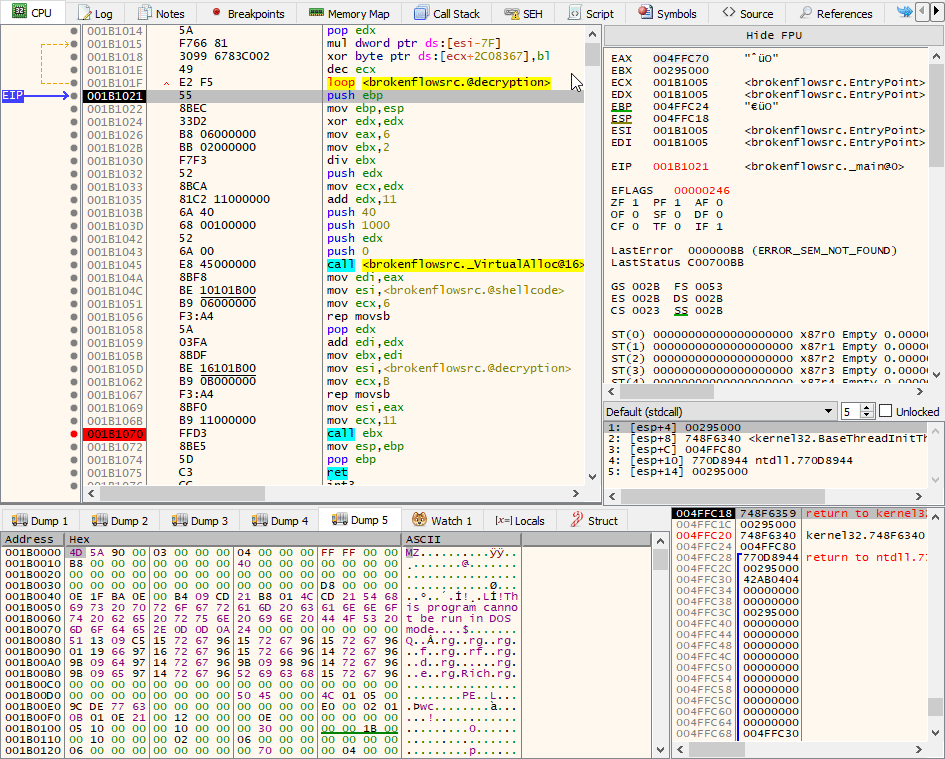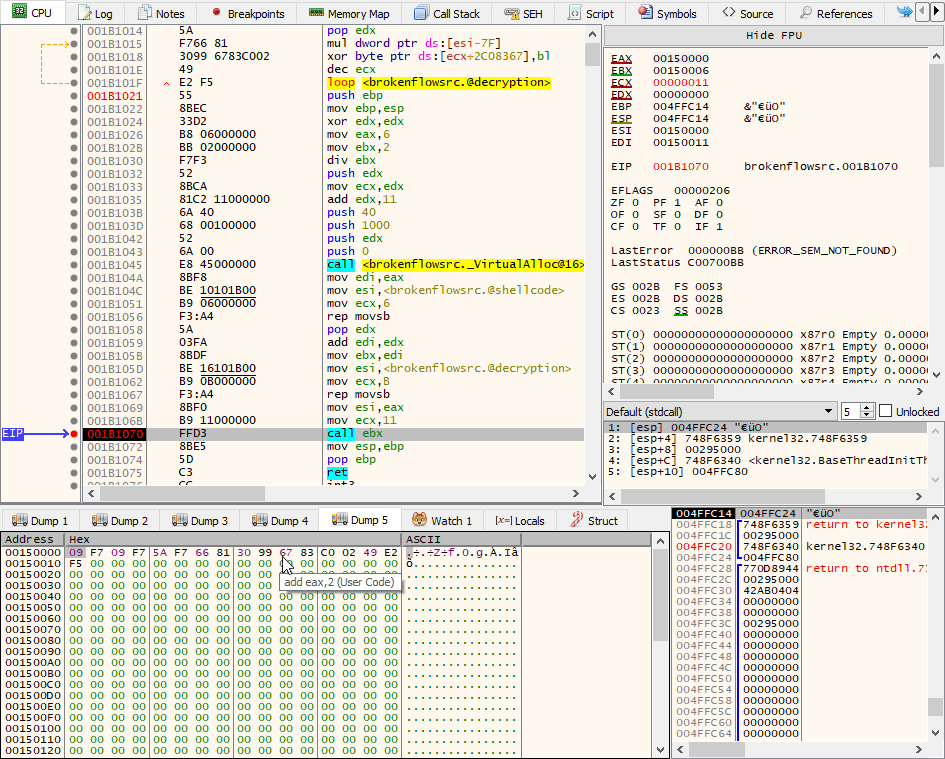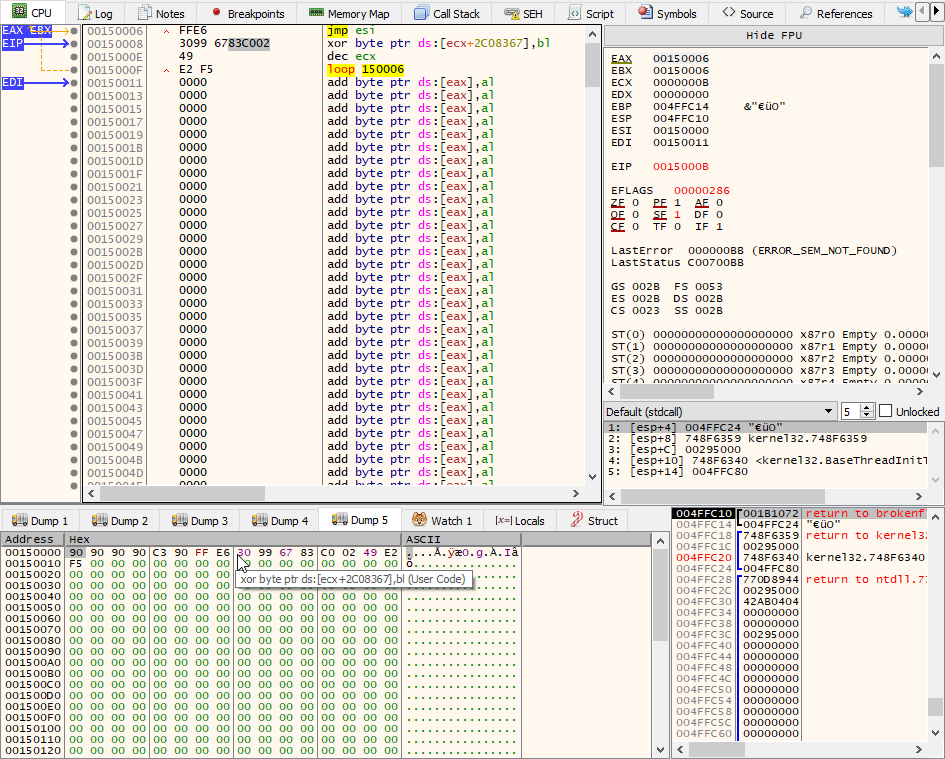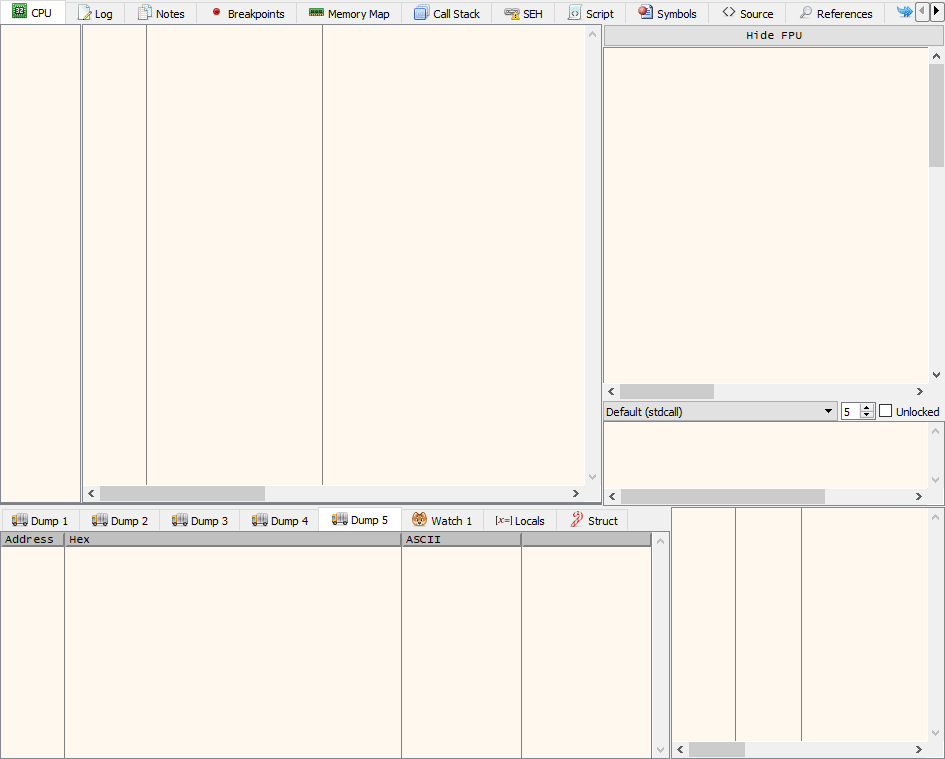 enkomio/brokenflow
A simple PoC to invoke an encrypted shellcode by using an hidden call
 offsecginger/pythonaesobfuscate
Obfuscates a Python Script and the accompanying Shellcode.
 coolboy4me/cve-2019-0708_bluekeep_rce
it works on xp (all version sp2 sp3)
 blacknbunny/encdecshellcode
Shellcode Encrypter & Decrypter via XOR Cipher
 ruoji6/cve-2025-55182-rce-shell
Burp Suite/antsword - Interactive shell (HTTP hijack + POST + AES-256-CBC/BASE64)
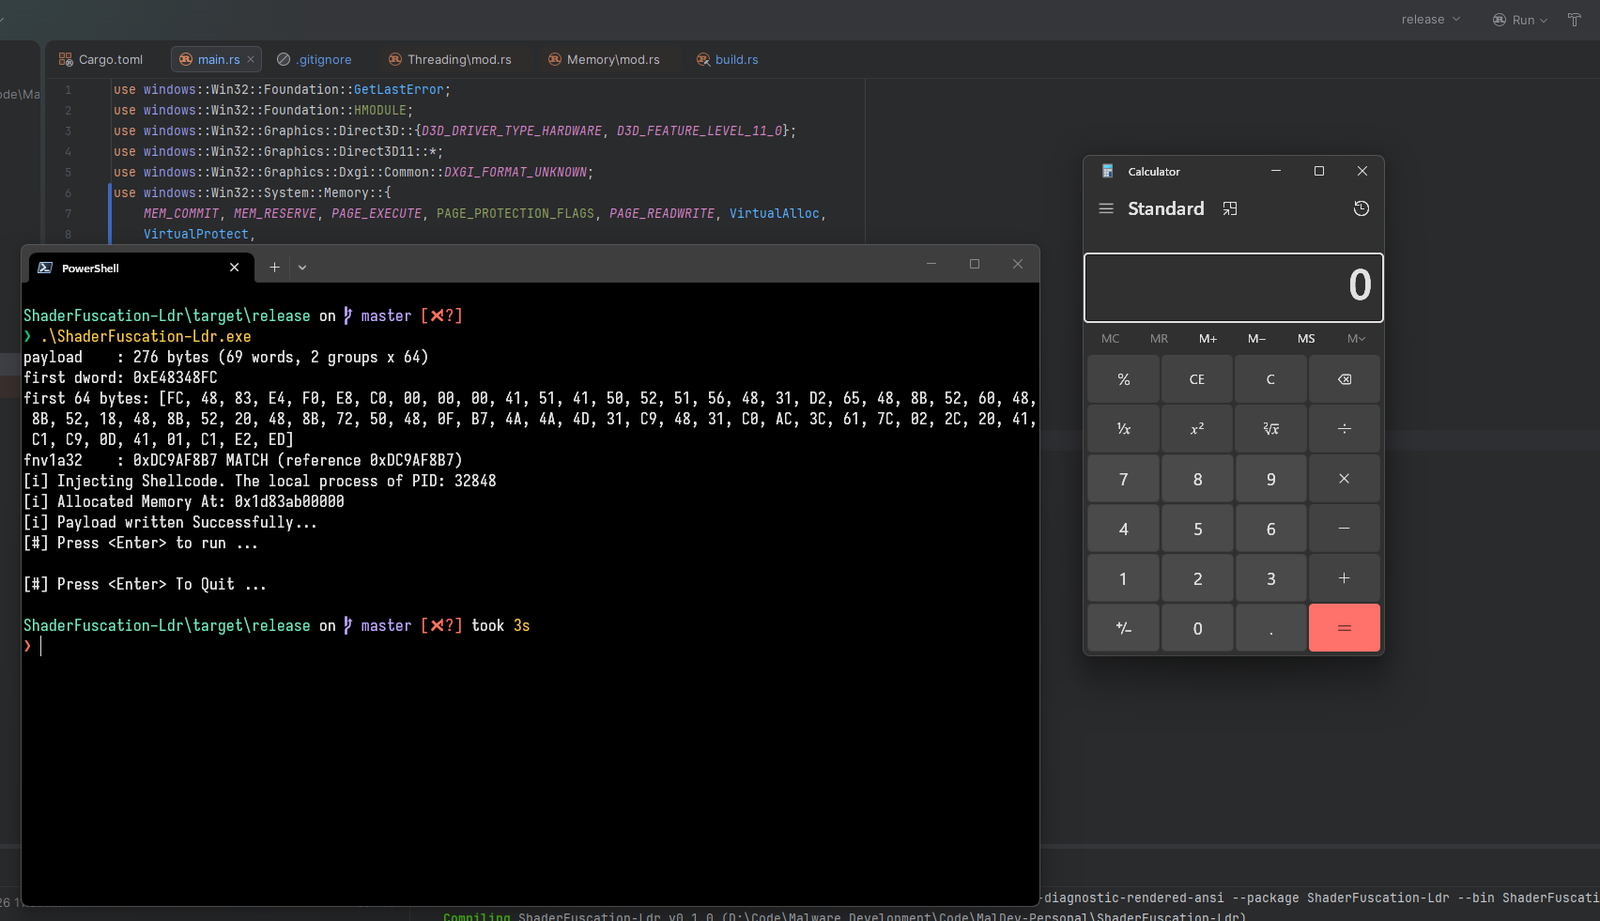 dovelus/polychrome-rs
A PoC on how to use a Compute Shader as Payload
 gmh5225/packer-payload-entropyreducer
Reduce Entropy And Obfuscate Youre Payload With Serialized Linked Lists
 superzerosec/cve-2020-7247
OpenSMTPD version 6.6.2 remote code execution exploit
 vuducmanhno100-cloud/cve-2024-6387
CVE-2024-6387 POC (Currently being edited)
 jayngng/bludit-cve-2019-17240
Bypass bludit mitigation login form and upload malicious to call a rev shell
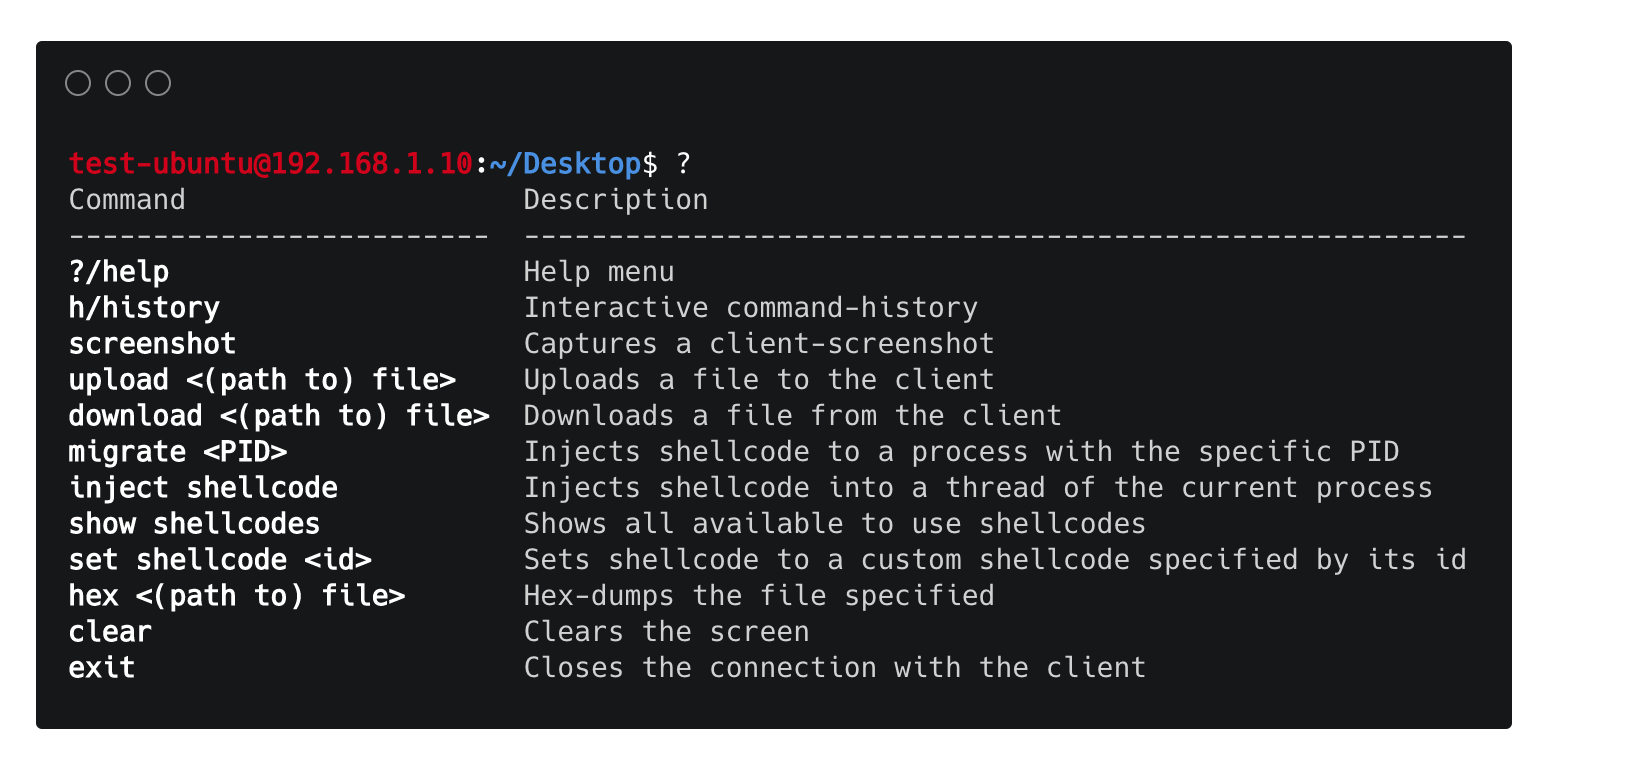 chrispetrou/hrshell
HRShell is an HTTPS/HTTP reverse shell built with flask. It is an advanced C2 server with many features & capabilities.
 ch0pin/aviator
Antivirus evasion project
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 algo7/bluekeep_cve-2019-0708_poc_to_exploit
An Attempt to Port BlueKeep PoC from @Ekultek to actual exploits