
CVE-2022-31814
 sh4den/cve-2022-31814
Proof of concept for CVE-2022-31814
exploitationpenetration-testingred-teaming+3
1
sh4den/cve-2022-31814Proof of concept for CVE-2022-31814
 natteesetobol/cve-2019-0567-ms-edge
My proof of concept for CVE-2019 Microsoft-Edge
 s3n4t0r-0x0/rustywater-shellcode-dropper
RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.
 forrest-orr/doublestar
A personalized/enhanced re-creation of the Darkhotel "Double Star" APT exploit chain with a focus on Windows 8.1 and mixed with some of my own…
 rnnsz/cve-2017-8367
Python-based proof-of-concept exploit for CVE-2017-8367, a stack-based buffer overflow in Easy Mov Converter. Generates a payload file for local…
 charchit-subedi/chamilo-lms-unauthenticated-rce-poc
This is a script written in Python that allows the exploitation of the Chamilo's LMS software security flaw described in CVE-2023-4220
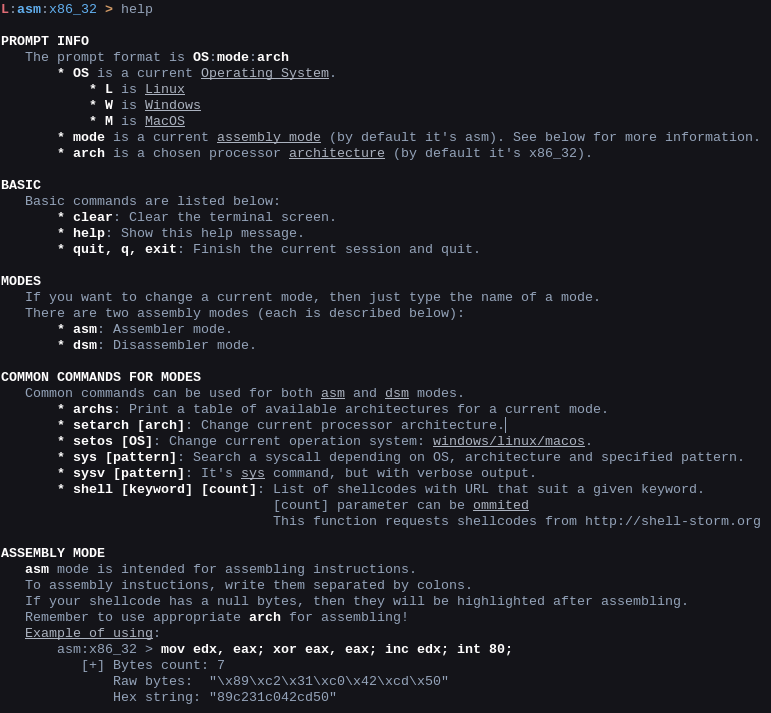 konatabrk/shellen
:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes
 mdsecactivebreach/sharpshooter
Payload Generation Framework
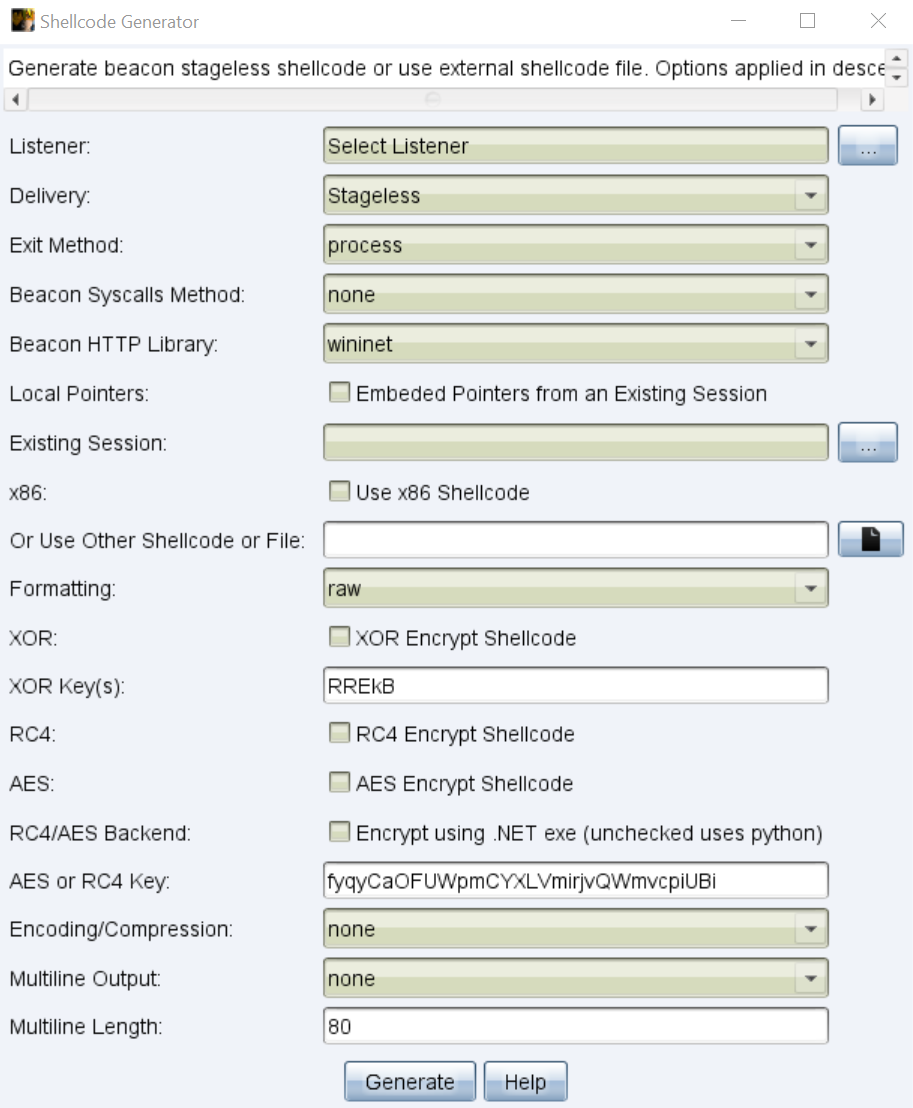 rcstep/cssg
Cobalt Strike aggressor script for generating, formatting, and encrypting beacon shellcode with support for multiple exit methods, syscalls, and…
 iilegacyyii/datainject-bof
Hijacks code execution via overwriting Control Flow Guard pointers in combase.dll
 vulncheck-oss/cve-2025-55182
VulnCheck CVE-2025-55182 react2shell
 arthurhendrich/cve-2022-42475-poc
Exploit for CVE-2022-42475, a pre-auth RCE in FortiOS SSL VPN. Supports validation, benign verification, and full exploitation with connect-back…
 u20024804/bash-4.3-fixed-cve-2014-6271
Patched GNU Bash 4.3 with fix for Shellshock (CVE-2014-6271). Provides a secure Bourne Again SHell with command-line editing, job control, and…
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 dec0ne/dllnotificationinjection
A POC of a new “threadless” process injection technique that works by utilizing the concept of DLL Notification Callbacks in local and remote…
 3xpl01tc0d3r/obfuscator
The program is designed to obfuscate the shellcode.
 lesnuages/hershell
Multiplatform reverse shell generator