WordPress-HT-Contact-CVE-2025-7340-RCE

Python exploit for CVE-2025-7340, an unauthenticated file upload vulnerability in the WordPress HT Contact Form widget, enabling remote code…

Python exploit for CVE-2025-7340, an unauthenticated file upload vulnerability in the WordPress HT Contact Form widget, enabling remote code…

a exp for cve-2018-9948/9958 , current shellcode called win-calc

posix sh poc for CVE-2009-2265 (deps: curl,msfvenom,uuidgen,tr)

Mass exploit for CVE-2024-25600, uploading webshells to vulnerable WordPress sites via a list of targets.

Vbullettin RCE - CVE-2025-48827

🐍 Python Exploit for CVE-2022-46169

Rejetto HFS (HTTP File Server) is a simple web file server that facilitates file sharing over a network or the internet.

Python exploit script for CVE-2022-41544 in GetSimple CMS. Automates API key leakage, CSRF token extraction, PHP shell upload, and reverse shell…

CVE-2023-41425 Refurbish

https://www.exploit-db.com/exploits/49757

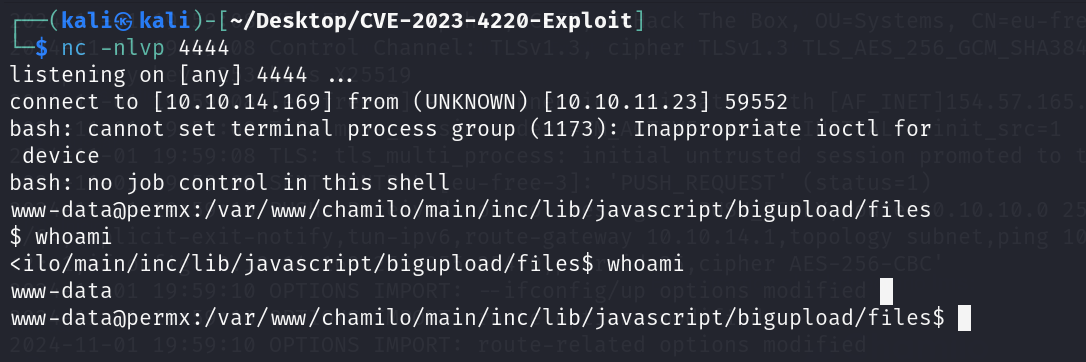
This is a script written in Python that allows the exploitation of the Chamilo's LMS software security flaw described in CVE-2023-4220

Python exploit for CVE-2022-29464 targeting WSO2 web servers with automated webshell upload and command execution capabilities.

C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode in…

Python exploit for CVE-2019-11447 that uploads a PHP reverse shell to CuteNews 2.1.2, enabling remote command execution on vulnerable web…

CVE-2023-4220 Chamilo Exploit

Automated exploit for CVE-2024-23741 targeting Hyper on macOS. Validates vulnerability and injects code to spawn a remote shell via RunAsNode and…

Go-based exploit for CVE-2025-32433

Automated exploit tool targeting CVE-2024-52010 for penetration testing and vulnerability validation.