
CVE-2024-45519
 p33d/cve-2024-45519
SMTP vulnerability scanner and exploit script that checks for CVE-2024-45519 and establishes a reverse shell on vulnerable servers.
exploitationpayload-generationpenetration-testing+3
42
p33d/cve-2024-45519SMTP vulnerability scanner and exploit script that checks for CVE-2024-45519 and establishes a reverse shell on vulnerable servers.
 aethervm/aethervm
LLVM-native binary analysis and emulation platform that lifts AArch64 and x86_64 machine code to LLVM IR for instrumentation, deobfuscation, and…
 0x00jeff/cve-2025-27591
self cleaning CVE-2025-27591 Poc that grants a root reverse shell instead of modifying passwd files
 racoten/reflectivepluginloader
Minimal Windows x64 reflective PE mapper that loads DLLs from memory without LoadLibrary, resolves exports, and dispatches calls through a…
 soralis0912/cve-2026-43499-aristotle-apk
Android kernel exploit for CVE-2026-43499 (Futex-PI use-after-free) that gains temporary root on Xiaomi XIG04 to enable ADB. Includes automated…
 hhj4ck/cve-2016-2067
GPU IOMMU DMA exploit for Android devices that overwrites vdso.so with shellcode to escalate privileges and spawn a reverse root shell on Nexus 6p.
 b0ysie7e/notepad-8.8.1_cve-2025-49144
Proof of Concept (PoC) that exploits the CVE-2025-49144 vulnerability in the Notepad++ 8.8.1 installer.
 ull0a/msrmapper
Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…
 jlsakuya/cve-2022-0847-container-escape
A simple exploit that uses dirtypipe to inject shellcode into runC entrypoint to implement container escapes.
 gmh5225/memory-relocalloc
C proof-of-concept that locates code caves in the .reloc section of mapped DLLs to allocate and execute small shellcode, replacing typical memory…
 gbonacini/cve-2026-31431
Standalone C++/x86-64 assembly implementation of CVE-2026-31431 (Copyfail) for local privilege escalation. Compiles to a dependency-free binary that…
 3x1t1um/cve-2007-2447
Python exploit for CVE-2007-2447 that triggers Samba username map script command injection to open a reverse shell on vulnerable targets.
 dahalsamir/cve-2011-2523-exploit
Python exploit for vsFTPd 2.3.4 backdoor (CVE-2011-2523) that triggers a hidden shell on port 6200 via a crafted username, enabling remote command…
 zerx0r/dvenom
🐍 Double Venom (DVenom) is a tool that provides an encryption wrapper and loader for your shellcode.
 optiv/mangle
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
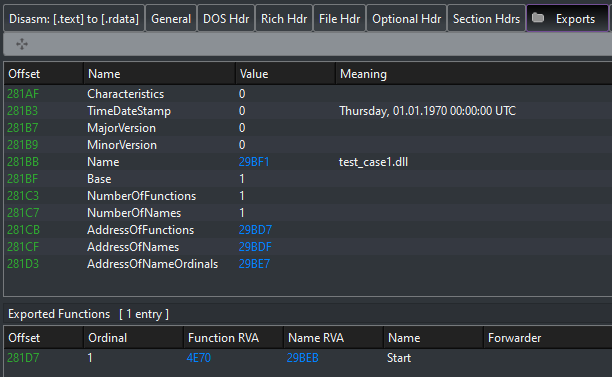 hasherezade/exe_to_dll
Converts a EXE into DLL
 nickvourd/supernova
Multi-cipher shellcode encryptor and obfuscator with automatic output conversion to C, C#, Rust, Nim, Python, and more. Supports ROT, XOR, RC4, AES,…