

 rek7/postshell
PostShell - Post Exploitation Bind/Backconnect Shell
 klezvirus/rpcproxyinvoke
Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar
 epotseluevskaya/aspx_webshell_coffloader
ASPX web shell with COFF loader for executing Beacon Object Files (BOFs) on target servers via a semi-interactive Python client, designed for…
 ariary/volana
🌒 Shell command obfuscation to avoid detection systems
 choisg/onedriveupdatersideloading
Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post

 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)
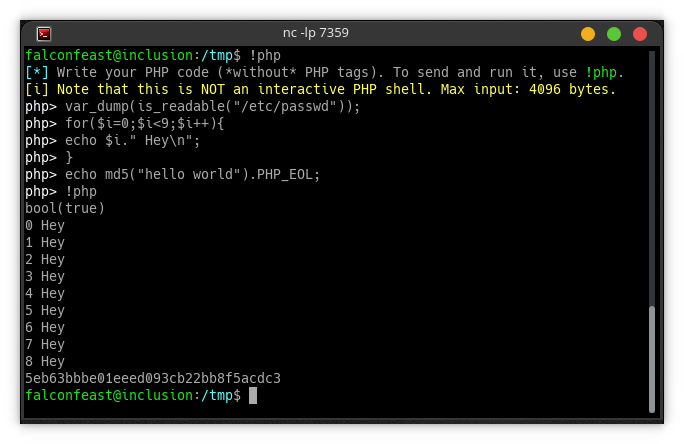 nickguitar/yaps
Yet Another PHP Shell - The most complete PHP reverse shell

 0xsp-srd/aether
Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
 nul0x4c/manualrsrcdatafetching
Get your data from the resource section manually, with no need for windows apis
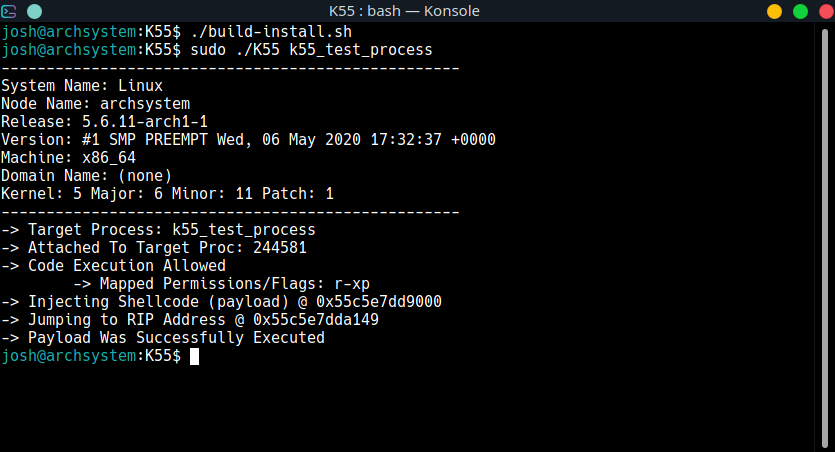
 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 schich/lucky-spark
A stealthy stager designed for shellcode payloads staged with http/https like Sliver, or on github raw.
 boogipop/cve-2023-22527-godzilla-memshell
CVE-2023-22527 内存马注入工具
 chaelsoo/nimcrypt
Nim-based encryption tool for obfuscating shellcode and payloads for evading Windows Defender.
 gildasio/wshlient
A simple tool to interact with web shells and command injection vulnerabilities