
CVE-2023-41425
 xpltive/cve-2023-41425
WonderCMS v3.2.0 - v3.4.2 XSS to RCE exploit
exploitationpayload-generationpenetration-testing+3
11 year ago
xpltive/cve-2023-41425WonderCMS v3.2.0 - v3.4.2 XSS to RCE exploit
 somisec/cve-2024-28397-reverse-shell
Reverse shell for CVE-2024-28397.
 3x1t1um/cve-2007-2447
Python exploit for CVE-2007-2447 that triggers Samba username map script command injection to open a reverse shell on vulnerable targets.
 0xryuk/cve-2022-24637
Open Web Analytics 1.7.3 - Remote Code Execution Exploit v2
 giovannipajeu1/cve-2024-23738
Proof-of-concept exploit for CVE-2024-23738 targeting Postman on macOS. Automates vulnerability detection and code injection via Electron settings to…
 giovannipajeu1/cve-2024-23742
Proof-of-concept exploit for CVE-2024-23742 in Loom for macOS. Validates vulnerability and injects arbitrary code via RunAsNode settings to gain a…
 pr1or95/cve-2023-4220-exploit
Carga de archivos sin restricciones en la funcionalidad de carga de archivos grandes en `/main/inc/lib/javascript/bigupload/inc/bigUpload.php` en…
 g01d3nw01f/cve-2015-8351
this script is exploit for wordpress old plugin gwolle
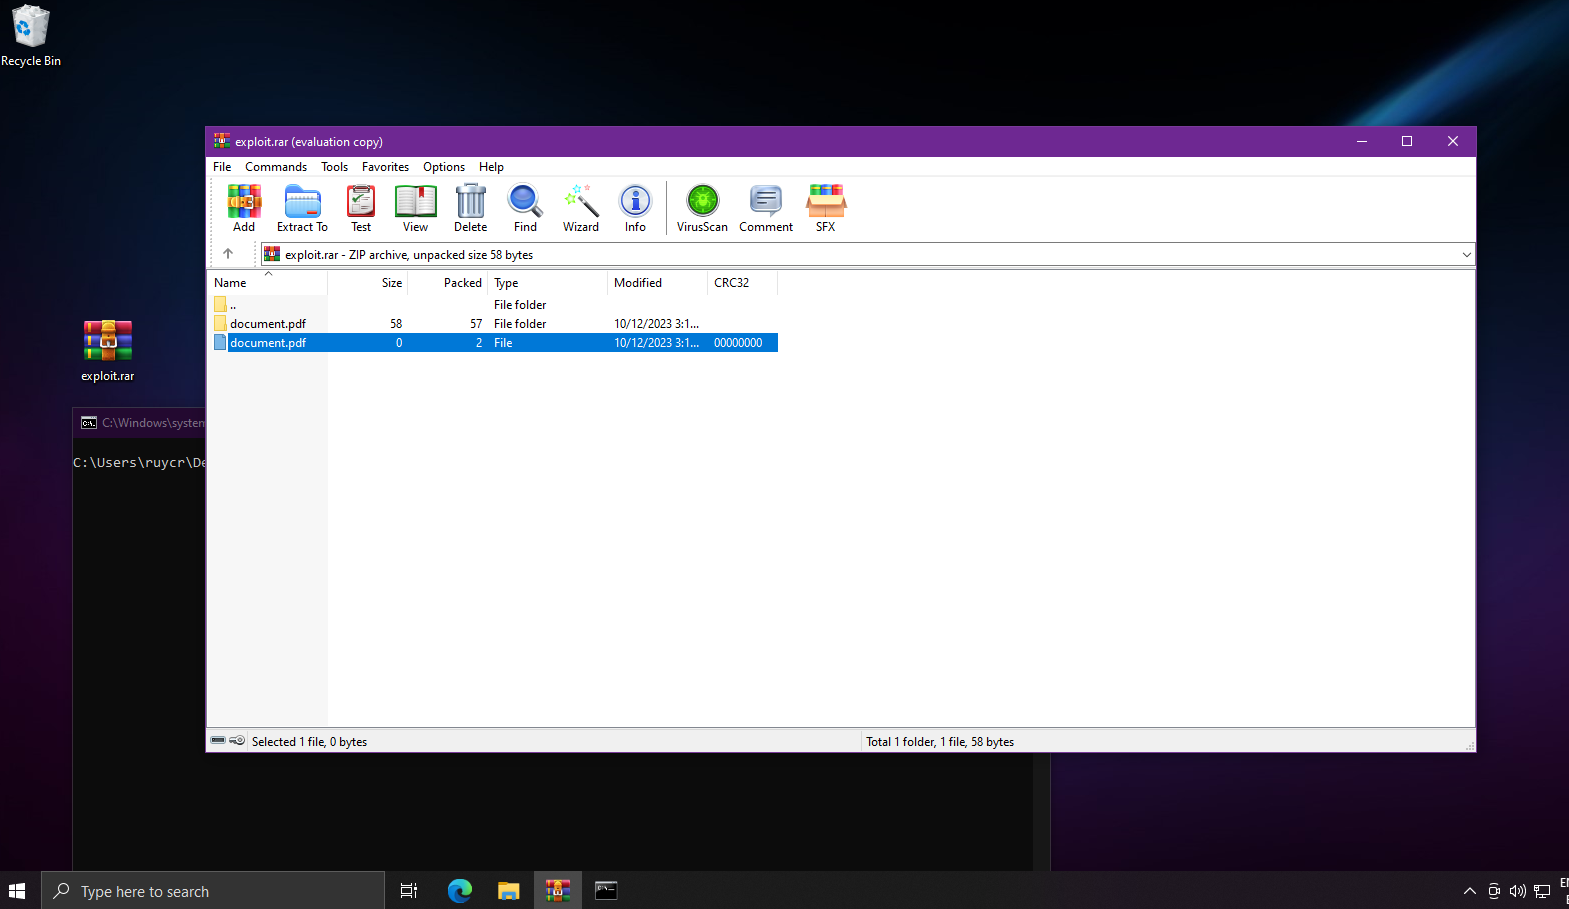 ruycr4ft/cve-2023-38831
Proof-of-concept exploit for CVE-2023-38831 targeting vulnerable versions, delivering a reverse shell via automated exploitation.
 giovannipajeu1/cve-2024-23743
Automated exploit tool for CVE-2024-23743 targeting Notion macOS via RunAsNode and enableNodeClilnspectArguments, enabling remote code execution and…
 skyw4r33x/cve-2023-4226
Vulnerabilidad de carga de archivos sin restricciones en **Chamilo LMS** (<= v1.11.24).
 cristibtz/cve-2025-62369
This script exploits CVE-2025-62369 in Xibo CMS to execute a reverse shell command.
 schn1tzelme1ster/cve-2025-6002
Python exploit for CVE-2025-6002 targeting authenticated arbitrary file upload in VirtueMart < 4.4.10. Logs in, uploads a PHP webshell, and triggers…
 btar1gan/exploit_cve-2024-39205
Exploit for CVE-2024-39205, a js2py sandbox escape that enables remote code execution and establishes a reverse shell.
 amkkk221/cve-2025-43990-magento-rce
Magento APSB25-94 Unauthenticated File Upload to RCE (CVE-2026-XXXX) - Eval Shell + Probe Scanner
 1lkla/poc-exploit-for-dolibarr
POC exploit for Dolibarr <= 17.0.0 (CVE-2023-30253)
 notrustedx/exploit_ms08-067
MS08-067 | CVE-2008-4250
 ruthvikvegunta/drupalgeddon2
CVE-2018-7600 | Drupal < 7.58 / < 8.3.9 / < 8.4.6 / < 8.5.1 - 'Drupalgeddon2' RCE