
CVE-2024-6387
 yassdev221608/cve-2024-6387
Python exploit for CVE-2024-6387 (OpenSSH signal handler race condition) targeting glibc-based 32-bit Linux systems, with multi-threaded concurrency…
binary-exploitationexploitationpayload-development+3
yassdev221608/cve-2024-6387Python exploit for CVE-2024-6387 (OpenSSH signal handler race condition) targeting glibc-based 32-bit Linux systems, with multi-threaded concurrency…
 jedai47/cve-2017-16994
Linux kernel local privilege escalation exploit for CVE-2017-16994, leveraging null pointer dereference and mmap_min_addr bypass to achieve root…
 shard77/blackpill
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 owasp/zsc
OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/
 n00py/hwacha
Deploy payloads to *Nix systems en masse
 jm00nj/phantom-evasion-loader
x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 juanbindez/cve-2026-31431
Copy Fail - CVE-2026-31431
 cyb3r-techie/pezor-docker
With the help of this docker image, you can easily access PEzor on your system!
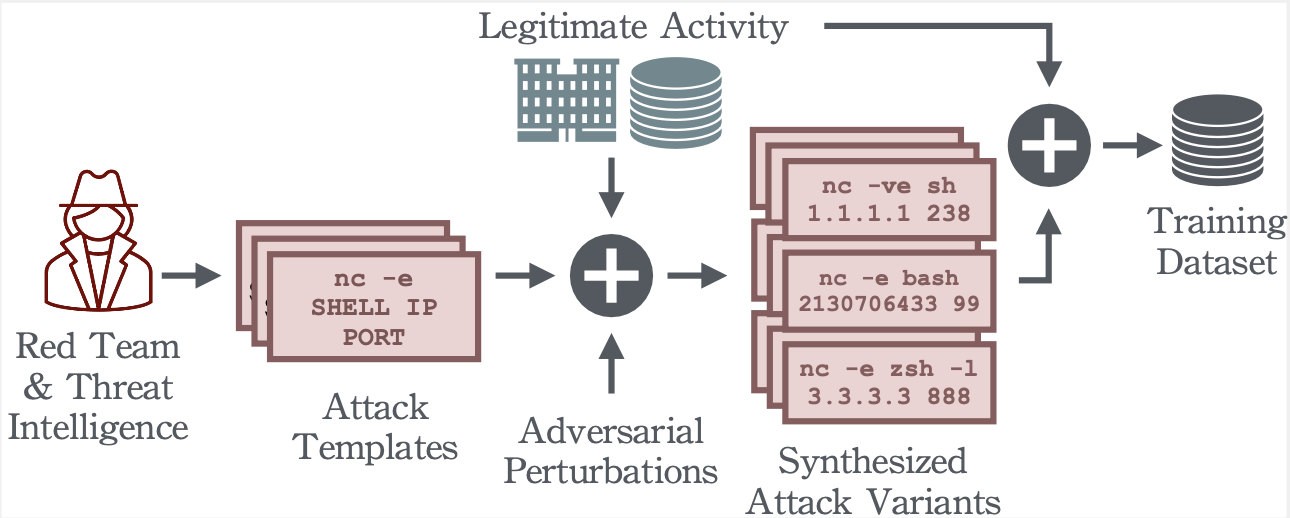 dtrizna/quasarnix
Reverse Shell Detection with Machine Learning
 jarpex/cve-2023-4911-exploit-optimized
Pure C exploit for CVE-2023-4911 (Looney Tunables) — x86_64 & aarch64 implementations. Multi-processing brute-forcing, dynamic calibration,…
 sudoytang/copyfail-arm64
Analysis and ARM64 reproduction of Copy Fail (CVE-2026-31431)
 pankass/cve-2024-37032_cve-2024-45436
CVE-2024-45436
 madfxr/cve-2024-26581-checker
[CVE-2024-26581] Vulnerability Checker for BGN Internal
 ivanitlearning/cve-2018-12613
Modified standalone exploit ported for Python 3
 morgenm/dirtypipe
DirtyPipe (CVE-2022-0847) exploit written in Rust