
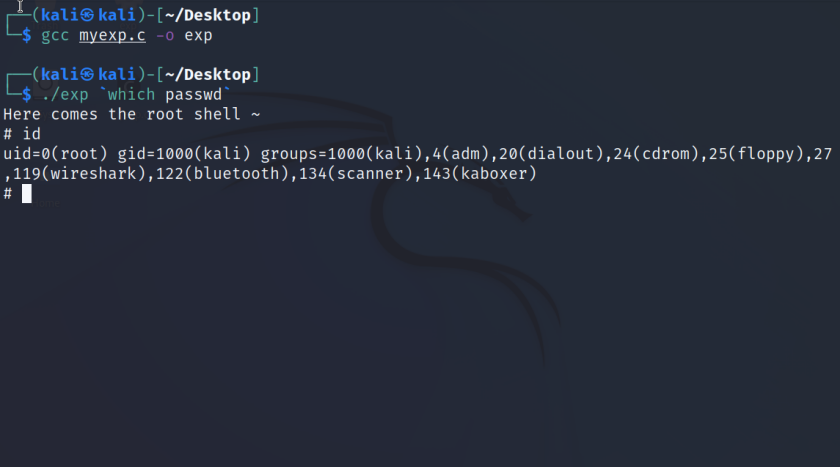
Dirty-Pipe
 rabomen/dirty-pipe
exp of CVE-2022-0847
binary-exploitationexploitationpayload-development+3
rabomen/dirty-pipeexp of CVE-2022-0847
 sh4den/cve-2022-31814
Proof of concept for CVE-2022-31814
 gkweb76/exploits
Collection of shellcode and proof-of-concept exploits for known vulnerabilities, intended for local testing and verifying software or network…
 szerszen199/ps-cve-2020-7352
Powershell implemetation of CVE-2020-7352
 nu11secur1ty/metasploit-framework-nu11secur1ty
Extending of metasploit-framework
 maorbuskila/windows-x64-rat
Remote Access Trojan (RAT) for Windows x64 using a combination of vulnerability CVE-2023-38831 (WinRAR < 6.23 vulnerability) and Shellcode…
 nonameuserosint-hue/copyfail-sh
A Bash implementation of copyfail (CVE-2026-31431)
 koshmare-blossom/pintheft-asm
A x86_64 ASM implementation of PinTheft (CVE-2026-43494)
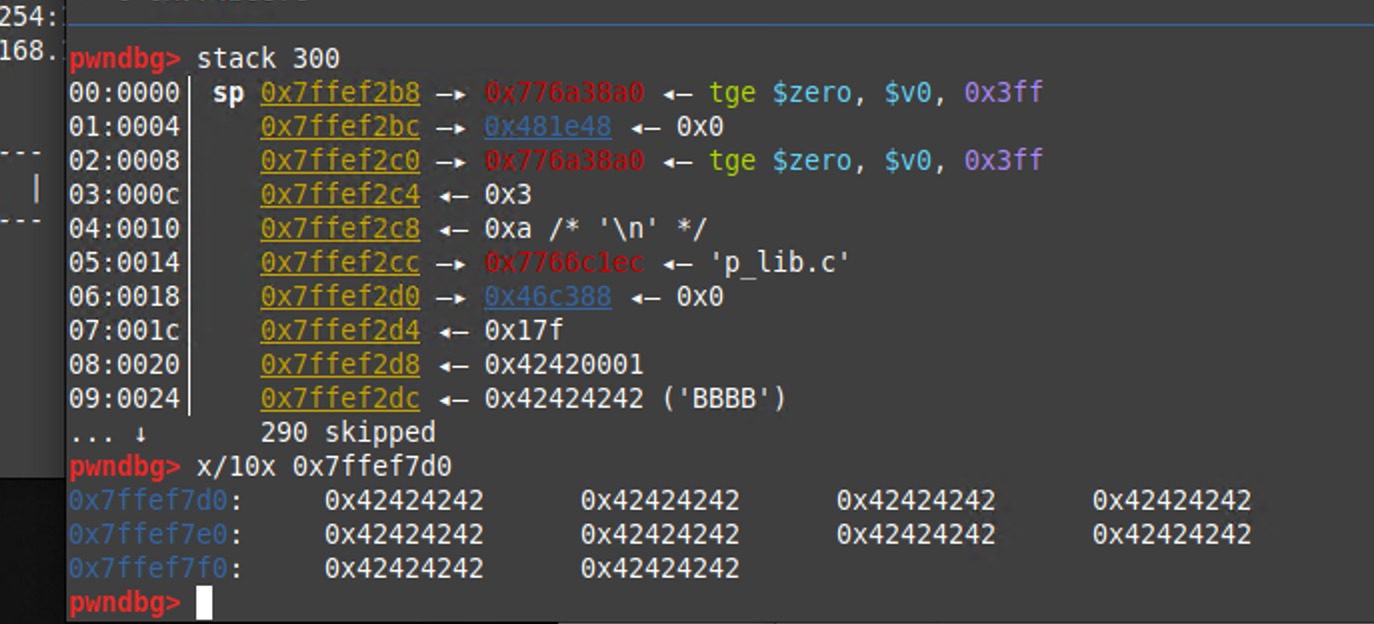 laskdjlaskdj12/cve-2024-29671-poc
This is POC of CVE-2024-29671
 diego57709/cve-2025-5548
Structured lab for controlled exploitation of CVE-2025-5548 (FreeFloat FTP Server). Includes environment setup, fuzzing, EIP control, badchars…
 alberto-galindo/cve-2025-5548
Security research and reproduction of CVE-2025-5548: A stack-based buffer overflow in FreeFloat FTP Server 1.0. Includes binary analysis, crash…
 charlyrr/cve-2025-5548
Educational lab documenting step-by-step exploitation of CVE-2025-5548 (Stack Buffer Overflow) on Windows 11, from fuzzing and crash analysis to…
 qduarte-42/rainfall
Introduction to the exploitation of ELF binaries.
 orf53975/rig-exploit-for-cve-2018-8174
Rig Exploit for CVE-2018-8174 As with its previous campaigns, Rig’s Seamless campaign uses malvertising. In this case, the malvertisements have a…
 jeromeyoung/cve-2021-27965
Proof of concept for CVE-2021-27965 (Stack-based Buffer Overflow)
 svchostmm/cve-2024-25600-mass
Mass exploit for CVE-2024-25600, uploading webshells to vulnerable WordPress sites via a list of targets.
 rnnsz/cve-2017-8367
Python-based proof-of-concept exploit for CVE-2017-8367, a stack-based buffer overflow in Easy Mov Converter. Generates a payload file for local…
 pwncone/cve-2004-2271-minishare-1.4.1-bof
A python implementation of CVE-2004-2271 targeting MiniShare 1.4.1.