
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
275 results
Voidgate preview

Voidgate

GitHubvxcrypt0r/voidgate

A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…
adversarial-attackdebuggersids-ips-evasion+3
596
2 years ago
phantom-frida preview

phantom-frida

GitHubtheqmaks/phantom-frida

Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
android-securitybinary-analysisdynamic-analysis-sandboxing+7
3812 months ago
LazySign preview

LazySign

GitHubjfmaes/lazysign

Create fake certs for binaries using windows binaries and the power of bat files
binary-analysisdefensive-toolsimpersonation-tools+6
5692 years ago
shellnoob preview

shellnoob

GitHubreyammer/shellnoob

A shellcode writing toolkit

binary-analysisdebuggerseducation+6
6961 year ago
sharem preview

sharem

GitHubbw3ll/sharem

SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…

ai-securitybinary-analysisdebuggers+5
4936 months ago
shells preview

shells

GitHub4ndr34z/shells

Script for generating revshells

command-and-controlctfeducation+9
4872 years ago
NimPackt-v1 preview

NimPackt-v1

GitHubchvancooten/nimpackt-v1

Nim-based assembly packer and shellcode loader for opsec & profit
binary-exploitationexploit-frameworkspayload-generation+3
4863 years ago
spawn preview

spawn

GitHubboku7/spawn

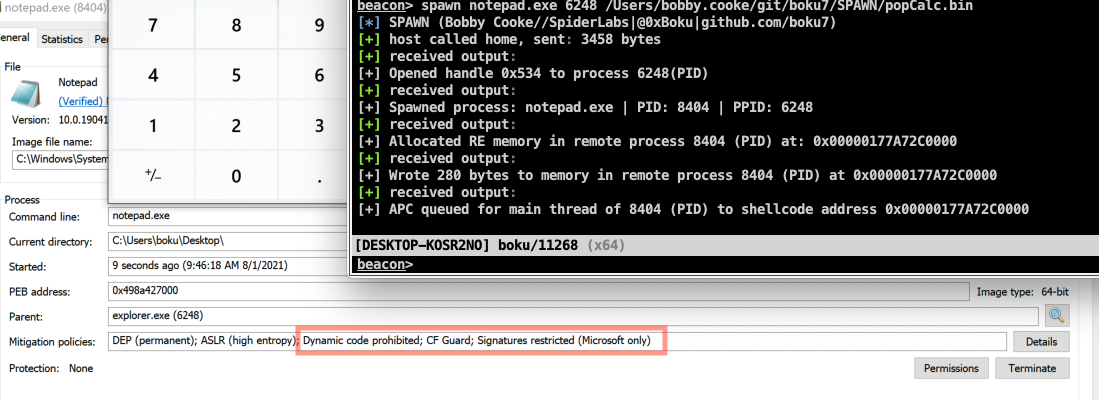
Cobalt Strike BOF that spawns a sacrificial process, injects it with shellcode, and executes payload. Built to evade EDR/UserLand hooks by spawning…
command-and-controlexploitationpayload-development+5
4643 years ago
ropium preview

ropium

GitHubboyan-milanov/ropium

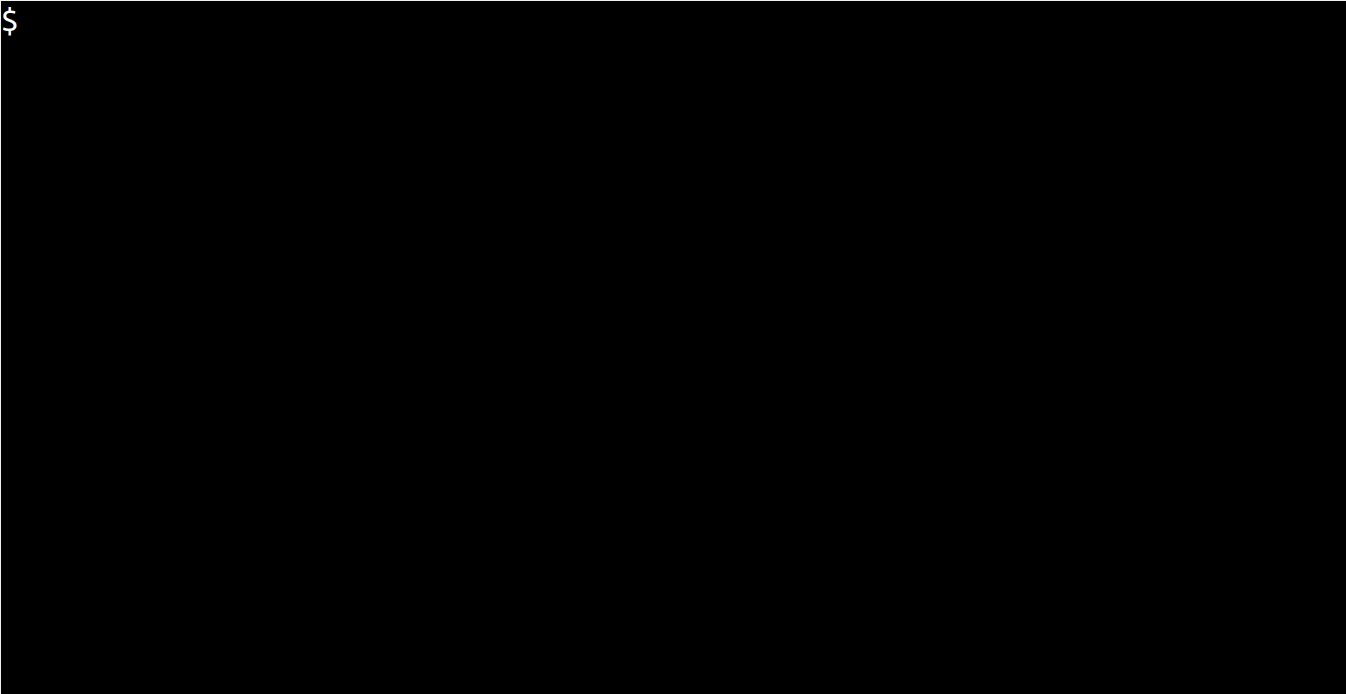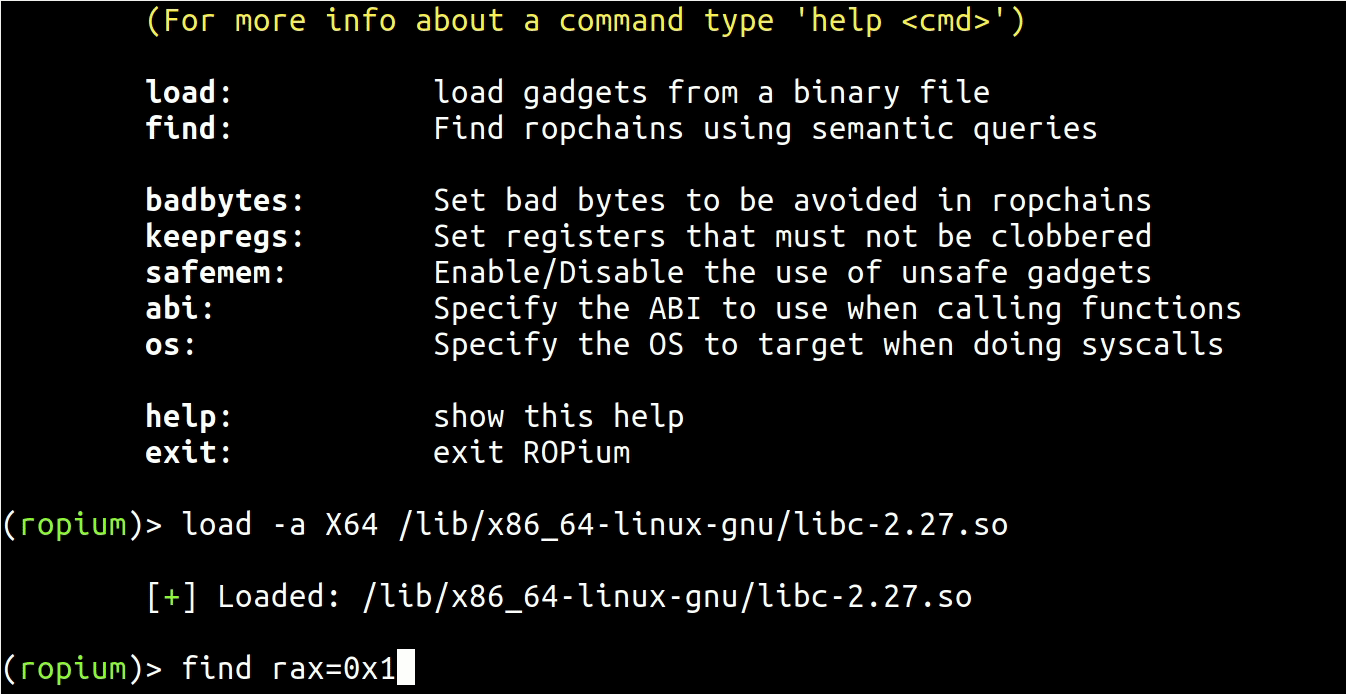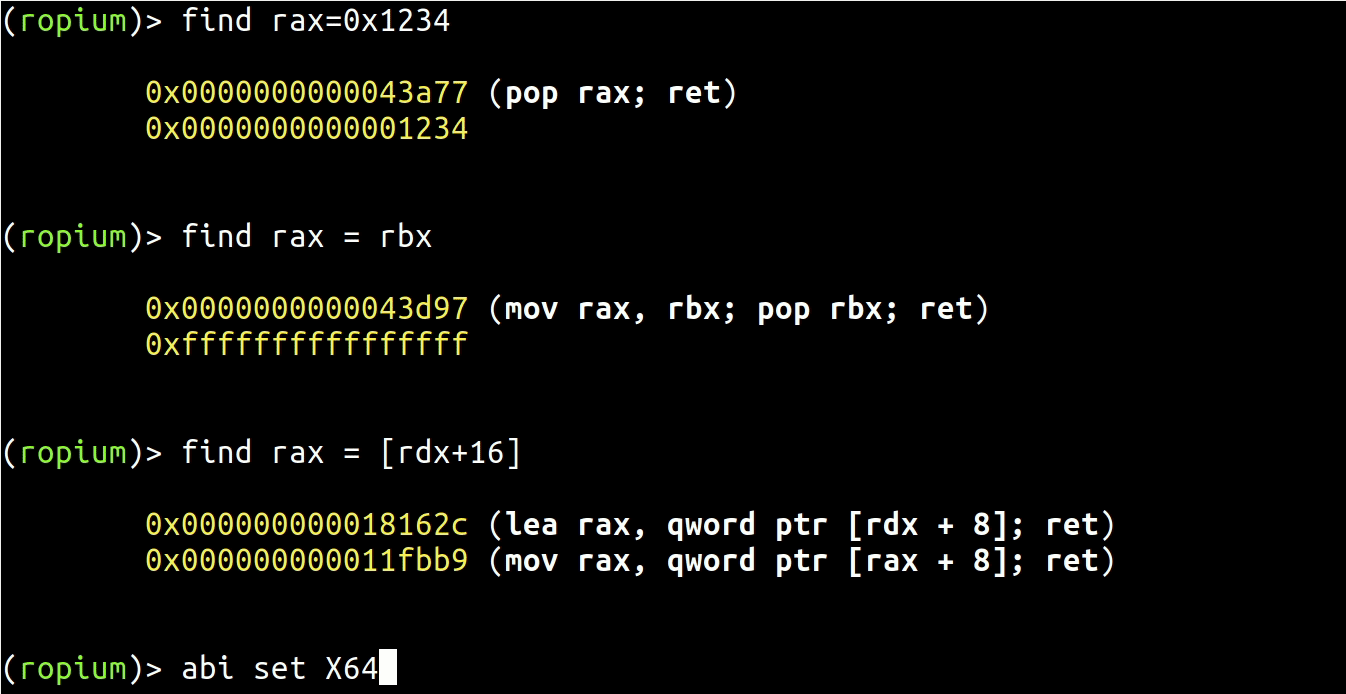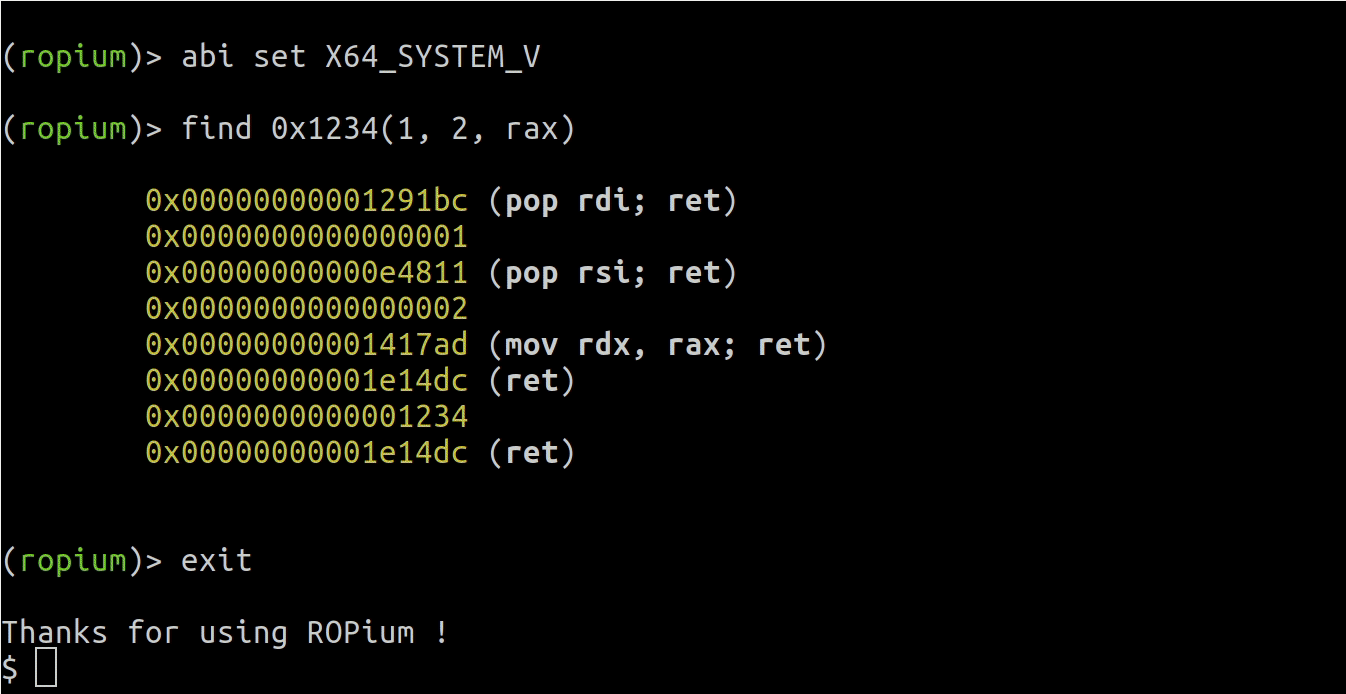
Automated ROP chain builder that extracts and analyzes gadgets from binaries using semantic queries, supporting X86/X64 architectures with a Python…

binary-exploitationexploit-frameworkspayload-development+2
4024 years ago
Shellcode-Hide preview

Shellcode-Hide

GitHubsaadahla/shellcode-hide

This repo contains : simple shellcode Loader , Encoders (base64 - custom - UUID - IPv4 - MAC), Encryptors (AES), Fileless Loader (Winhttp, socket)
cryptographyencryption-decryption-toolsids-ips-evasion+4
4393 years ago
anamnesis-release preview

anamnesis-release

GitHubseanheelan/anamnesis-release

Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
ai-securitybinary-exploitationeducation+9
6347 months ago
monomorph preview

monomorph

GitHubdavidbuchanan314/monomorph

MD5-Monomorphic Shellcode Packer - all payloads have the same MD5 hash

binary-exploitationcryptographyexploitation+5
7913 years ago
RedPeanut preview

RedPeanut

GitHubb4rtik/redpeanut

RedPeanut is a small RAT developed in .Net Core 2 and its agent in .Net 3.5 / 4.0.

command-and-controlexploit-frameworkspayload-generation+7
3306 years ago
Java-Shellcode-Loader preview

Java-Shellcode-Loader

GitHubyzddmr6/java-shellcode-loader

基于Java实现的Shellcode加载器
payload-developmentpenetration-testingred-teaming+1
4143 years ago
metasm preview

metasm

GitHubjjyg/metasm

This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby
binary-analysiscode-analysisdebuggers+2
4756 months ago
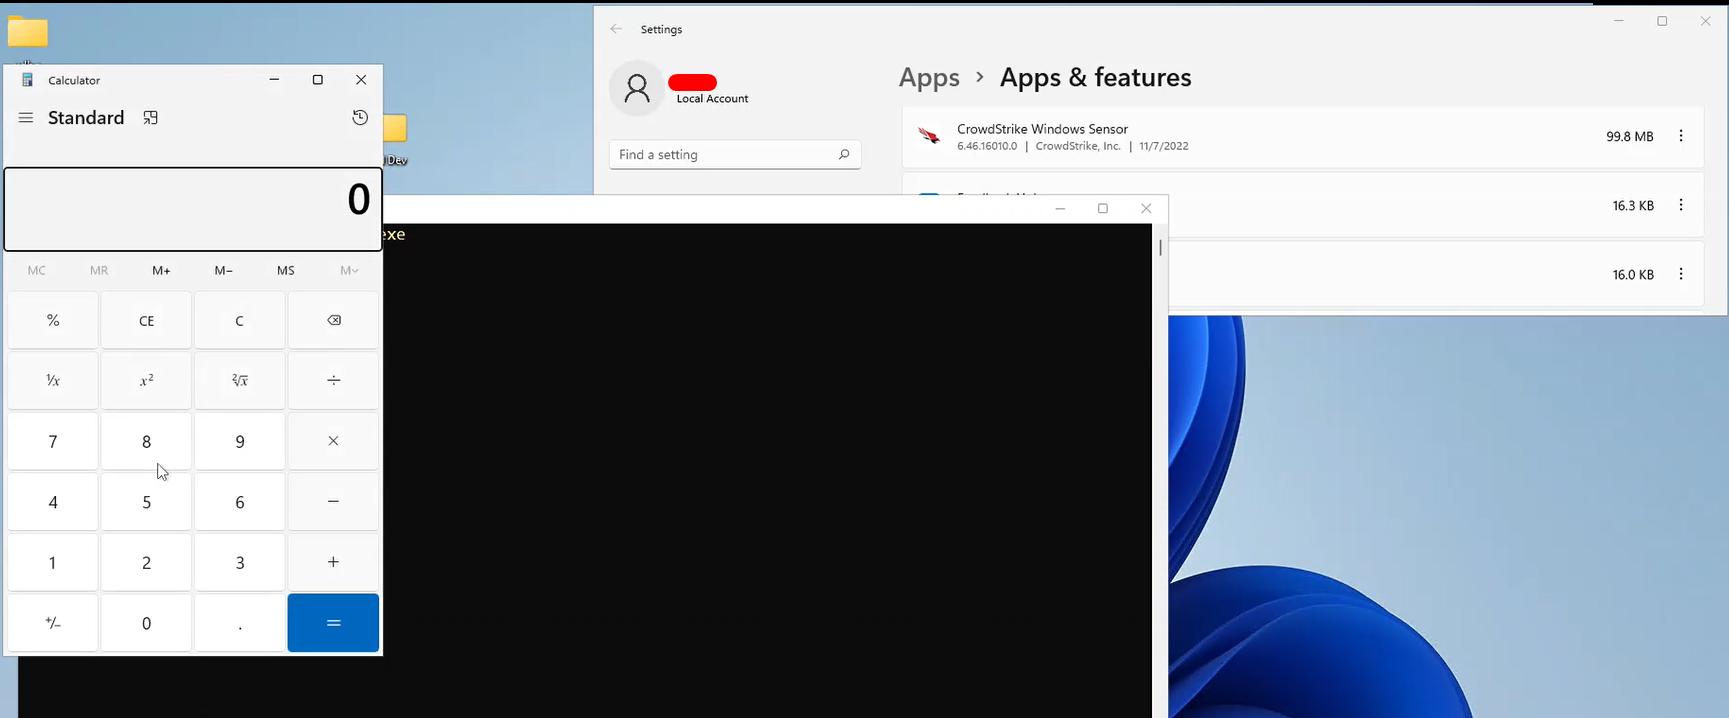
D1rkLdr preview

D1rkLdr

GitHubsaadahla/d1rkldr

Shellcode Loader with Indirect Dynamic syscall Implementation , shellcode in MAC format, API resolving from PEB, Syscall calll and syscall…
ids-ips-evasionpayload-developmentred-teaming+1
3223 years ago
ropr preview

ropr

GitHubben-lichtman/ropr

A blazing fast™ multithreaded ROP Gadget finder. ropper / ropgadget alternative (currently x86 only)

binary-analysisexploitationreverse-engineering+1
5585 months ago
frostbyte preview

frostbyte

GitHubpwn1sher/frostbyte

Combines AppDomain Manager injection with shellcode embedding in signed binaries to evade EDR/AV detection for red team payloads.

shellcodeshellcode-generation
3824 years ago
Previous1…456…16Next