
CVE-2022-3552
 bakalmode/cve-2022-3552
CVE-2022-3552 RCE with detailed exploitation steps
exploitationpayload-generationpenetration-testing+3
21 year ago
bakalmode/cve-2022-3552CVE-2022-3552 RCE with detailed exploitation steps
 gagaltotal/cve-2026-48908-sp-page-builder-joomla
CVE-2026-48908 - SP Page Builder Joomla Unauthenticated RCE
 blackjuker2/cve-2019-0232
Apache Tomcat CGI Servlet RCE (Windows)
 sh4den/cve-2022-31814
Proof of concept for CVE-2022-31814
 mlgzackfly/cve-2026-6643
ASUSTOR ADM 5.1.2 vpnupload.cgi Format String & Stack Buffer Overflow RCE (CVE-2026-6643)
 xpltive/cve-2023-41425
WonderCMS v3.2.0 - v3.4.2 XSS to RCE exploit
 themalwareguardian/cve-2020-13768
Stack-based buffer overflow in MiniShare 1.4.1 reachable through a single HTTP PUT request.
 1lkla/poc-exploit-for-dolibarr
POC exploit for Dolibarr <= 17.0.0 (CVE-2023-30253)
 schn1tzelme1ster/cve-2025-6002
Python exploit for CVE-2025-6002 targeting authenticated arbitrary file upload in VirtueMart < 4.4.10. Logs in, uploads a PHP webshell, and triggers…
 innocentx0/cve-2015-6967-exploit
CVE-2015-6967 PoC Exploit
 h3x0v3rl0rd/cve-2022-41544
Python exploit script for CVE-2022-41544 in GetSimple CMS. Automates API key leakage, CSRF token extraction, PHP shell upload, and reverse shell…
 gazettel/cve-2020-24186
Exploit script for CVE-2020-24186 in WordPress that uploads a camouflaged PHP webshell and provides interactive or reverse shell access with optional…
 0xdtc/wondercms-4.3.2-xss-to-rce-exploits-cve-2023-41425
CVE-2023-41425 Refurbish
 yassdev221608/cve-2024-6387
Python exploit for CVE-2024-6387 (OpenSSH signal handler race condition) targeting glibc-based 32-bit Linux systems, with multi-threaded concurrency…
 nobodyatall648/cve-2009-0182
CVE-2009-0182 VUPlayer2.49_LocalBufferOverflow
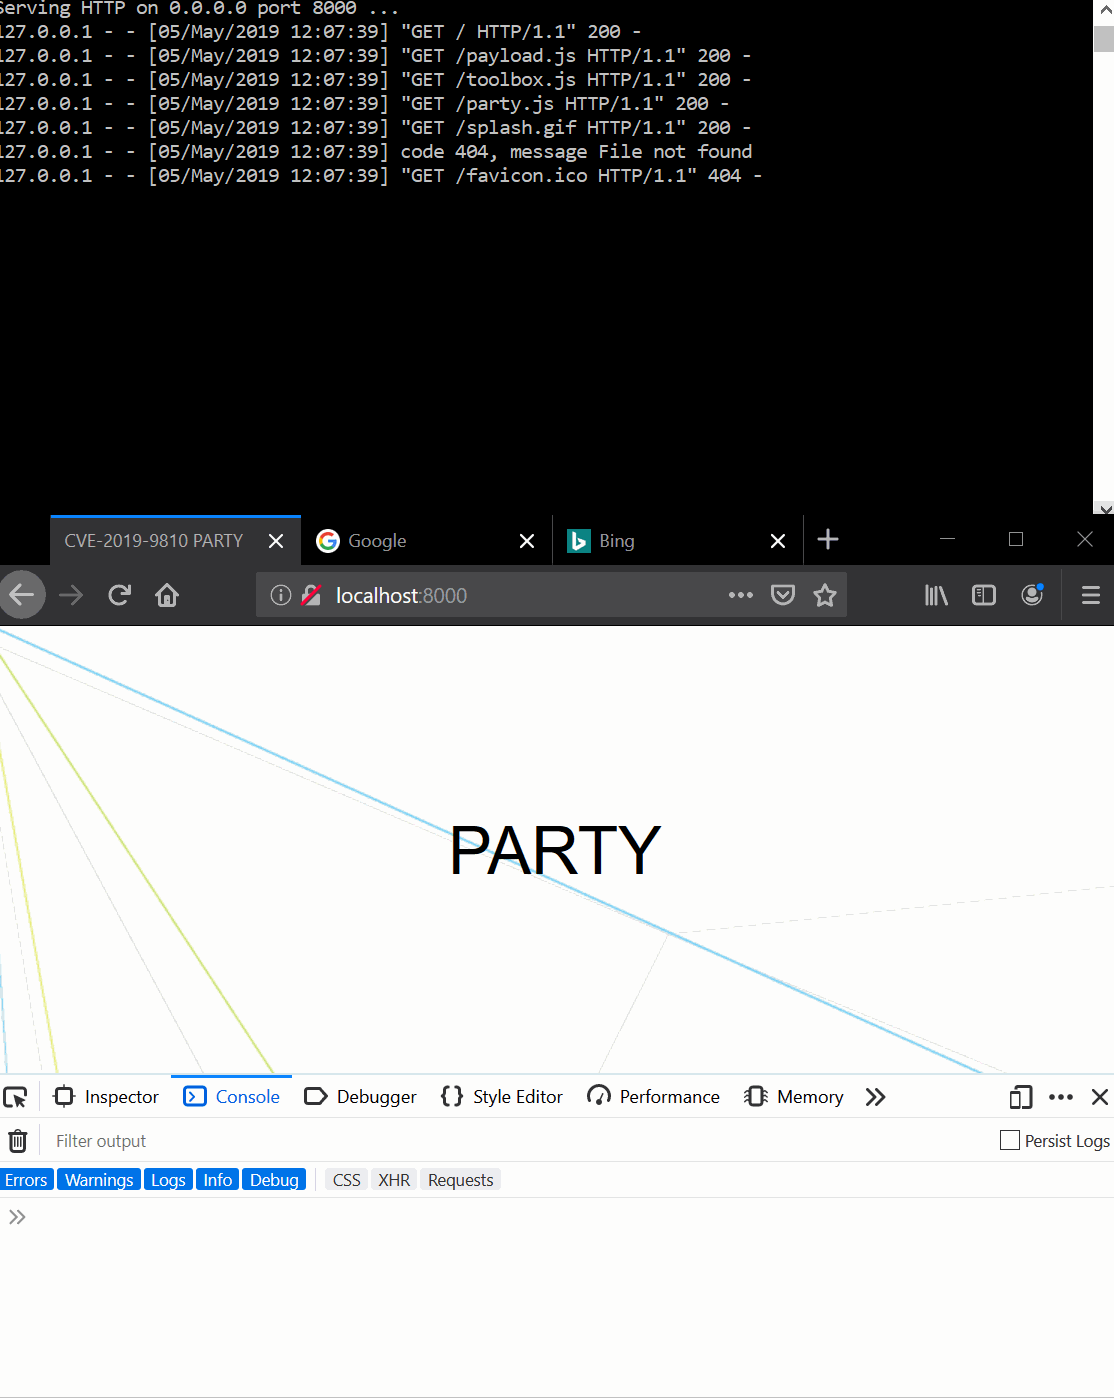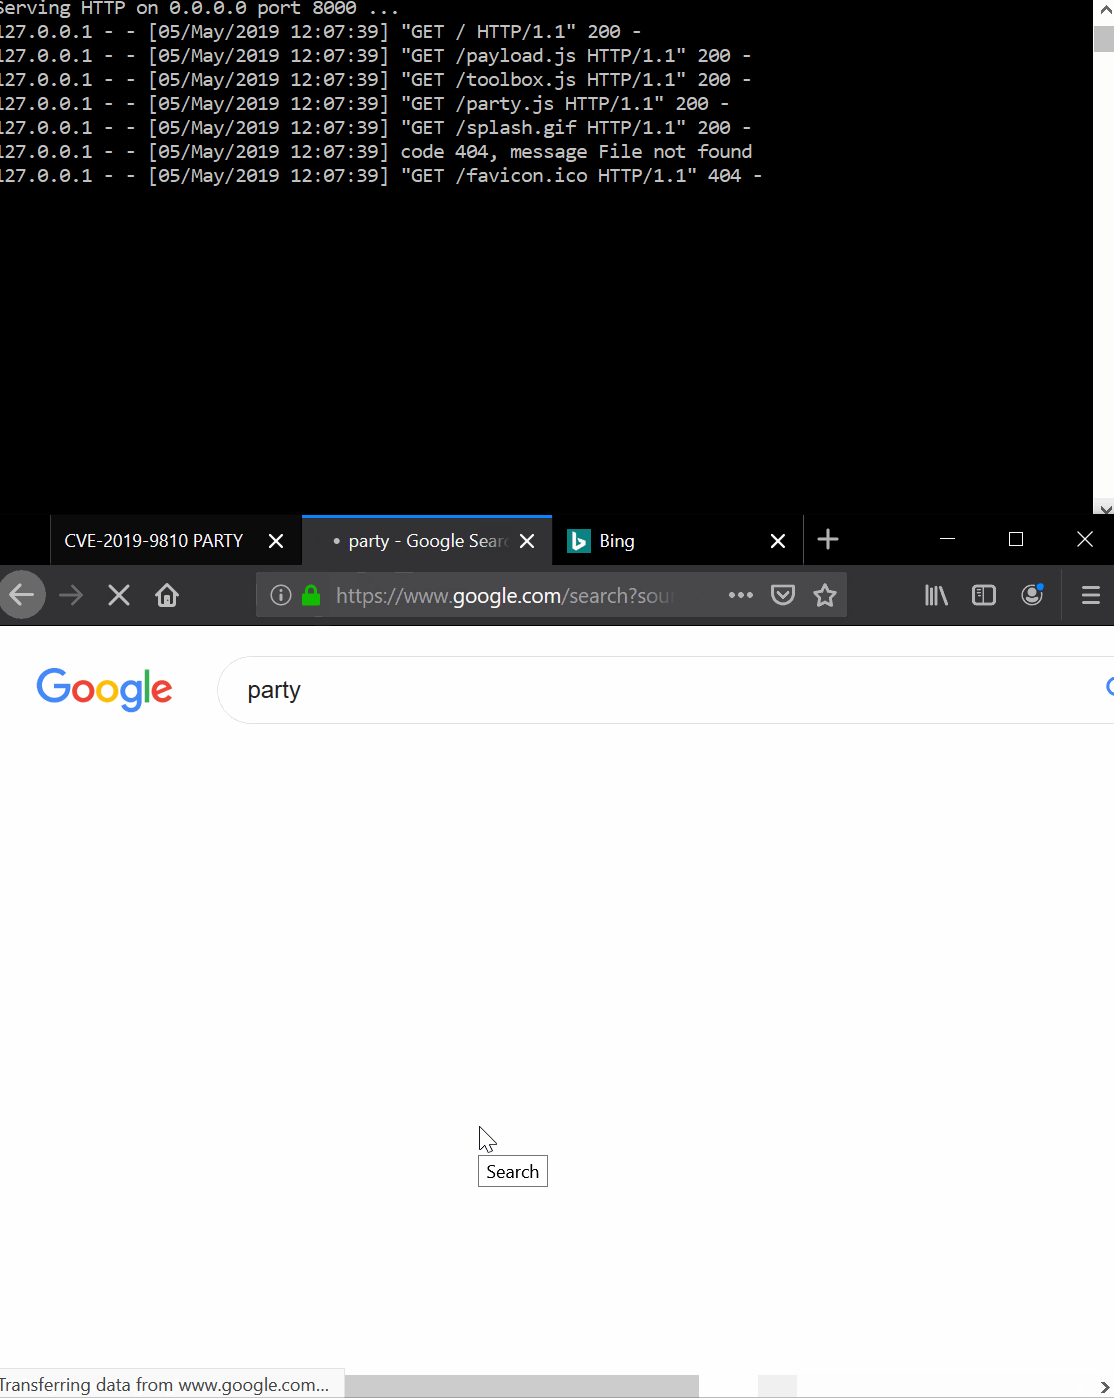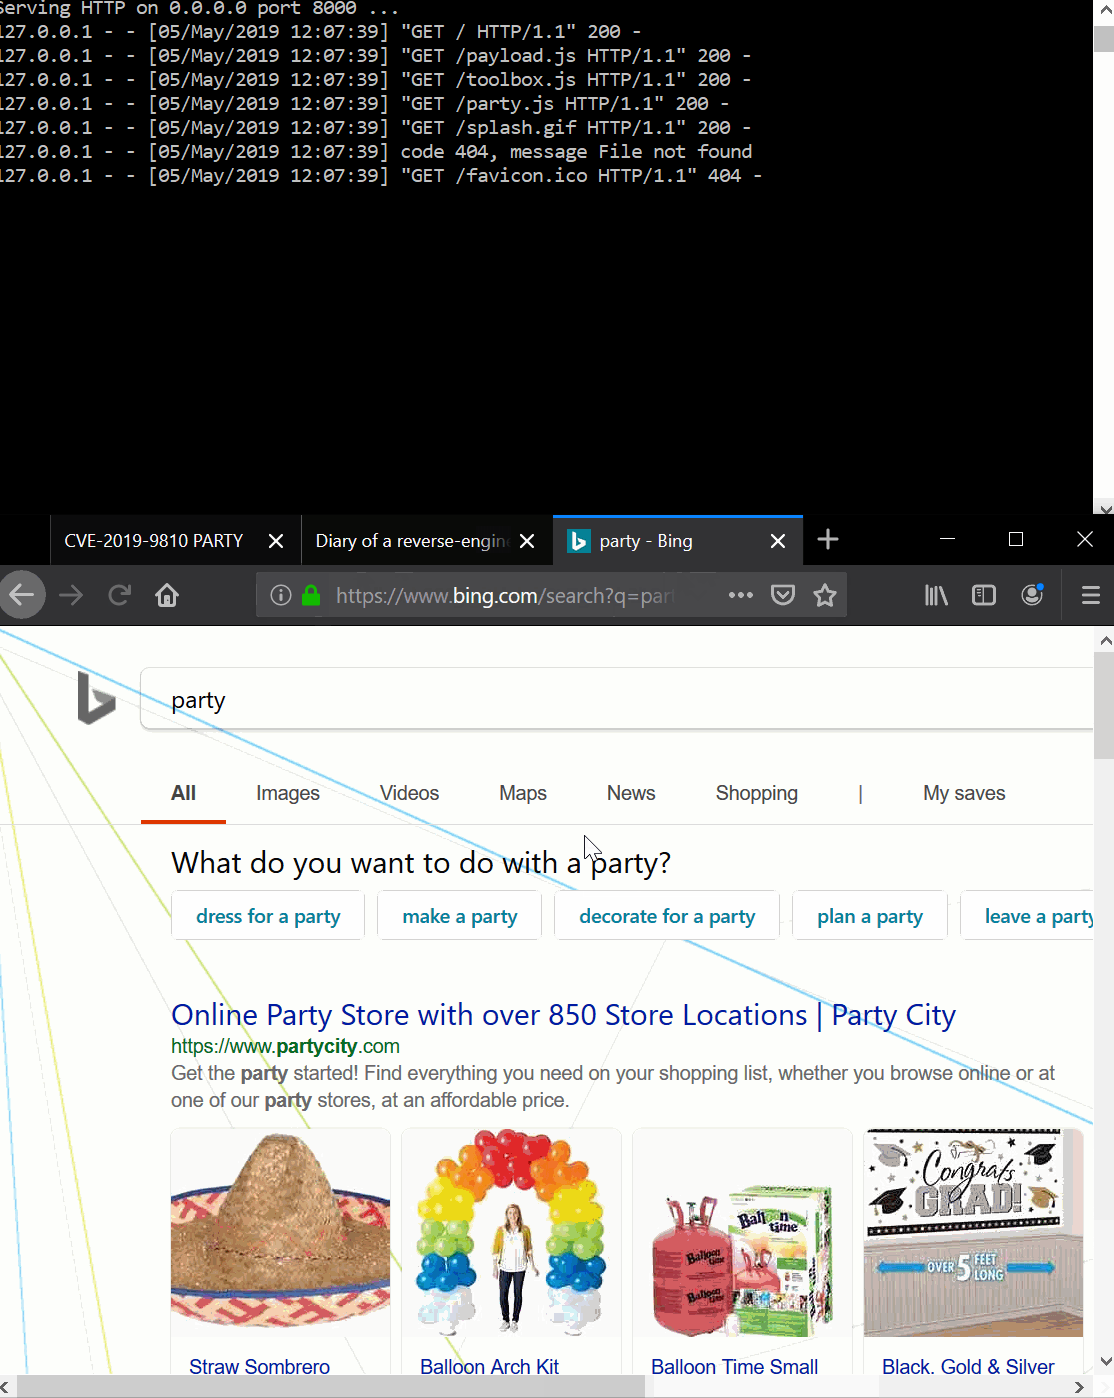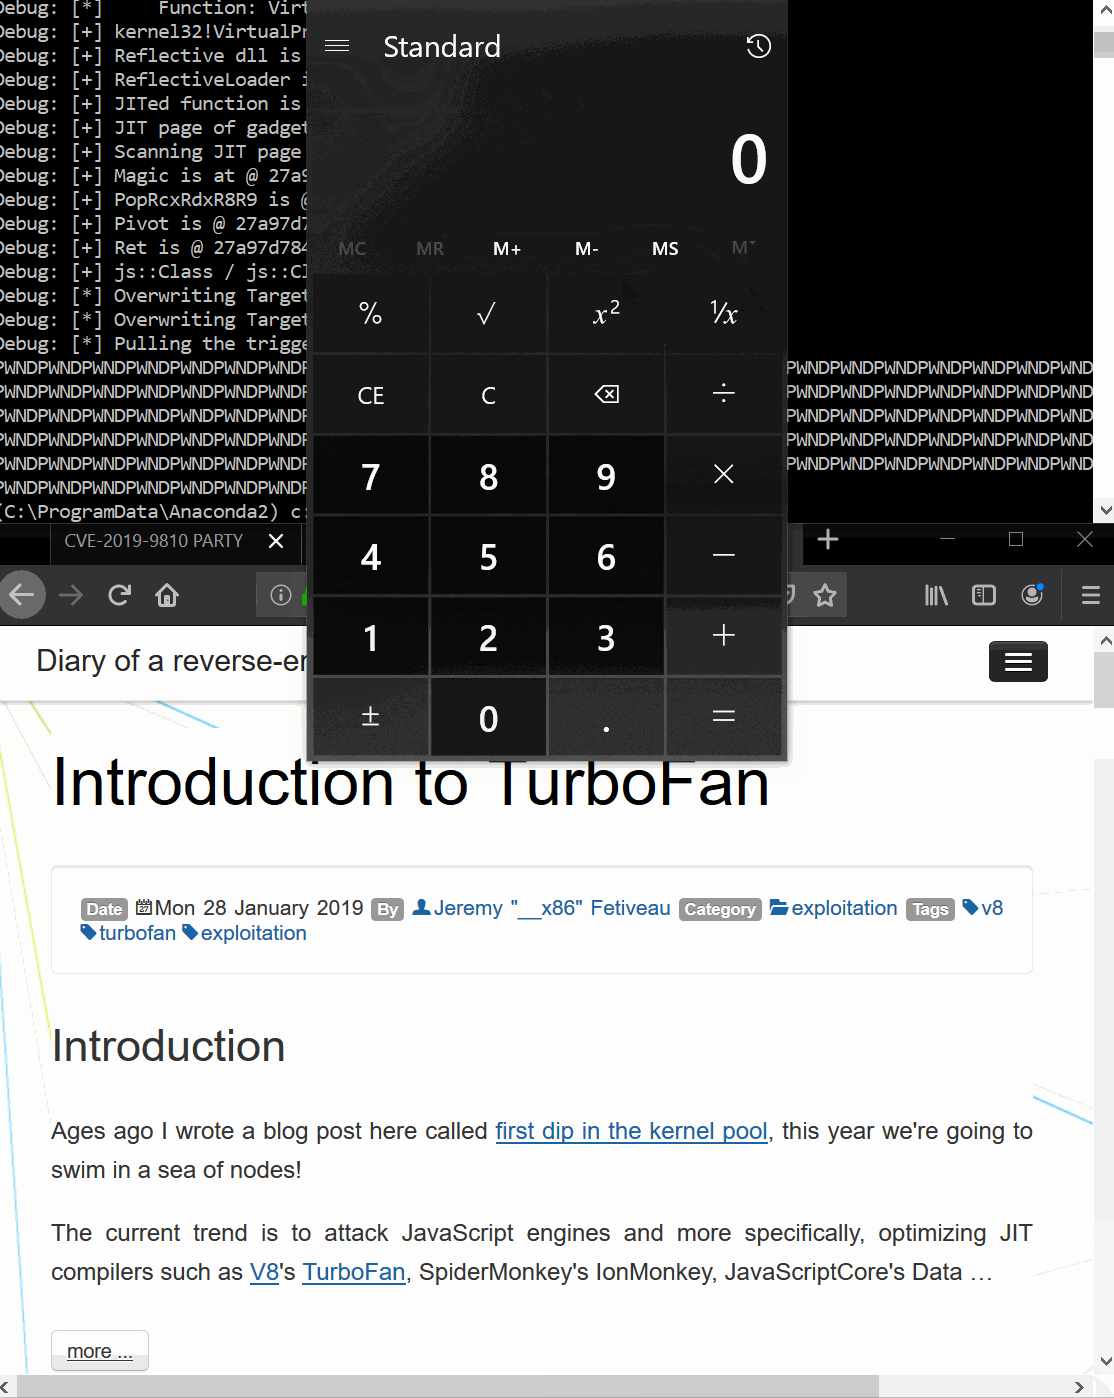 0vercl0k/cve-2019-9810
Exploit for CVE-2019-9810 Firefox on Windows 64-bit.
 zhzyker/exphub
Exphub[漏洞利用脚本库] 包括Webloigc、Struts2、Tomcat、Nexus、Solr、Jboss、Drupal的漏洞利用脚本,最新添加CVE-2020-14882、CVE-2020-11444、CVE-2020-10204、CVE-2020-10199、CVE-2020-1938…
 jenderal92/cve-2026-48908
CVE-2026-48908 — PoC exploit for unauthenticated RCE in SP Page Builder (Joomla) via arbitrary file upload. Multi‑threaded, case‑bypass, shell…