
Partial-deobfuscated-sc-from-HackingTeam-Malware.-
 spiralbl0ck/partial-deobfuscated-sc-from-hackingteam-malware.-
This repo stores necessary files for the analysis blog which will come soon
binary-analysiseducationmalware-analysis+3
spiralbl0ck/partial-deobfuscated-sc-from-hackingteam-malware.-This repo stores necessary files for the analysis blog which will come soon
 popclom/cve-2025-5548
Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
 lorenzoporrasduque/cve-2025-5548-poc
Educational lab demonstrating a stack buffer overflow (CVE-2025-5548) in FreeFloat FTP Server. Covers full exploit development: vulnerability…
 alberto-galindo/cve-2025-5548
Security research and reproduction of CVE-2025-5548: A stack-based buffer overflow in FreeFloat FTP Server 1.0. Includes binary analysis, crash…
 jsantos1990/cve-2025-5548
🚀 Complete analysis and exploitation of CVE-2025-5548 (FreeFloat FTP Server 1.0 - NOOP Buffer Overflow) Full methodology: manual tool installation,…
 themalwareguardian/cve-2019-25485
Stack-based buffer overflow in R 3.4.4. Full exploitation on x86, but only RIP control with gadget analysis on x64 due to program constraints. The…
 victor875/cve-2025-5548
Develops a proof-of-concept exploit for CVE-2025-5548, a stack-based buffer overflow enabling remote code execution, with detailed technical analysis…
 charlyrr/cve-2025-5548
Educational lab documenting step-by-step exploitation of CVE-2025-5548 (Stack Buffer Overflow) on Windows 11, from fuzzing and crash analysis to…
 anasrami12/cve-2025-5548
Methodology for vulnerability analysis and exploit development, covering static/dynamic analysis, fuzzing, patch diffing, and 0-day research with…
 f01965/cve-2019-8014
PoC and exploit for CVE-2019-8014 with shellcode payload (calc/CMD) triggered via crafted BMP image. Includes binary exploitation analysis.
 woshigenm/cve-2026-97555
Analysis, POC, and arm64 exploit chain for a Linux cifs.ko DACL heap overflow (CVE-2026-97555), escalating to a uid-0 credential overwrite on the…
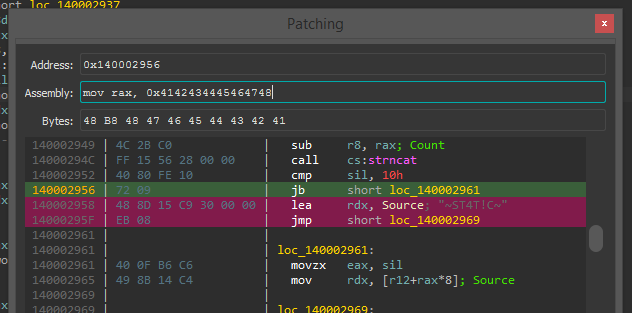 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro

 zx0cf1/shredder-rs
A high-fidelity x86_64 polymorphic mutation engine focused on instruction-level fragmentation and context preservation.
 chris1sflaggin/lcsajdump
An ML powered Graph-Based Multi-Architecture Approach for ROP Gadget Detection
 trustedsec/lazzzy_dump
Statically extracts and decrypts AES-CBC/XOR-obfuscated shellcode from laZzzy-wrapped PE binaries via signature matching and RIP-relative address…
 paulsery/cve-2021-30632
m-y-mo: https://github.com/github/securitylab/tree/main/SecurityExploits/Chrome/v8/CVE-2021-30632
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…