
chakra-exploit-framework
 ntdelta/chakra-exploit-framework
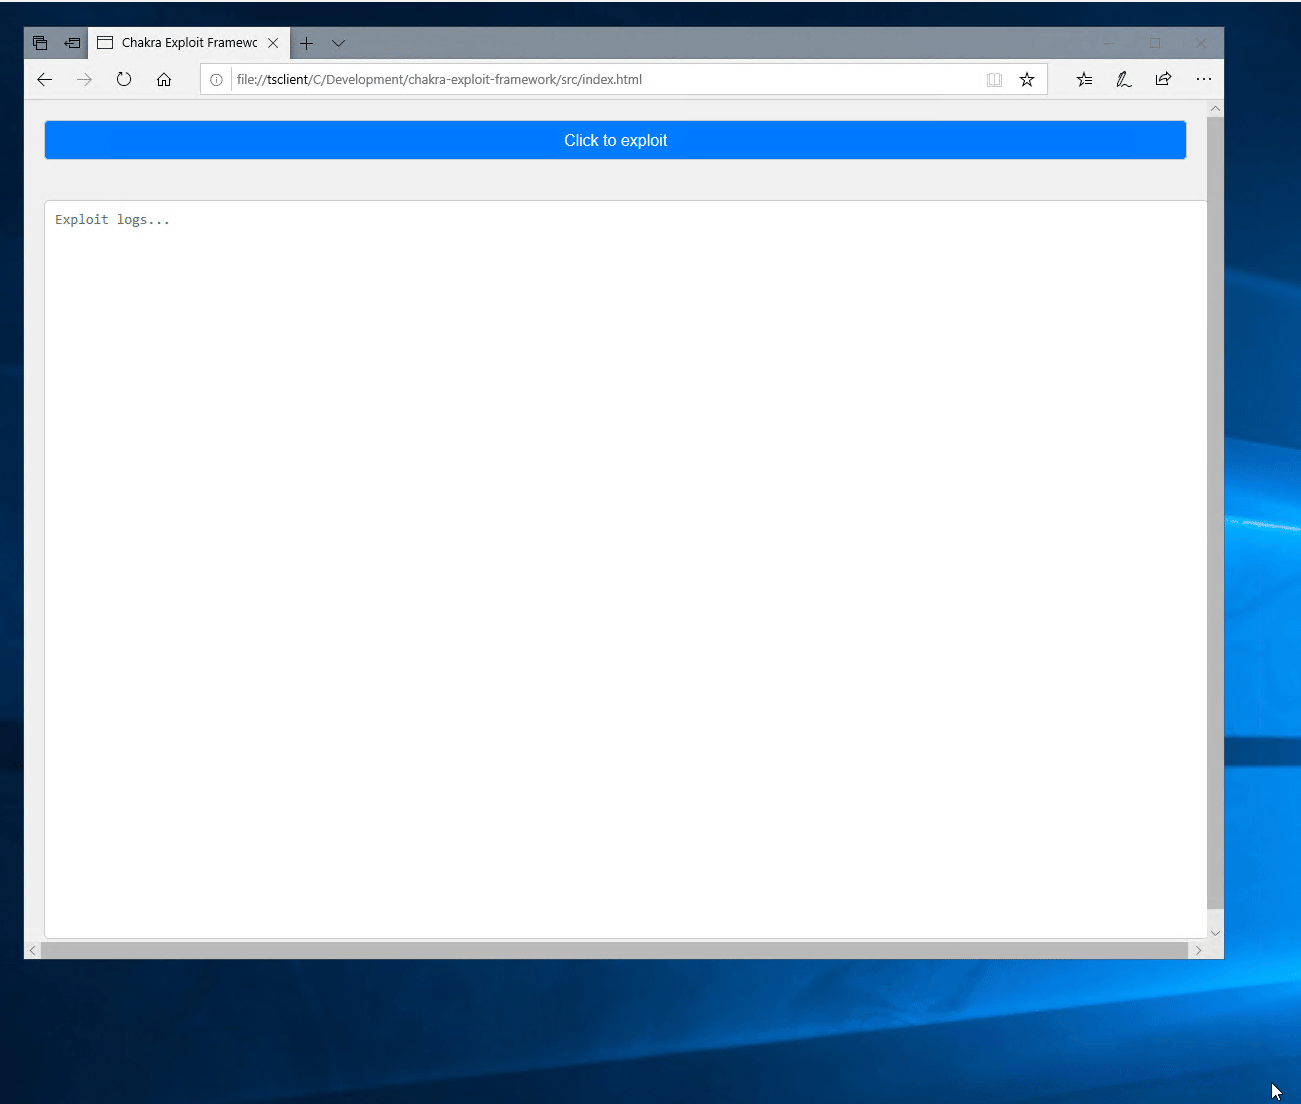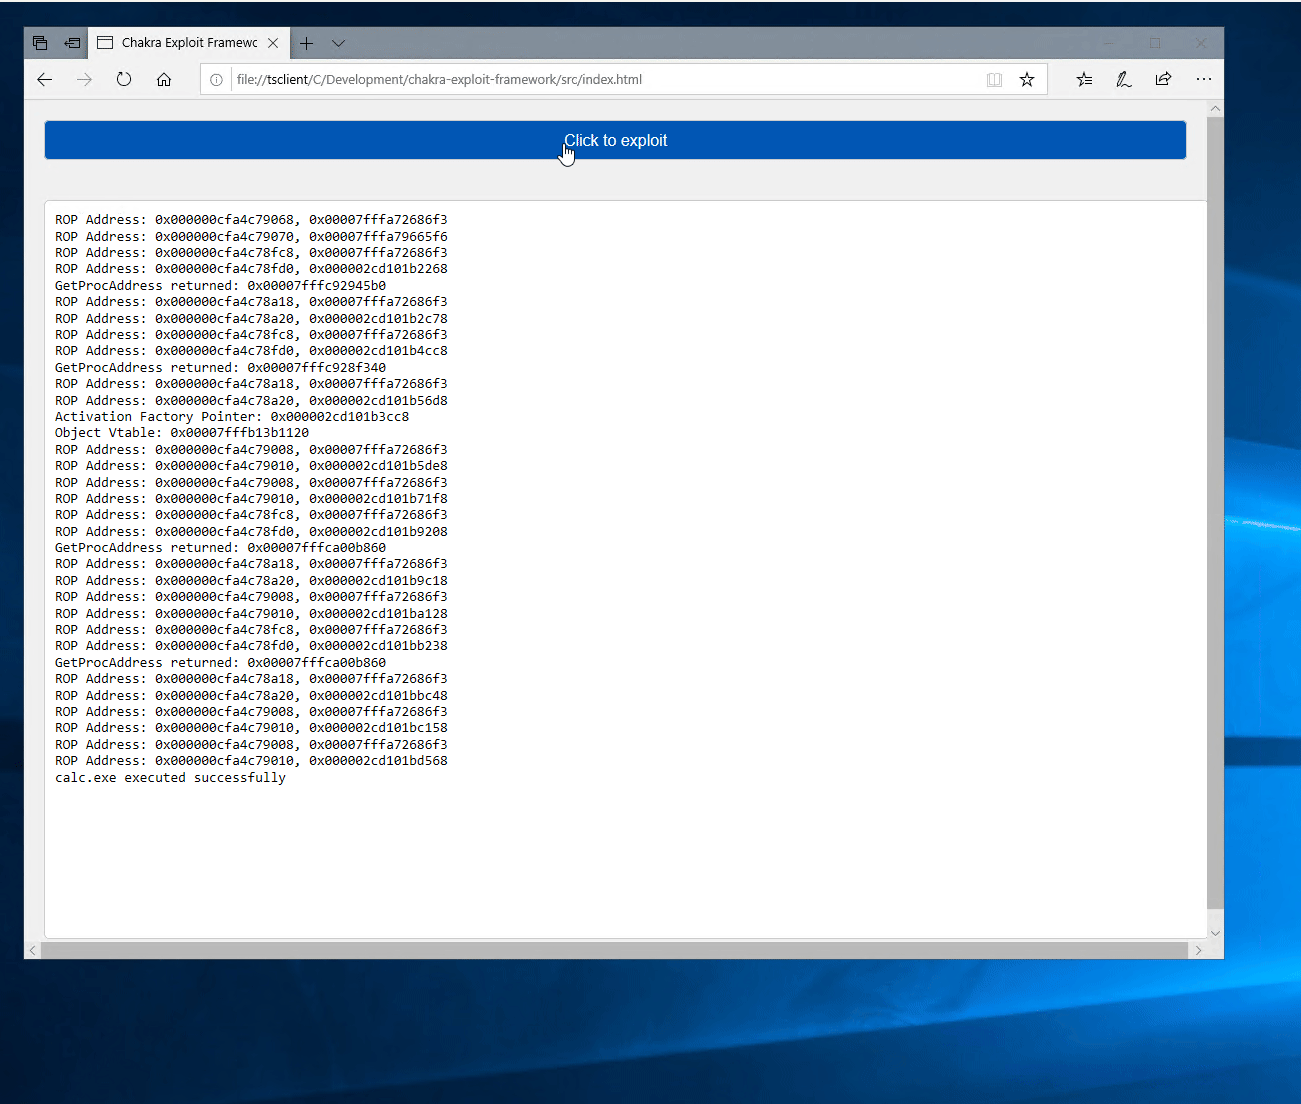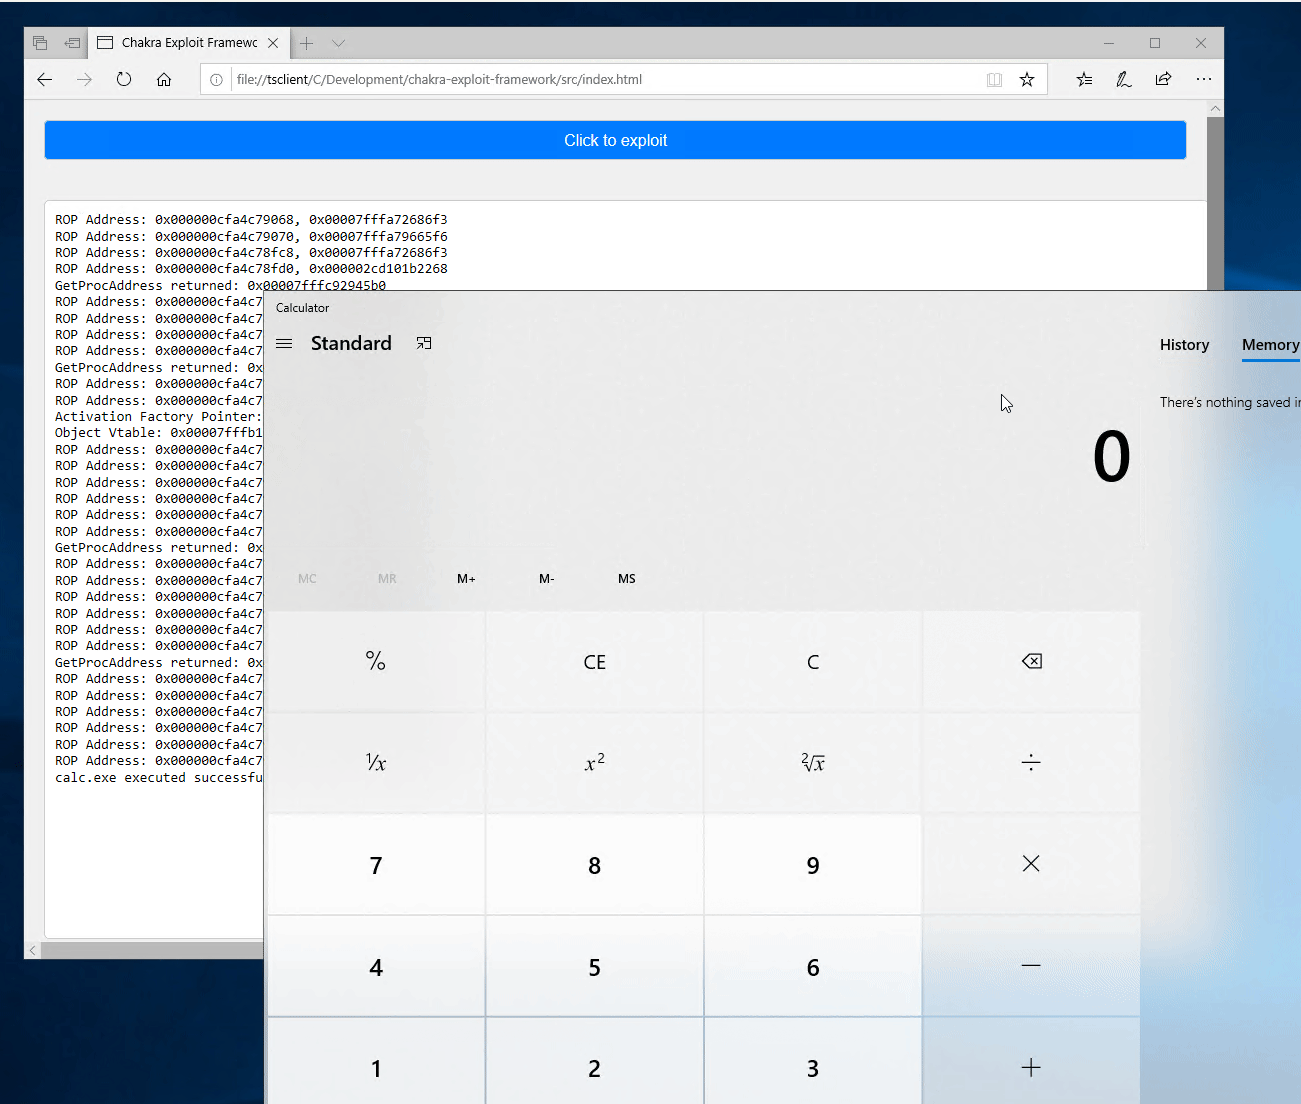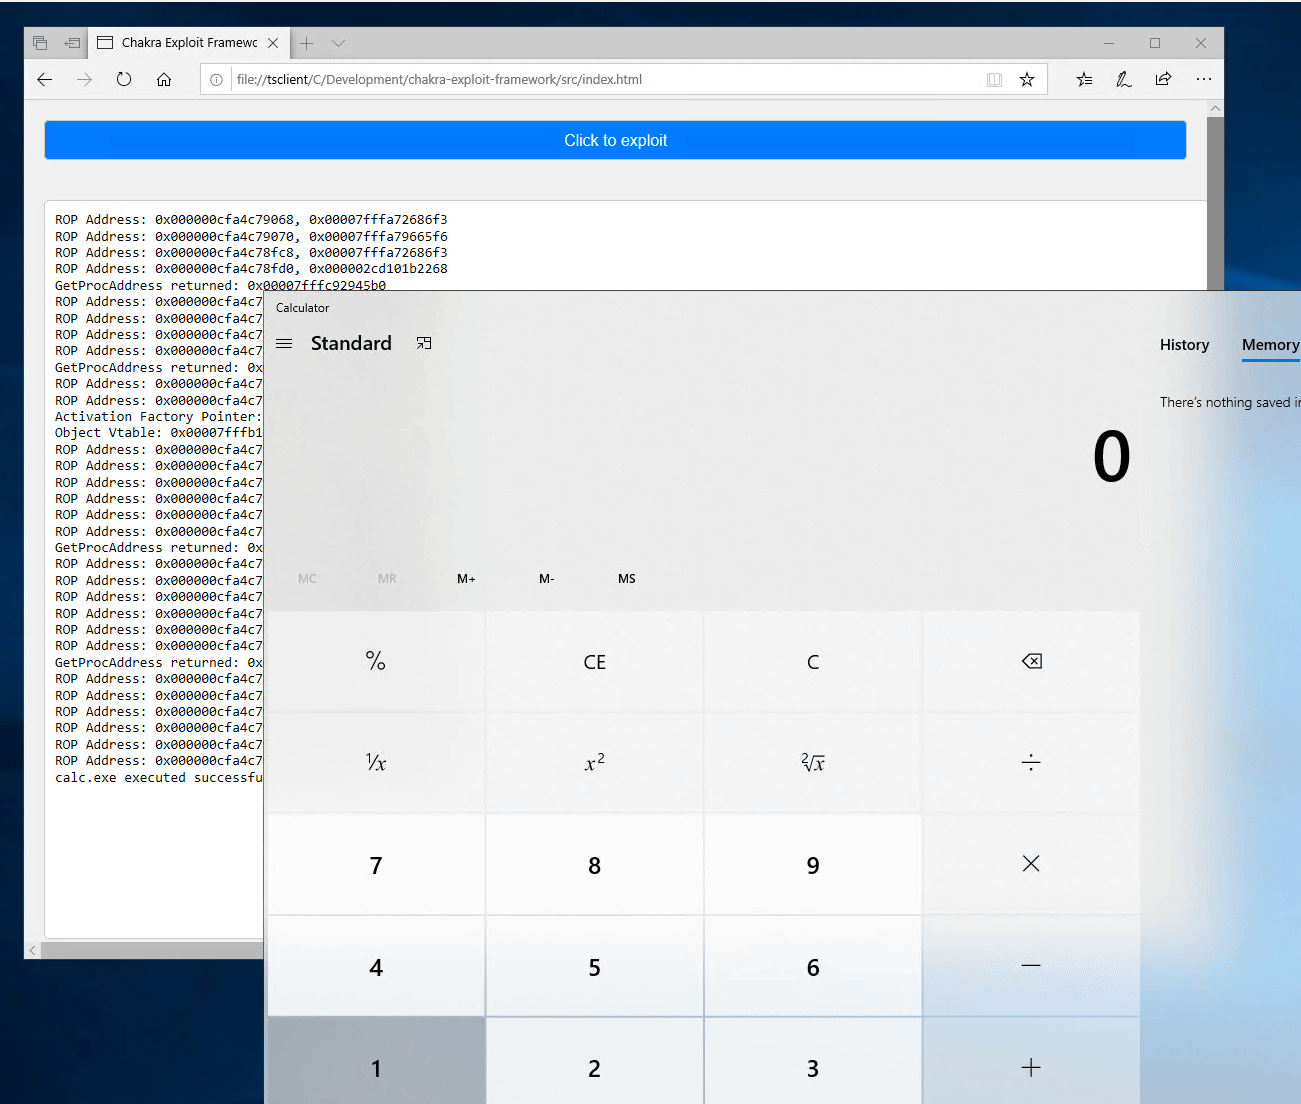
Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567
binary-exploitationeducationexploit-frameworks+6
1
ntdelta/chakra-exploit-frameworkBrowser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567
 diego57709/cve-2025-5548
Structured lab for controlled exploitation of CVE-2025-5548 (FreeFloat FTP Server). Includes environment setup, fuzzing, EIP control, badchars…
 gmh5225/icall-gadget
Exploit for redirecting control flow of a legit kernel module to your own illegitimate kernel module to evade anti-cheats stack walking
 qduarte-42/rainfall
Introduction to the exploitation of ELF binaries.
 egebalci/egesploit
EGESPLOIT is a golang library for malware development
 optiv/ivy
Ivy is a payload creation framework for the execution of arbitrary VBA (macro) source code directly in memory. Ivy’s loader does this by utilizing…
 zardus/ctf-tools
Some setup scripts for security research tools.
 bishopfox/sliver
Adversary Emulation Framework
 ne0nd0g/merlin
Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
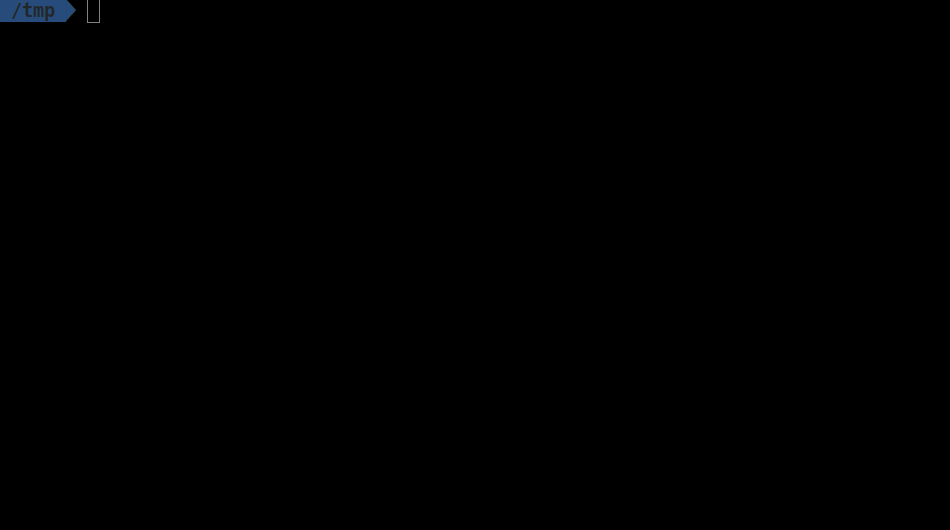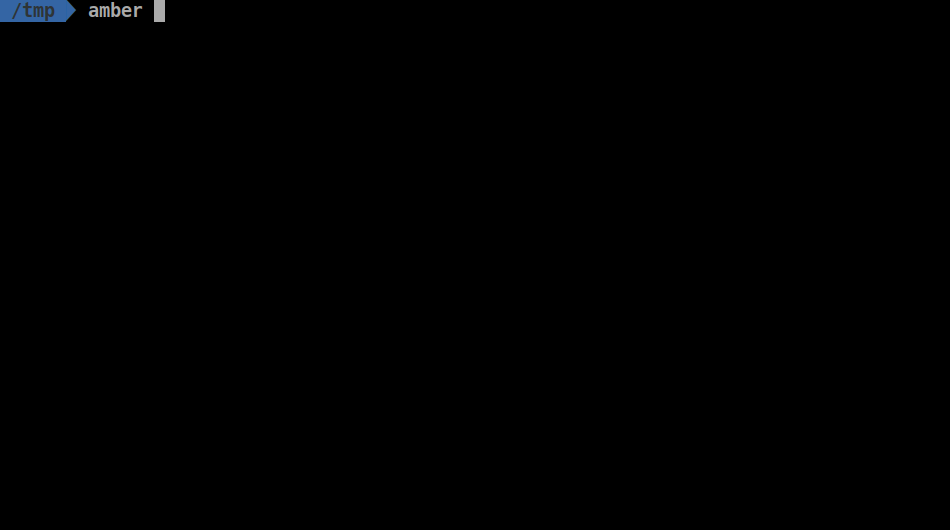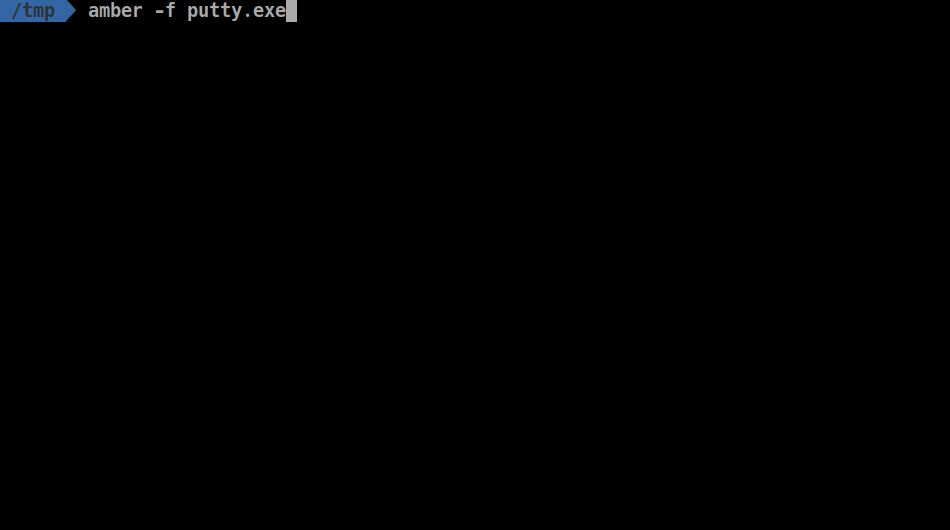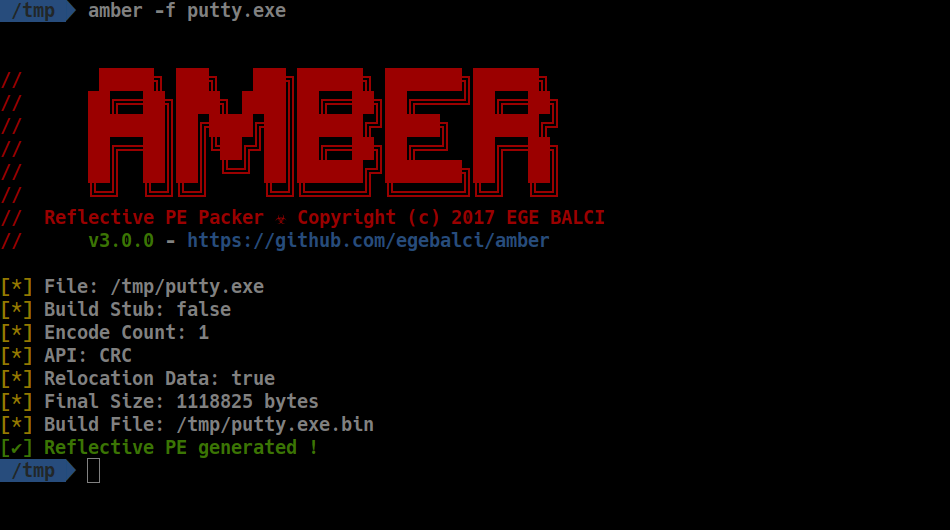 egebalci/amber
Reflective PE packer.
 virtualalllocex/defcon-31-syscalls-workshop
Contains all the material from the DEF CON 31 workshop "(In)direct Syscalls: A Journey from High to Low".
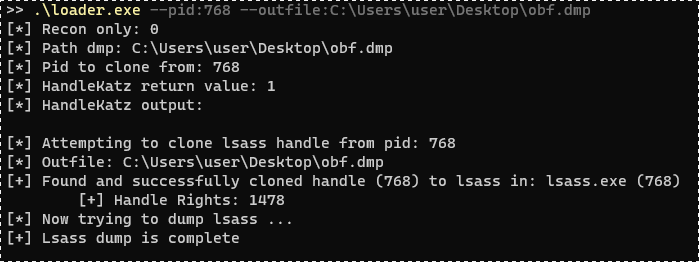 codewhitesec/handlekatz
PIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
 davidbuchanan314/monomorph
MD5-Monomorphic Shellcode Packer - all payloads have the same MD5 hash
 jjyg/metasm
This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby
 f1zm0/acheron
indirect syscalls for AV/EDR evasion in Go assembly