
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
843 results
mwemu preview

mwemu

GitHubmwemuorg/mwemu

Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…

binary-analysisexploit-frameworksmalware-analysis+2
313
5 days ago
Shellcode-Injection-Techniques preview

Shellcode-Injection-Techniques

GitHubplackyhacker/shellcode-injection-techniques

C# implementations of shellcode injection techniques including classic injection, thread hijacking, process hollowing, and atom bombing, using…
exploitationpost-exploitationred-teaming+1
4664 years ago
NimPackt-v1 preview

NimPackt-v1

GitHubchvancooten/nimpackt-v1

Nim-based assembly packer and shellcode loader for opsec & profit
binary-exploitationexploit-frameworkspayload-generation+3
4863 years ago
MorphAES preview

MorphAES

GitHubcryptolok/morphaes

IDPS & SandBox & AntiVirus STEALTH KILLER. MorphAES is the world's first polymorphic shellcode engine, with metamorphic properties and capability to…
binary-exploitationexploitationids-ips-evasion+4
3244 years ago
spawn preview

spawn

GitHubboku7/spawn

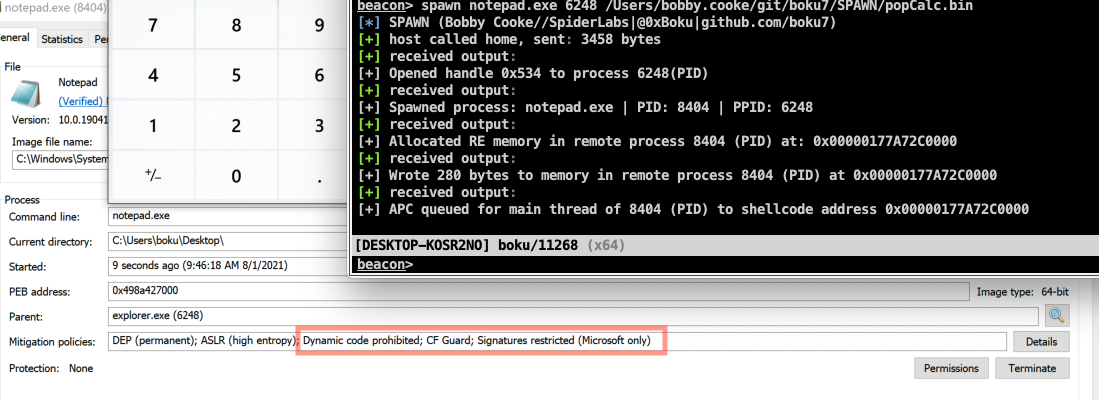
Cobalt Strike BOF that spawns a sacrificial process, injects it with shellcode, and executes payload. Built to evade EDR/UserLand hooks by spawning…

command-and-controlexploitationpayload-development+5
4663 years ago
DllNotificationInjection preview

DllNotificationInjection

GitHubdec0ne/dllnotificationinjection

A POC of a new “threadless” process injection technique that works by utilizing the concept of DLL Notification Callbacks in local and remote…
exploitationred-teamingshellcode
4683 years ago
Medusa preview

Medusa

GitHubmythicagents/medusa

Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
command-and-controlexploit-frameworkslateral-movement+8
2101 month ago
anamnesis-release preview

anamnesis-release

GitHubseanheelan/anamnesis-release

Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…

ai-securitybinary-exploitationeducation+9
6347 months ago
RedPeanut preview

RedPeanut

GitHubb4rtik/redpeanut

RedPeanut is a small RAT developed in .Net Core 2 and its agent in .Net 3.5 / 4.0.
command-and-controlexploit-frameworkspayload-generation+7
3316 years ago
KittyStager preview

KittyStager

GitHubenelg52/kittystager

KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
command-and-controleducationencryption-decryption-tools+6
2283 years ago
FUD-UUID-Shellcode preview

FUD-UUID-Shellcode

GitHubbl4ckm1rror/fud-uuid-shellcode

C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…

binary-exploitationdefensive-toolsexploitation+6
3343 years ago
SMBGhost_AutomateExploitation preview

SMBGhost_AutomateExploitation

GitHubbarriuso/smbghost_automateexploitation

SMBGhost (CVE-2020-0796) Automate Exploitation and Detection
exploitationpayload-generationpenetration-testing+3
3584 years ago
D1rkLdr preview

D1rkLdr

GitHubsaadahla/d1rkldr

Shellcode Loader with Indirect Dynamic syscall Implementation , shellcode in MAC format, API resolving from PEB, Syscall calll and syscall…
ids-ips-evasionpayload-developmentred-teaming+1
3223 years ago
NyxInvoke preview

NyxInvoke

GitHubblacksnufkin/nyxinvoke

NyxInvoke is a Rust CLI tool for running .NET assemblies, PowerShell, and BOFs with Patchless AMSI and ETW bypass features. with Dual-build support

command-and-controlexploitationids-ips-evasion+6
2421 year ago
BadAssMacros preview

BadAssMacros

GitHubinf0secrabbit/badassmacros

C# tool that generates malicious VBA macros with shellcode injection, VBA purging, and sandbox detection for red team operations.

exploit-frameworkspayload-generationred-teaming+1
4455 years ago
tools preview

tools

GitHubnullsecuritynet/tools

Curated collection of security tools, exploits, proof-of-concept code, shellcodes, and scripts for penetration testing and educational offensive…
curated-resourceseducationexploitation+5
711 month ago
p3-loader preview

p3-loader

GitHuborange-cyberdefense/p3-loader

P³-Shellcode Loader is a loader that implements a code injection technique which leverages the Process Parameters structure as an execution and…
binary-exploitationdefensive-toolseducation+8
2142 months ago
Beaconator preview

Beaconator

GitHubcapt-meelo/beaconator

A beacon generator using Cobalt Strike and a variety of tools.

command-and-controlexploit-frameworkspayload-generation+2
4475 years ago
Previous1…345…47Next