


 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 lem0nsec/shellghost
A memory-based evasion technique which makes shellcode invisible from process start to end.
 nickvourd/supernova
Multi-cipher shellcode encryptor and obfuscator with automatic output conversion to C, C#, Rust, Nim, Python, and more. Supports ROT, XOR, RC4, AES,…
 frkngksl/shoggoth
Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…
 egebalci/amber
Reflective PE packer.
 0xsp-srd/mortar
evasion technique to defeat and divert detection and prevention of security products (AV/EDR/XDR)
 hasherezade/exe_to_dll
Converts a EXE into DLL
 xdnice/pcshare
PCShare是一款强大的远程控制软件,可以监视目标机器屏幕、注册表、文件系统等。
 mgeeky/threadstackspoofer
Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
 virtualalllocex/defcon-31-syscalls-workshop
Contains all the material from the DEF CON 31 workshop "(In)direct Syscalls: A Journey from High to Low".
 mthbernardes/rsg
ReverShellGenerator - A tool to generate various ways to do a reverse shell
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
 x86byte/obfusk8
Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries
 codewhitesec/handlekatz
PIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…
 rvn0xsy/cooolis-ms
Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…
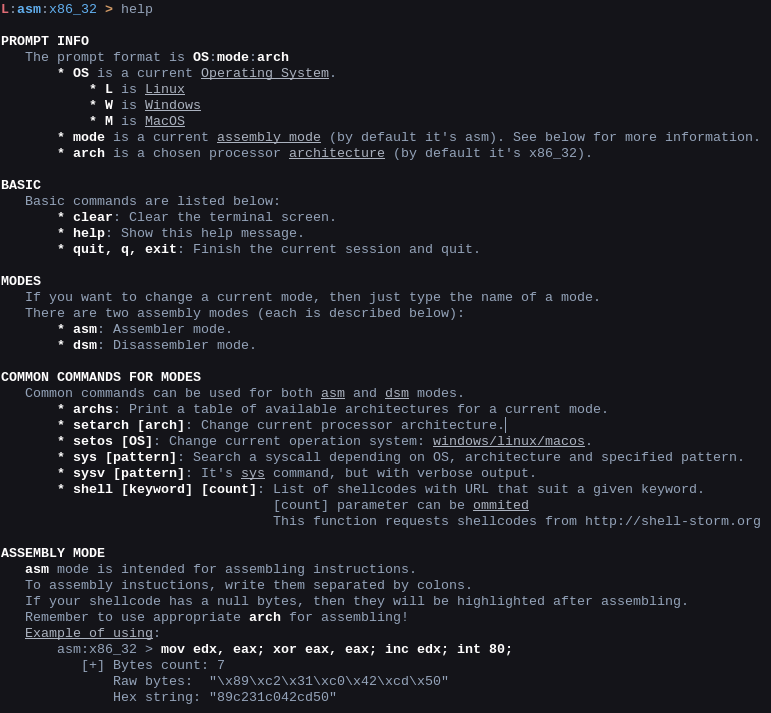 konatabrk/shellen
:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes