
pylibemu
 buffer/pylibemu
A Libemu Cython wrapper
binary-analysisdynamic-analysis-sandboxingmalware-analysis+2
1282 years ago
buffer/pylibemuA Libemu Cython wrapper
 ariary/volana
🌒 Shell command obfuscation to avoid detection systems
 choisg/onedriveupdatersideloading
Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post
 airbus-cert/yara-ttd
Use YARA rules on Time Travel Debugging traces
 cobalt-strike/eden
A PoC UDRL for Cobalt Strike built with Crystal Palace that combines Raphael Mudge's page streaming technique with a modular call gate (Draugr)
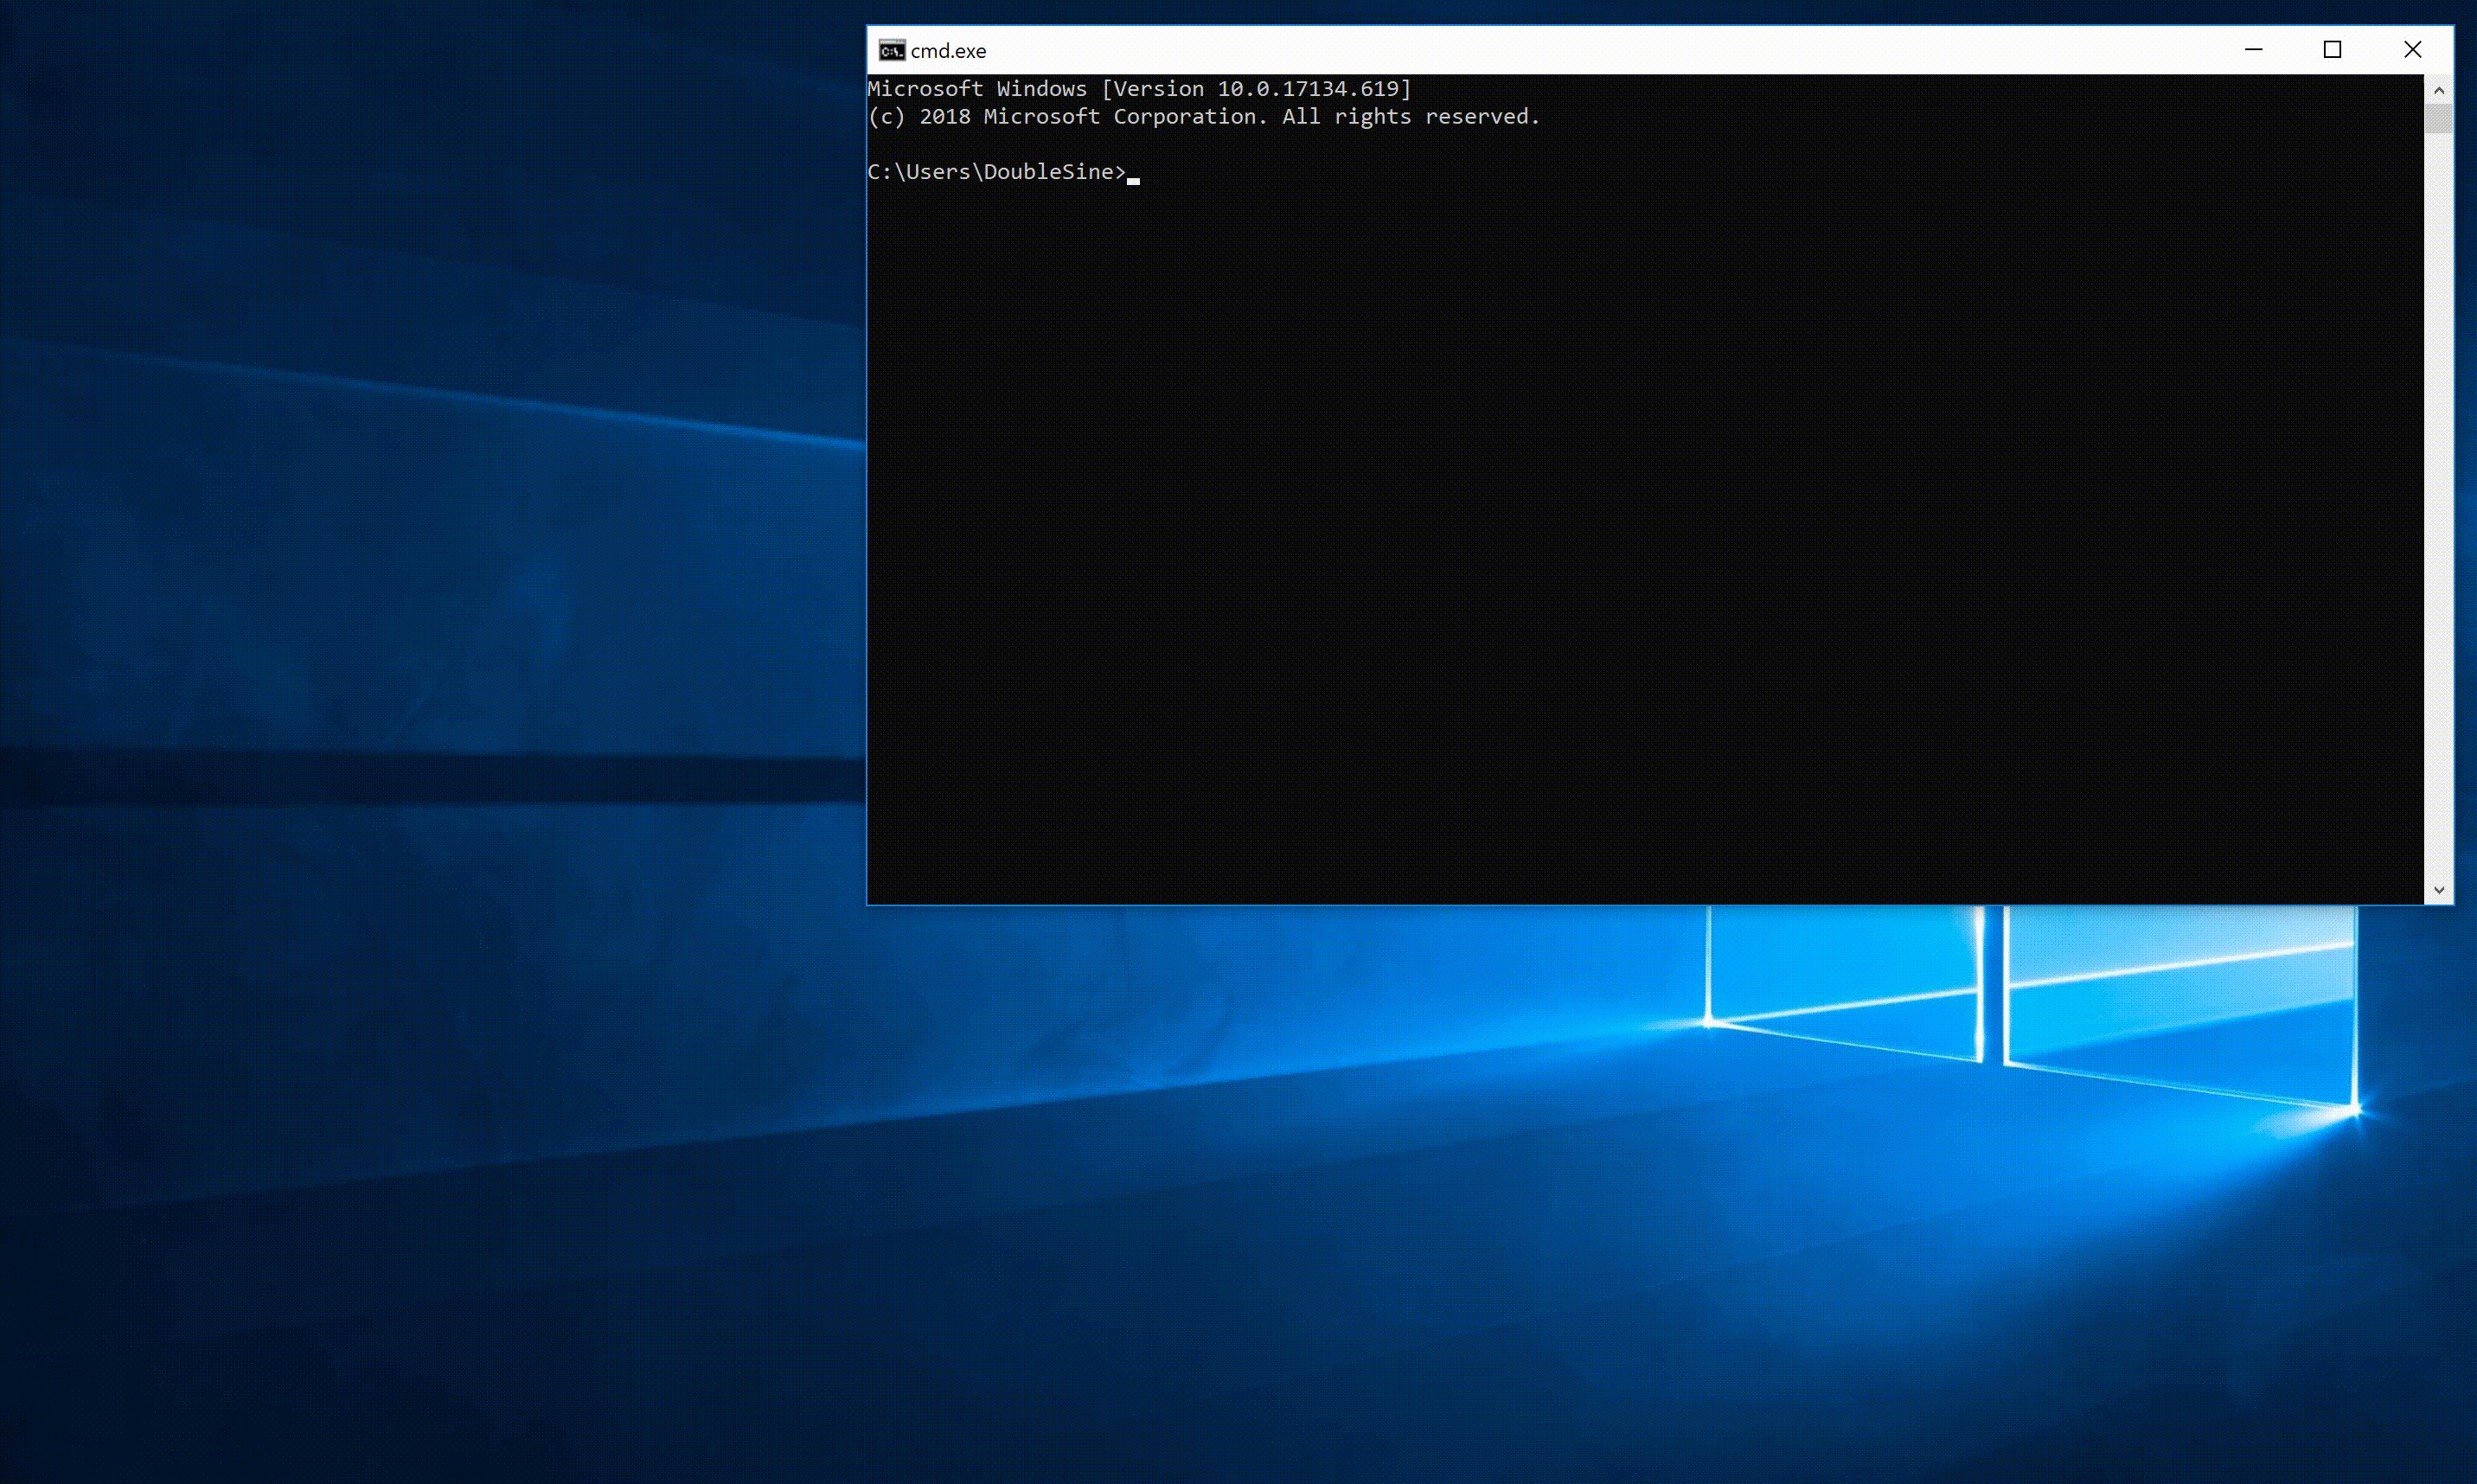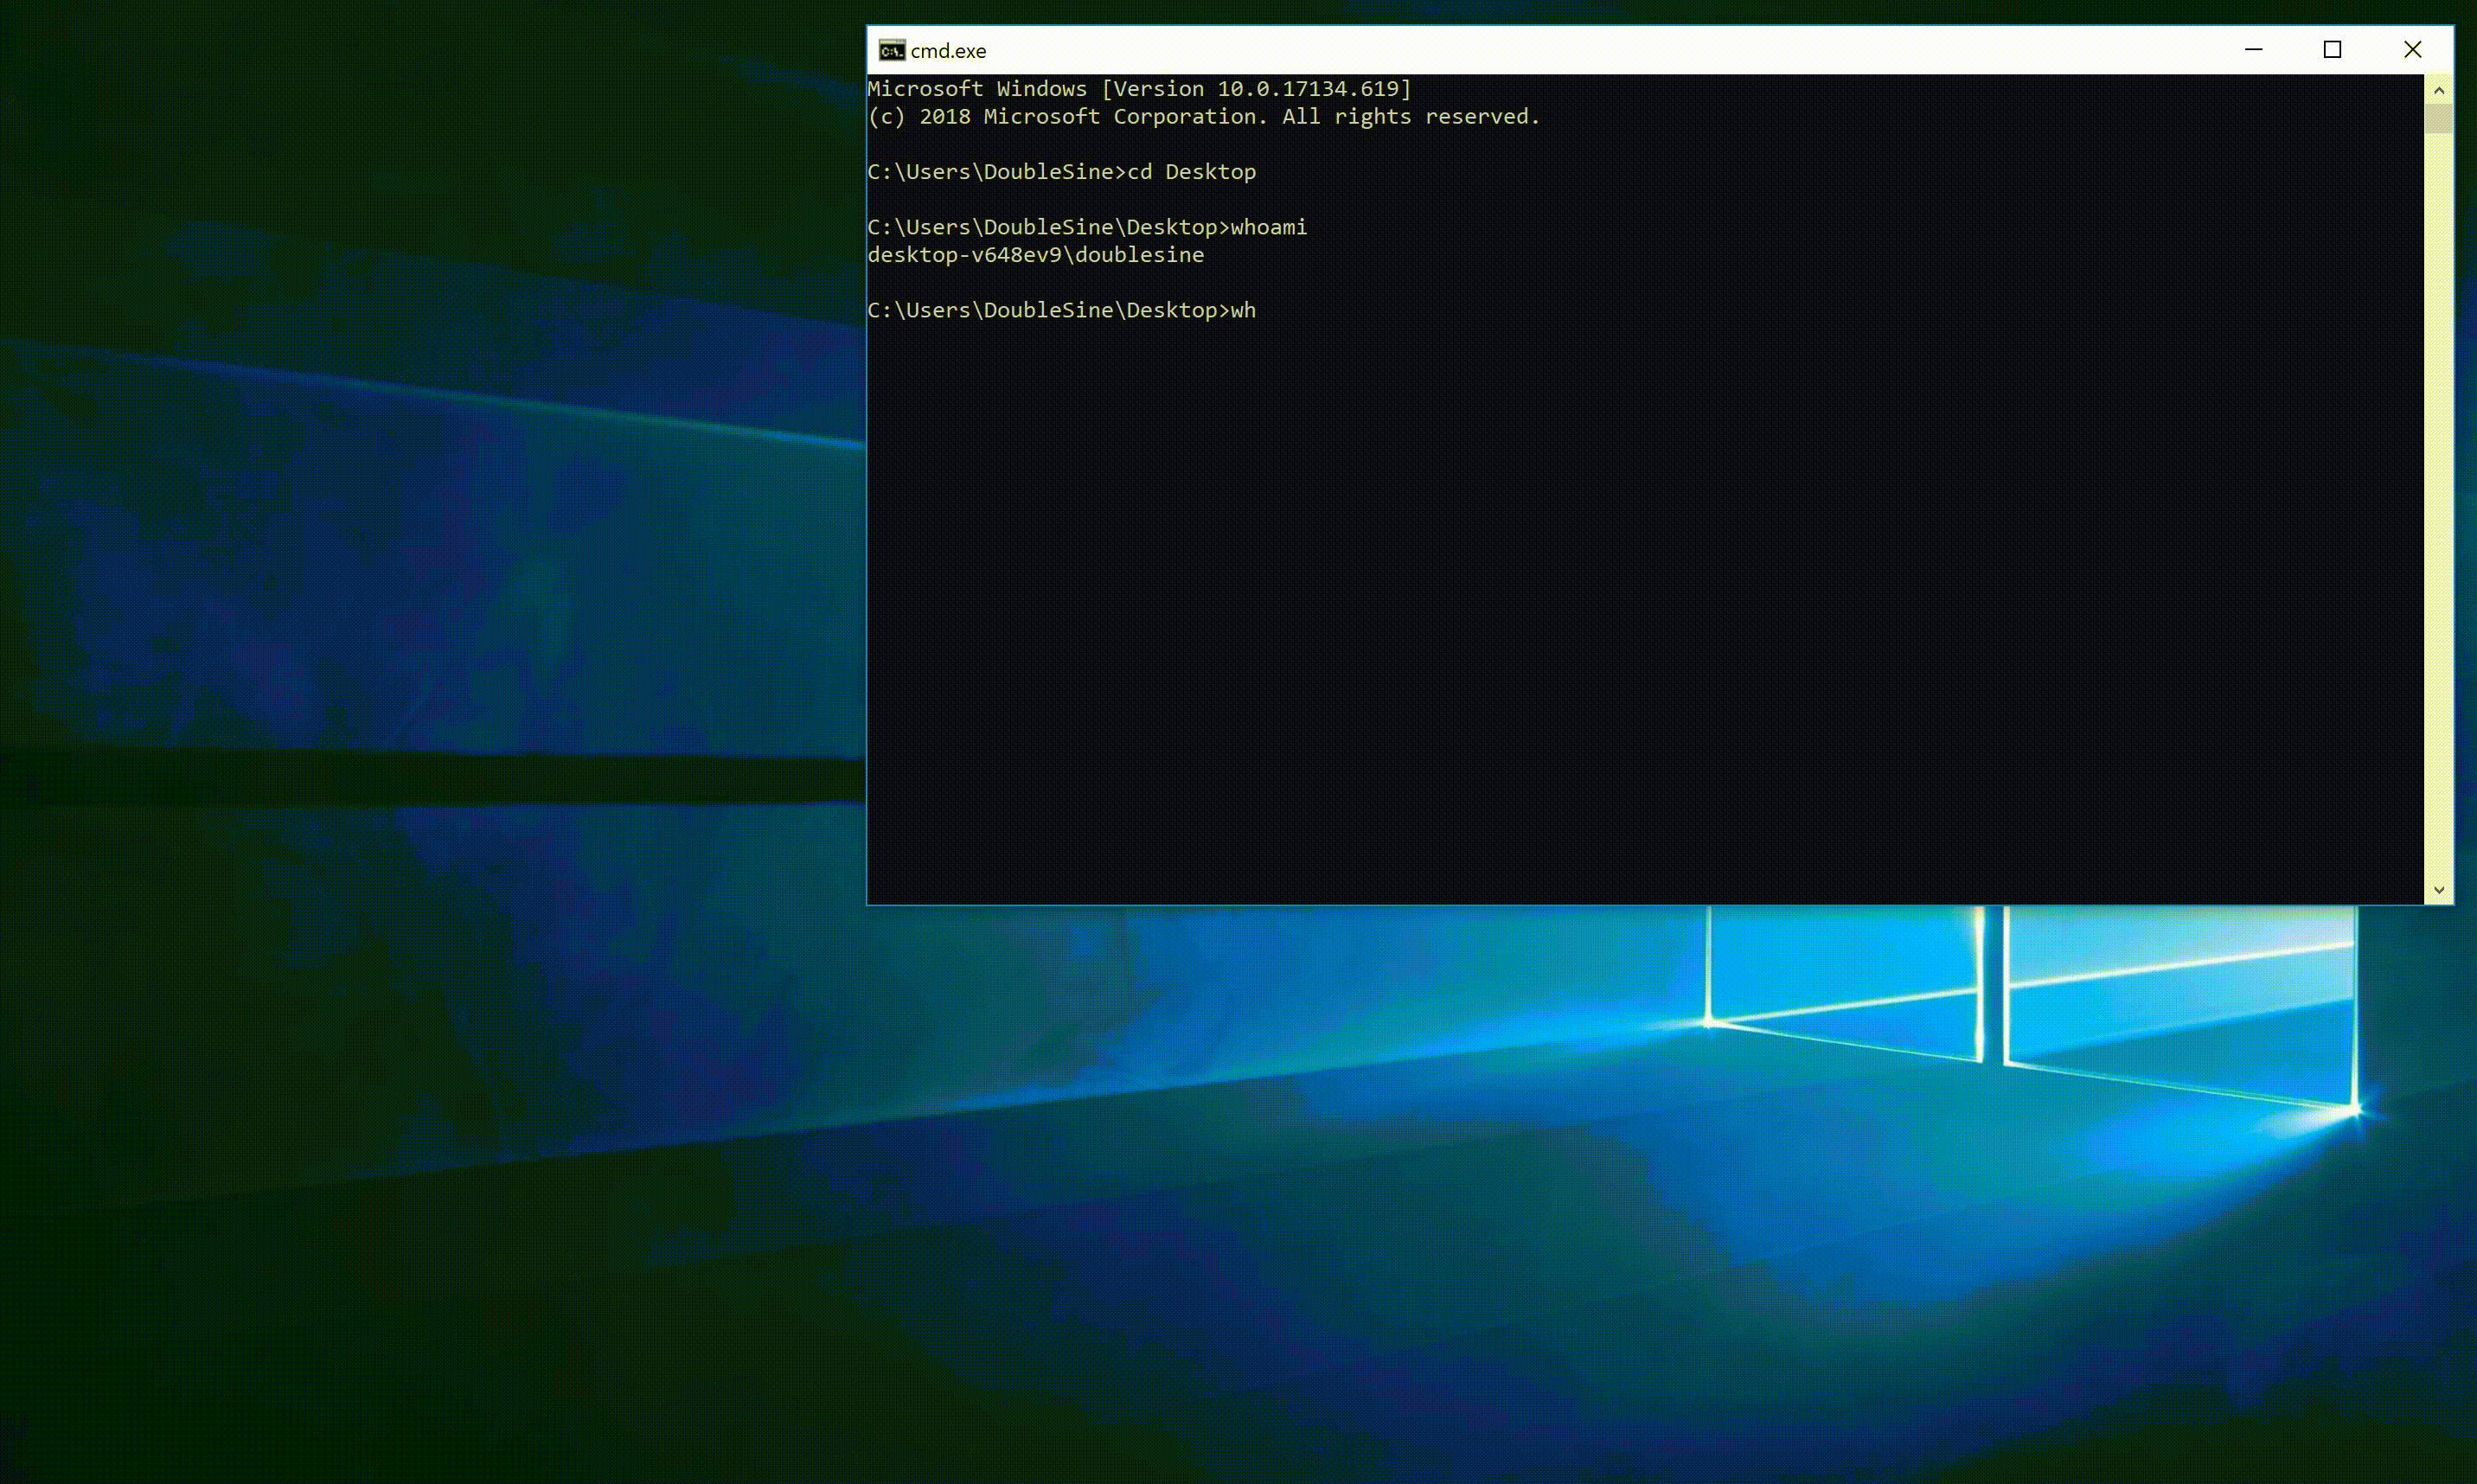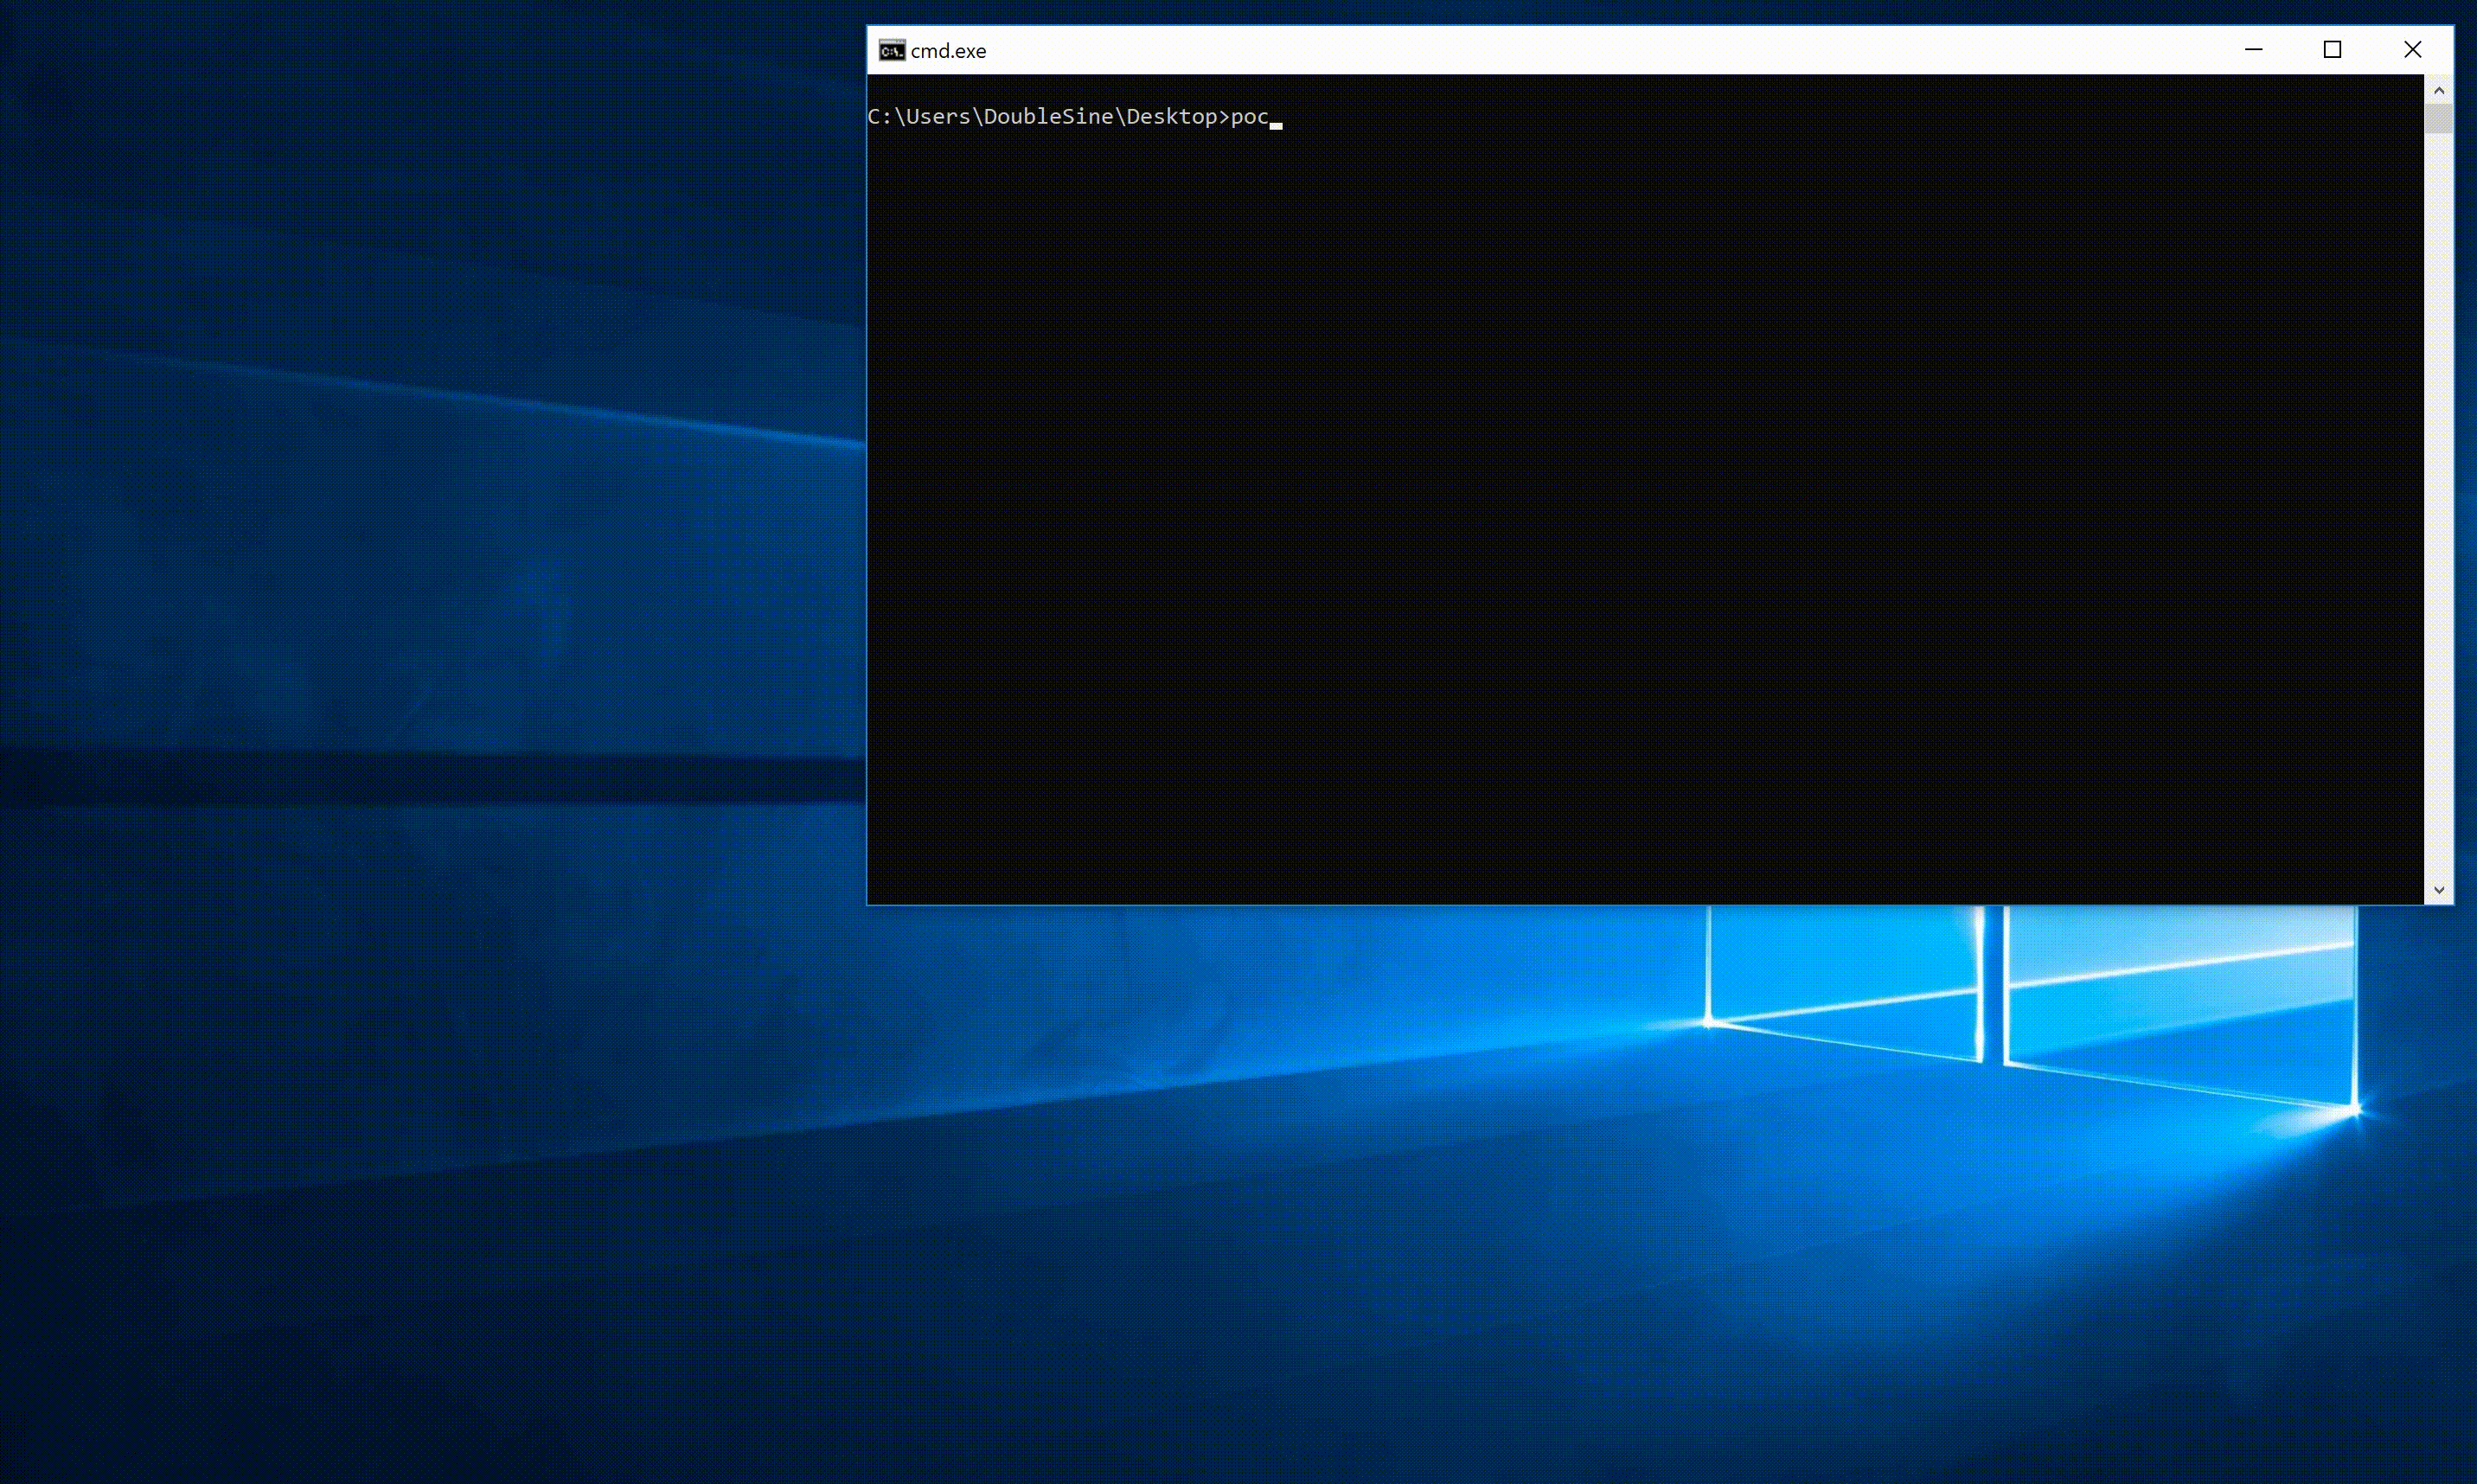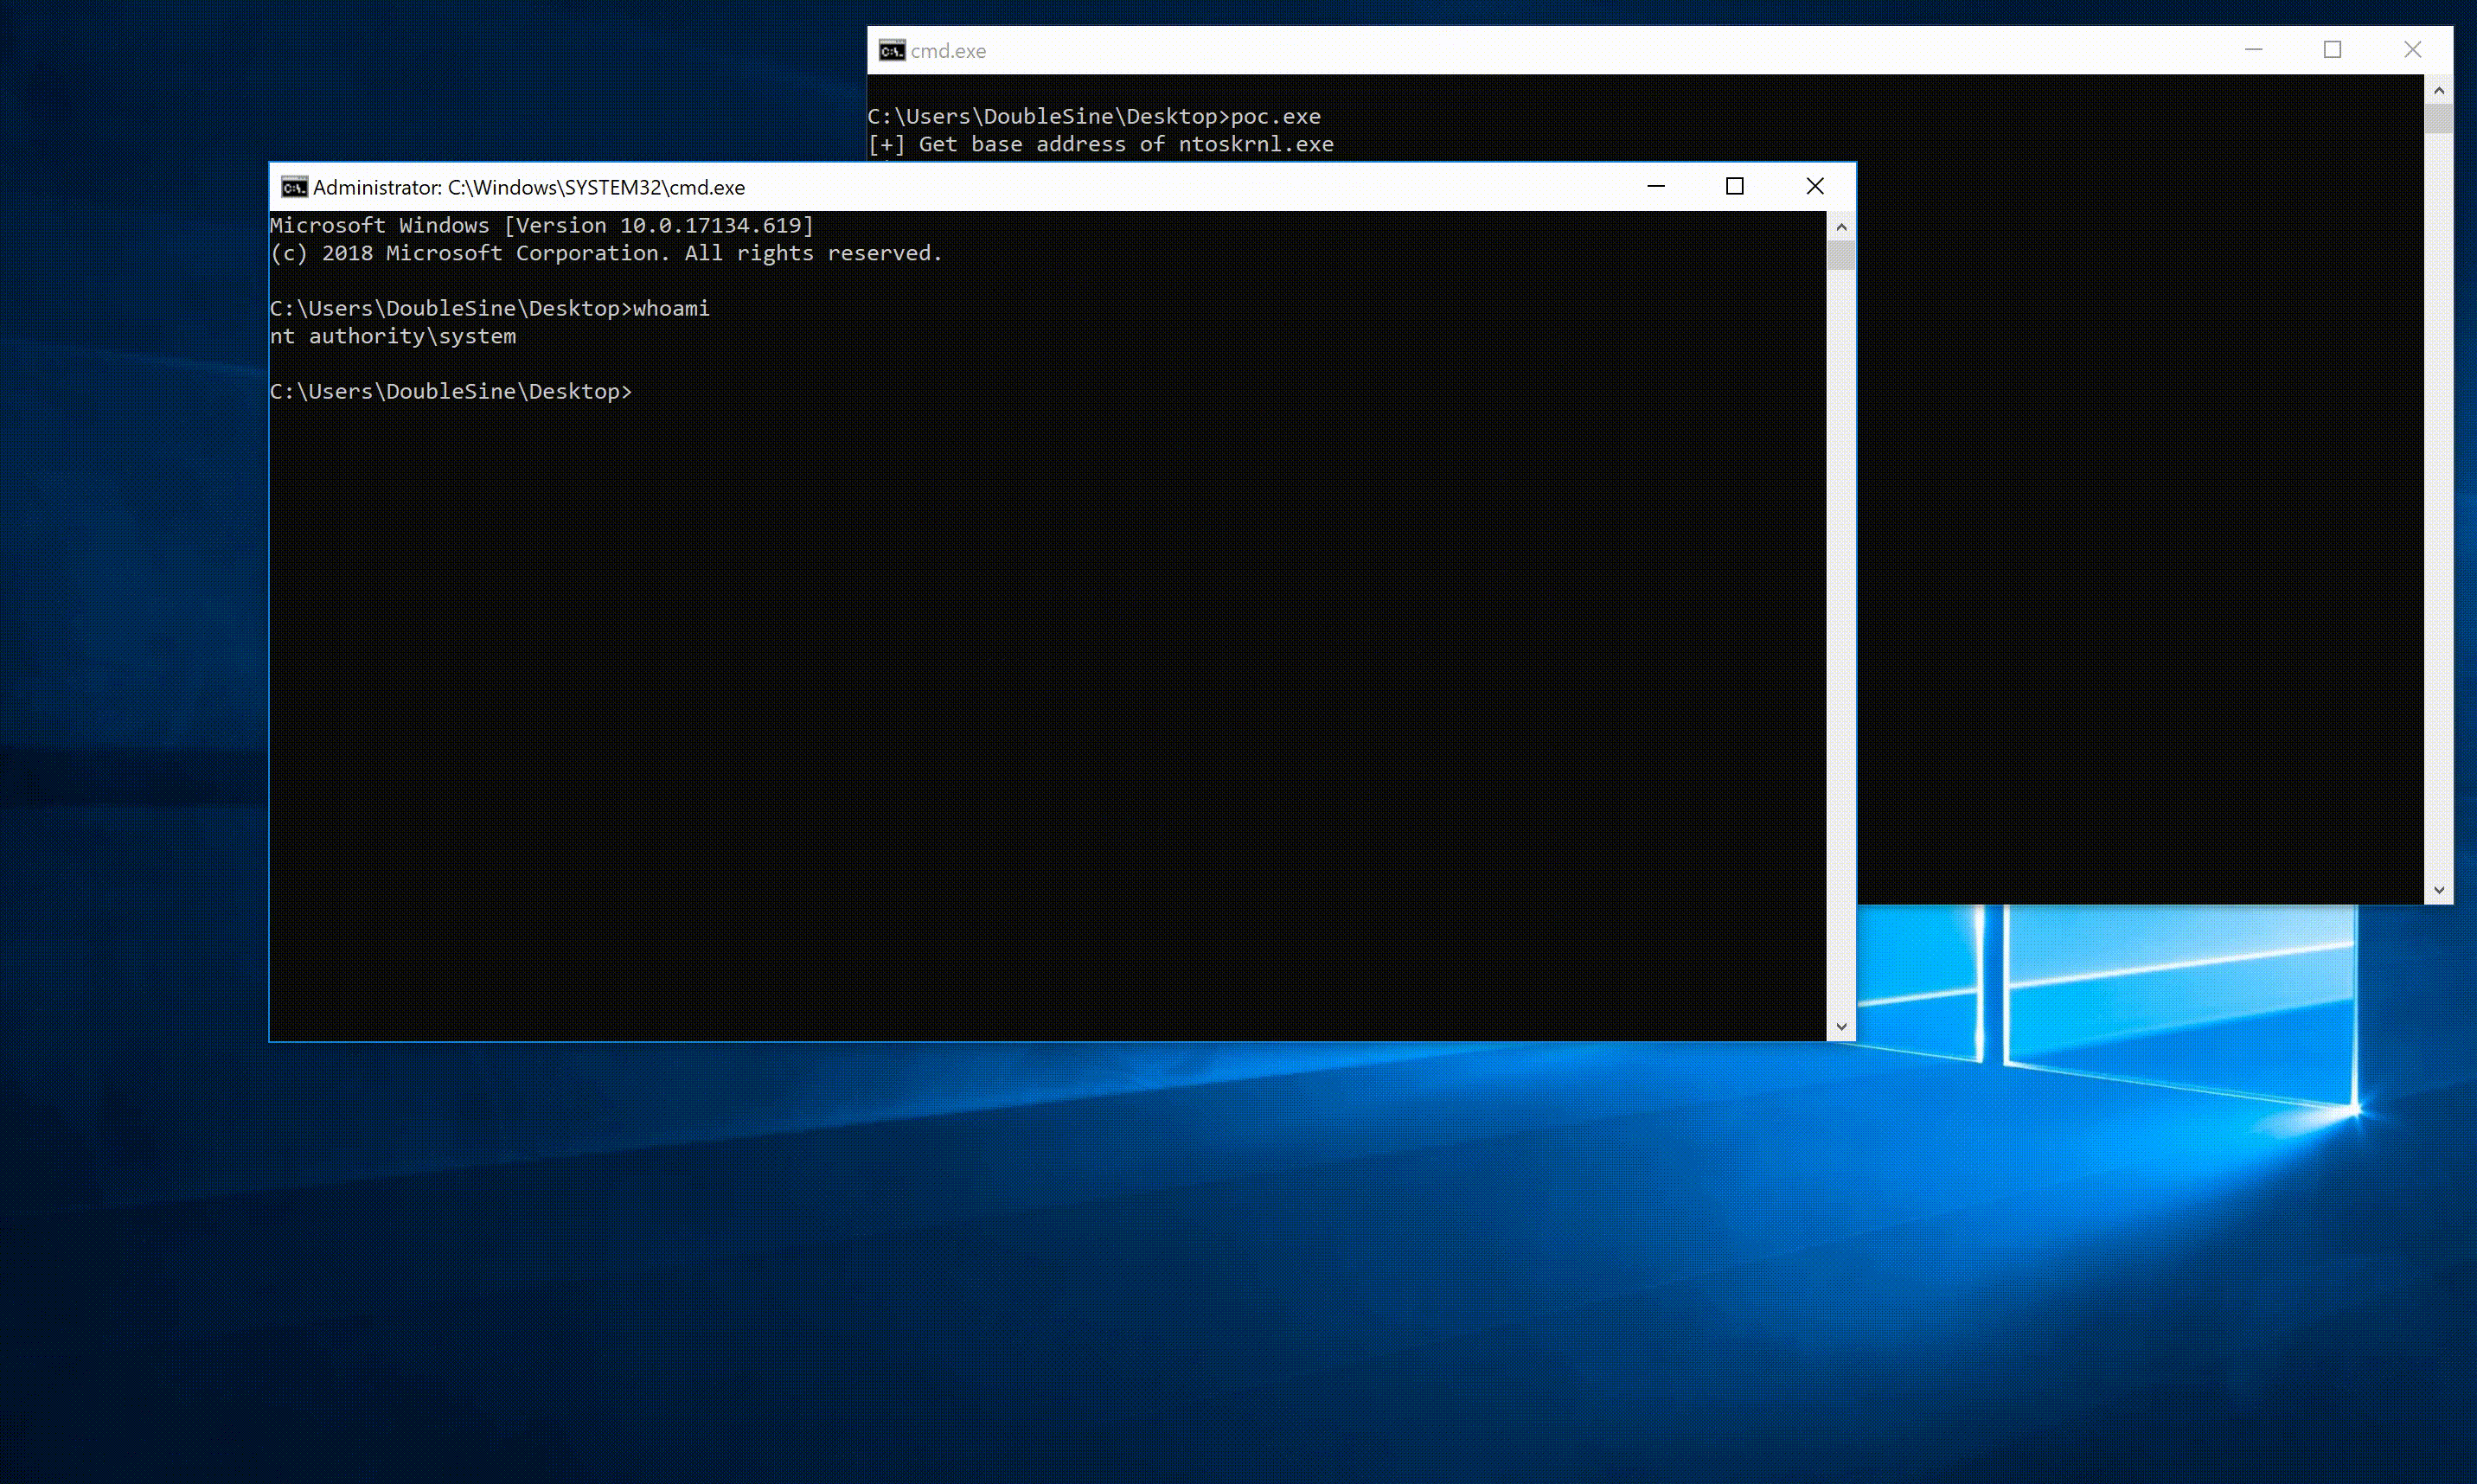 hypersine/sdokeycrypt-sys-local-privilege-elevation
CVE-2019-9729. Transferred from https://github.com/DoubleLabyrinth/SdoKeyCrypt-sys-local-privilege-elevation
 hood3drob1n/cve-2016-3714
ImaegMagick Code Execution (CVE-2016-3714)
 catherines77/activemq-exptools
Apache ActiveMQ漏洞综合利用工具(CVE-2015-5254,CVE-2016-3088,CVE-2022-41678,CVE-2023-46604,CVE-2024-32114,CVE-2026-34197,CVE-2026-40466, CVE-2026-42588)
 backdoorskid/customloadimage
Stealthy .NET assembly loading using AssemblyNative::LoadFromBuffer
 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)
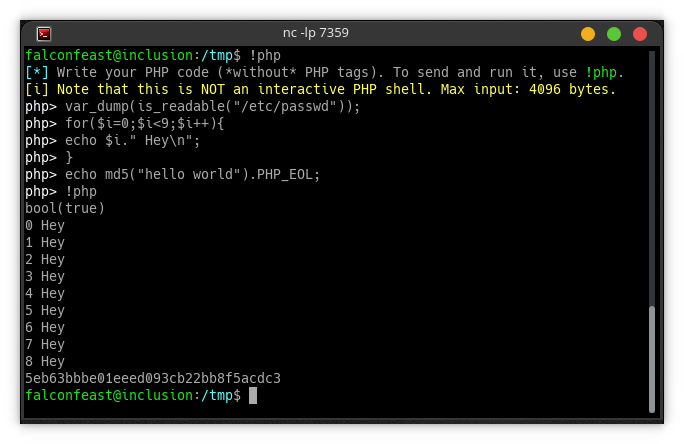 nickguitar/yaps
Yet Another PHP Shell - The most complete PHP reverse shell

 h3x0v3rl0rd/ms17-010_cve-2017-0143
MS17-010_CVE-2017-0143
 nul0x4c/manualrsrcdatafetching
Get your data from the resource section manually, with no need for windows apis
 schich/lucky-spark
A stealthy stager designed for shellcode payloads staged with http/https like Sliver, or on github raw.
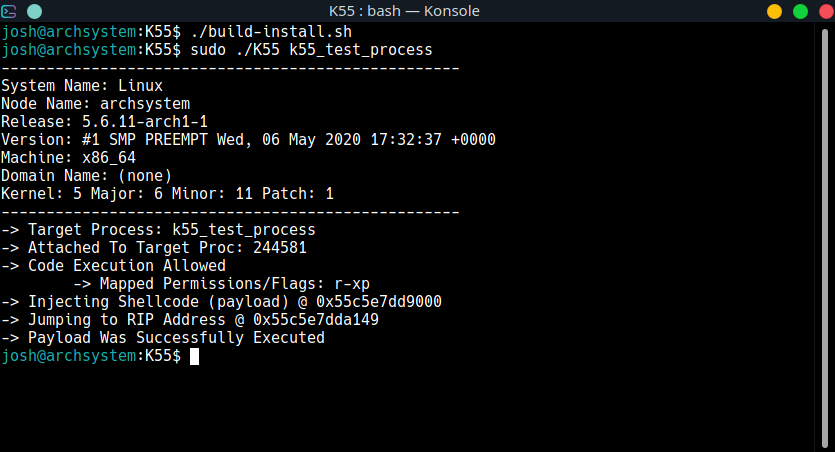
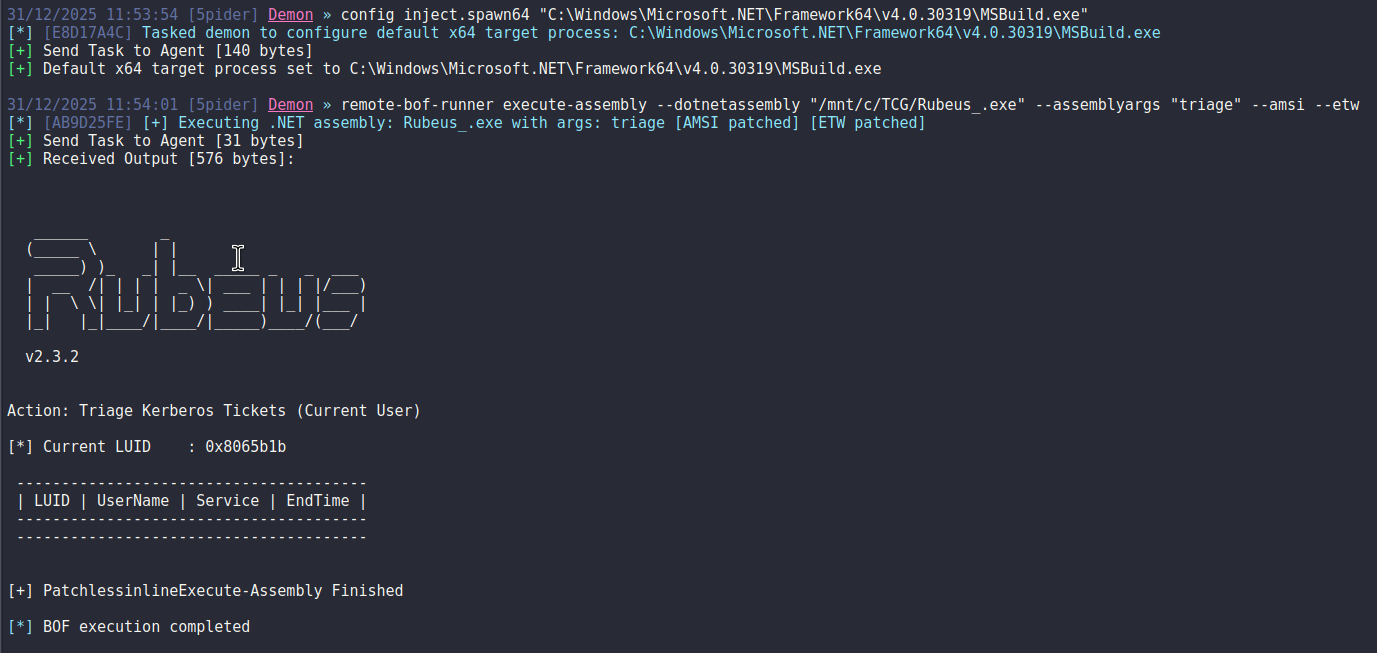 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 kasturixbm5/staged-dll-injection-smb-
Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).