
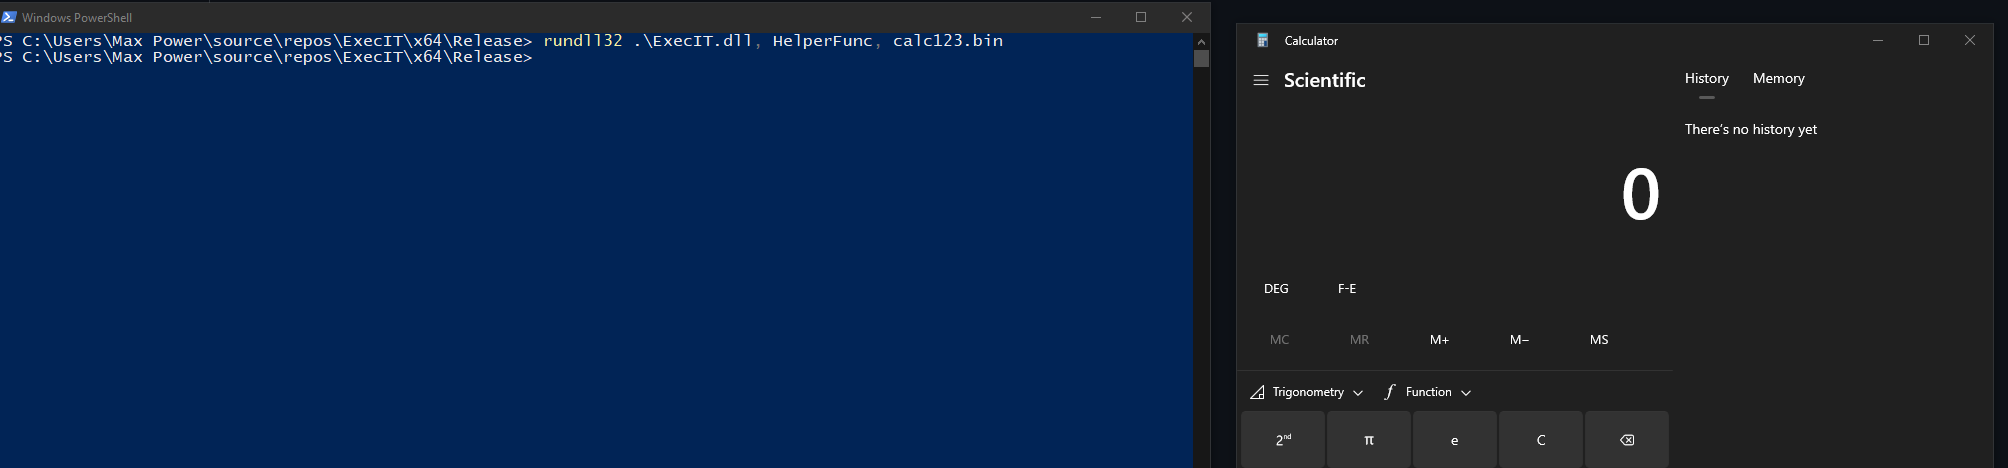
ExecIT
 florylsk/execit
Execute shellcode files with rundll32
ids-ips-evasionmalware-analysispayload-development+4
florylsk/execitExecute shellcode files with rundll32
 hkl1x/bypass_av
Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
 nbaertsch/nimvoke
Indirect syscalls + DInvoke made simple.
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 ps1337/lastenzug
Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
 xaff-xaff/black-angel-rootkit
Black Angel is a Windows 11/10 x64 kernel mode rootkit. Rootkit can be loaded with enabled DSE while maintaining its full functionality.
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
 alberto-galindo/cve-2025-5548
Security research and reproduction of CVE-2025-5548: A stack-based buffer overflow in FreeFloat FTP Server 1.0. Includes binary analysis, crash…
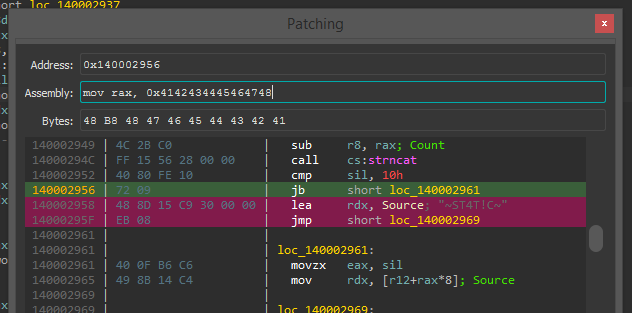 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
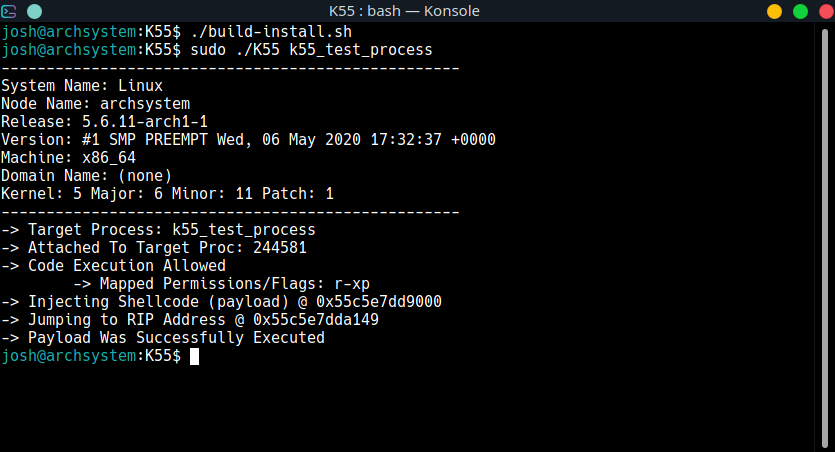
 davidbuchanan314/dlinject
Inject a shared library (i.e. arbitrary code) into a live linux process, without ptrace
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
 abedalqaderswedan1/aswcrypter
An Bash&Python Script For Generating Payloads that Bypasses All Antivirus so far [FUD]
 0xdea/shellcode
A collection of my shellcode samples.
 mahmoudimus/static_asm
Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding
 chainmanner/gzdoom-arbitrary-code-execution-via-zscript-poc
Proof of concept for CVE-2024-54756, a vulnerability I found in GZDoom's ZScript scripting engine.
 soralis0912/cve-2026-43499-aristotle-apk
Android kernel exploit for CVE-2026-43499 (Futex-PI use-after-free) that gains temporary root on Xiaomi XIG04 to enable ADB. Includes automated…
 k3ystr0k3r/cve-2025-32463-exploit
A PoC exploit for CVE-2025-32463 - Sudo Privilege Escalation